
An assistant agent must call a downstream Microsoft Graph API to read only the signed-in user’s calendar. Compliance forbids the agent from using an app-only permission that can read all calendars in the tenant. Which authentication flow should you design?
Select an answer to reveal the explanation.
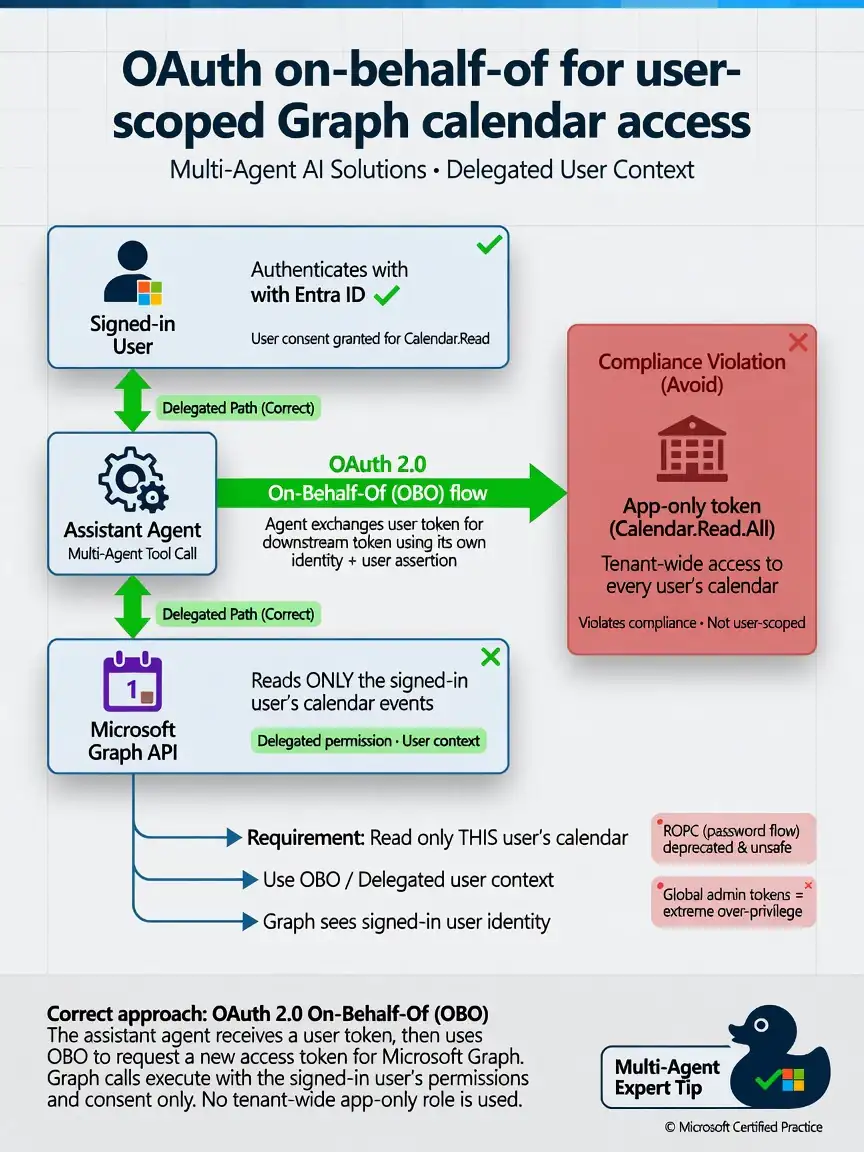
Short Explanation
You need delegated on-behalf-of flow so the agent acts as the signed-in user, not a tenant-wide app-only reader. That keeps Microsoft Graph seeing only that user’s calendar and consent. Don't hand over passwords or global admin tokens—they're way too risky.
Full Explanation
Delegated OAuth 2.0 on-behalf-of is correct. Multi-agent auth flows include user impersonation, on-behalf-of, API keys, and OAuth 2.0. Reading only the signed-in user’s calendar requires delegated OBO/user context so Graph sees that user, not tenant-wide app-only read. The shared tenant-wide Calendar.Read option violates least privilege and compliance. Passing the user’s password for resource-owner-password-credentials is insecure and unsuitable. Storing a global admin refresh token massively over-privileges the agent. Design OBO through your API layer carefully with consent and token exchange. Exam tip: user-scoped Graph access means delegated OBO, not app-only all-users.