
A multi-agent order-fulfillment system stores third-party shipping API credentials and signing certificates used by tool connectors. Compliance requires centralized secret storage, role-based access to secrets, automated rotation, and encryption at rest. Agents run on Azure with managed identities. Which design best satisfies these requirements?
Select an answer to reveal the explanation.
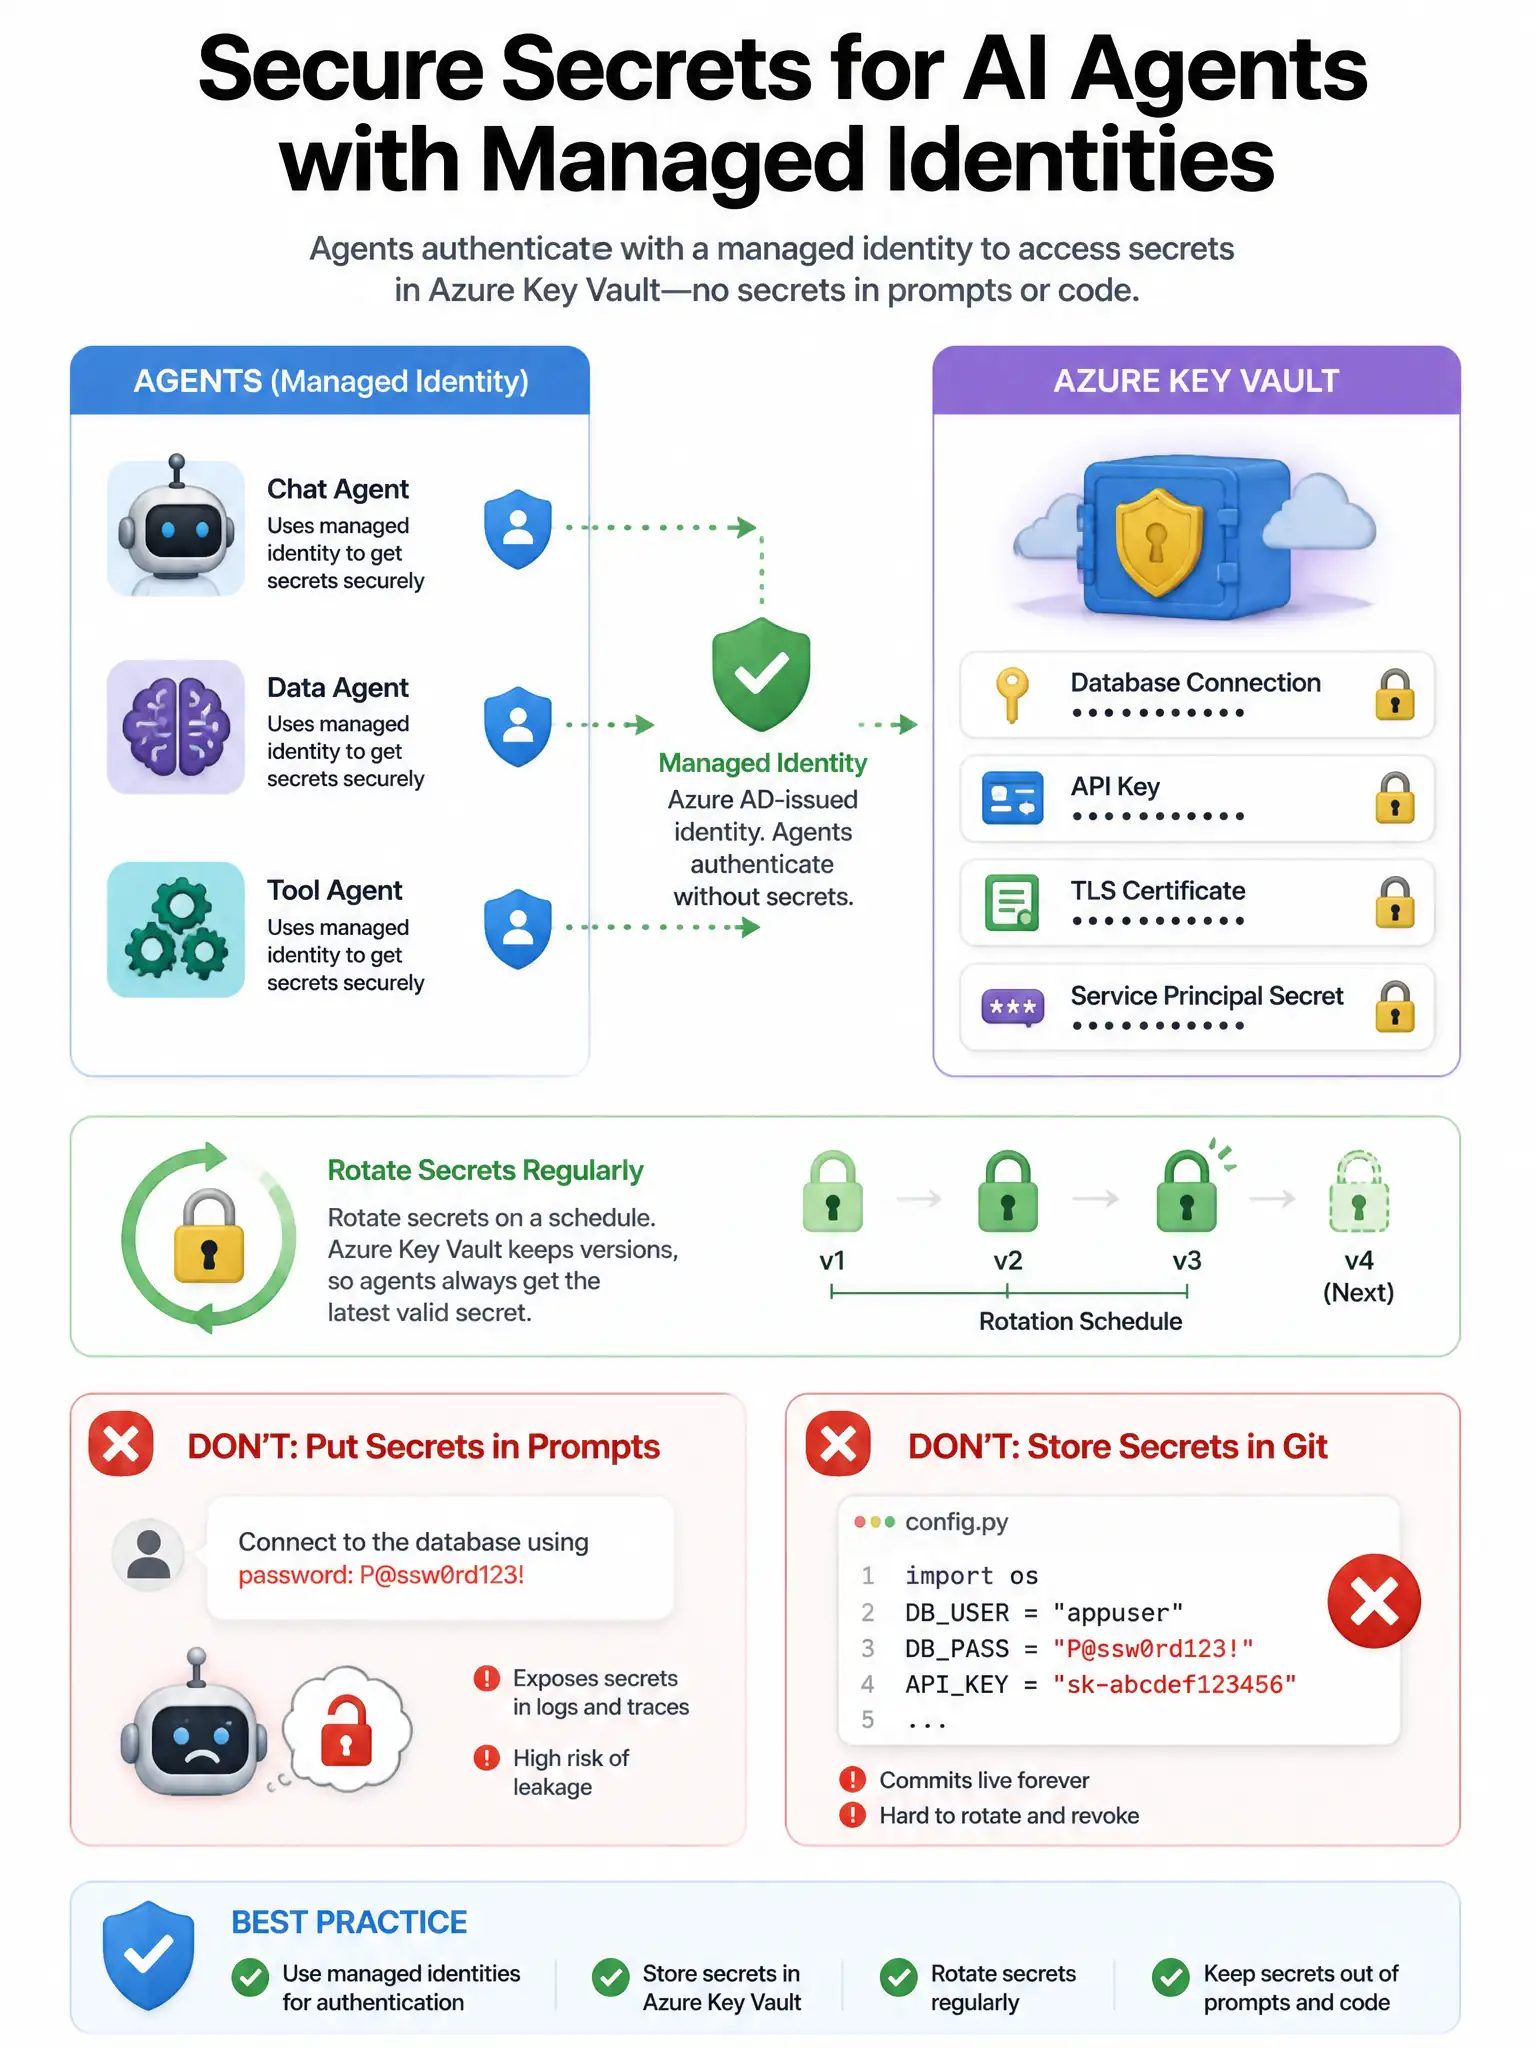
Short Explanation
You want Azure Key Vault as the secrets plane for multi-agent solutions: certificates and keys stay encrypted at rest, access is role-based per identity, and rotation can be automated. Agents with managed identities pull only the secrets they need at runtime over HTTPS. Git-based .env files, broad App Configuration Contributor access, and keys in prompts all fail compliance and leak secrets.
Full Explanation
The AI-500 skills measured explicitly call out secrets management with Azure Key Vault: secrets, certificates, key rotation, role-based access to secrets, and encryption. Production multi-agent systems should never treat prompts, Git, or flat config as the system of record for credentials. With managed identities, agents authenticate to Key Vault without embedded vault keys. Scope each identity to specific secret names or prefixes, using get/list rather than set/delete unless the agent must write, and retrieve secrets at runtime over HTTPS. Enable rotation and dual-version windows so tools can refresh without downtime. The encrypted .env files in a private Git repository with a hard-coded passphrase fail audit and rotation requirements. Placing secrets in Azure App Configuration without Key Vault references and granting all agents Contributor confuses configuration with secrets governance and grants write-capable roles too broadly. Embedding shipping API keys in system prompts is an anti-pattern that guarantees secret exposure in observability pipelines. Layer Key Vault references from App Service or Container Apps when useful, but keep the vault as the authoritative store and audit secret access with diagnostic logs.