
A city SRE must confirm Foundry-dependent model endpoints are reachable only through the private network before go-live. What should they validate?
Select an answer to reveal the explanation.
Short Explanation
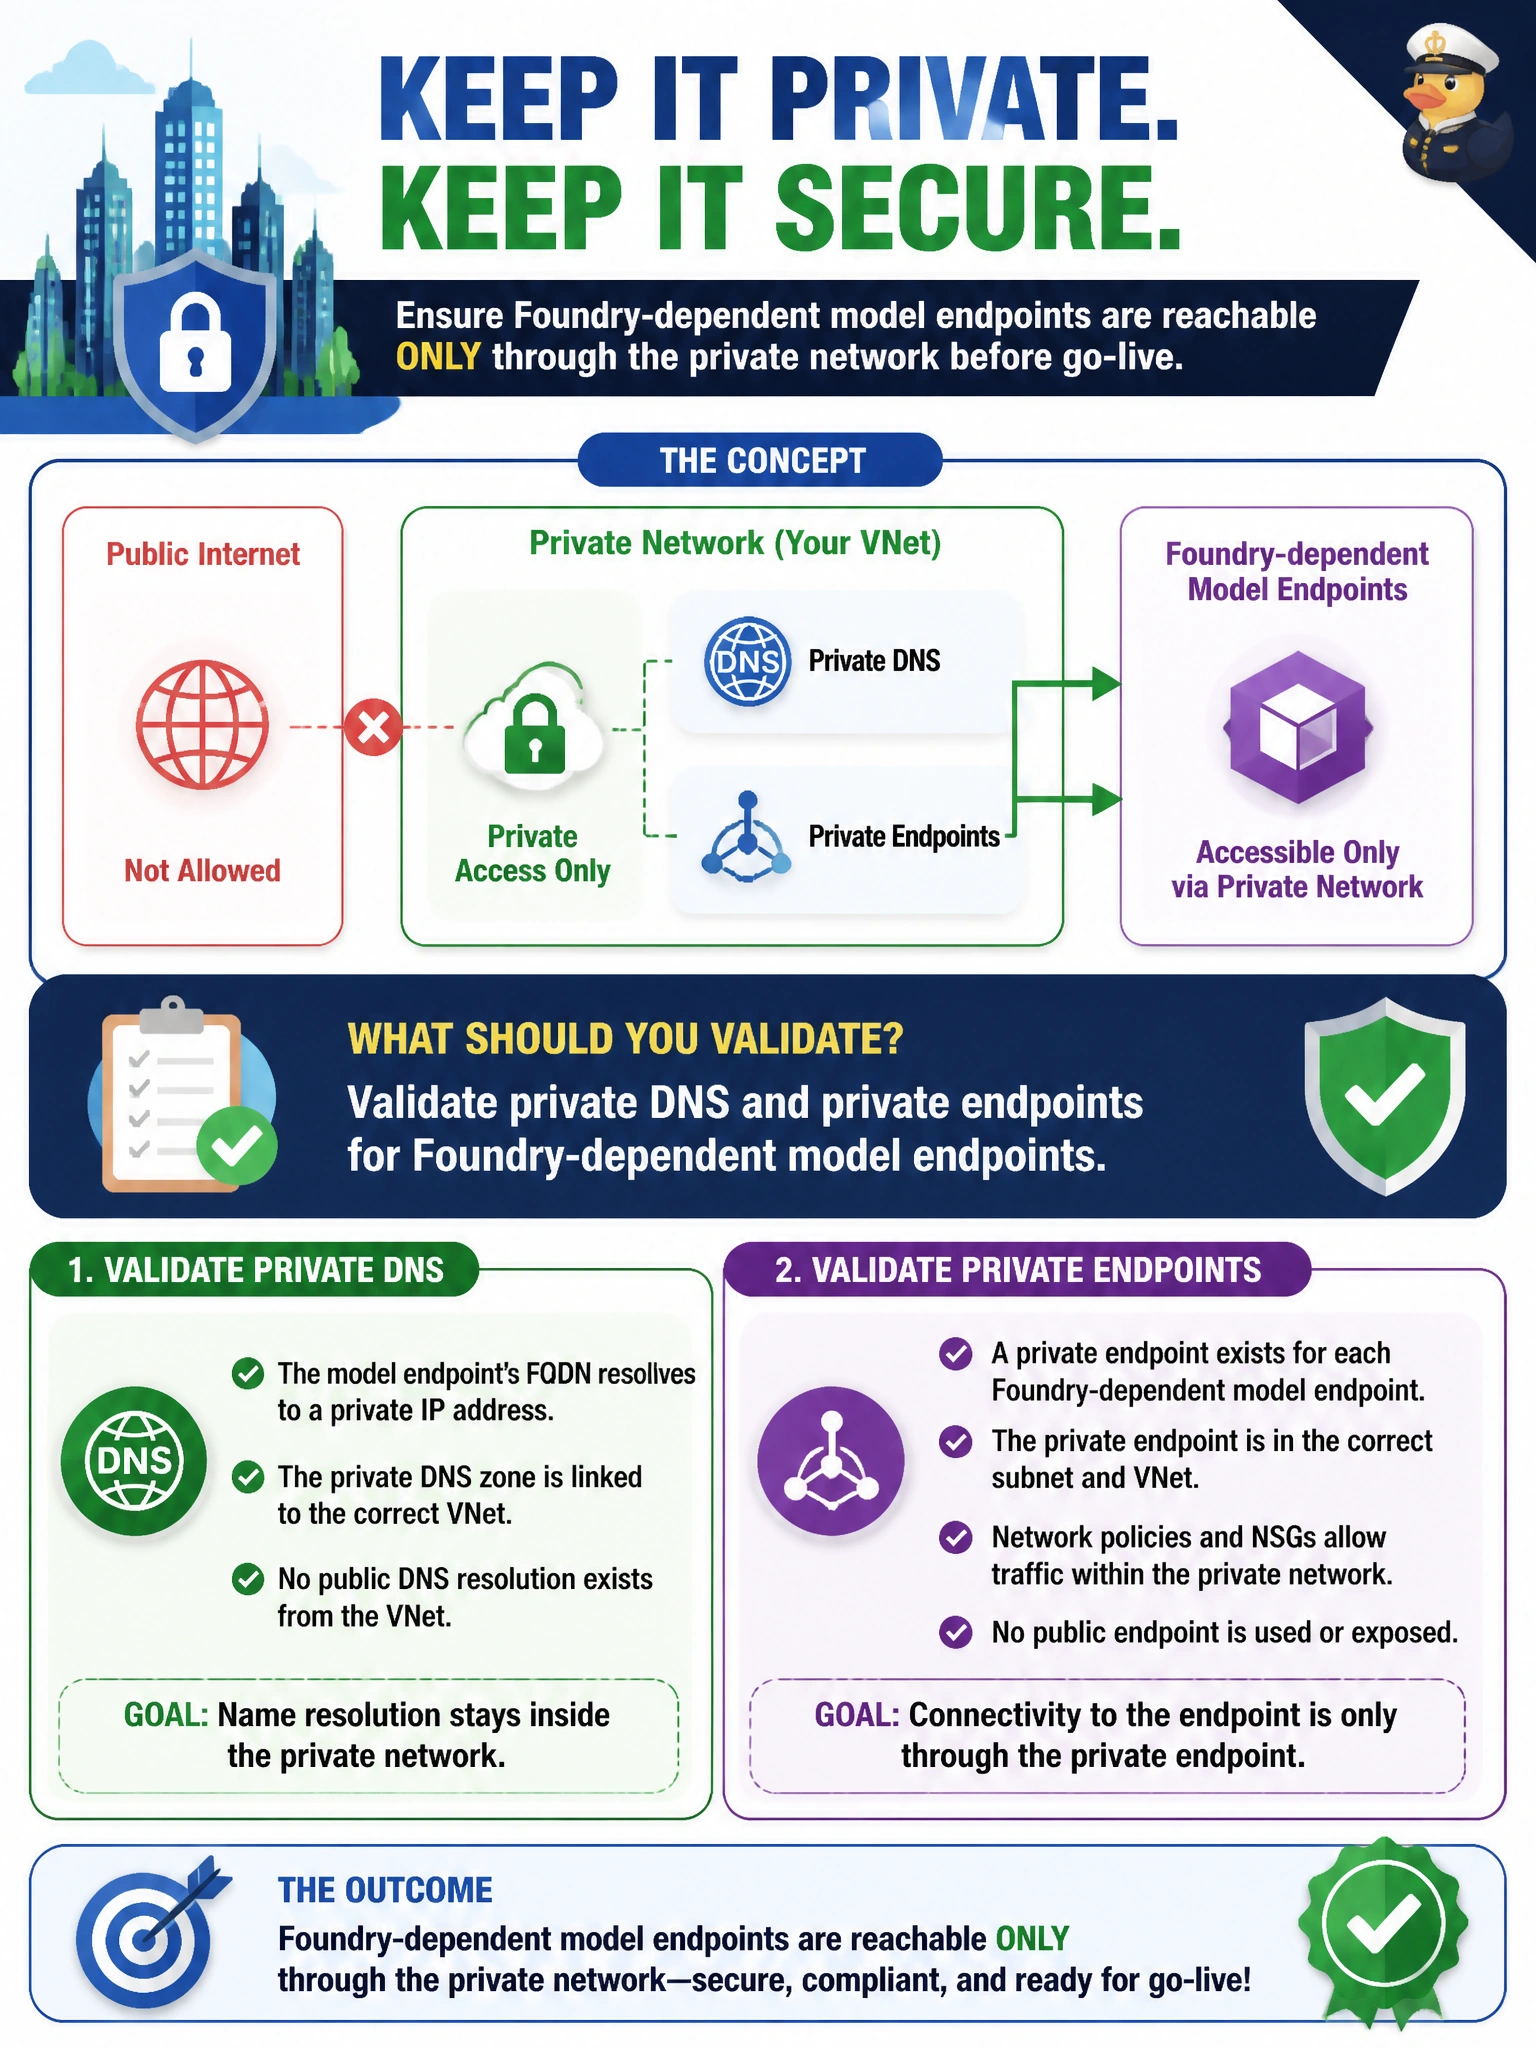
Go-live is not the time to discover DNS still points at the public front door. Validate private endpoints and private DNS before residents show up.
Full Explanation
Validating private DNS and private endpoints for Foundry-dependent model endpoints is the correct pre-go-live check for a city SRE confirming reachability only through the private network. Private endpoints place the model/Foundry-dependent service on a private IP in the civic VNet, and private DNS zones ensure names resolve to those private addresses instead of public fronts. SRE validation should prove resolution from approved networks, deny or fail public paths as intended, and confirm dependent agents and apps use the private names before residents are cut over.
Validating private DNS and service endpoints for Foundry-dependent model endpoints fails because service endpoints extend VNet identity to the service without placing the endpoint on a private IP or closing the public front door, so even with private DNS entries you cannot prove traffic stays private-only or that public paths are blocked. Validating private endpoints and VNet peering for Foundry-dependent model endpoints fails because peering only provides routing between VNets and does not prove names resolve to the private endpoint IPs or that public access is denied, so it cannot confirm exclusive private-network reachability. Validating private DNS and firewall rules for Foundry-dependent model endpoints fails because firewall rules can restrict source access but without validating the private endpoint itself you have not proven the model is reachable on a private IP only through the private network or that the intended private path actually works.
Exam caveat: private DNS with firewall rules that filter sources does not prove traffic stays off the public internet; private DNS and private endpoints must still be validated for a private-only go-live. On exam items that mention "reachable only through the private network," look for private DNS + private endpoints rather than private endpoints with only VNet peering that lacks proof of private name resolution and closed public paths.
Operational check: from an approved jump host or subnet, resolve the model endpoint FQDN to a private IP, confirm connectivity through the private endpoint, and verify that public or off-VNet clients cannot reach the production endpoint intended for go-live.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.