
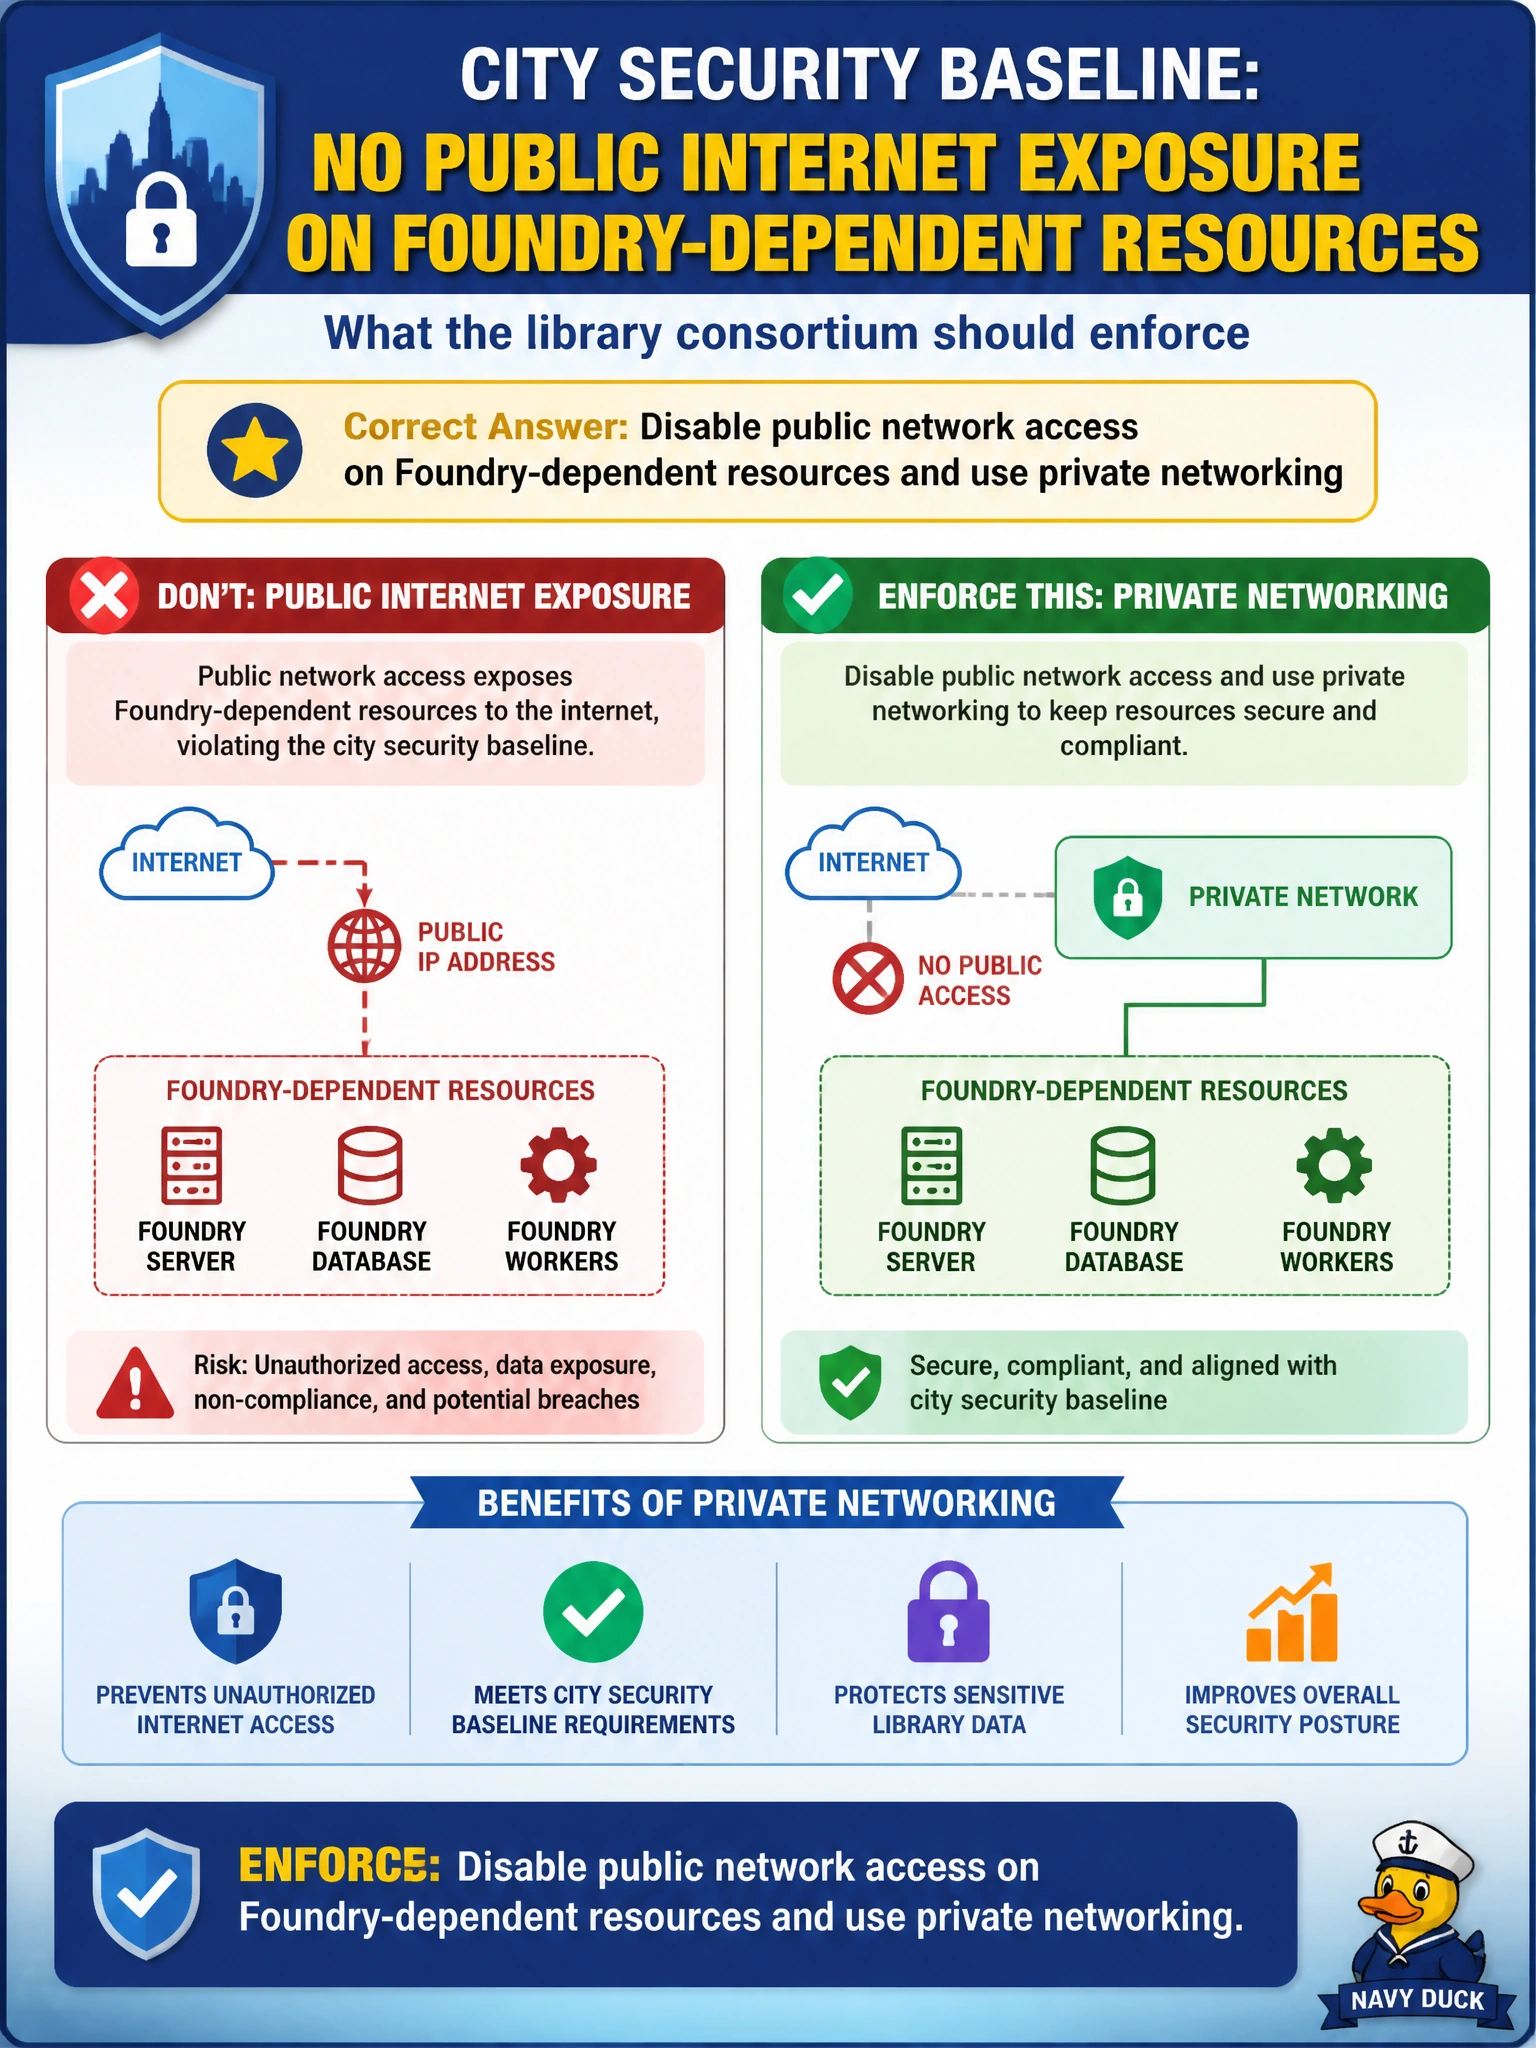
A library consortium must meet the city security baseline that forbids public internet exposure on Foundry-dependent resources. What should they enforce?
Select an answer to reveal the explanation.
Short Explanation
If the city says no public hangout for Foundry, flip public access off and go private. You'll still come up short with service endpoints because they're not private networking.
Full Explanation
Disabling public network access on Foundry-dependent resources and using private networking is the correct enforcement for a library consortium bound by a city security baseline that forbids public internet exposure. Municipal GenAIOps commonly places Azure AI Foundry-related endpoints, dependent model hosting, and supporting services behind private endpoints, private DNS, and VNet integration so library GenAI traffic stays on approved civic networks. Turning public network access off removes the internet-facing control plane/data plane paths that conflict with the baseline while still allowing authorized campus and hub connectivity through private paths. Disabling public network access on Foundry-dependent resources and using service endpoints fails because service endpoints keep traffic on the Azure backbone but do not provide private networking with private endpoints and private DNS, which the baseline posture requires. Disabling public network access on Foundry-dependent resources and using Entra identity protection fails because Entra identity protection addresses identity risk, not private connectivity, so it does not satisfy the private networking requirement. Disabling public network access on Foundry-dependent resources and using Firewall service tags fails because Firewall service tags only scope firewall allowlisting and do not establish private networking with private paths. Exam caveat: “Disable public network access + private networking” is the posture; private endpoints and private DNS are the usual implementation details. On scenario questions, pick the private-access answer when the stem cites a baseline that forbids public internet exposure on Foundry-dependent resources. Operational check: confirm public network access is disabled on the relevant Foundry-dependent resources, private endpoints and private DNS resolve correctly from library networks, and unauthorized public clients cannot reach the endpoints while approved private paths still succeed.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.