
Production agent credentials live in Key Vault and must survive accidental deletion. Which protection should be enabled?
Select an answer to reveal the explanation.
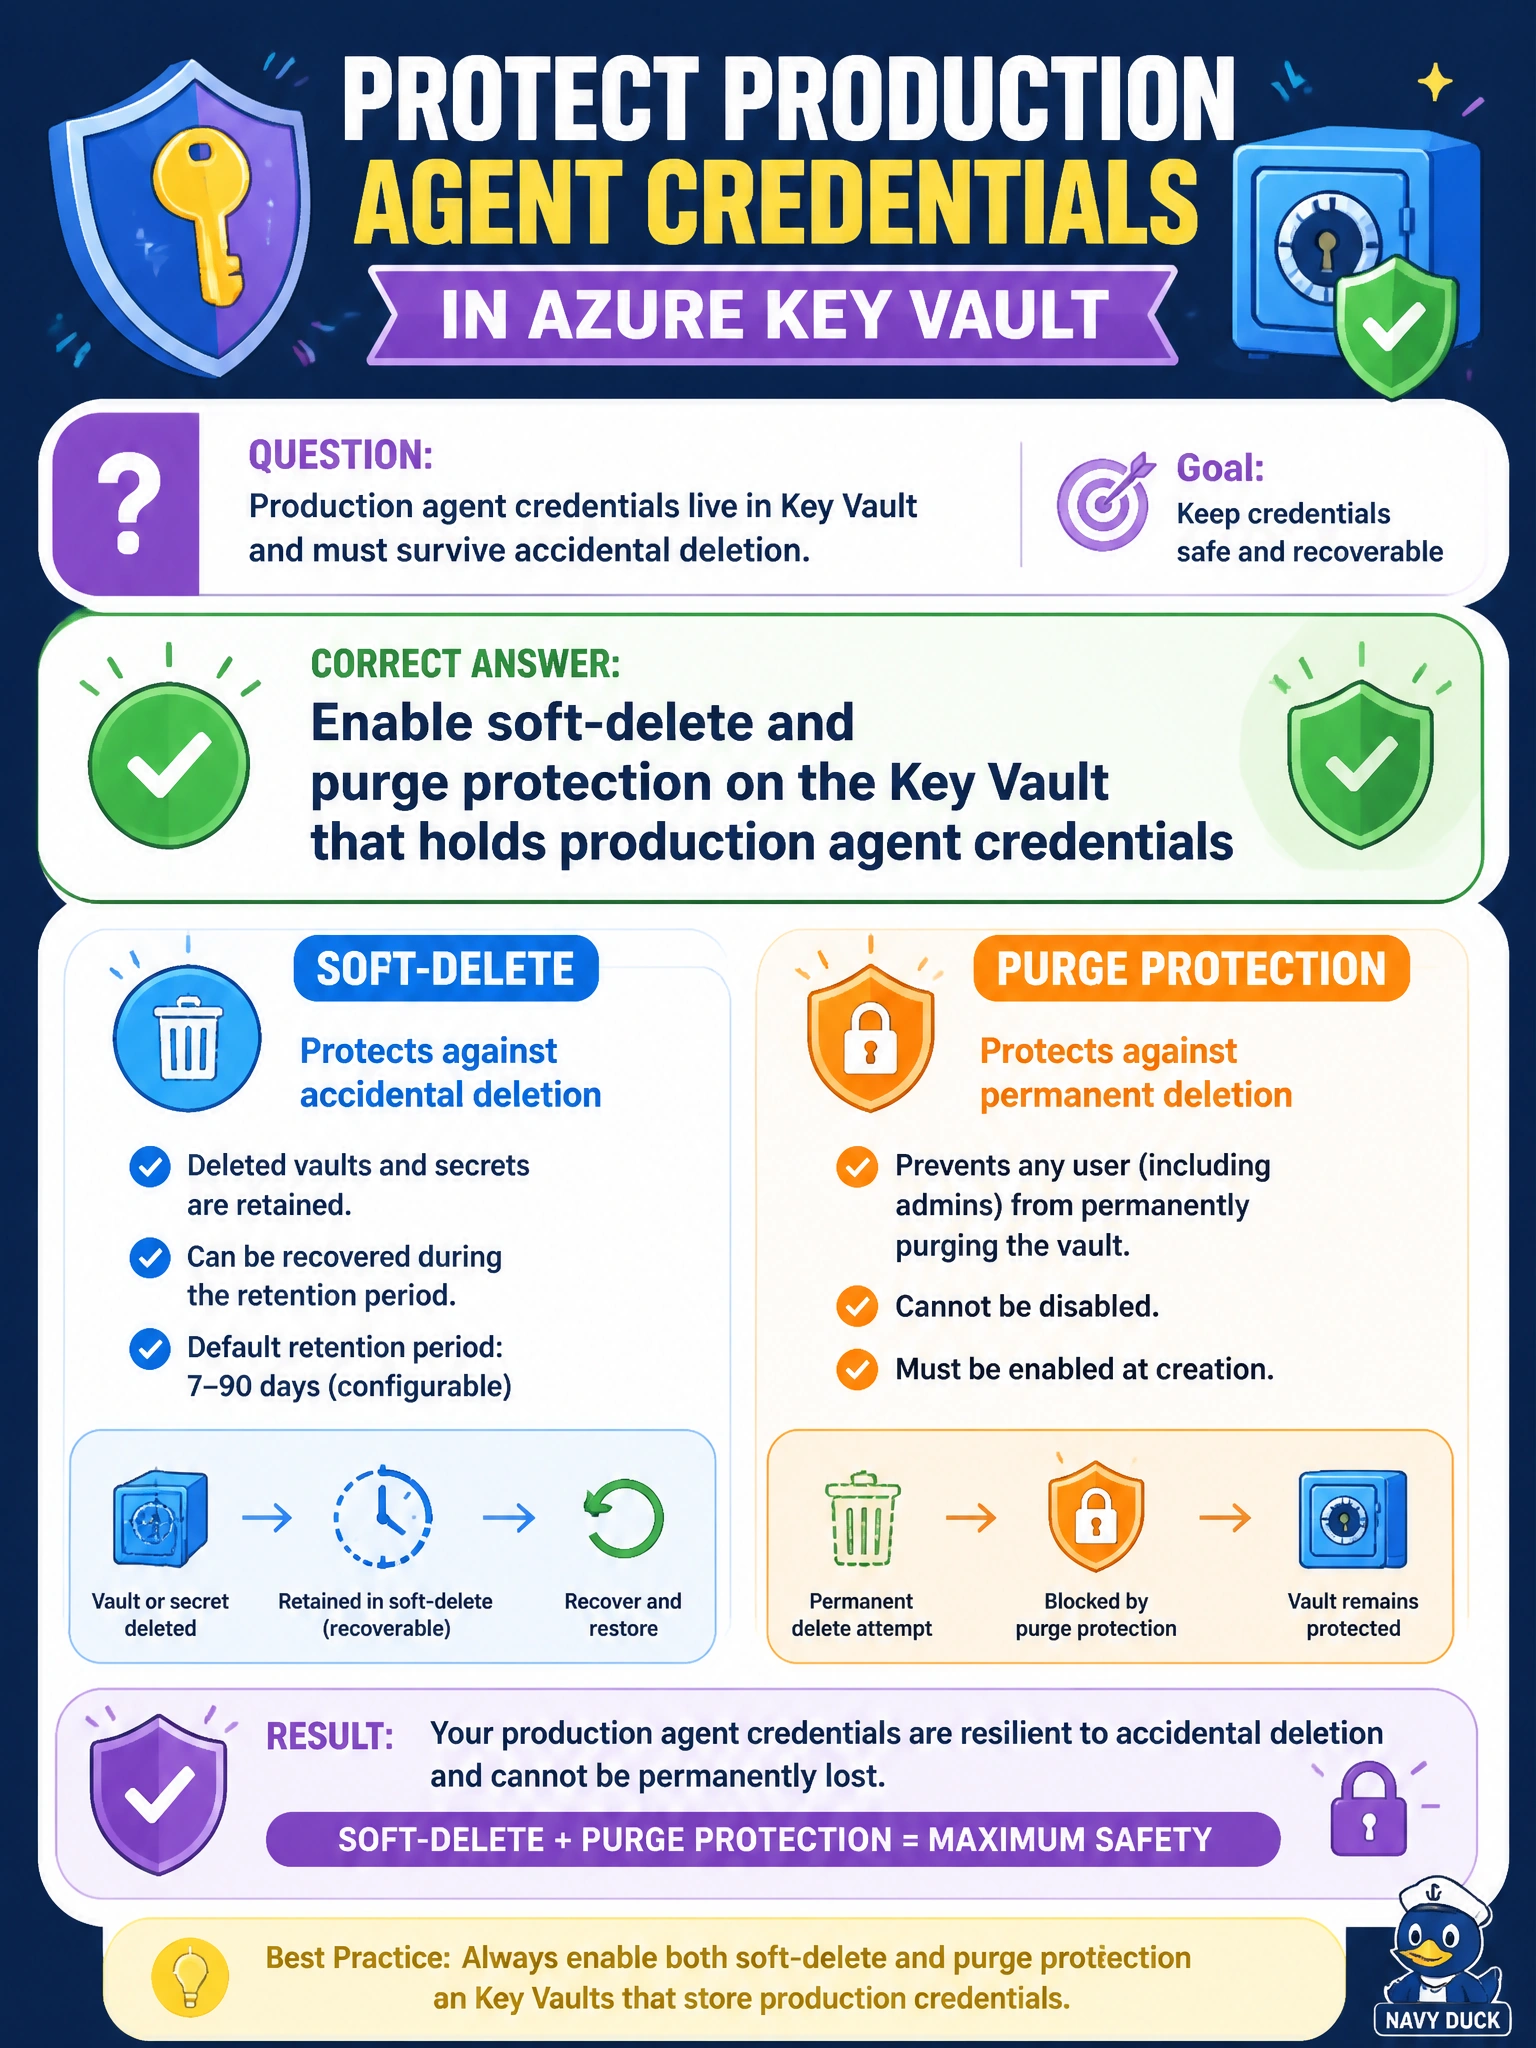
Short Explanation
Soft-delete plus purge protection is the municipal recycle bin with a lock—someone can empty the trash, but not permanently until the retention window passes.
Full Explanation
Production agent credentials in Key Vault must survive accidental deletion, which is exactly what soft-delete plus purge protection provide. Soft-delete retains deleted vaults and secret objects for a recoverable retention window so municipal operators can restore after a mistaken portal click or automation bug. Purge protection prevents permanent purge of those soft-deleted objects until the retention period expires, blocking attackers or rushed admins from immediately erasing recovery paths. Together they give the city a locked recycle bin for AI agent secrets rather than irreversible loss.
Turning off all recovery features so deleted secrets vanish immediately fails the survival requirement: there is no restore path when an operator deletes the wrong secret name during an incident. Storing only a screenshot of secret values in a shared mailbox fails as a control—screenshots are not rotatable secrets, mailboxes lack Key Vault’s access model and versioning, and OCR or forward history spreads credentials. Mirroring production secrets into an unsecured public blob container for ‘backup’ fails confidentiality: a public blob is a leak, not a backup, and it bypasses Key Vault’s RBAC and purge protections entirely.
Exam caveat: soft-delete is often enabled by default on newer vaults, but purge protection is an explicit choice and can be irreversible for the vault’s lifetime—know the difference. Soft-delete alone still allows privileged purge; purge protection is what blocks that until retention ends. Recovery also depends on having roles that can recover objects, not only delete them.
Operational check: in a non-production vault, delete a test secret, confirm it appears as soft-deleted, verify purge is denied while purge protection is on, restore the secret, and confirm the production agent identity can again resolve the credential without redeploying plaintext copies.