
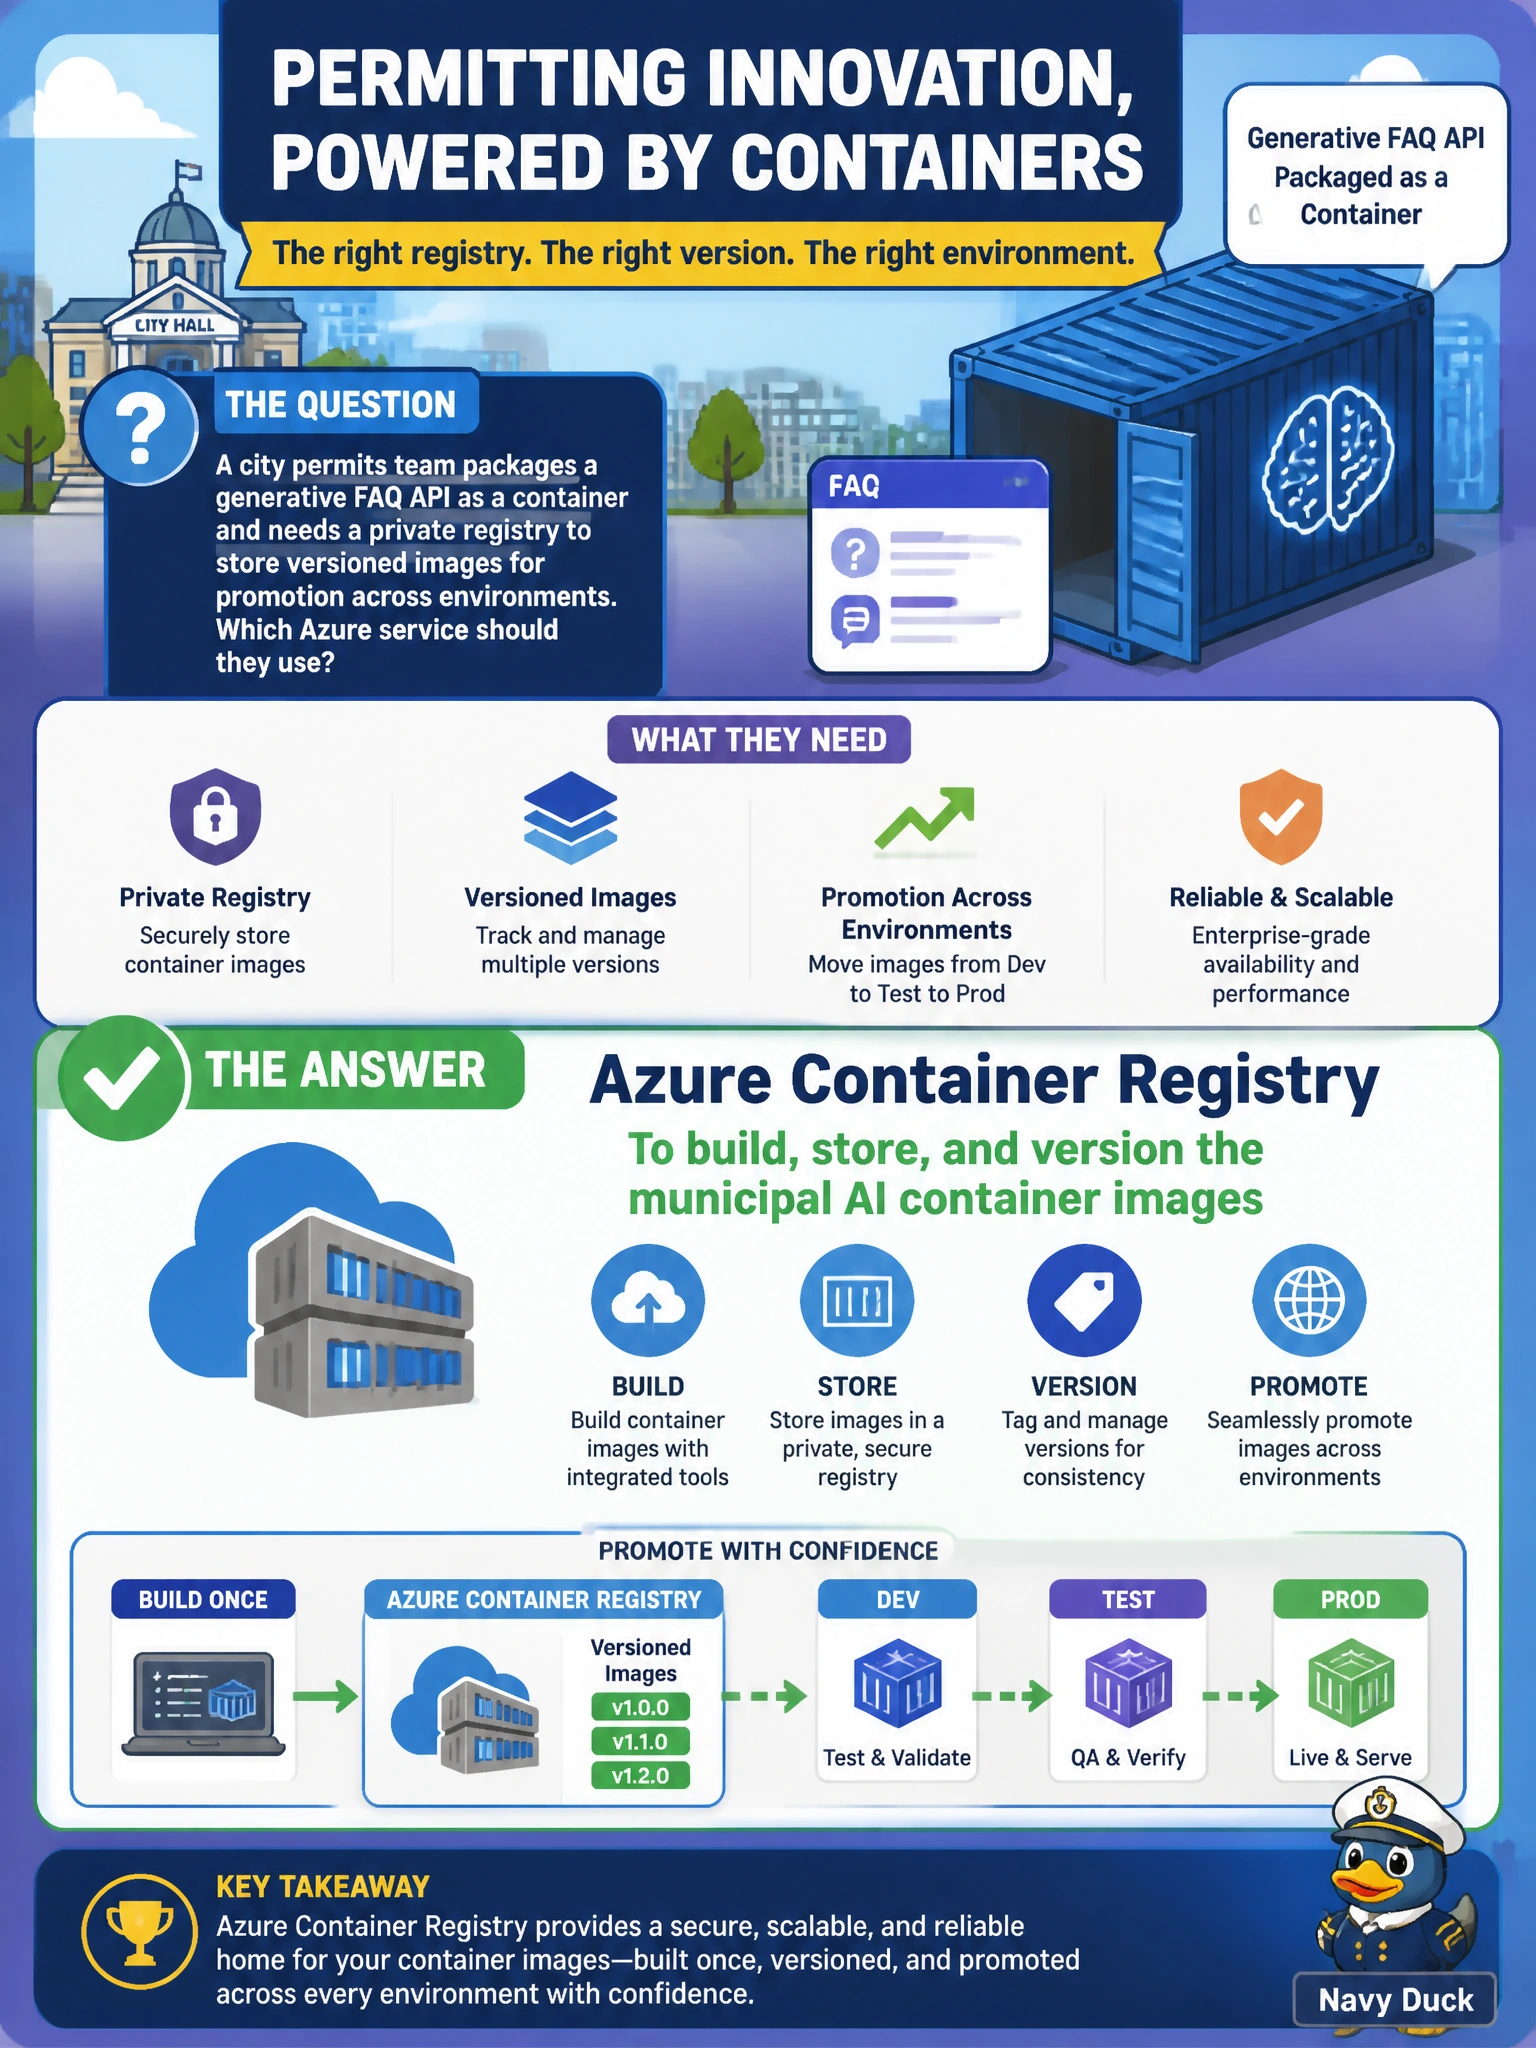
A city permits team packages a generative FAQ API as a container and needs a private registry to store versioned images for promotion across environments. Which Azure service should they use?
Select an answer to reveal the explanation.
Short Explanation
Think of Azure Container Registry (ACR) as your city’s private warehouse for container images, rather than public storage or an archive share. You can tag the permits FAQ image there and have staging and production pull the same versioned image instead of relying on mystery builds.
Full Explanation
Azure Container Registry (ACR) is Azure’s private registry for storing, tagging, and promoting container images across environments. For the city permits team’s generative FAQ API, it supports authenticated push and pull, image tags and digests, and a consistent source for development, staging, and production. You can build or publish a versioned image, then promote the same digest without rebuilding, helping make deployments reproducible and auditable. Azure Blob Storage with public read access is object storage for image tarballs, not a private OCI registry with authenticated pulls, manifests, and registry-style image references. Azure Files can hold exported image archives, but an archive share is not a private registry that provides versioned container images for promotion. Azure CDN with anonymous pull would distribute images without registry authentication, undermining confidentiality and supply-chain control for private municipal workloads. Exam caveat: ACR stores the image; it does not host the FAQ API, which still needs a compute target that pulls from the registry. Geo-replication, retention policies, and content trust are related ACR features, not requirements for identifying the registry. Practical check: verify the image has a pinned tag or digest in ACR, that each environment’s deployment identity has AcrPull, and that deployments reference that pinned image rather than an unauthenticated archive.