
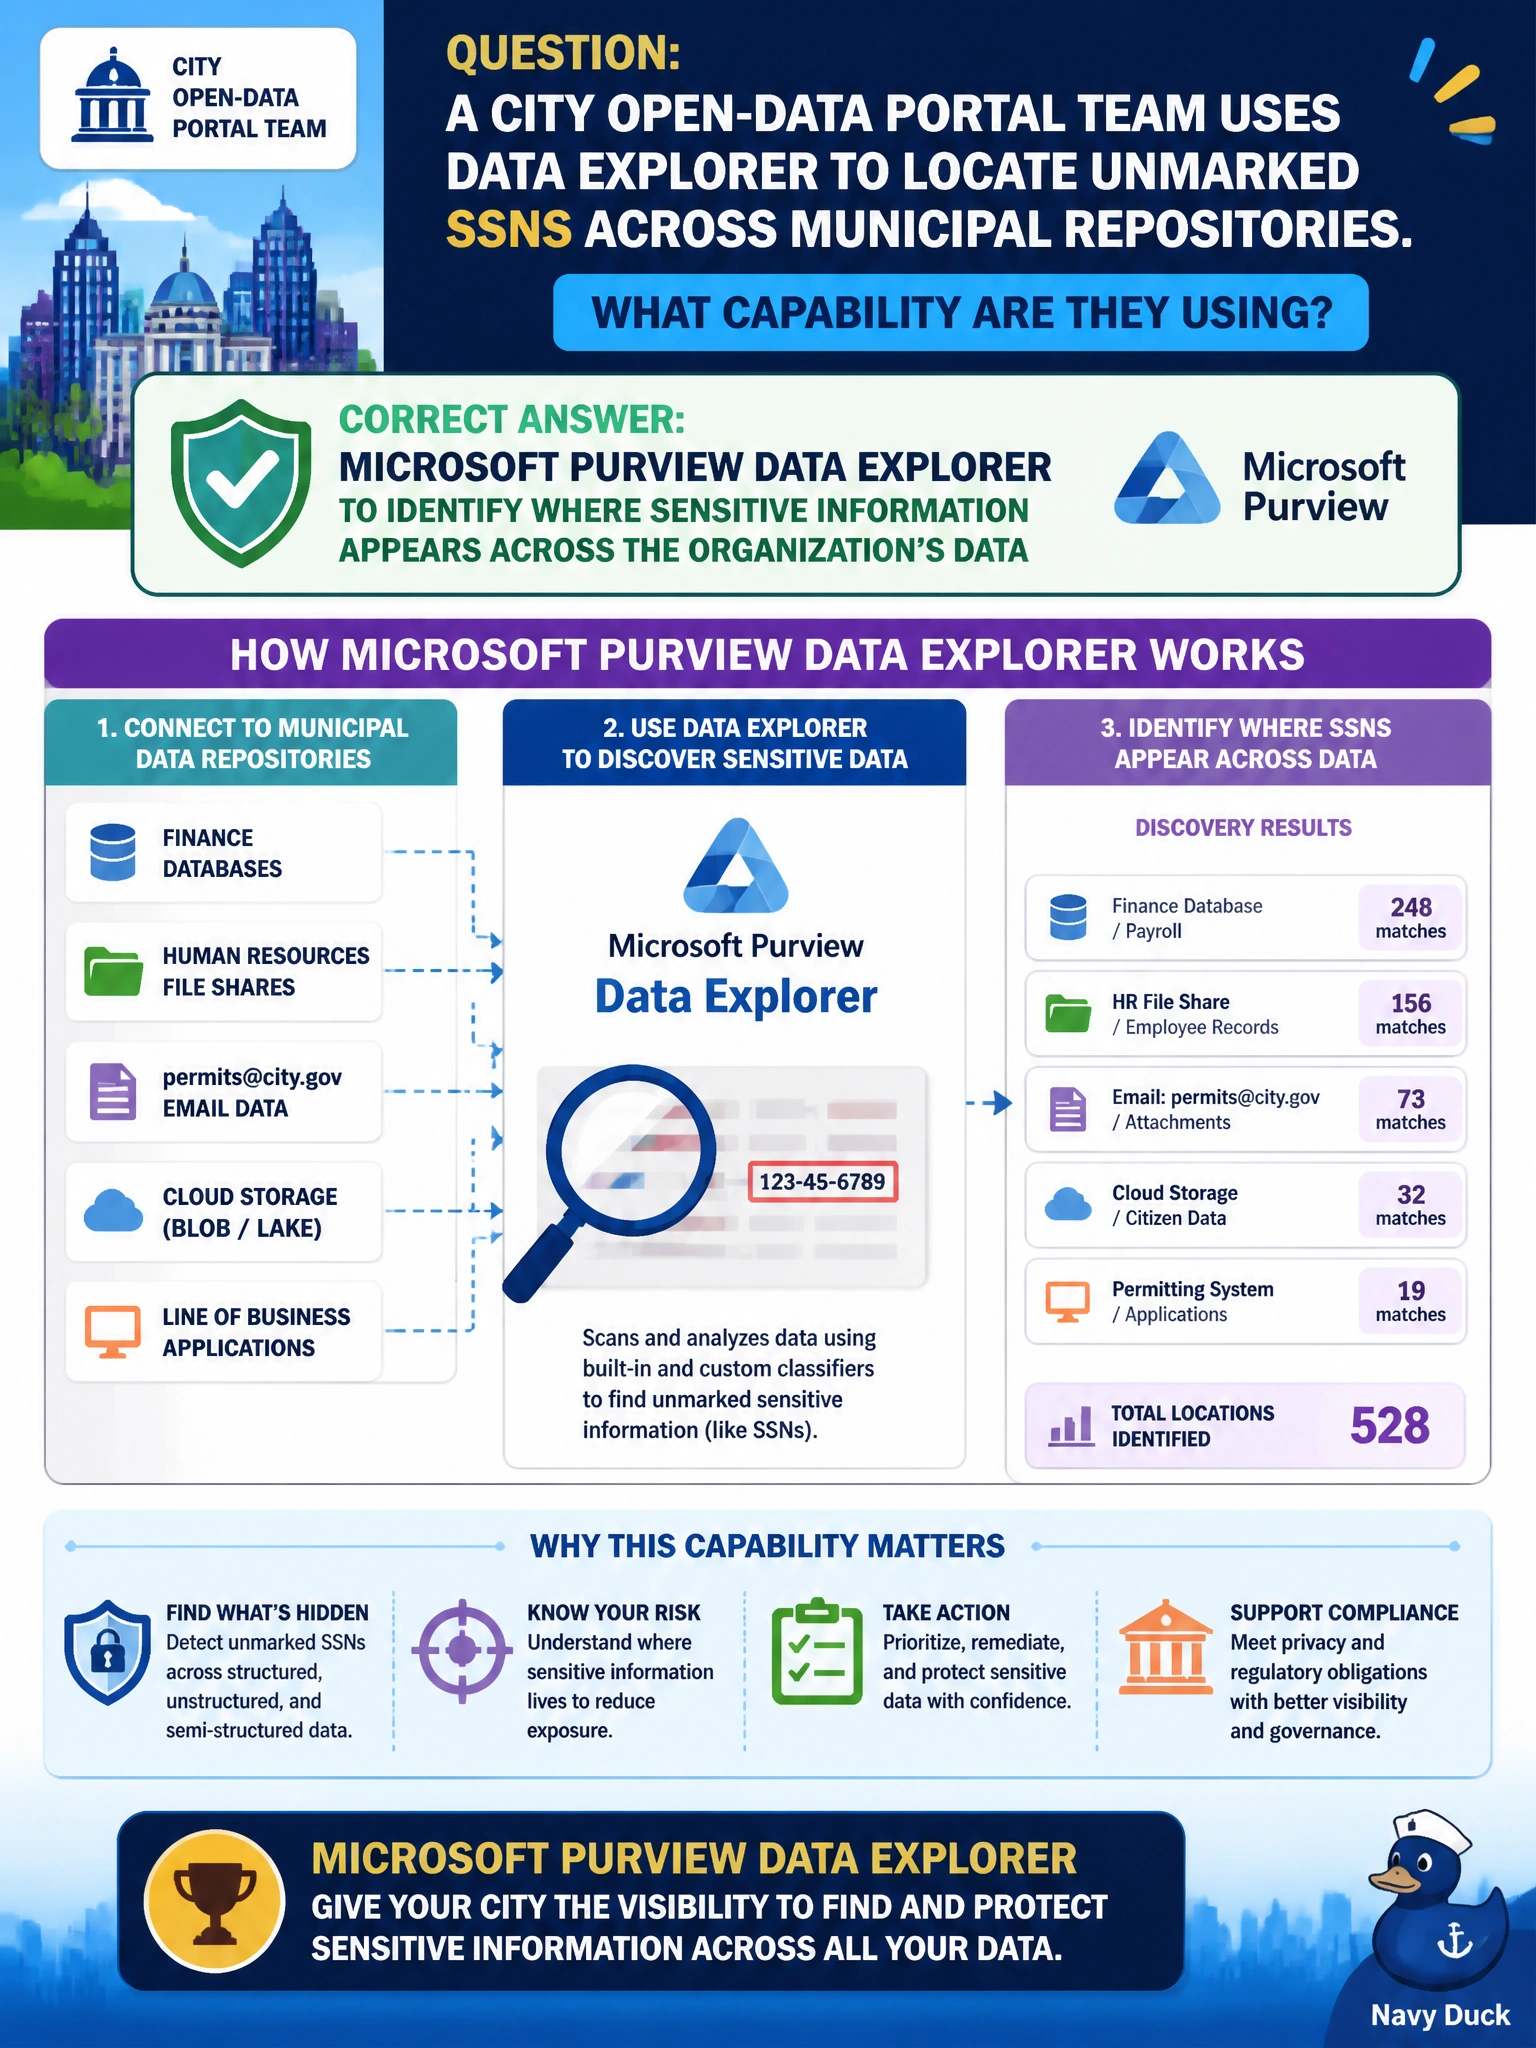
A city open-data portal team uses Data Explorer to locate unmarked SSNs across municipal repositories. What capability are they using?
Select an answer to reveal the explanation.
Short Explanation
Data Explorer is the ‘where did unmarked SSNs hide?’ flashlight across municipal repos. It isn't your tool for blocking external sharing when sensitive info is found, calculating compliance scores, or surfacing portal content through managed properties and result sources. Find the sensitive stuff first, then protect it.
Full Explanation
When a city open-data portal team uses Data Explorer to locate unmarked SSNs across municipal repositories, they are using Microsoft Purview Data Explorer to identify where sensitive information appears across the organization’s data. Discovery of unmarked identifiers is a governance prerequisite: you cannot label, DLP-protect, or responsibly expose open-data assets until you know where sensitive values actually live in SharePoint, OneDrive, Exchange, and related repositories.
Microsoft Purview Data Explorer to block external sharing when sensitive information is detected in content fails the discovery concept: Data Explorer is read-only visibility into where sensitive data lives, not an enforcement tool that blocks sharing, which is the role of DLP policies. Microsoft Purview Data Explorer to calculate compliance scores for regulatory assessments across the organization fails as a discovery description: calculating compliance scores is Compliance Manager's assessment role, not Data Explorer's capability to show where unmarked SSNs physically live. Microsoft Purview Data Explorer to surface relevant portal content through managed properties and result sources fails both accuracy and purpose: surfacing portal content through managed properties and result sources is a SharePoint search-discovery feature, not sensitive-data discovery, and it is not Data Explorer's role.
Exam caveat: AB-900 expects identify-level recognition of Data Explorer for finding where sensitive information appears. Exact UI click-paths and every classifier name are out of scope; knowing discovery precedes prioritization of labeling and protection is in scope.
Operational check: Run or review Data Explorer findings for SSN (or equivalent) classifiers across municipal repositories that feed or sit near the open-data program, inventory high-hit locations, and queue labeling/DLP owners before any broader public dataset refresh that might include unmarked identifiers.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.