
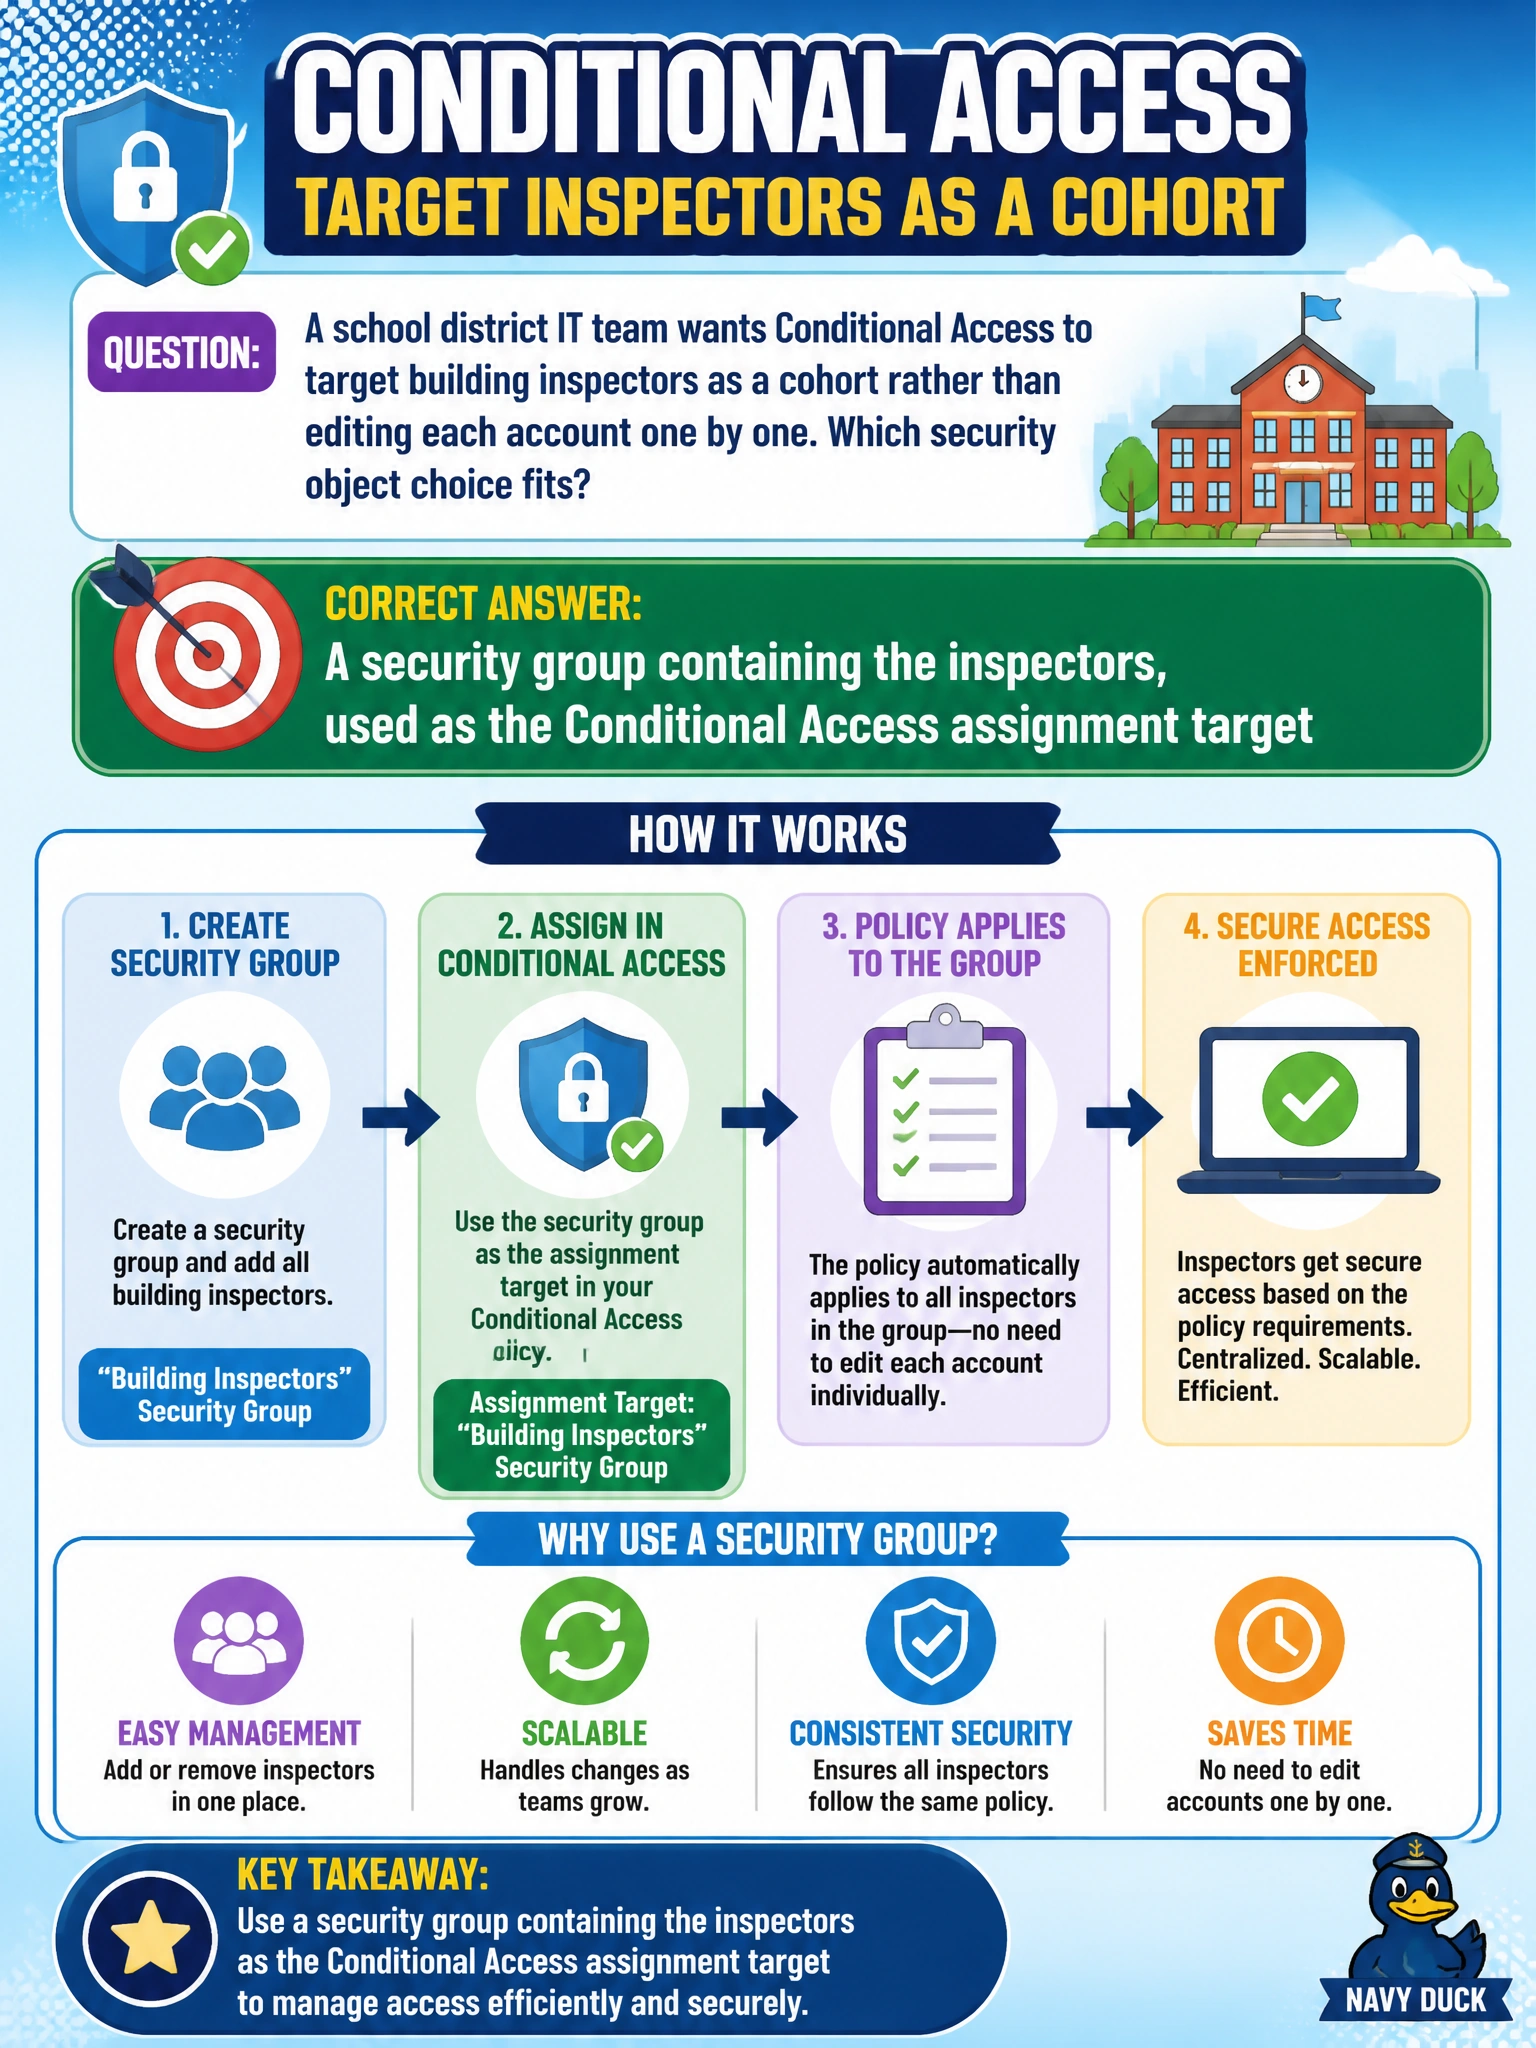
A school district IT team wants Conditional Access to target building inspectors as a cohort rather than editing each account one by one. Which security object choice fits?
Select an answer to reveal the explanation.
Short Explanation
Herding inspectors one account at a time is like rewriting every parking permit by hand. Drop them in a security group and aim Conditional Access at the group. You'll miss if you target a distribution group, a Microsoft 365 group, or an administrative unit since distribution groups can't enforce CA, Microsoft 365 groups add collaboration baggage you don't need, and administrative units only scope admin delegation.
Full Explanation
Users and groups are core security objects in Microsoft 365 identity administration. Placing building inspectors in a security group and using that group as the Conditional Access assignment target lets a school district IT team apply policy to the cohort without editing each account one by one. Group-based targeting scales municipal Conditional Access cleanly as inspectors join or leave.
A distribution group containing the inspectors, used as the Conditional Access assignment target fails by concept because distribution groups are mail-enabled, not security-enabled, so Conditional Access cannot select and enforce them as assignment targets.
A Microsoft 365 group containing the inspectors, used as the Conditional Access assignment target fails as fit because it provisions collaboration workloads like Teams, SharePoint, and mailbox when only security scoping is needed, while a security group provides cohort Conditional Access without that extra footprint.
An administrative unit containing the inspectors, used as the Conditional Access assignment target fails because administrative units define delegated administrative scope, not security principals that Conditional Access evaluates for user assignment.
Exam caveat: Fundamentals items test choosing the right object for security scoping—security groups for cohort Conditional Access—not building every policy condition. Distribution groups, Microsoft 365 groups, and administrative units used as Conditional Access assignment targets remain non-answers for security-scoped cohort Conditional Access because distribution groups can't be enforced, Microsoft 365 groups add unneeded collaboration footprint, and administrative units only scope delegation. Keep inspectors in maintainable groups.
Operational check: Create or reuse a security group for building inspectors, assign the Conditional Access policy to that group, add a test inspector account to the group and confirm the policy applies, remove the account and confirm targeting stops. Verify a distribution group used as the Conditional Access assignment target, a Microsoft 365 group used as the Conditional Access assignment target, and an administrative unit used as the Conditional Access assignment target were not selected, since only the security group gives correct cohort enforcement without mail-only limits, extra collaboration, or delegation-scope mismatch.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.