
Pinnacle Staffing Solutions has hired 50 contract workers for a 90-day software development project. These contractors need access to a specialized AI coding agent within Microsoft 365 for the duration of the project only. After 90 days, their access should automatically expire without manual intervention. Which approach should the administrator use?
Select an answer to reveal the explanation.
Short Explanation
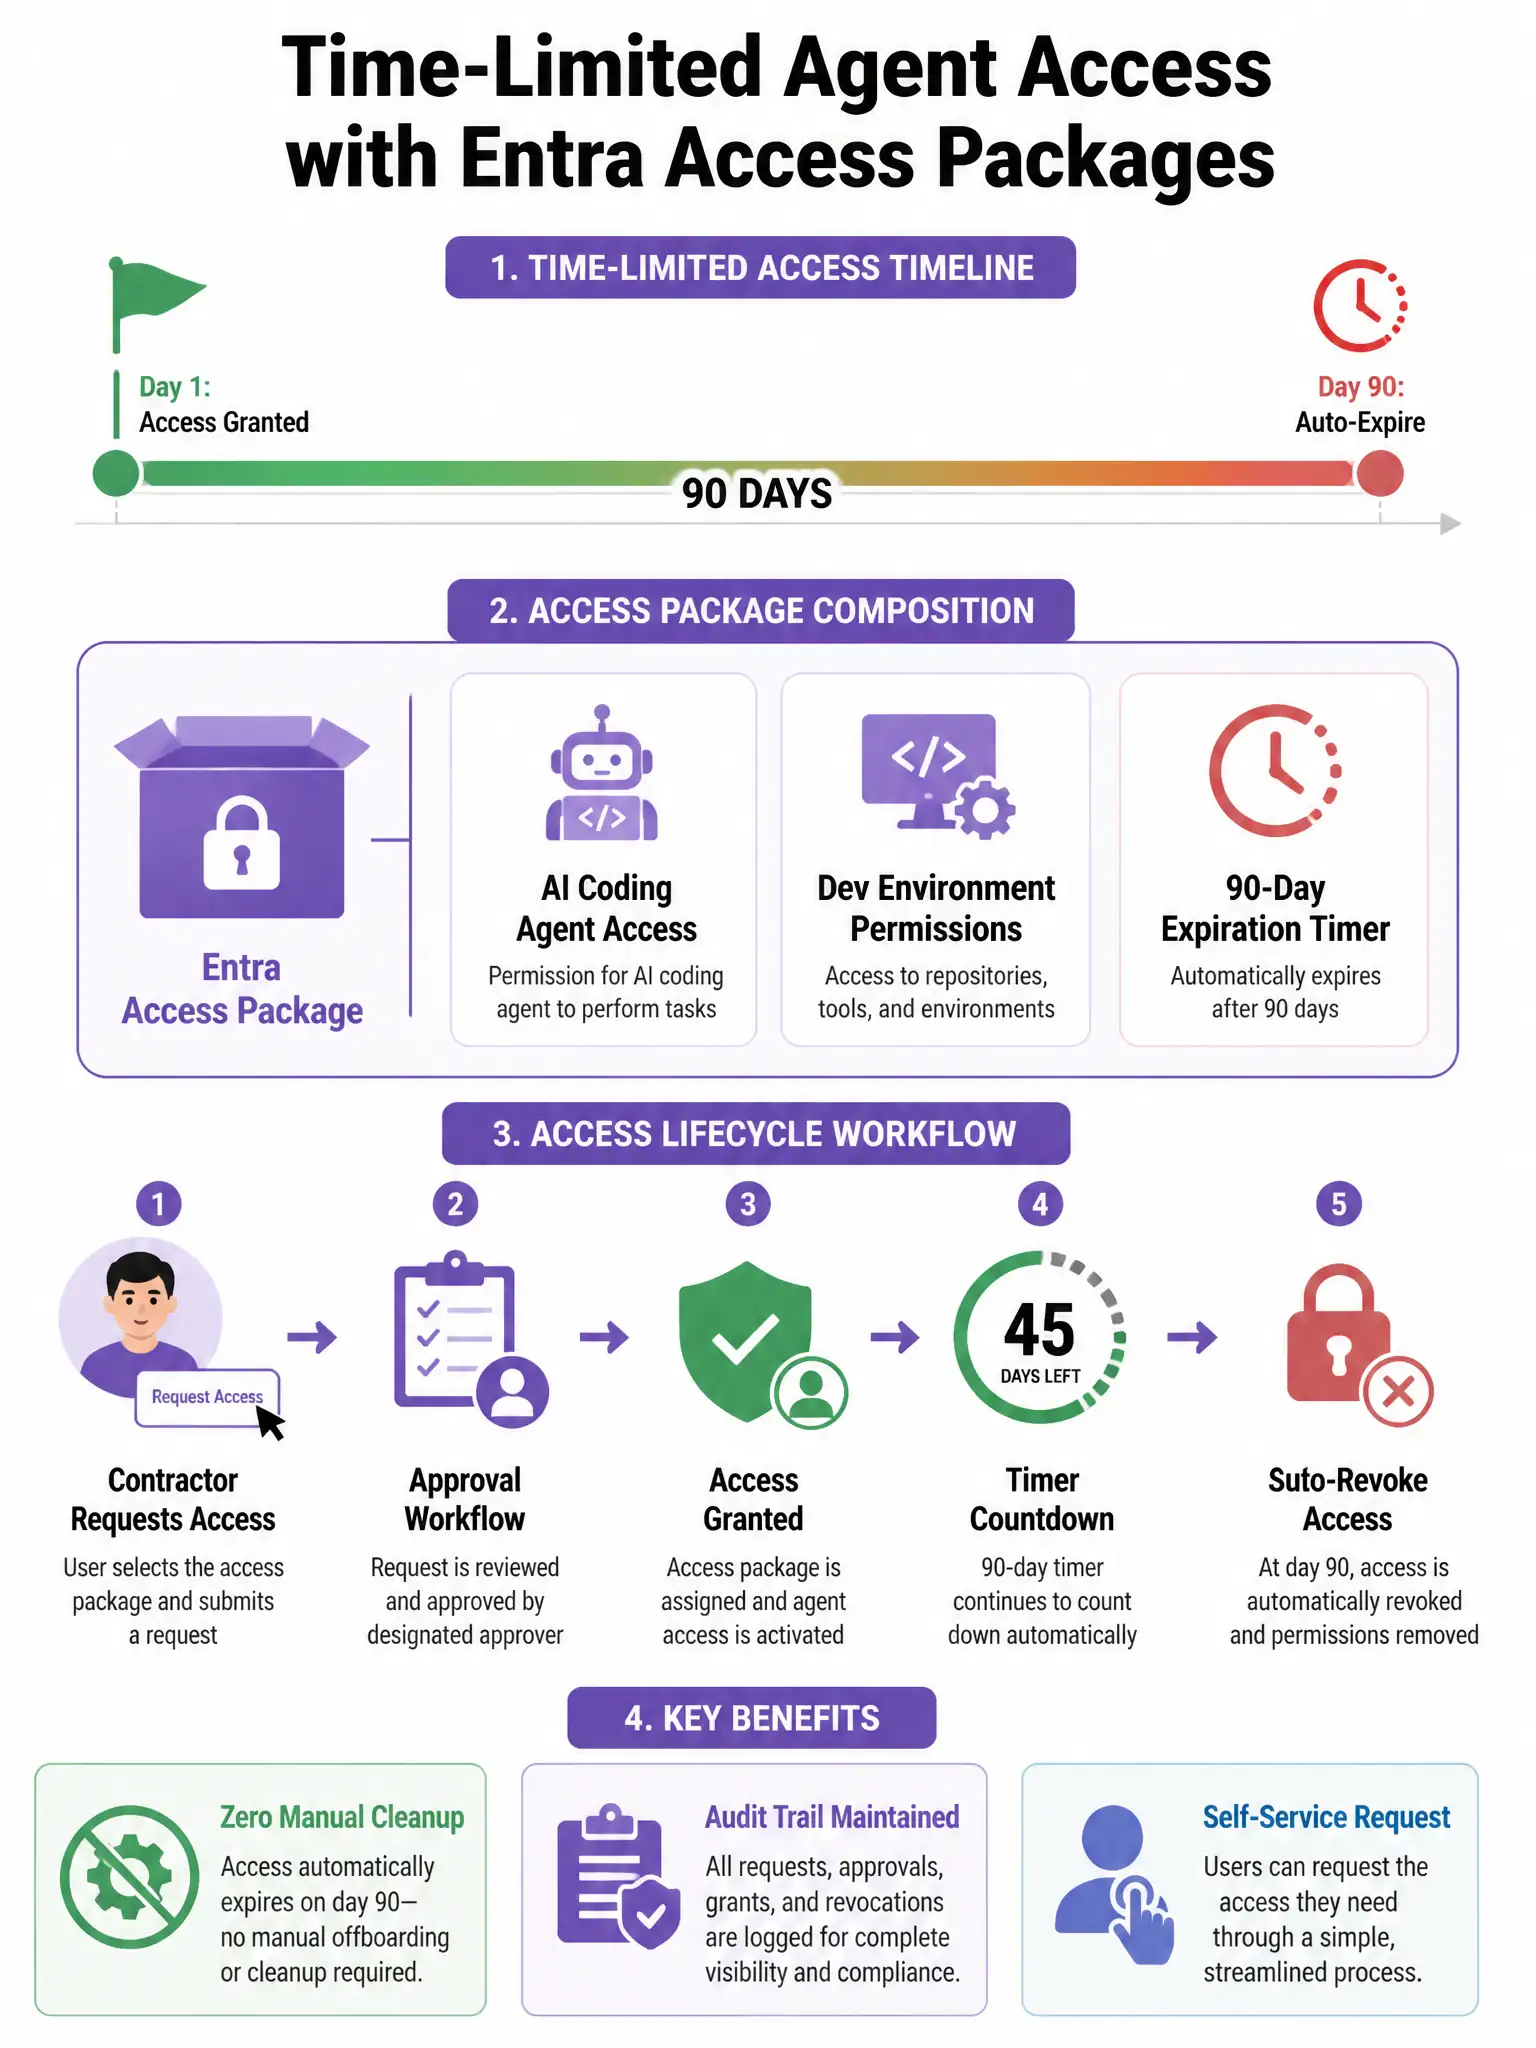
You need an Entra access package that bundles the agent access and expires in 90 days. Contractors request it, and access goes away automatically when the project ends. No manual cleanup or lingering contractor accounts.
Full Explanation
Microsoft Entra Identity Governance access packages allow administrators to bundle resources (including access to AI agents and other applications) into a package with defined eligibility criteria, approval workflows, and expiration policies. By creating an access package that includes the coding agent access, requiring contractors to request it, and setting a 90-day maximum duration, contractors' access automatically expires at the project end date without any manual administrator action. This is the designed Microsoft solution for time-limited access to specific resources.
The manual security-group approach is incorrect because manually adding contractors to a security group that grants agent access, then setting a calendar reminder to remove them after 90 days, is an unreliable, human-error-prone process. If the reminder is missed or the administrator is unavailable, contractor access persists indefinitely — exactly the type of security exposure that Identity Governance access packages are designed to eliminate.
The Microsoft 365 Copilot license approach is incorrect because assigning Copilot licenses with a subscription end date set to 90 days from the start date does not properly control the requested agent access. Microsoft 365 Copilot licenses govern access to Copilot features broadly; they don't specifically control access to individual AI agents, and license subscription terms are commercial/billing constructs, not access control mechanisms. Even if a license expired, the underlying agent access might persist through group membership.
The time-based Conditional Access approach is incorrect because Conditional Access policies enforce access conditions at sign-in time (device compliance, location, risk level, etc.) but are not designed to implement time-bound access expiration for specific resources. Conditional Access policies don't have a fixed expiration-date mechanism for specific users or resources — that's the domain of Identity Governance.
Exam tip: Entra access packages are the correct answer whenever you see: time-limited access, contractor/temporary worker access, self-service access request with approval, or automatic expiration requirements. These are the four hallmarks of an access package scenario.