
Crestview University's IT governance board has mandated that only IT-approved AI agents may be used within the organization. Users must not be able to create personal agents or use agents from outside the approved list. As the Microsoft 365 administrator, which configuration satisfies this requirement?
Select an answer to reveal the explanation.
Short Explanation
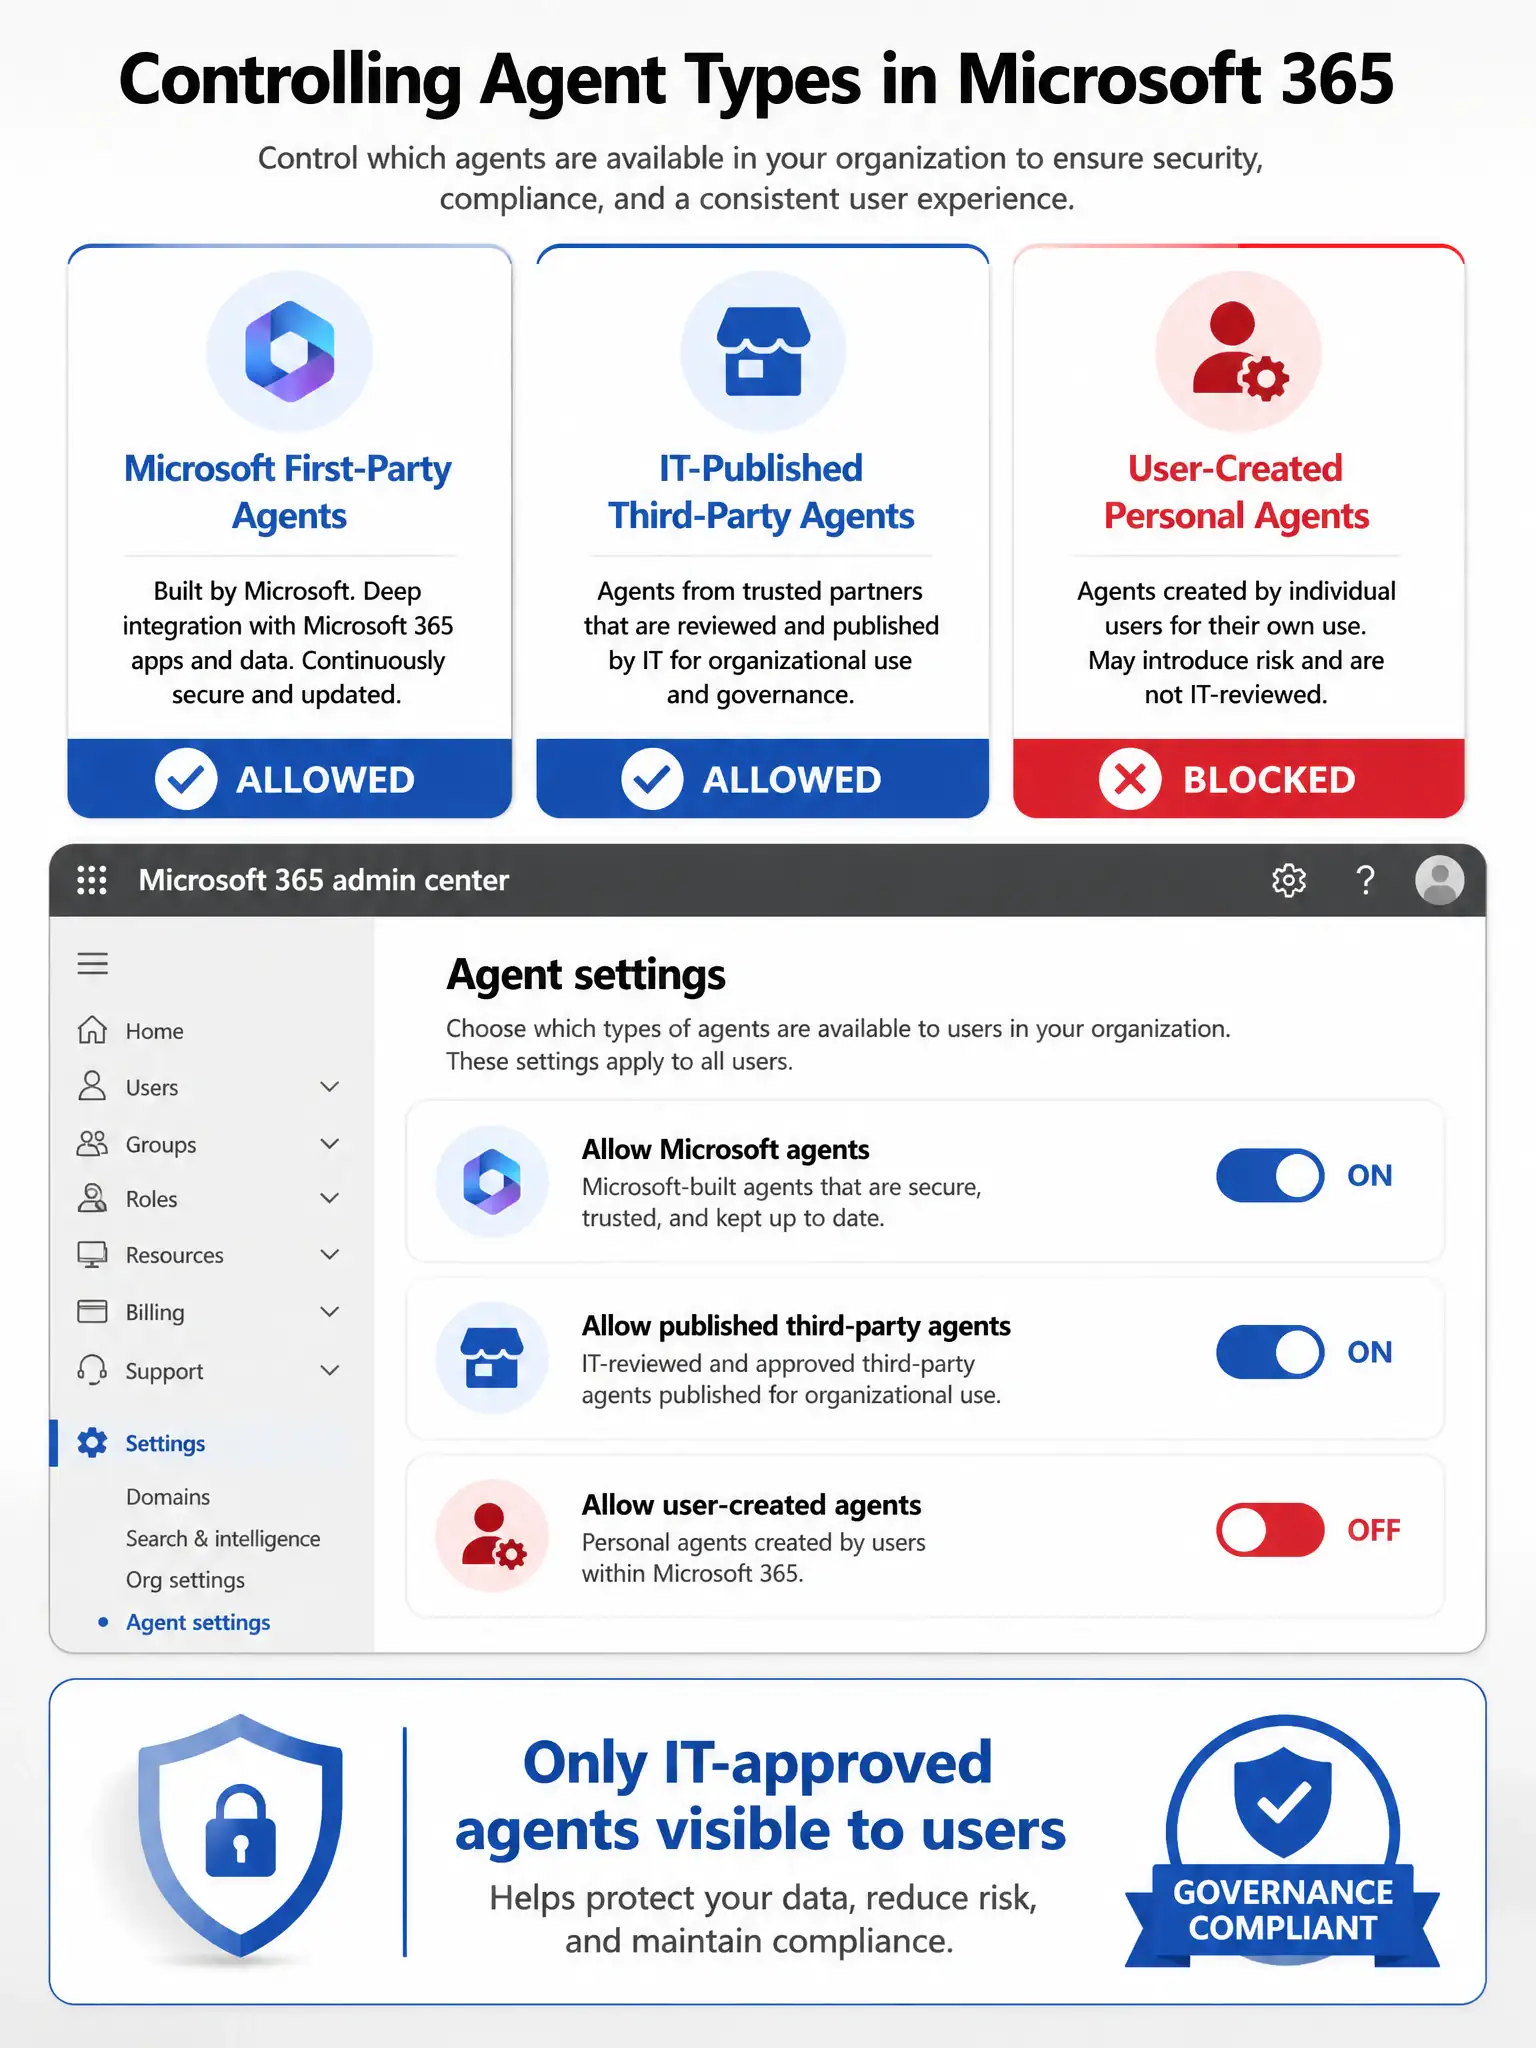
You need to use Microsoft 365 agent settings to allow only Microsoft and published third-party agents and turn off user-created agents. That keeps personal or outside agents from being used while leaving approved agents available.
Full Explanation
The Microsoft 365 admin center provides Agent Settings under the Copilot/Agents section that allow administrators to control which types of agents are permitted, including Microsoft first-party agents, IT-published third-party agents, and user-created agents; whether users can create their own agents; and sharing permissions. By restricting allowed agent types to Microsoft and published third-party agents and disabling user-created agents, the administrator limits the tenant to only agents that have been reviewed and published through the official agent registry workflow, satisfying the governance board's requirement.
The approach that removes all users from the Copilot user experience group is incorrect because it would disable Copilot access entirely for those users, a far broader action than just restricting agent types. The question is about managing which agents are allowed, not disabling Copilot altogether.
The sensitivity-label approach that blocks agent sharing across the tenant is incorrect because Microsoft Purview sensitivity labels control data classification and protection, such as encryption and access restrictions on documents, not the creation or deployment of AI agents. Labels have no mechanism for blocking agent types.
The Azure Policy deny-list approach that prevents agent creation in Azure subscriptions is incorrect because Azure Policy governs Azure resource deployment and configuration in Azure subscriptions. Microsoft 365 Copilot agents are Microsoft 365-layer constructs managed through the Microsoft 365 admin center, not Azure Policy. Azure Policy cannot reach into Microsoft 365 agent settings.
Exam tip: Know that agent settings, including allowed types, user creation permissions, sharing controls, and templates, are all configured in the Microsoft 365 admin center. The exam may present scenarios where a company wants to restrict agent creation; the answer will always point back to the agent settings in the Microsoft 365 admin center, not third-party tools.