
Quantum Analytics has deployed an internal AI agent that processes sensitive financial forecasts. The security team wants to ensure that this agent can only be accessed by users who are connecting from compliant, Intune-managed devices. Non-compliant device access attempts should be blocked. What should the administrator configure to enforce this requirement?
Select an answer to reveal the explanation.
Short Explanation
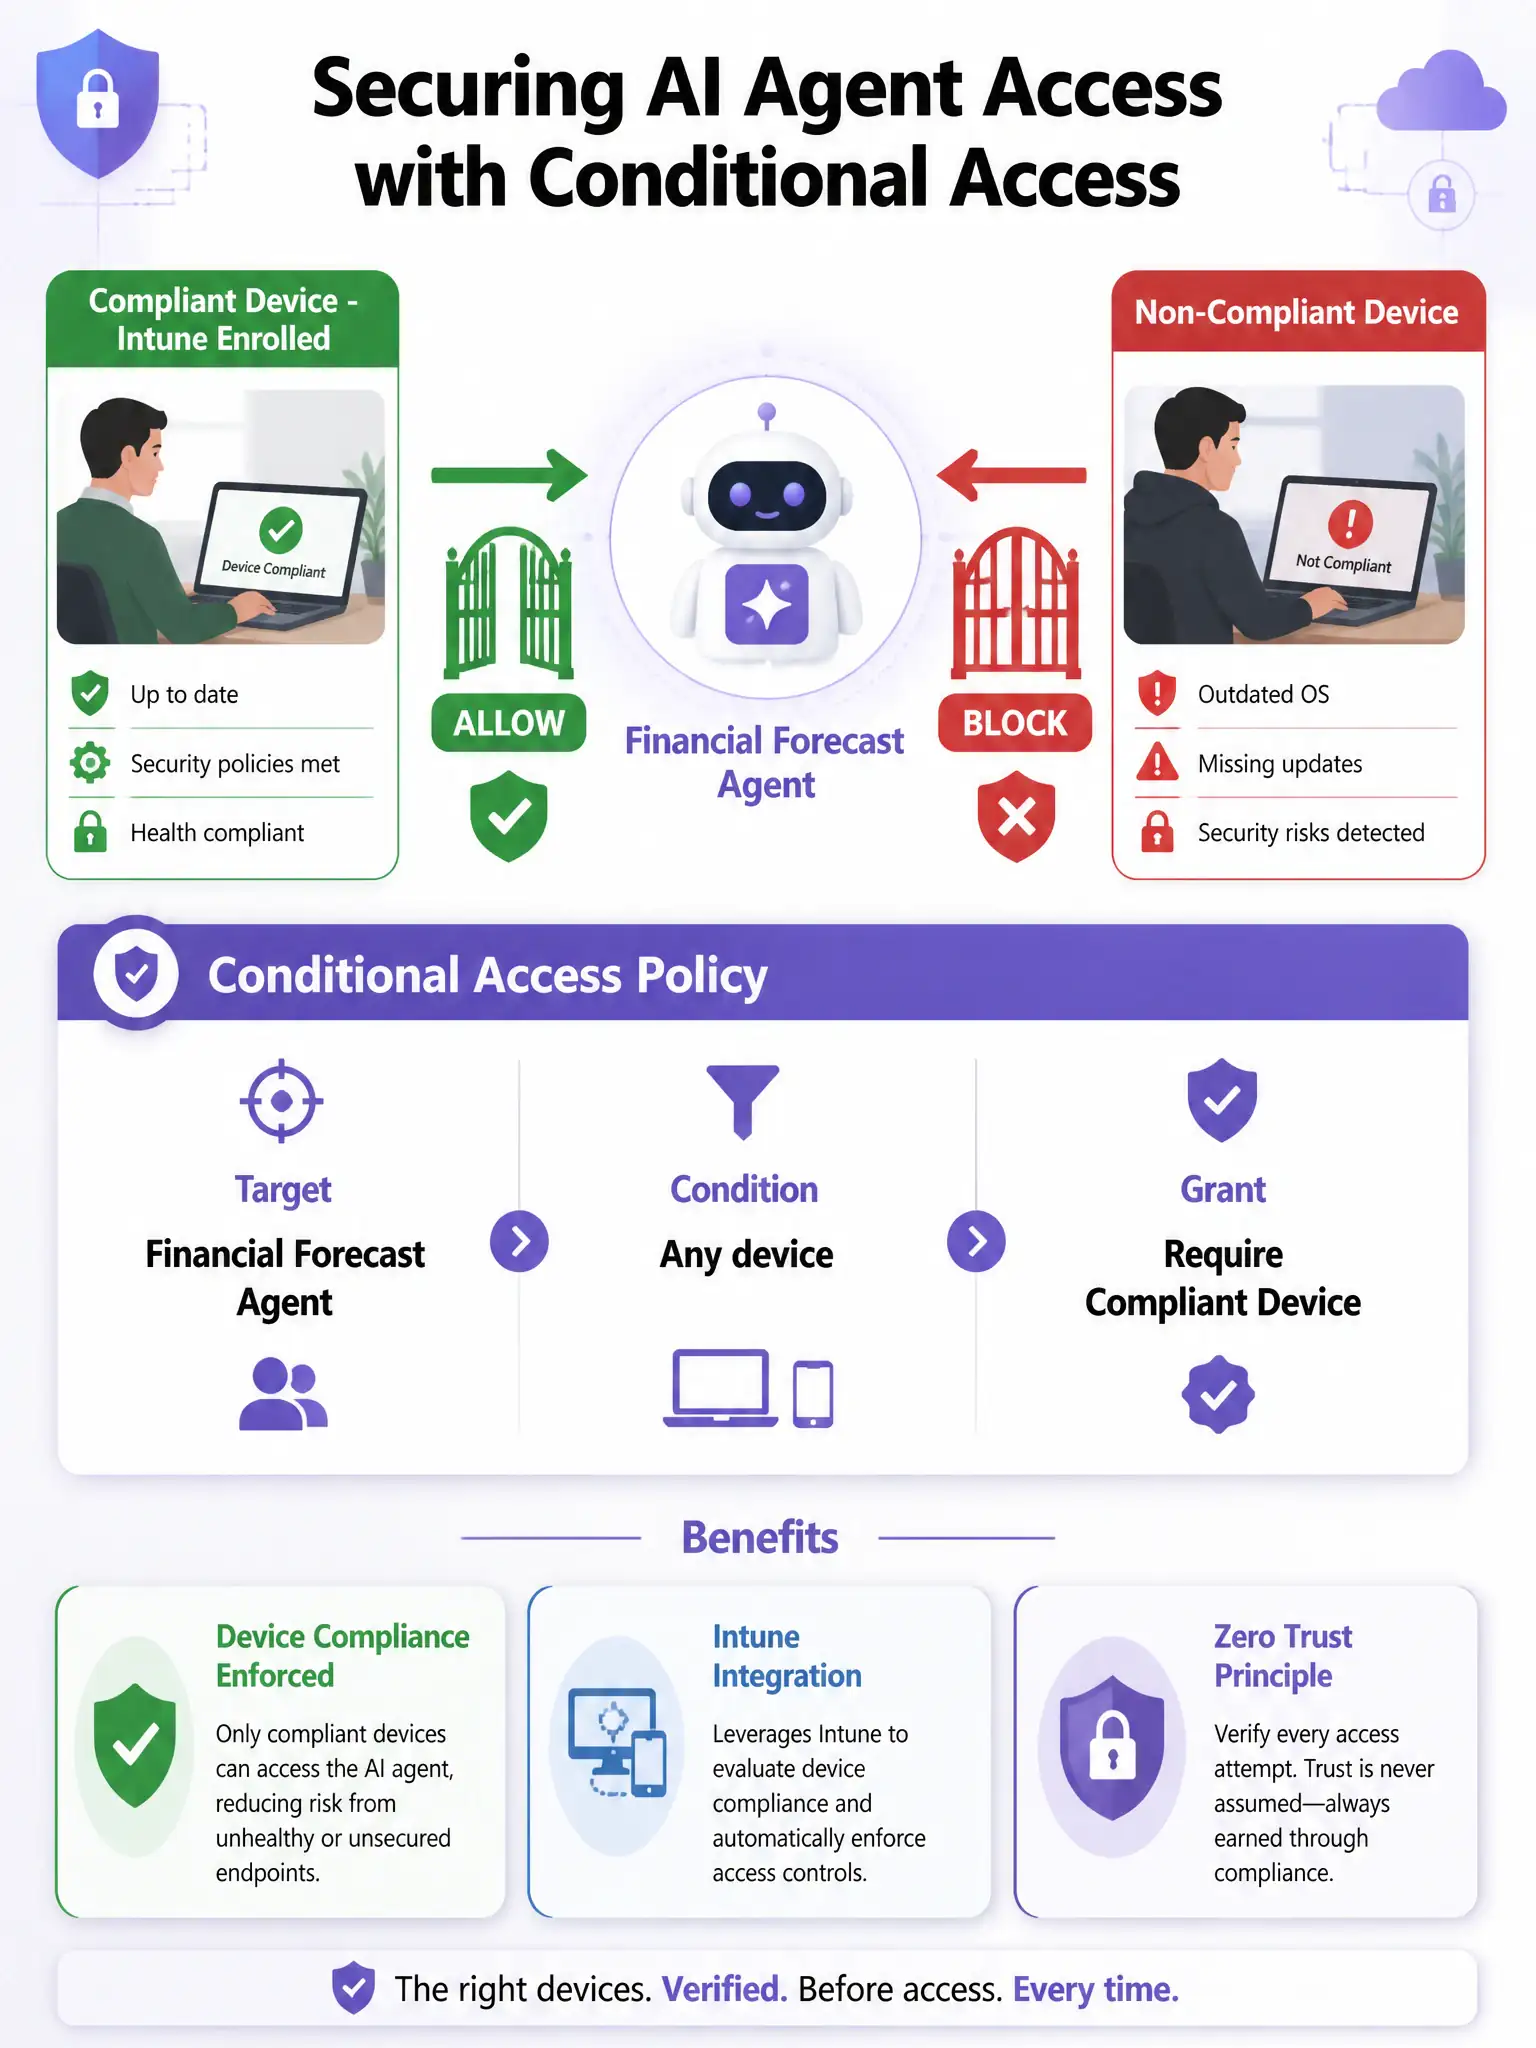
Conditional Access is your policy enforcement engine for both users and agents. Target the agent's Entra identity and require a compliant device as the grant control, and you'll block non-Intune-managed access before the agent runs.
Full Explanation
The correct configuration is to create a Conditional Access policy in Microsoft Entra ID targeting the agent identity that requires a compliant device as a grant control. Microsoft Entra Conditional Access policies can target AI agent identities registered via Entra Agent ID, enabling the same access control enforcement that applies to users and traditional apps. By creating a Conditional Access policy scoped to the financial forecasting agent and specifying 'Require device to be marked as compliant' as a grant control, the administrator ensures that any access attempt from a non-Intune-managed device is blocked before the agent even executes.
The IP address restriction in the agent's configuration in the agent registry is incorrect because it is a coarse network-level control, not a device compliance check. A user on a non-compliant device connected via VPN, which might appear on the corporate IP range, would bypass this control. It also does not enforce Intune enrollment status specifically.
The SharePoint permission policy that restricts the agent's underlying data to users with Intune enrollment is incorrect because SharePoint permission policies control data access on SharePoint sites, not access to the agent itself. The requirement is to restrict who can invoke the agent, not just what data the agent can read. Even if SharePoint permissions were restricted, the agent itself could still be accessed and might surface data from other sources.
Enabling multi-factor authentication for all users in the tenant is incorrect because it is a much broader change that does not specifically address device compliance for agent access. Multi-factor authentication ensures the user is who they say they are, but it does nothing to validate whether the accessing device is enrolled in Intune and meets compliance policy requirements.
Exam caveat: This exam tests that Conditional Access can target agent identities, not just users. Know the policy path: Microsoft Entra admin center > Protection > Conditional Access > New policy > Target resources, including the agent app or identity > Conditions and Grant controls.