
Adatum Corp's security team wants to test the phishing awareness of employees in the Finance department only. The simulation should use a credential harvesting technique — presenting a fake login page when the user clicks a link — and any employee who clicks the link should automatically be enrolled in a security awareness training course without any manual intervention by the security team. What is the correct way to set up this simulation in Microsoft 365?
Select an answer to reveal the explanation.
Short Explanation
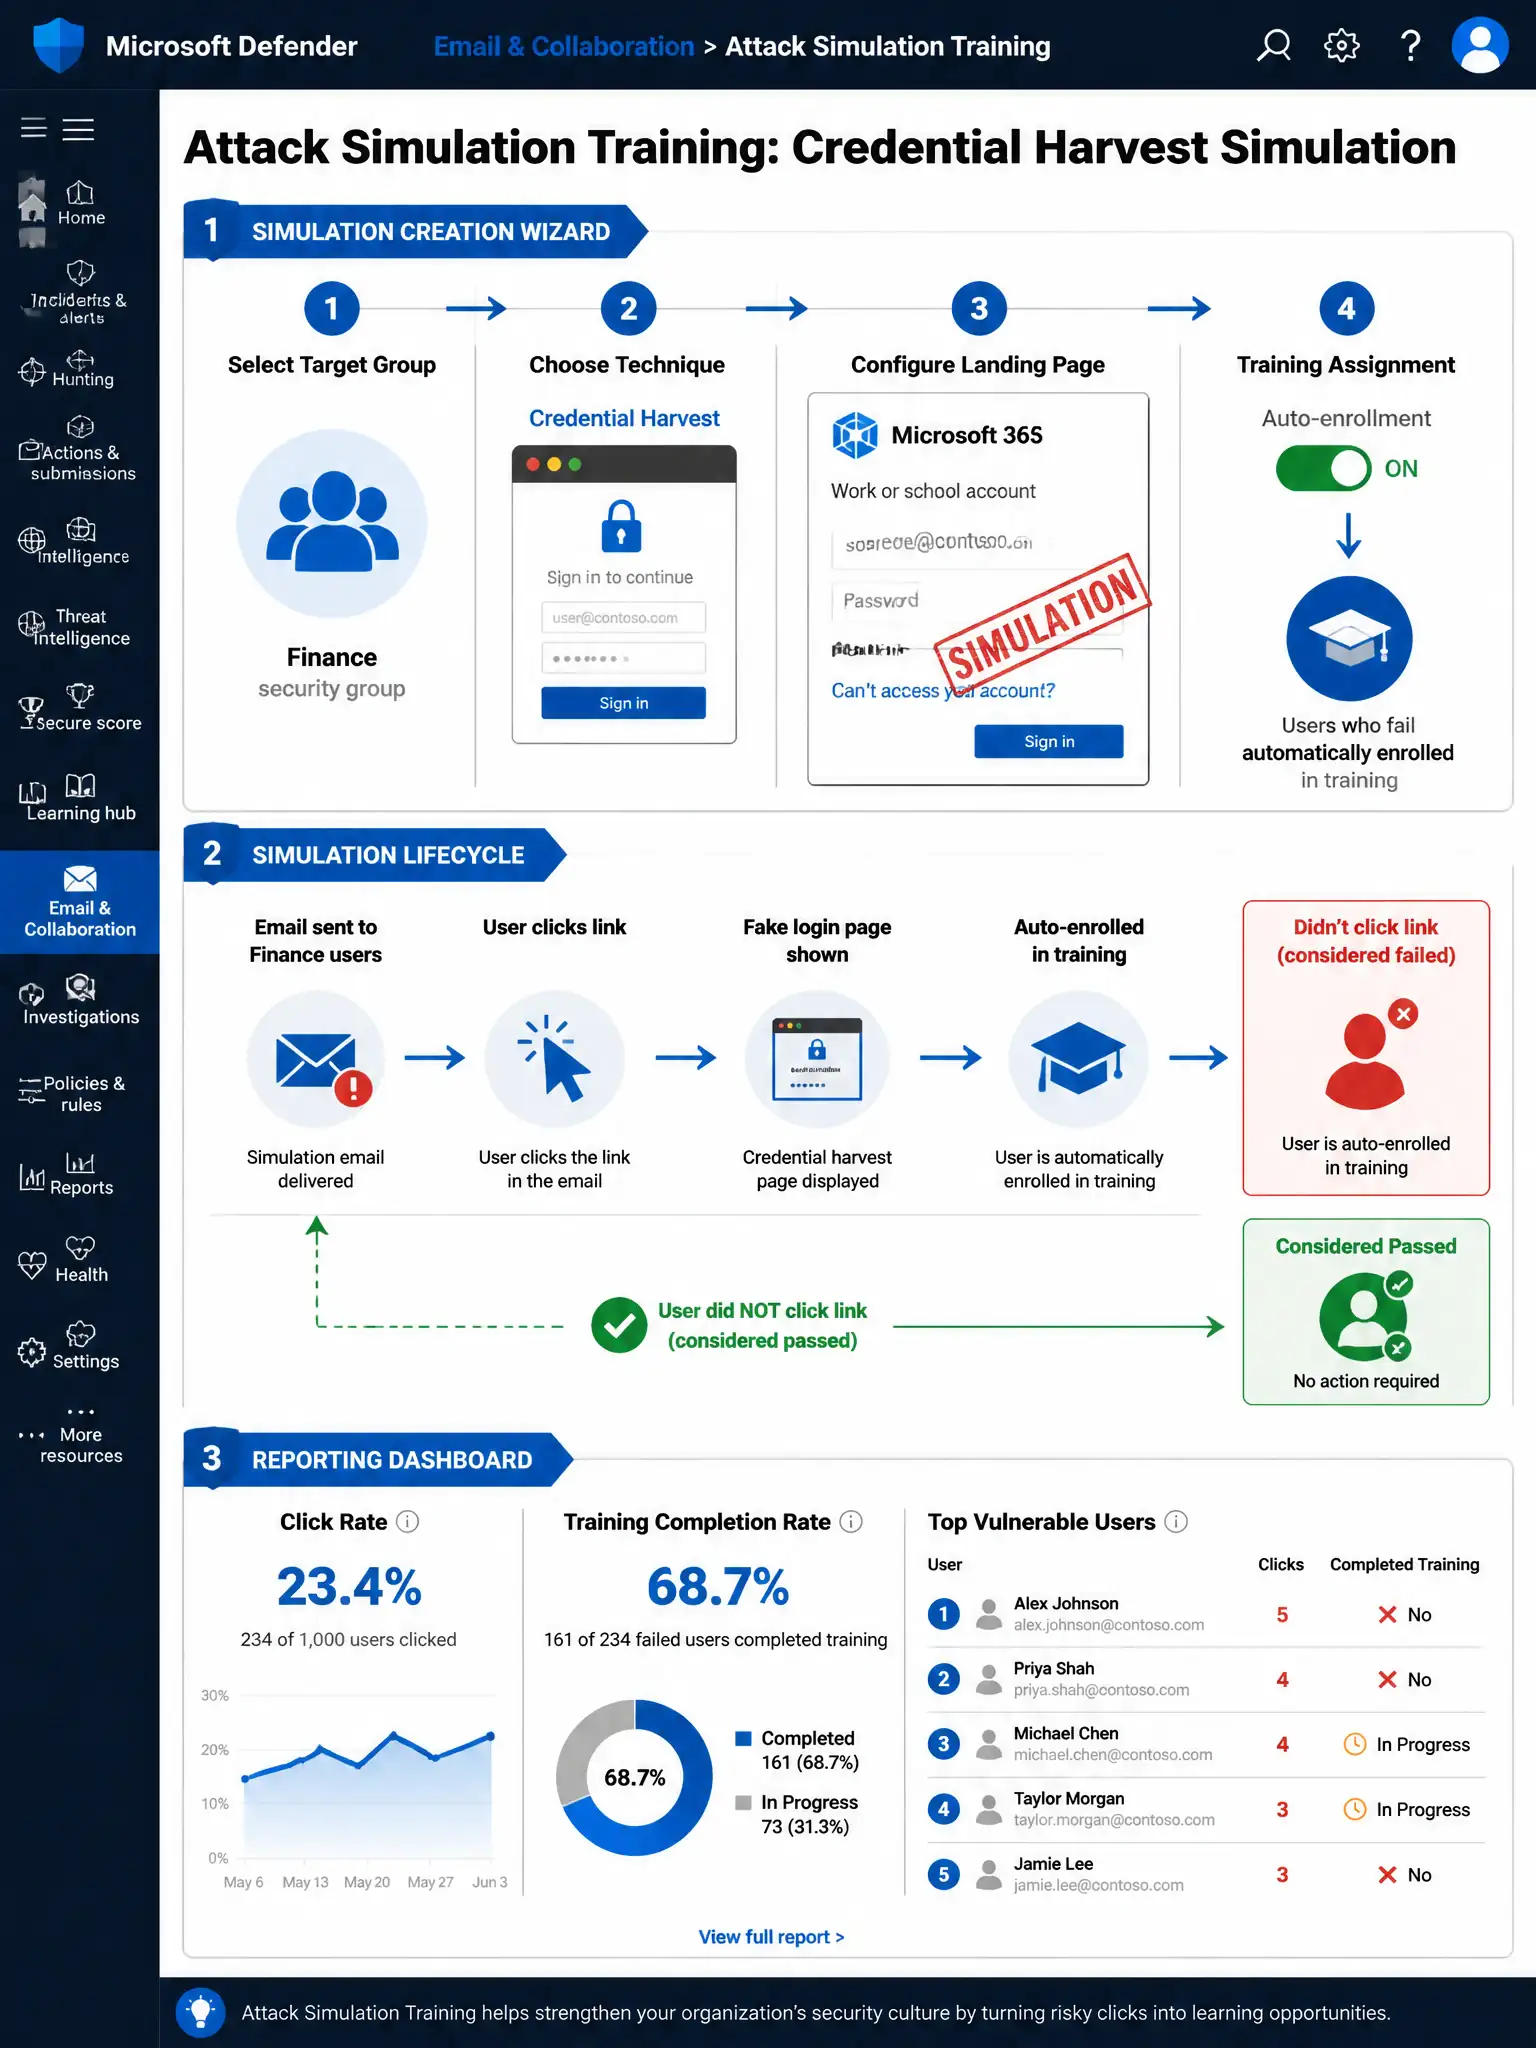
Attack Simulation Training is purpose-built for exactly this — it's like a fire drill where the fire department handles everything: you pick the Finance security group, choose Credential Harvest, and anyone who clicks the fake login link automatically gets signed up for training. No manual follow-up, no Exchange trickery needed. It handles targeting, technique, landing page, and auto-training enrollment all in one workflow.
Full Explanation
The correct approach is to use Attack Simulation Training in the Microsoft Defender portal under Email & Collaboration > Attack Simulation Training. It provides a complete end-to-end workflow for running controlled phishing simulations. The administrator can target a specific Microsoft 365 security group for the Finance department, select Credential Harvest as the social engineering technique, which presents a fake sign-in page to capture simulated credentials, configure the phishing email payload and landing page, and in the Training assignment step configure the system to automatically assign a specific training course to any user who clicks the simulated phishing link. This auto-enrollment removes all manual follow-up work from the security team and ensures immediate, consistent training assignment. The approach that sends a controlled phishing test email through Exchange Online using a distribution list for the Finance department, then checks the message trace to identify who clicked and manually emails those users a training link, is incorrect and potentially dangerous. Sending actual emails with tracking links through Exchange Online is not a controlled simulation; it bypasses Safe Links and other defenses in unpredictable ways, may trigger security alerts, lacks the reporting dashboard and auto-training capabilities, and could cause confusion or compliance issues. Attack Simulation Training is the proper, sanctioned tool for this purpose. The approach that uses Microsoft Defender for Endpoint's attack surface reduction rules to simulate a credential theft scenario and generate a report of affected users in the Finance department is incorrect because Defender for Endpoint and its attack surface reduction rules are focused on endpoint-level threat prevention, such as blocking malicious scripts, restricting Office macros, and preventing credential theft from LSASS. These rules are not a simulation or training tool and cannot simulate phishing scenarios or enroll users in training. The approach that creates the simulation in the Microsoft 365 Defender portal under Incidents and Alerts and manually assigns training to users who triggered the alert after the simulation completes is incorrect because Incidents and Alerts in Microsoft Defender is the section for reviewing real security incidents detected by the platform. It is not a tool for creating controlled simulations. Attack Simulation Training has its own dedicated section in the Defender portal and its own creation wizard separate from incident management. Exam tip: Know the Attack Simulation Training workflow for AB-650: Navigate to Microsoft Defender portal > Email & Collaboration > Attack Simulation Training > Simulations > Launch a simulation. The five social engineering techniques available are Credential Harvest, Malware Attachment, Link in Attachment, Link to Malware, and Drive-by URL. Credential Harvest is the most common technique tested.