
Trey Research's CEO, Megan Bowen ([email protected]), has been impersonated in phishing emails sent to employees from external addresses. Multiple employees received emails appearing to be from Megan with requests to wire transfer funds. The Microsoft 365 administrator needs to ensure that future emails attempting to impersonate the CEO are automatically quarantined before reaching any employee inbox. What is the most effective configuration?
Select an answer to reveal the explanation.
Short Explanation
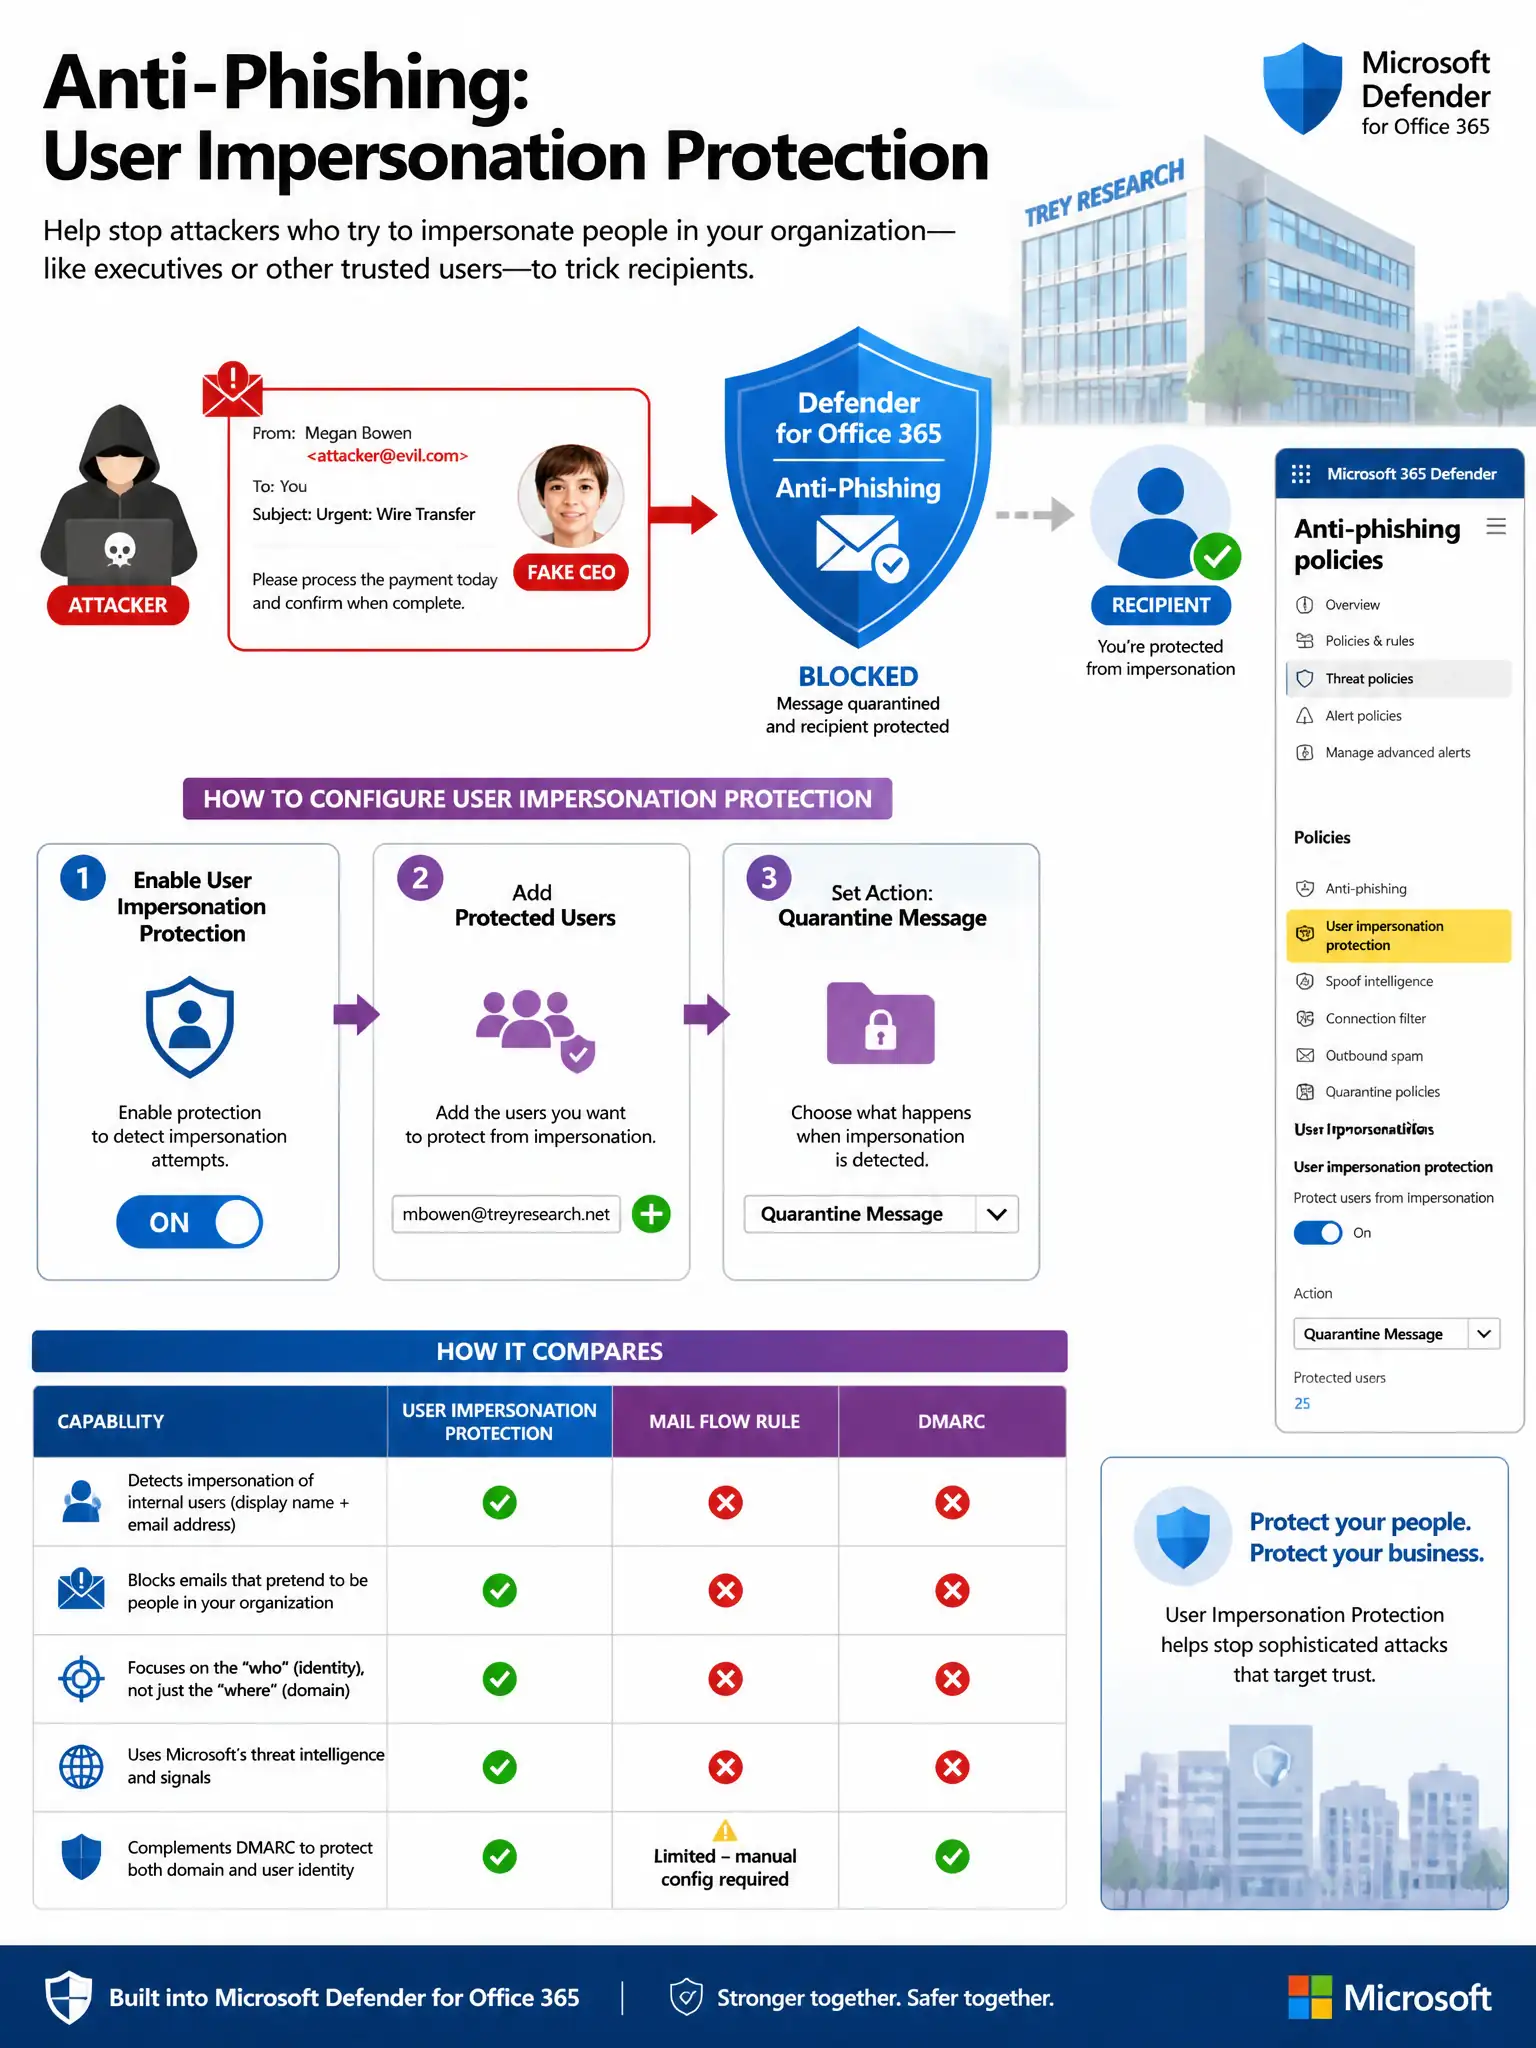
Think of User Impersonation Protection as putting a bodyguard around the CEO's address. You add [email protected] to the protected users list and set the action to quarantine, so Defender catches spoofed-name emails before they hit inboxes. Display-name rules, Safe Links, and outbound DMARC don't solve inbound CEO impersonation.
Full Explanation
The correct configuration is the Microsoft Defender for Office 365 anti-phishing policy with User impersonation protection enabled, [email protected] added to the protected users list, and the impersonation action set to Quarantine the message. This feature is designed for this scenario. Defender uses machine learning to detect when external emails appear to impersonate that user, even when the attacker does not spoof the actual domain. Setting the action to Quarantine the message ensures these emails never reach end user inboxes. Administrators can protect up to 350 individual users per policy. The mail flow rule that blocks all external emails where the From display name matches the CEO's name is incorrect because this is trivially bypassed by attackers. Display name matching in transport rules is unreliable; it generates excessive false positives on legitimate emails and false negatives when attackers change spacing, use Unicode lookalike characters, or slightly modify the name. It is not a security control Microsoft recommends for impersonation protection. The Safe Links policy approach that scans URLs in emails from external senders using the CEO's email domain is incorrect because Safe Links is designed to protect users from malicious URLs within emails, not to detect or block impersonation attempts. Configuring Safe Links does nothing to prevent an email that appears to come from the CEO from reaching the inbox. The DMARC enforcement approach is incorrect for this specific scenario. DMARC controls what happens when external senders try to spoof Trey Research's own domain. However, the attacker is not necessarily spoofing treyresearch.net; they are sending from a completely different domain while using the CEO's display name. DMARC also governs outbound policy, not protection of inbound impersonation attacks using display name tricks. Exam caveat: Distinguish between domain spoofing, caught by DMARC, SPF, and DKIM, and user impersonation, caught by Defender's User Impersonation Protection. The exam tests this distinction. User Impersonation Protection catches sophisticated attacks where the sending domain passes authentication but the human name tricks the recipient.