
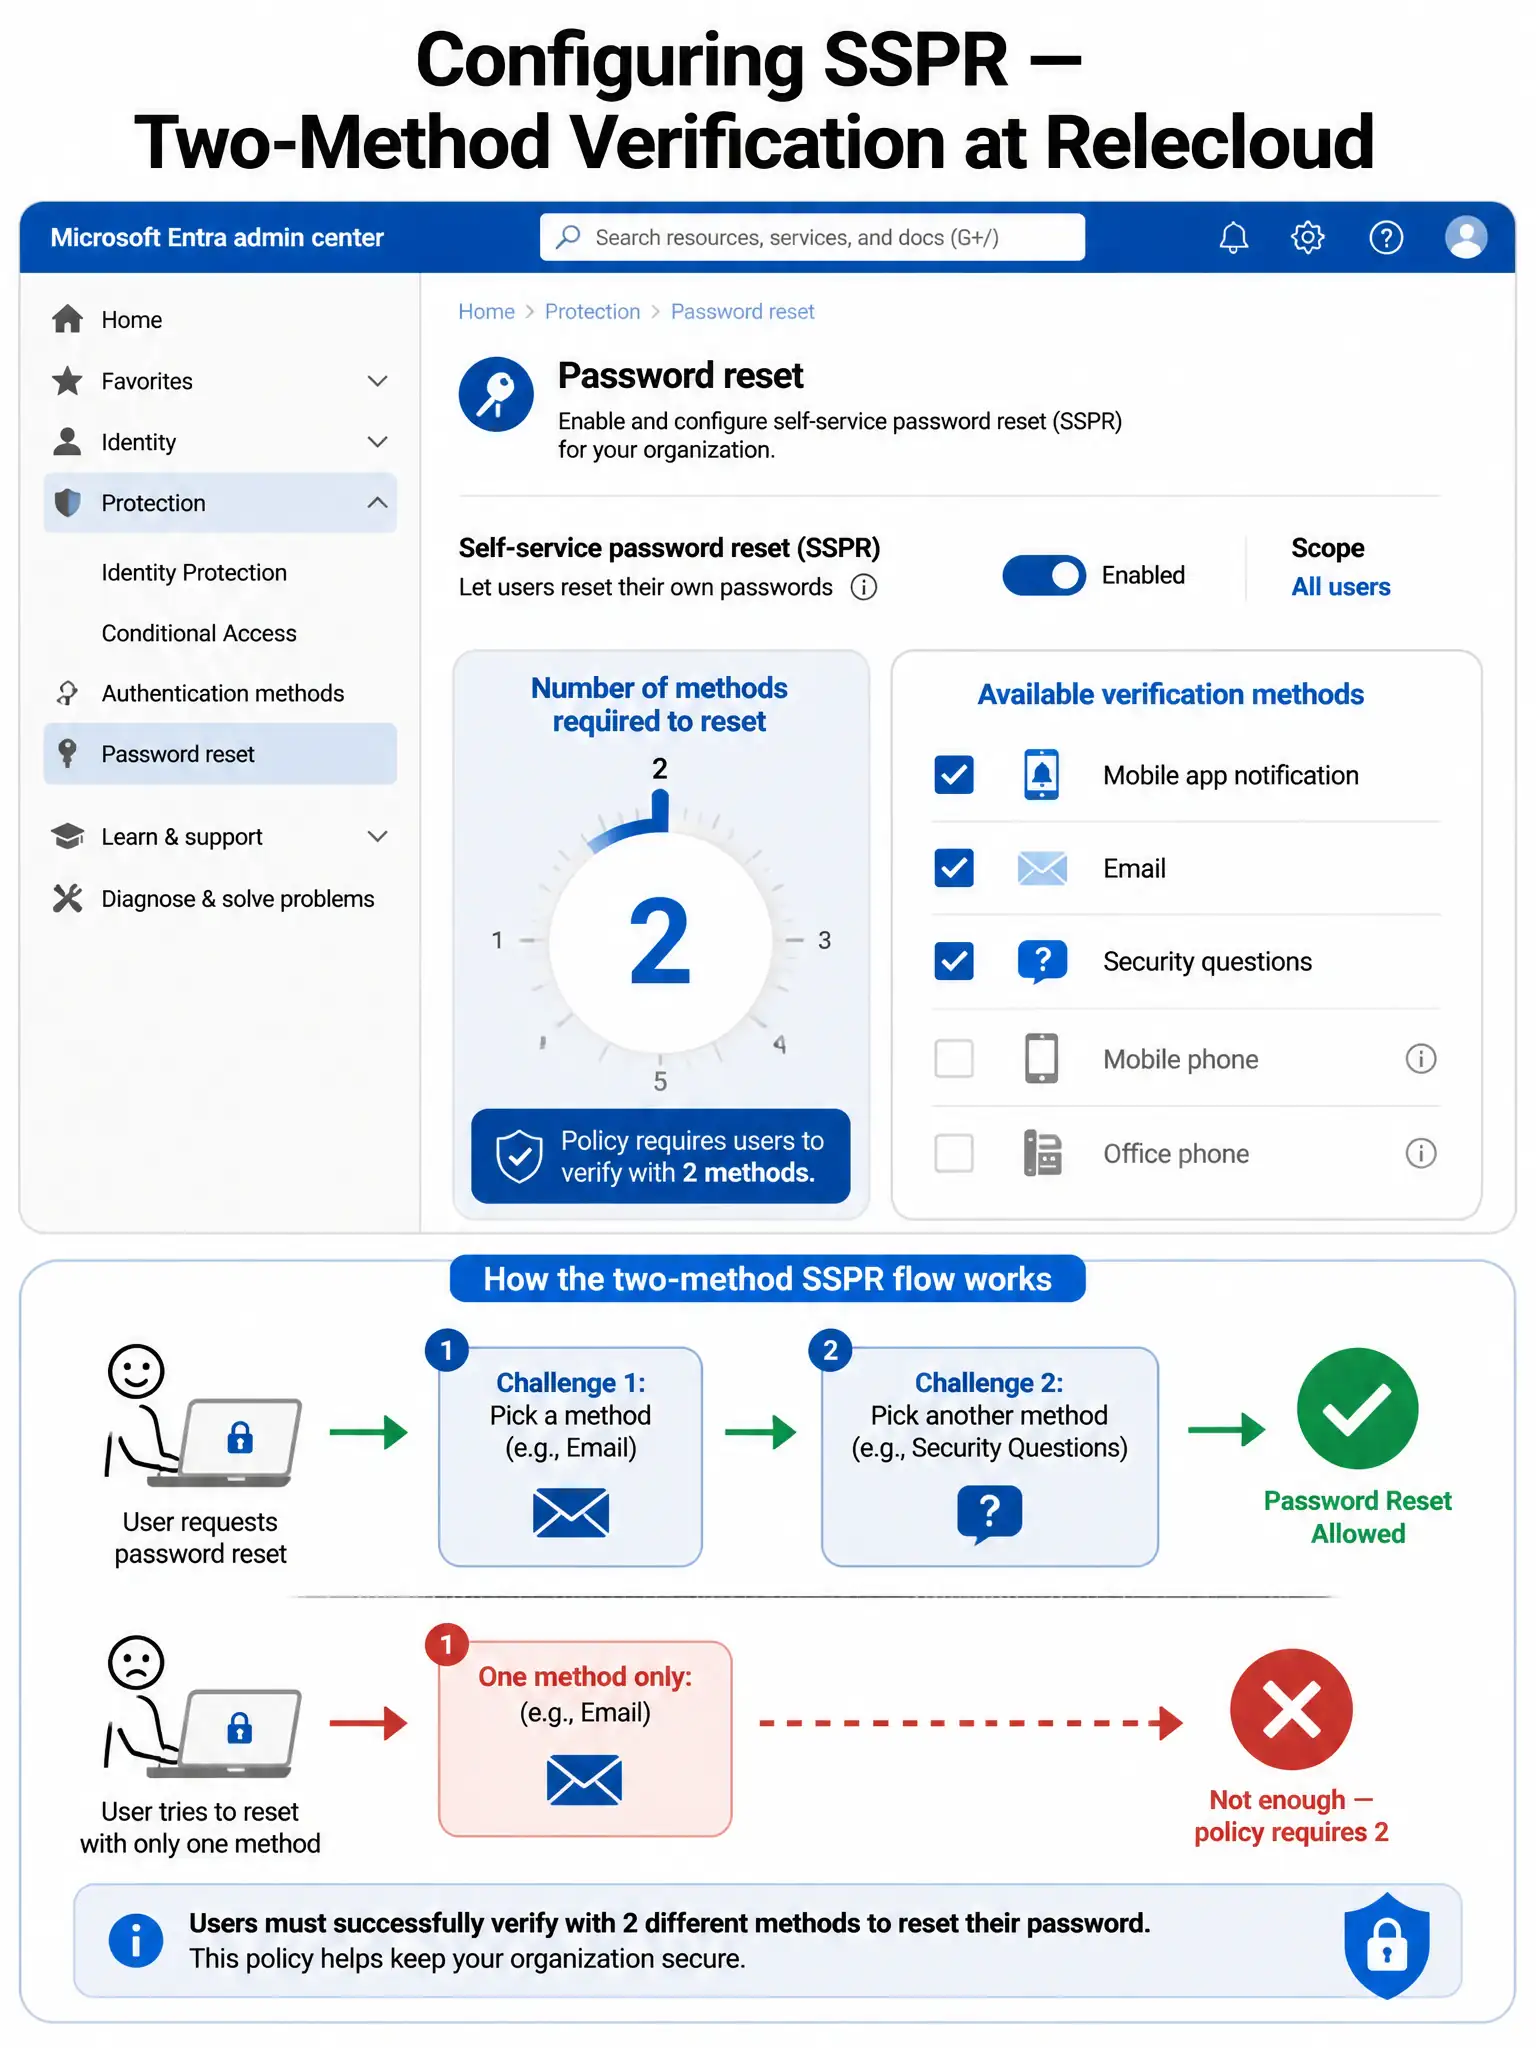
Relecloud wants to enable Self-Service Password Reset (SSPR) for all users in the organization. Their security policy requires that users verify their identity using at least TWO methods before being allowed to reset their password. The IT team wants to give users flexibility by offering mobile app notification, email, and security questions as available options. What is the correct minimum configuration in the SSPR settings to meet this requirement?
Select an answer to reveal the explanation.
Short Explanation
SSPR is like a bank's identity verification at the teller — the bank decides how many identity documents you need to show before they'll help you. Set the required methods to 2 and offer mobile app notification, email, and security questions so you must prove your identity twice, but you get to pick which two methods you've registered.
Full Explanation
Microsoft Entra SSPR is configured under Protection > Password reset. The key setting 'Number of methods required to reset' controls how many verification steps a user must complete before a password reset is allowed. Setting this to 2 means a user must successfully complete two distinct verification challenges. You then enable the methods users can register and use: Mobile app notification (Microsoft Authenticator push), Email (to an alternate email address), Security questions, Mobile app code, Mobile phone, and Office phone are all available options. The scenario specifically asks for mobile app notification, email, and security questions — enabling all three gives users flexibility to register and use any two of them.
The configuration that sets 'Number of methods required to reset' to 1 and enables only the Microsoft Authenticator app notification is incorrect because requiring only one method fails the security policy requiring TWO methods. Even if the Authenticator app is strong, requiring only one factor is a weaker configuration than the policy demands.
The approach that enables SSPR only for a pilot group first using a scoped group assignment, then expands to all users after a 30-day evaluation period, is incorrect because it is a rollout strategy decision, not a configuration for the authentication method requirement. The question asks what configuration meets the security policy, not what deployment approach to use. Rolling out to all users is specifically stated as the goal.
The configuration that requires a Helpdesk call as one of the two required verification factors so IT can manually verify identity before allowing a reset is incorrect because SSPR does not support a 'Helpdesk call' as one of its built-in verification methods. SSPR's purpose is to eliminate the helpdesk call for routine resets; requiring a helpdesk call defeats the feature's entire value proposition and is not a configurable SSPR method in Entra ID.
Exam tip: Know the difference between the number of methods required (1 or 2, controlled by the 'Number of methods required to reset' setting) and which methods are available. You configure them independently. Also note that security questions require users to have registered answers in advance — they cannot be used if not pre-registered.