
Contoso Healthcare has deployed AI agents in Microsoft 365 that access sensitive patient data stored in SharePoint. The security team wants to ensure these agents can only access resources when running from trusted, compliant execution environments. Which control should the administrator implement to enforce this requirement?
Select an answer to reveal the explanation.
Short Explanation
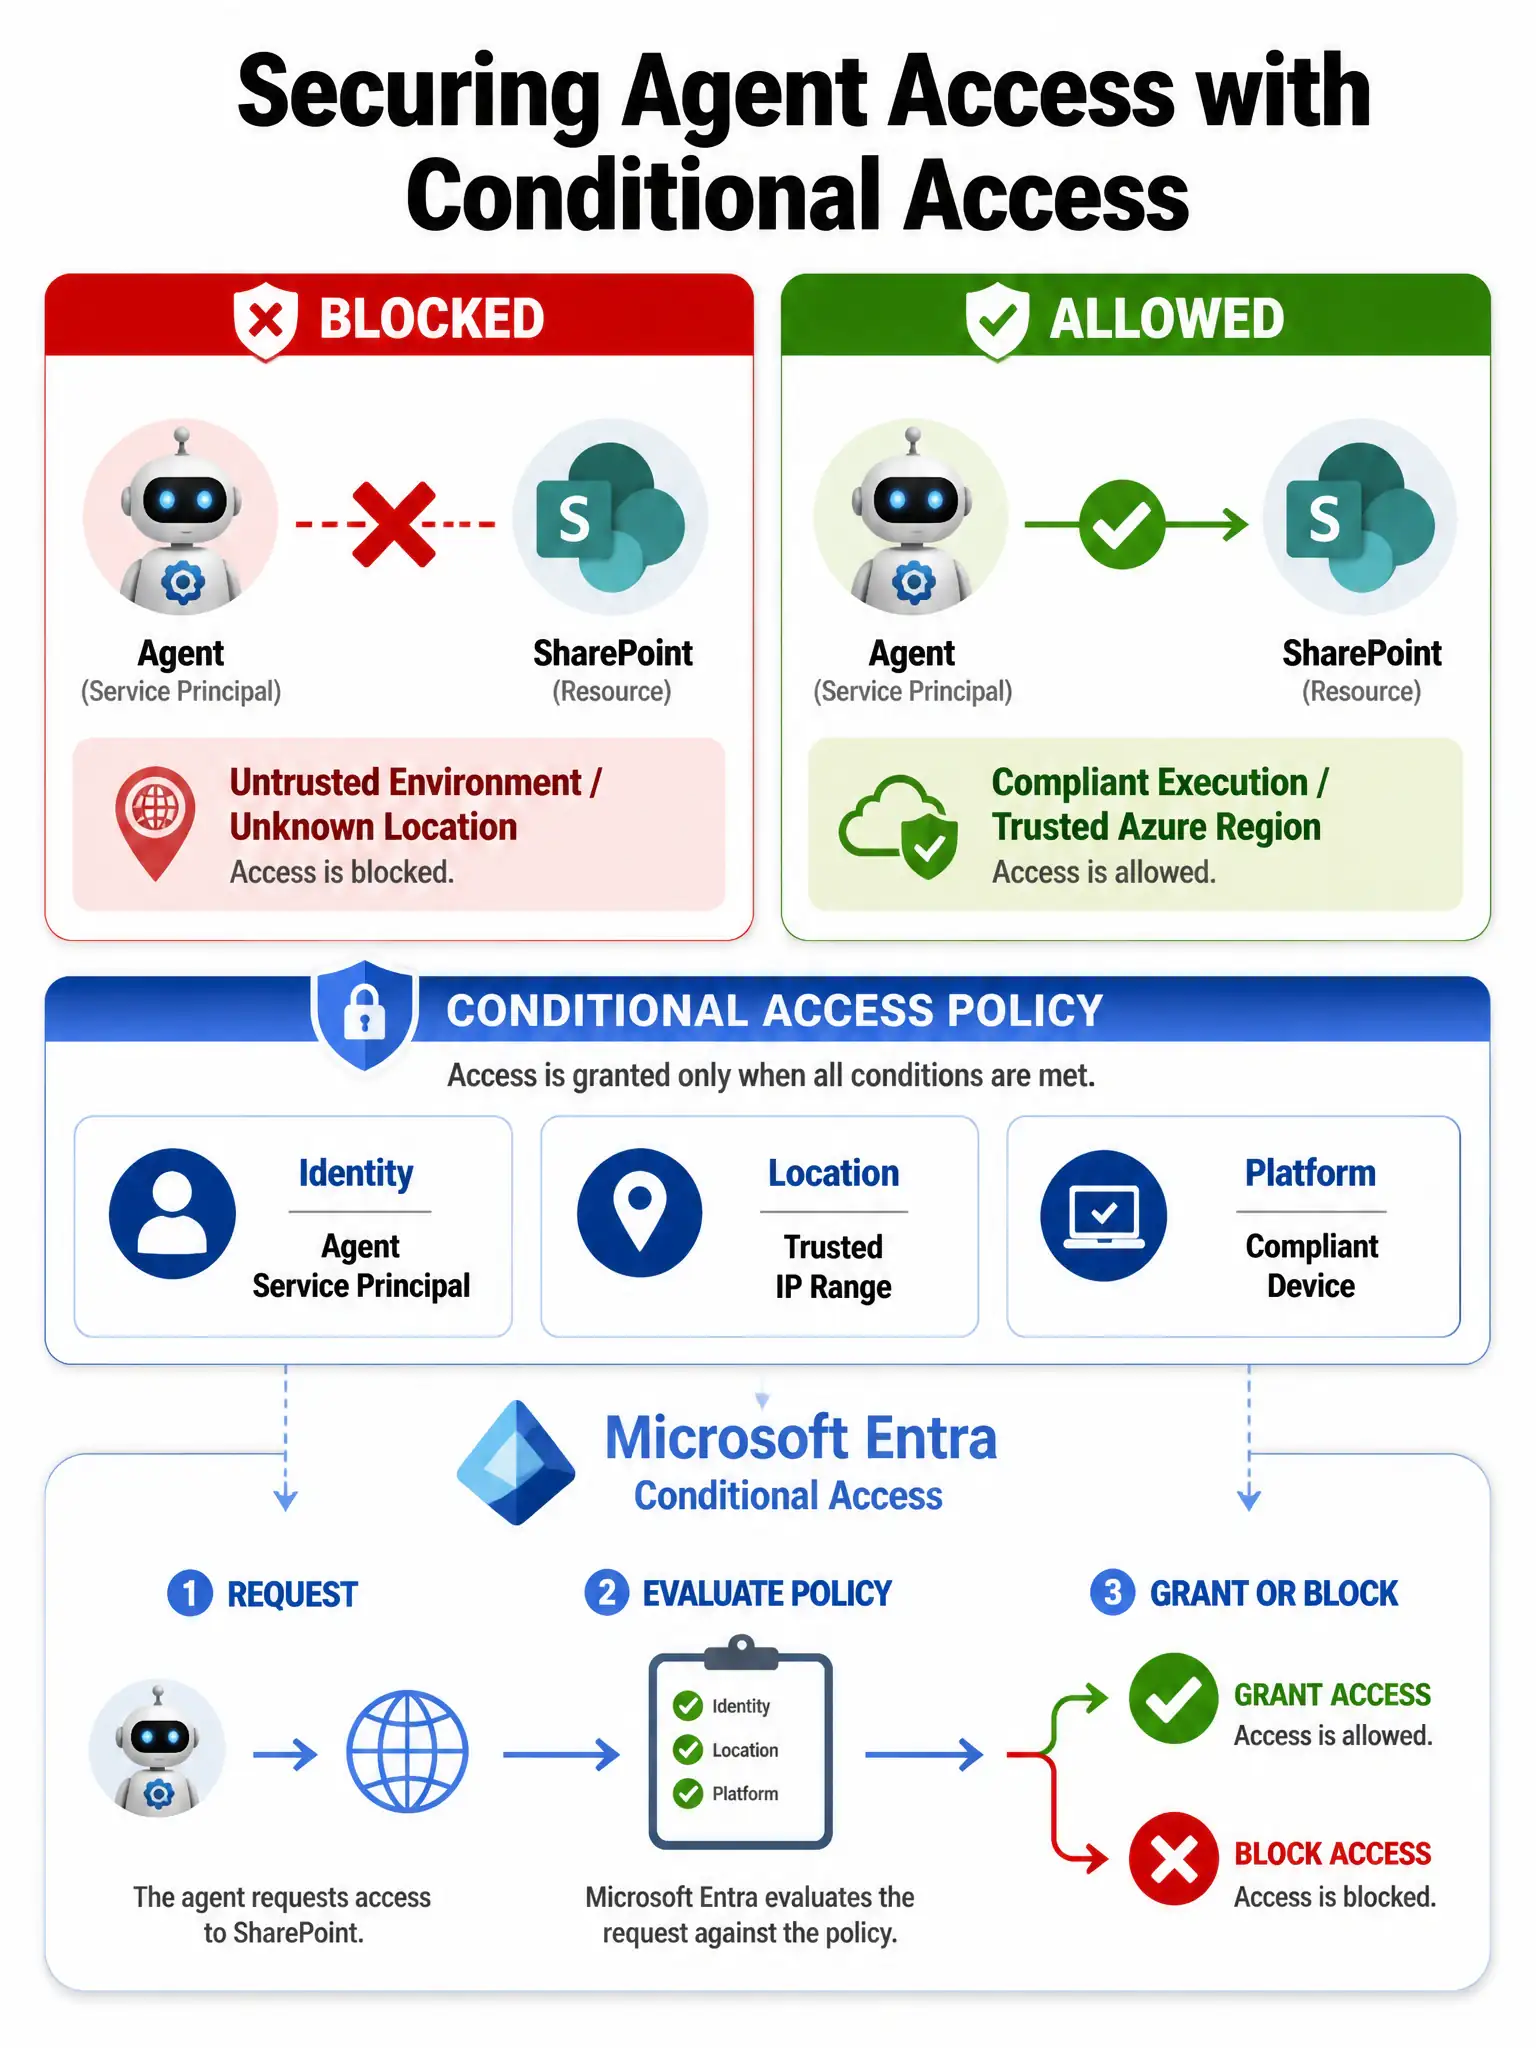
Conditional Access isn't just for people — it works for agents too. Point a policy at your agent identities and require compliant devices or trusted locations, so they only run from approved environments. It's like putting a bouncer on your data that checks agent credentials at the door.
Full Explanation
Microsoft Entra Conditional Access policies can target agent identities (service principals and managed identities registered through Entra Agent ID) just as they can target human user accounts. By creating a Conditional Access policy scoped to the agent service principals, administrators can enforce conditions such as trusted IP locations (for example, only from approved Azure regions or on-premises environments), compliant devices or platforms, trusted locations, and additional authentication controls. This ensures agents can only execute and access resources from approved environments, significantly reducing the attack surface if an agent identity is compromised.
The sensitivity label approach that applies labels to SharePoint sites and requires user authentication before agents can read content controls who can access and use labeled content based on user identity and label policy. However, sensitivity labels do not evaluate environmental compliance or the location of an agent's execution — they check label permissions, not network location or device compliance.
The SharePoint permission group approach that creates a group for agents and manually approves each agent access request provides basic access control but is not scalable, does not enforce execution environment compliance, and cannot dynamically enforce conditions like network location or platform compliance in real time.
The Microsoft Purview Insider Risk Management approach that monitors agent access to sensitive data monitors for risky user behavior patterns using signals from Microsoft 365 activity. It is a detection and investigation tool, not a preventive access control mechanism for agent identities.
Exam caveat: Conditional Access is the right answer whenever a question asks about enforcing environmental or contextual access conditions (location, device compliance, network) for identities — including agent identities. Remember that Conditional Access policies in Entra can target non-human identities (agents, service principals) as well as users.