
A financial services company requires that its Copilot Studio agent authenticate to an internal high-security trading API using mutual TLS (mTLS) with a client certificate. The API validates both the server certificate and the client certificate on every request. The organization stores certificates in Azure Key Vault. A Power Automate premium flow is used to call the API. Which configuration correctly enables client certificate authentication for this API call within the Power Platform solution?
Select an answer to reveal the explanation.
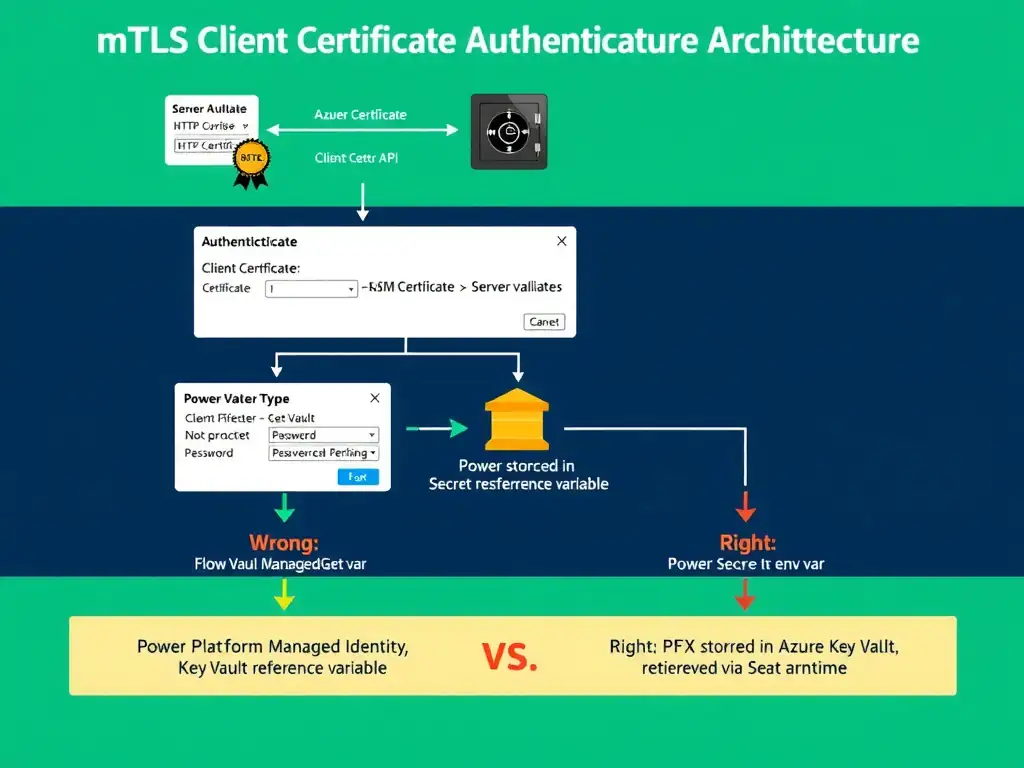
Short Explanation
Power Automate's HTTP action can do client certificate auth, so you set it to Client Certificate and feed it a base64-encoded PFX from an Azure Key Vault secret through a Power Platform Secret environment variable. You also grant the Power Platform managed identity permission to get that secret, keeping the private key in Key Vault and out of the flow definition.
Full Explanation
Mutual TLS (mTLS) requires both parties to present certificates during the TLS handshake. In Power Automate, the HTTP premium action supports client certificate authentication directly, but the security of this configuration depends on how the certificate is stored and referenced. The correct configuration is the one that sets the HTTP action's Authentication type to 'Client Certificate', provides the client certificate as a base64-encoded PFX stored directly in an Azure Key Vault secret, references that secret through a Power Platform Secret environment variable, and grants the Power Platform managed identity permission to get the secret value. The HTTP action's 'Client Certificate' authentication type accepts a base64-encoded PFX (PKCS#12 file containing both the certificate and private key) and, if password-protected, the PFX password. Storing the PFX as an Azure Key Vault secret referenced through a Power Platform Secret environment variable ensures that the certificate and private key are never stored in plain text within the Power Platform environment. The Power Platform managed identity must be granted the 'Get' permission on the Key Vault secret (Secret permissions -> Get) to retrieve the value at runtime. This approach keeps the private key in Key Vault's HSM-protected storage, keeps it out of the flow definition, and allows certificate rotation by updating the Key Vault secret without redeploying the flow. The configuration that configures the HTTP action with 'Client Certificate' authentication, references the client certificate's base64-encoded public-key certificate file and password stored as Power Platform Secret environment variables, and ensures the Key Vault secret contains the full certificate chain is incorrect because client certificate authentication needs the private key, not just a public-key certificate file. A public-key certificate file cannot prove the client's identity in mTLS, and a password does not compensate for a missing private key. This wording also does not clearly require the environment variable to be Key Vault-backed or grant the Power Platform managed identity the permission needed to read the secret at runtime. For a financial services high-security scenario, Key Vault-backed storage with managed identity access is the required pattern. The configuration that places an Azure API Management policy layer in front of the trading API to handle mTLS termination, has the Copilot Studio agent call APIM using a standard bearer token, and stores the client certificate in APIM's certificate store for outbound mTLS to the backend describes a valid architectural pattern, but it introduces significant additional infrastructure (APIM instance required, certificate stored in APIM, additional policy configuration) and adds latency. While this is a legitimate enterprise architecture choice, it is not the most direct answer to the question of how to configure client certificate authentication within the Power Platform solution itself. The configuration that registers the client certificate as an app credential in the Entra ID app registration for the Power Automate flow, then uses the Certificate authentication type in the HTTP action with the Entra ID tenant ID, client ID, and certificate thumbprint to authenticate to the trading API using OAuth 2.0 with certificate assertion, describes a different authentication mechanism. Using a certificate to sign a JWT assertion for OAuth token acquisition from Entra ID is the correct approach for authenticating to Entra ID-protected APIs using a certificate credential, but the scenario describes a trading API that requires mTLS client certificate authentication directly, not OAuth token acquisition. These are fundamentally different authentication patterns: mTLS presents the certificate at the transport layer, while OAuth certificate assertion uses the certificate to sign a token request at the application layer. Exam tip: Know that Power Automate HTTP action supports authentication types such as None, Basic, Client Certificate, Active Directory OAuth, and Raw. Client Certificate uses PFX format (base64-encoded). For high-security scenarios, always store certificates in Azure Key Vault and access them through Power Platform Secret environment variables with managed identity. Certificate thumbprint alone does not establish mTLS; the full private key must be accessible to the client.