
A Power Platform admin must ensure Copilot Studio agents across environments cannot exfiltrate Dataverse customer data to unsanctioned consumer connectors. Which governance control is primary?
Select an answer to reveal the explanation.
Short Explanation
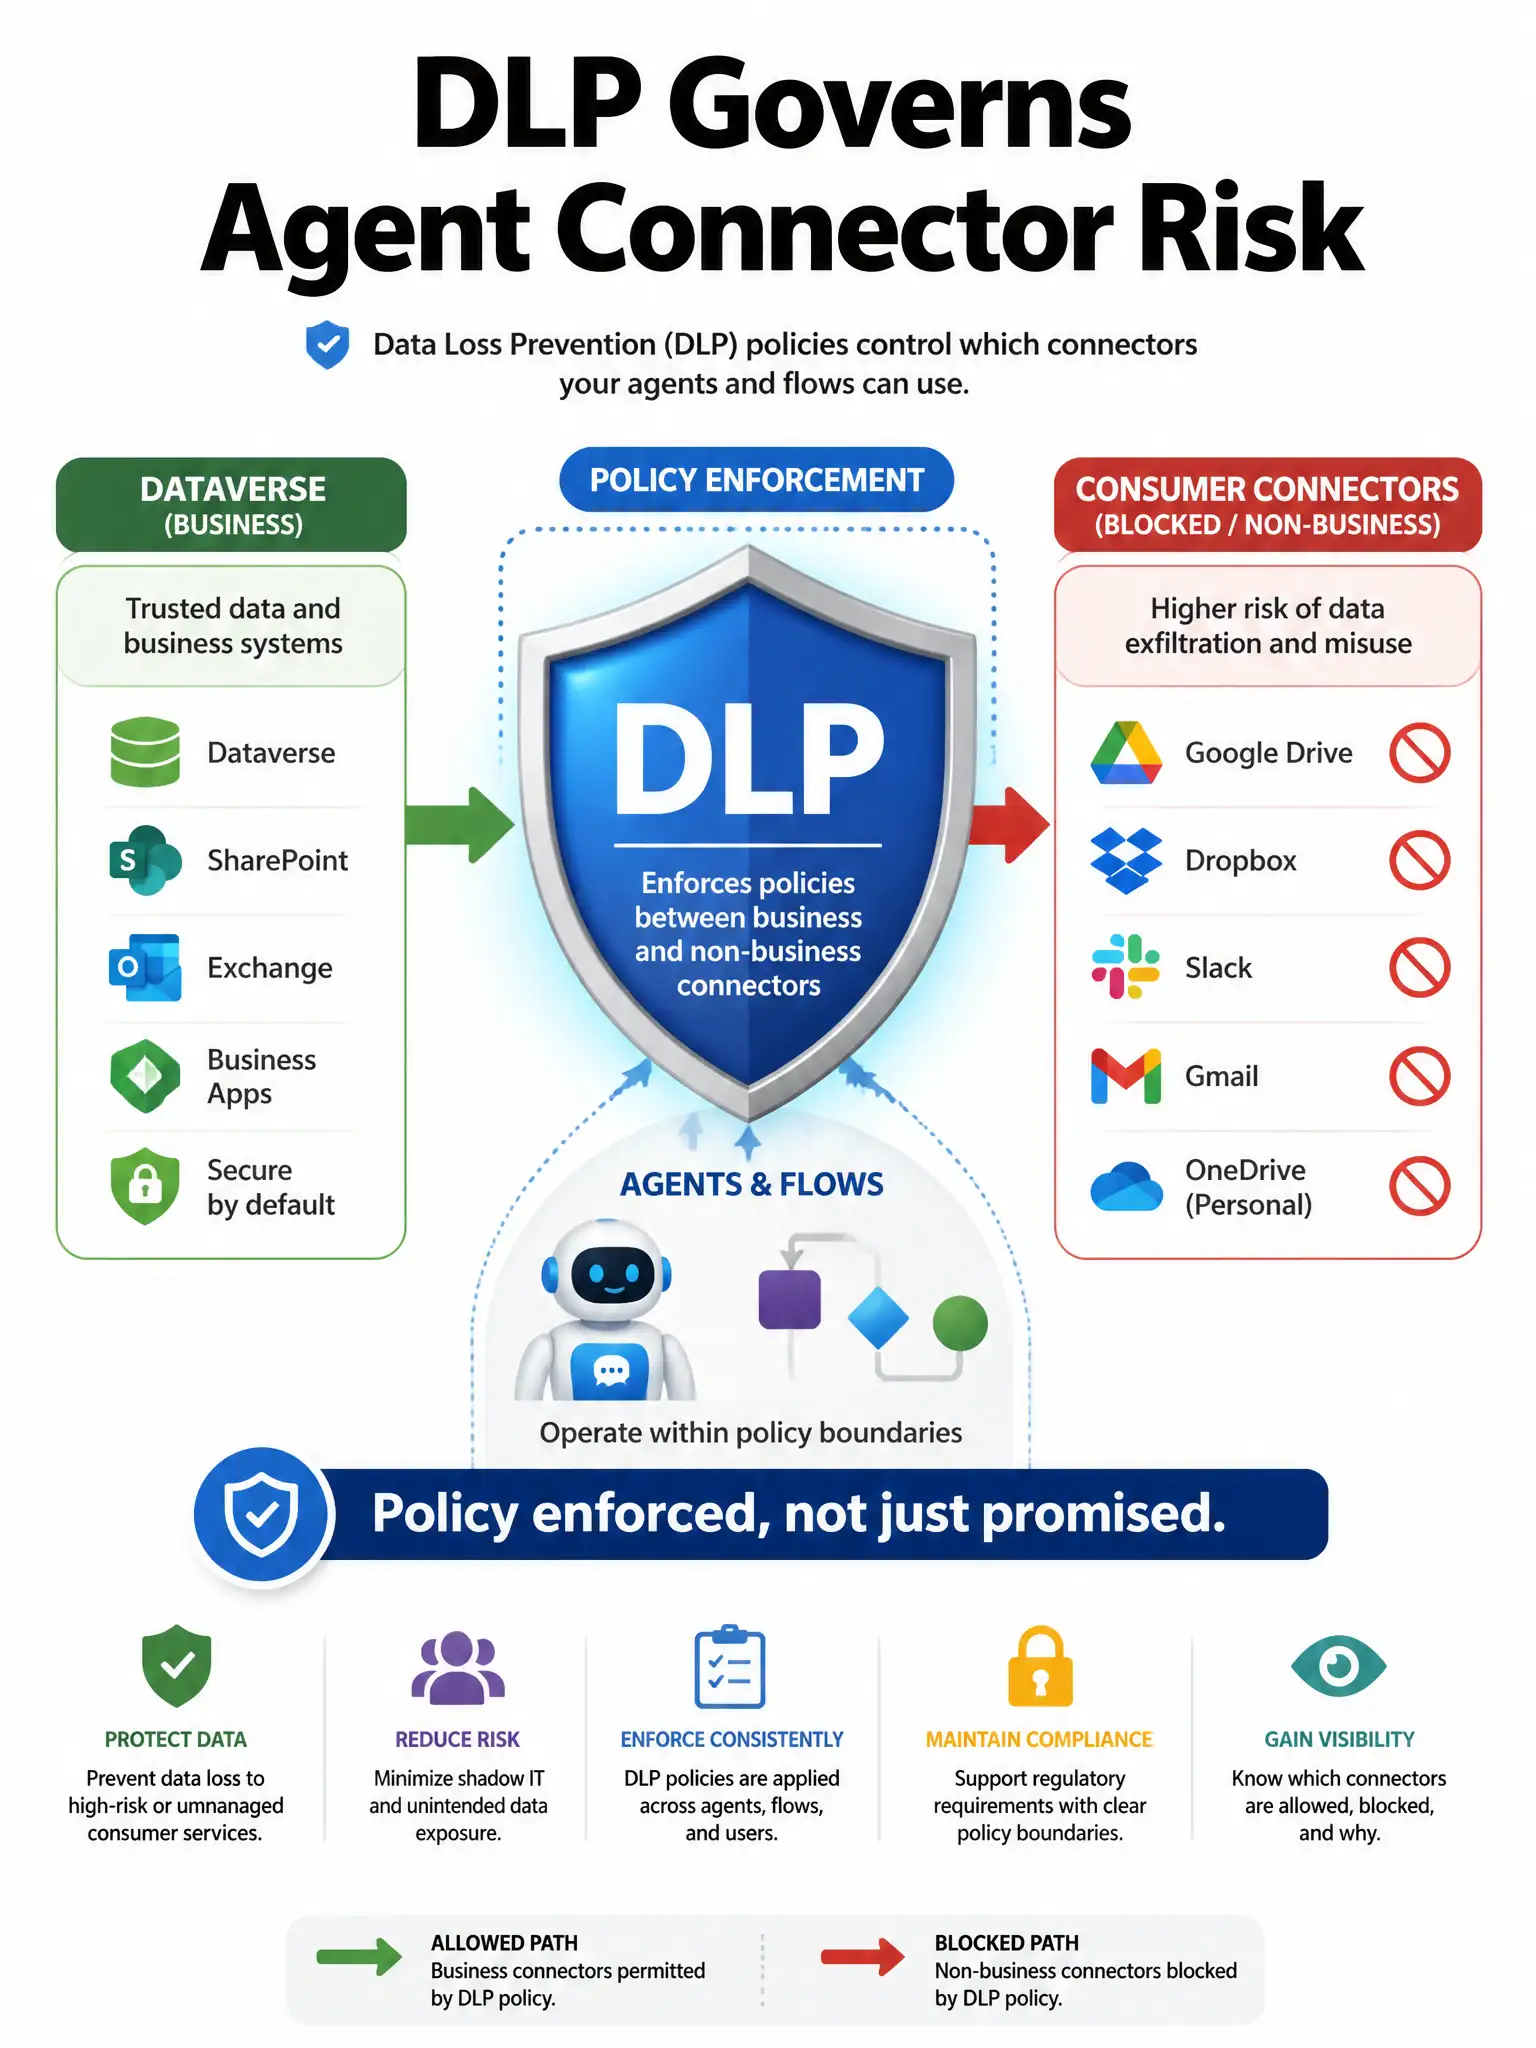
You need tenant/environment DLP policies to classify and restrict connectors so Dataverse Business data can't be combined with unsanctioned consumer connectors in flows or agent-related automations. That's the technical fence that actually prevents exfiltration.
Full Explanation
DLP policies are the primary control because they classify and restrict connectors, preventing Business data connectors from being combined with non-business or blocked connectors in flows and agent-related automations. Combined with environment strategy and RBAC, this reduces exfiltration paths. Asking makers to promise not to use consumer connectors is not enforceable. Relying on agent display names containing Secure is ineffective. Turning off Dataverse auditing only does not block connector calls. Exam tip: DLP+environment isolation+least-privilege roles.