
A Copilot Studio solution must call a partner REST API that authenticates with an API key in a custom HTTP header. The team uses a Power Automate HTTP action (or custom connector) invoked from a topic. Where should the API key be stored for production?
Select an answer to reveal the explanation.
Short Explanation
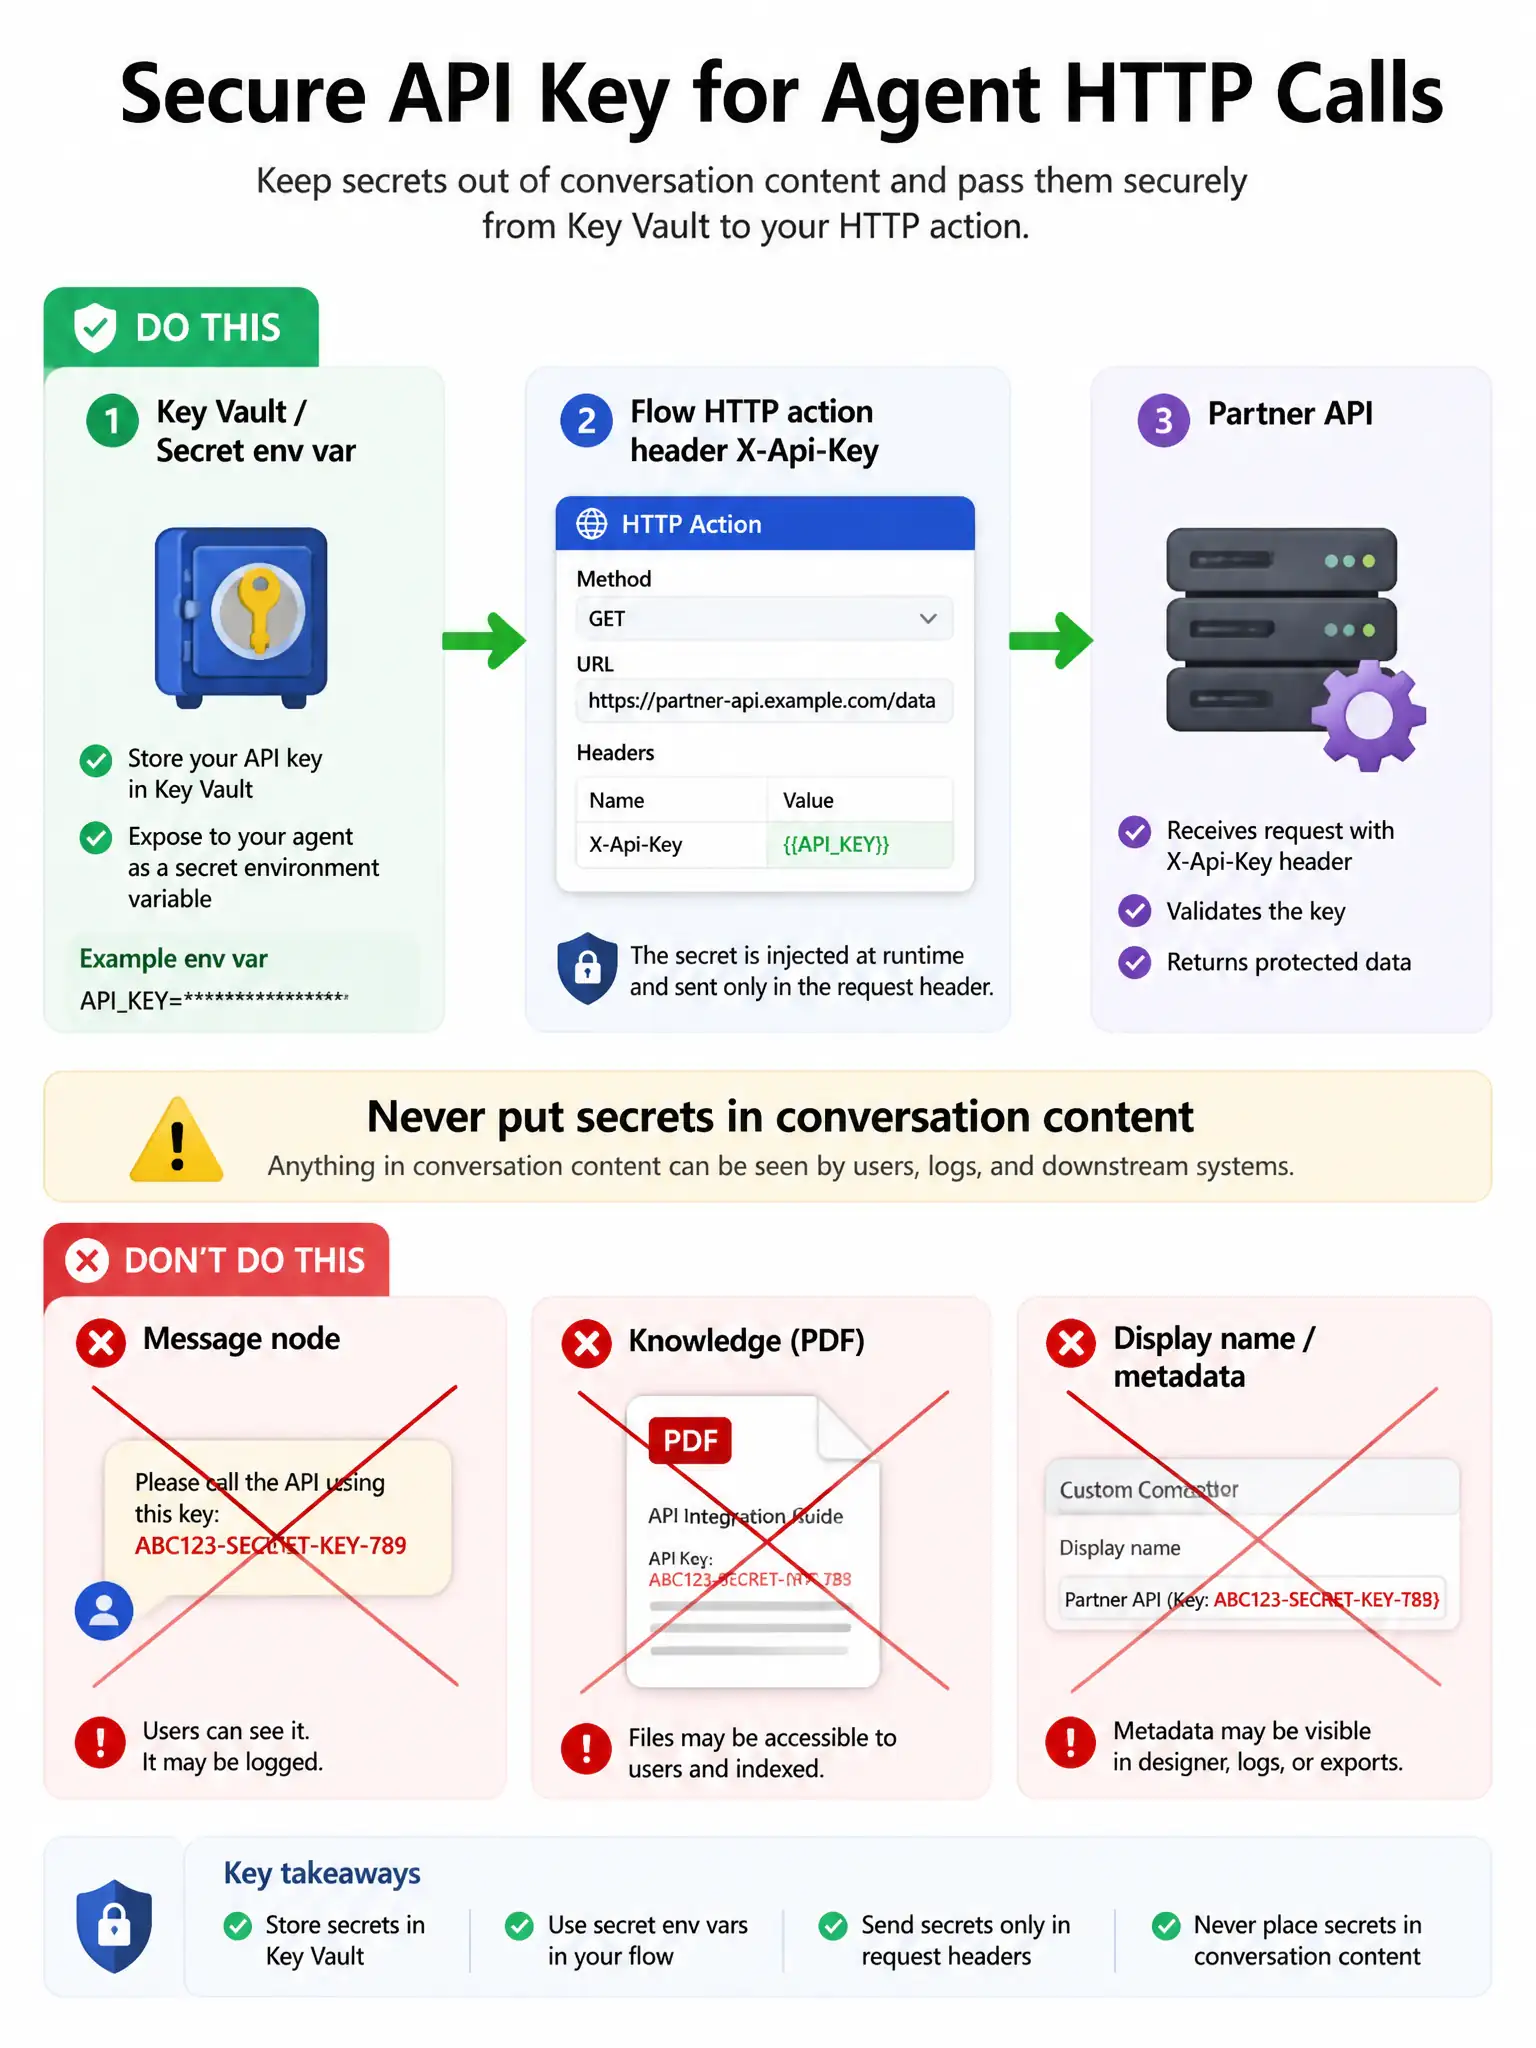
You should stash the API key in a secret-backed environment variable or Azure Key Vault–integrated secret configuration referenced by the flow or connector. Don't hard-code it in topic messages, display names, or knowledge PDFs. That keeps the key out of user-visible content and lets you rotate it without rewriting topics.
Full Explanation
API keys are secrets. Power Platform guidance is to use secret environment variables (Key Vault integration patterns) or secure custom connector authentication configuration, never user-visible content. Store the API key in a secret-backed environment variable or Azure Key Vault–integrated secret configuration referenced by the flow or connector, not hard-coded in topic messages. A public Message node exposes it to end users and transcripts. The agent display name field in channel settings is not a secret store. A SharePoint knowledge PDF titled 'secrets.pdf' uploaded to generative answers may surface secrets via retrieval and is an anti-pattern. Exam tip: Secret env vars / Key Vault + connection auth settings; rotate keys without rewriting topics.