
Your security architect raises a concern: if a computer-use agent visits a malicious website during an automated session, could malware on that site compromise your corporate network? Which design feature of Copilot Studio computer use specifically addresses this threat?
Select an answer to reveal the explanation.
Short Explanation
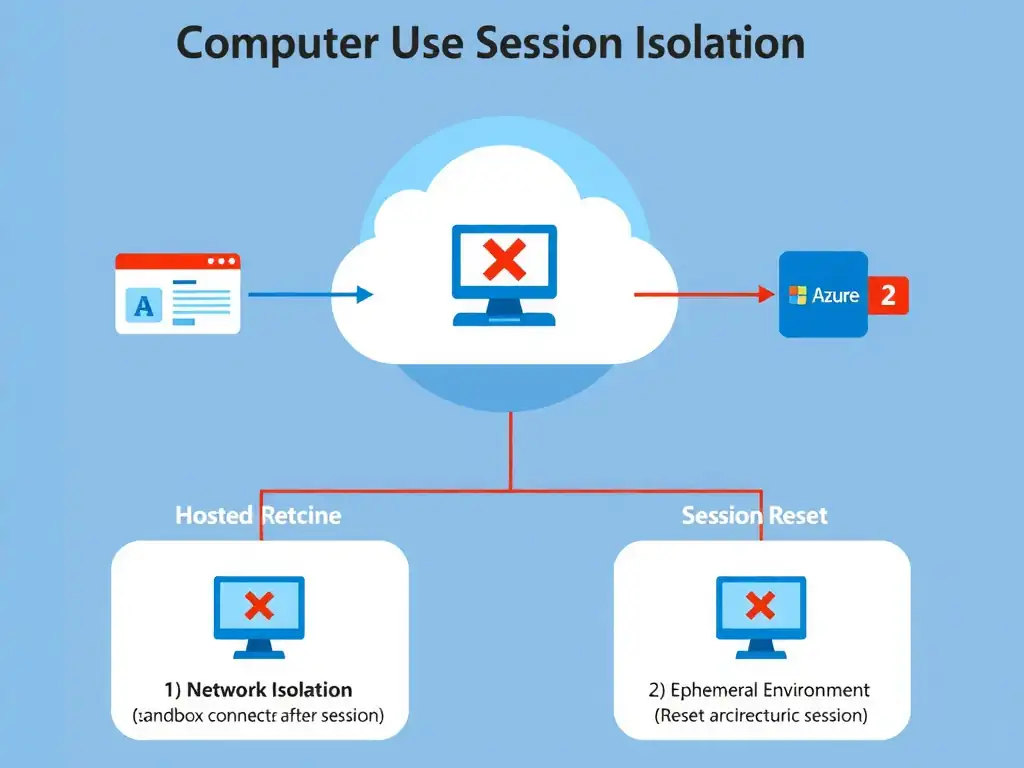
Think of the hosted machine as a disposable rental car — if something bad happens to it, you return it and get a fresh one. You're running computer use in isolated sandboxes with no path to the corporate network, and the machine image is reset after each session so nothing malicious persists.
Full Explanation
The design feature that addresses this threat is computer use sessions running on isolated hosted machines that are sandboxed from the corporate network, with the environment reset between sessions. Copilot Studio's computer use feature provisions hosted machines (virtual machines) in Microsoft's cloud infrastructure. These machines are isolated sandboxes — they are not joined to the corporate domain and have no direct network path to internal corporate resources by default. This network isolation is the primary defense against threats from malicious websites visited during a computer use session. Additionally, the hosted machine environment is ephemeral — it is reset to a clean baseline image after each session. Any malware, cookies, or artifacts from a session are wiped when the session ends, preventing persistence of threats. The read-only browser profile that prevents files from being downloaded is not the primary security isolation mechanism and is not the defining architectural feature, even though some configurations may restrict downloads. Microsoft Defender for Endpoint monitoring each computer use session in real time and blocking malware automatically is not the architectural isolation feature that addresses the corporate network compromise concern, even though Defender may be present in hosted environments. Blocking the agent's IP address from accessing external websites by default, limiting computer use to intranet sites only, would make computer use useless for most web automation scenarios because external site access is the entire point. Exam security principle for computer use: sandbox isolation + session reset = key security properties. The hosted machine is not on the corporate network; the session environment is ephemeral. These two properties together address the network compromise threat.