
A Copilot Studio developer has an 'Authenticate User' topic that collects and verifies a user's credentials. Three other topics ('Check Balance', 'Transfer Funds', 'View History') all need to run authentication before their main logic. What is the most maintainable way to implement this?
Select an answer to reveal the explanation.
Short Explanation
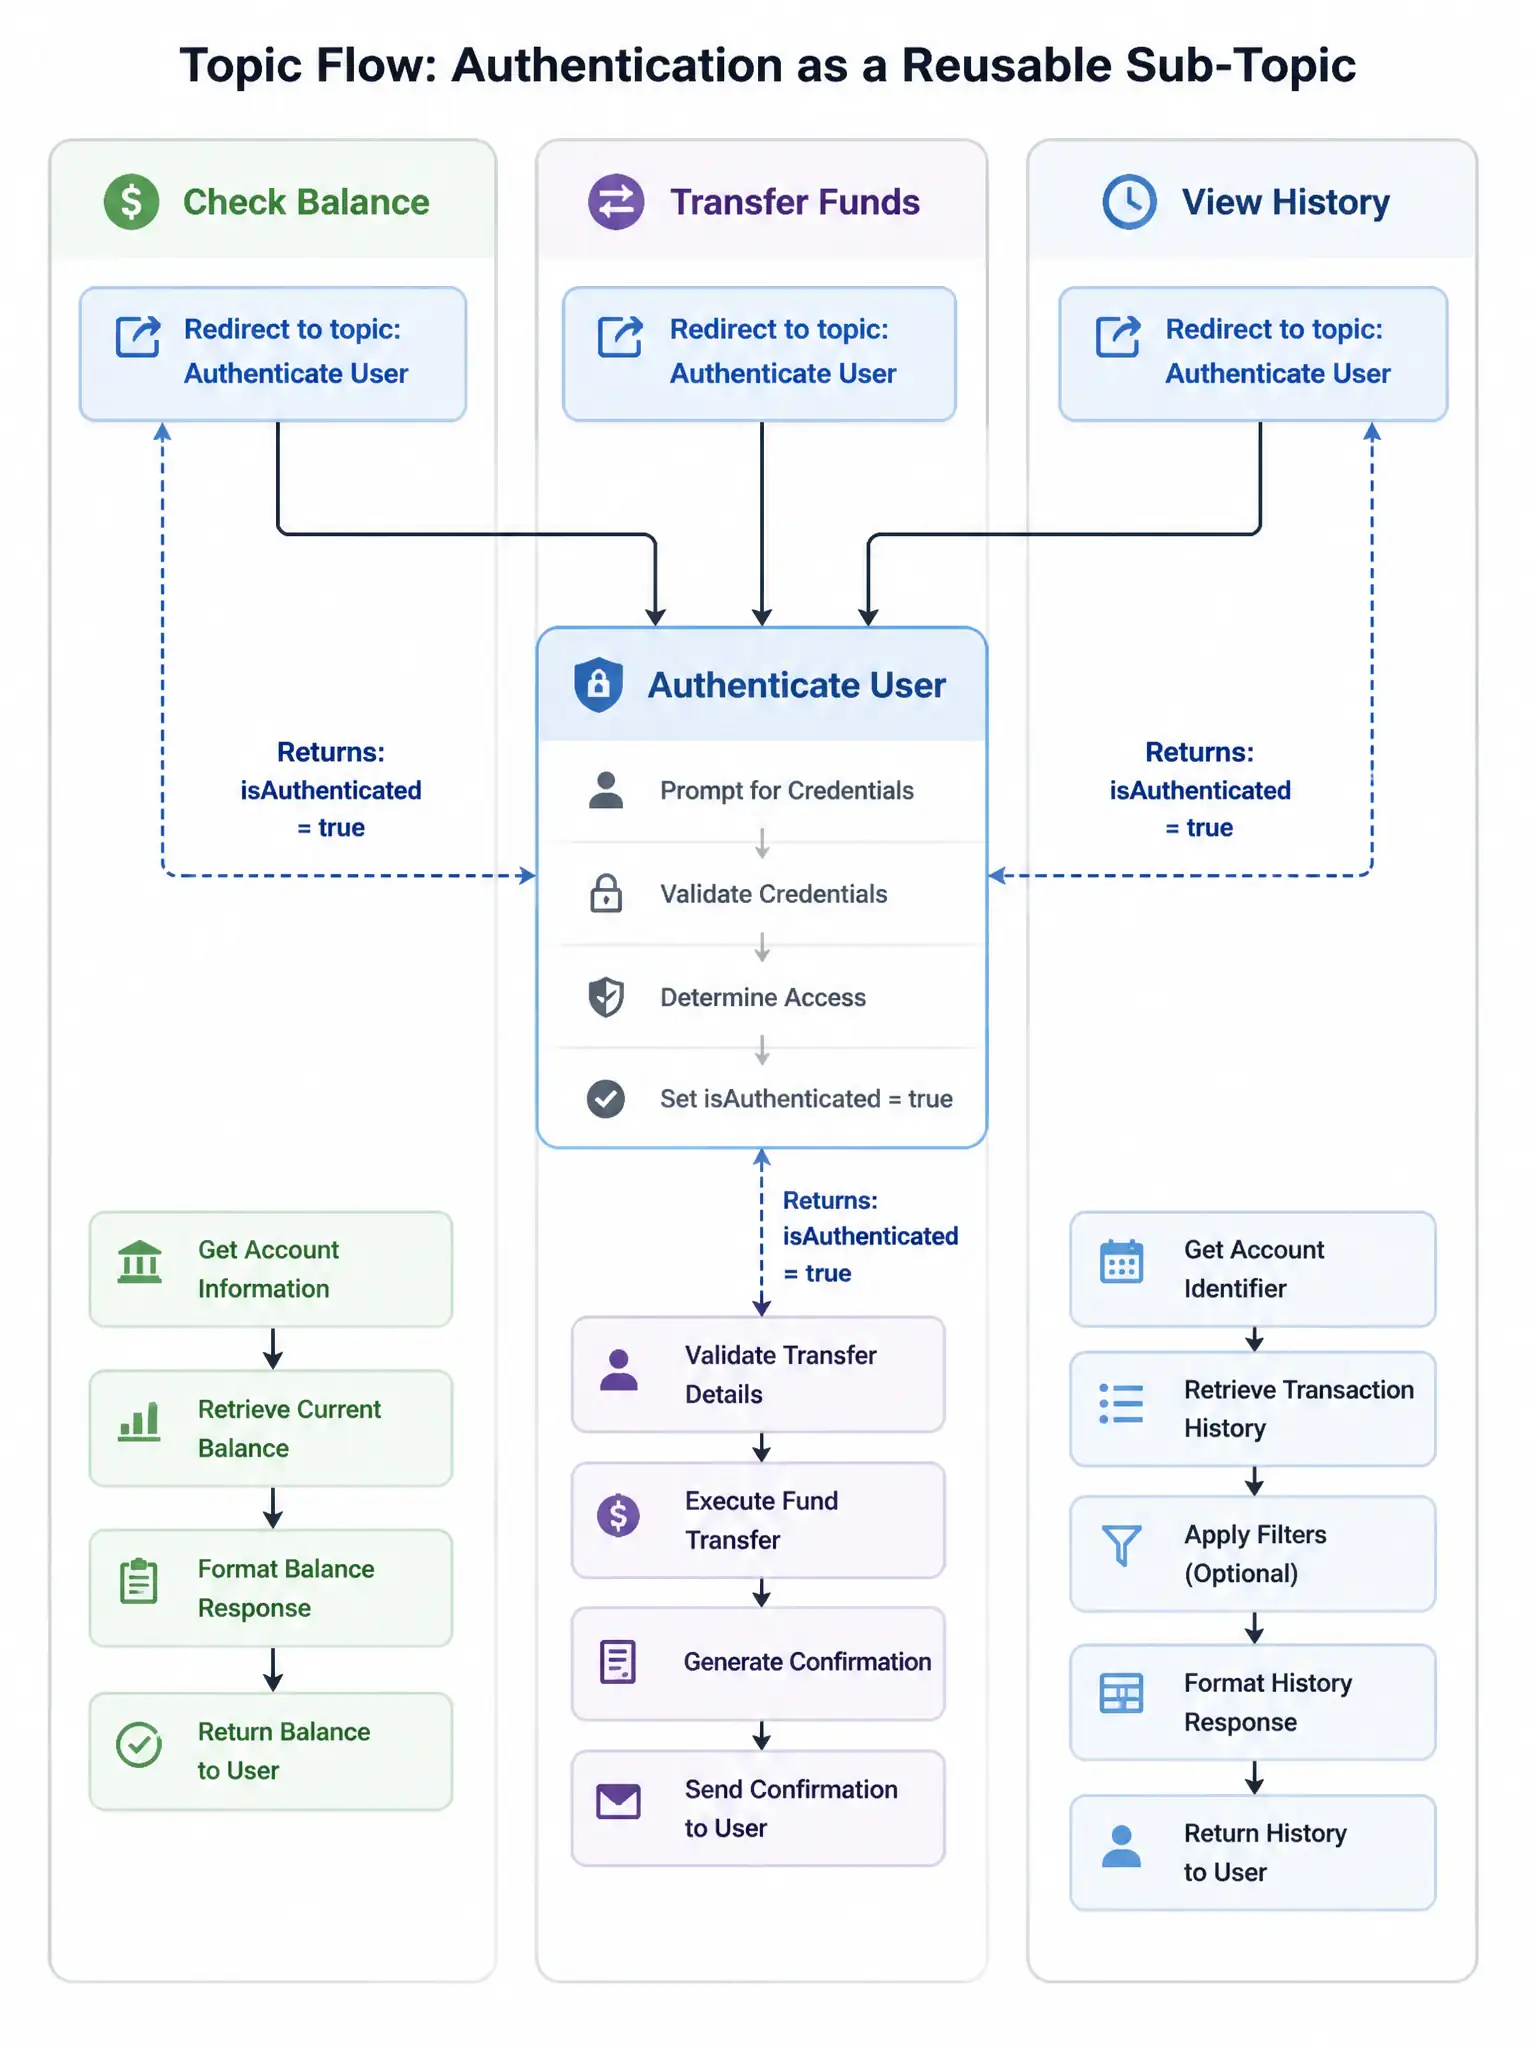
Use the redirect pattern: start each protected topic with a 'Redirect to topic' node that calls 'Authenticate User', then continue when it returns. You keep one authentication topic, so you change it once and every caller benefits.
Full Explanation
Copilot Studio supports topic composition through the 'Redirect to topic' node, which calls another topic and returns control to the calling topic when the redirected topic completes. This is the foundation of reusable topic design. The redirect-to-topic approach is correct. Each of the three financial topics starts with a 'Redirect to topic' node pointing to 'Authenticate User'. If the user isn't authenticated, the Authenticate User topic handles credential collection and verification. Upon return, the calling topic receives any variables set by the auth topic (like an authentication token or flag) and continues its main logic. If the authentication logic ever changes, the developer modifies only the 'Authenticate User' topic and all three callers are automatically updated. The copy-the-authentication-nodes approach is incorrect. Copying authentication logic into three topics creates maintenance debt: when the authentication flow changes (password policy update, new MFA requirement, etc.), the developer must remember to update all three copies. This leads to inconsistencies and bugs. The add-authentication-trigger-phrases approach is incorrect. Adding authentication trigger phrases to other topics would cause them to compete with the 'Authenticate User' topic for natural-language understanding matching. Redirect is the correct mechanism for topic composition — it is explicit, not matching-based. The conversation-start-system-topic approach is incorrect. Running authentication at conversation start is appropriate for some agents (especially those that always require login), but it forces authentication even for users who only want to perform actions that don't require it. The redirect pattern allows conditional authentication only when protected topics are accessed.