
A compliance team must be able to reconstruct which tools an AI assistant invoked, with which inputs, and when. According to the tools specification, which component SHOULD keep this record?
Select an answer to reveal the explanation.
Short Explanation
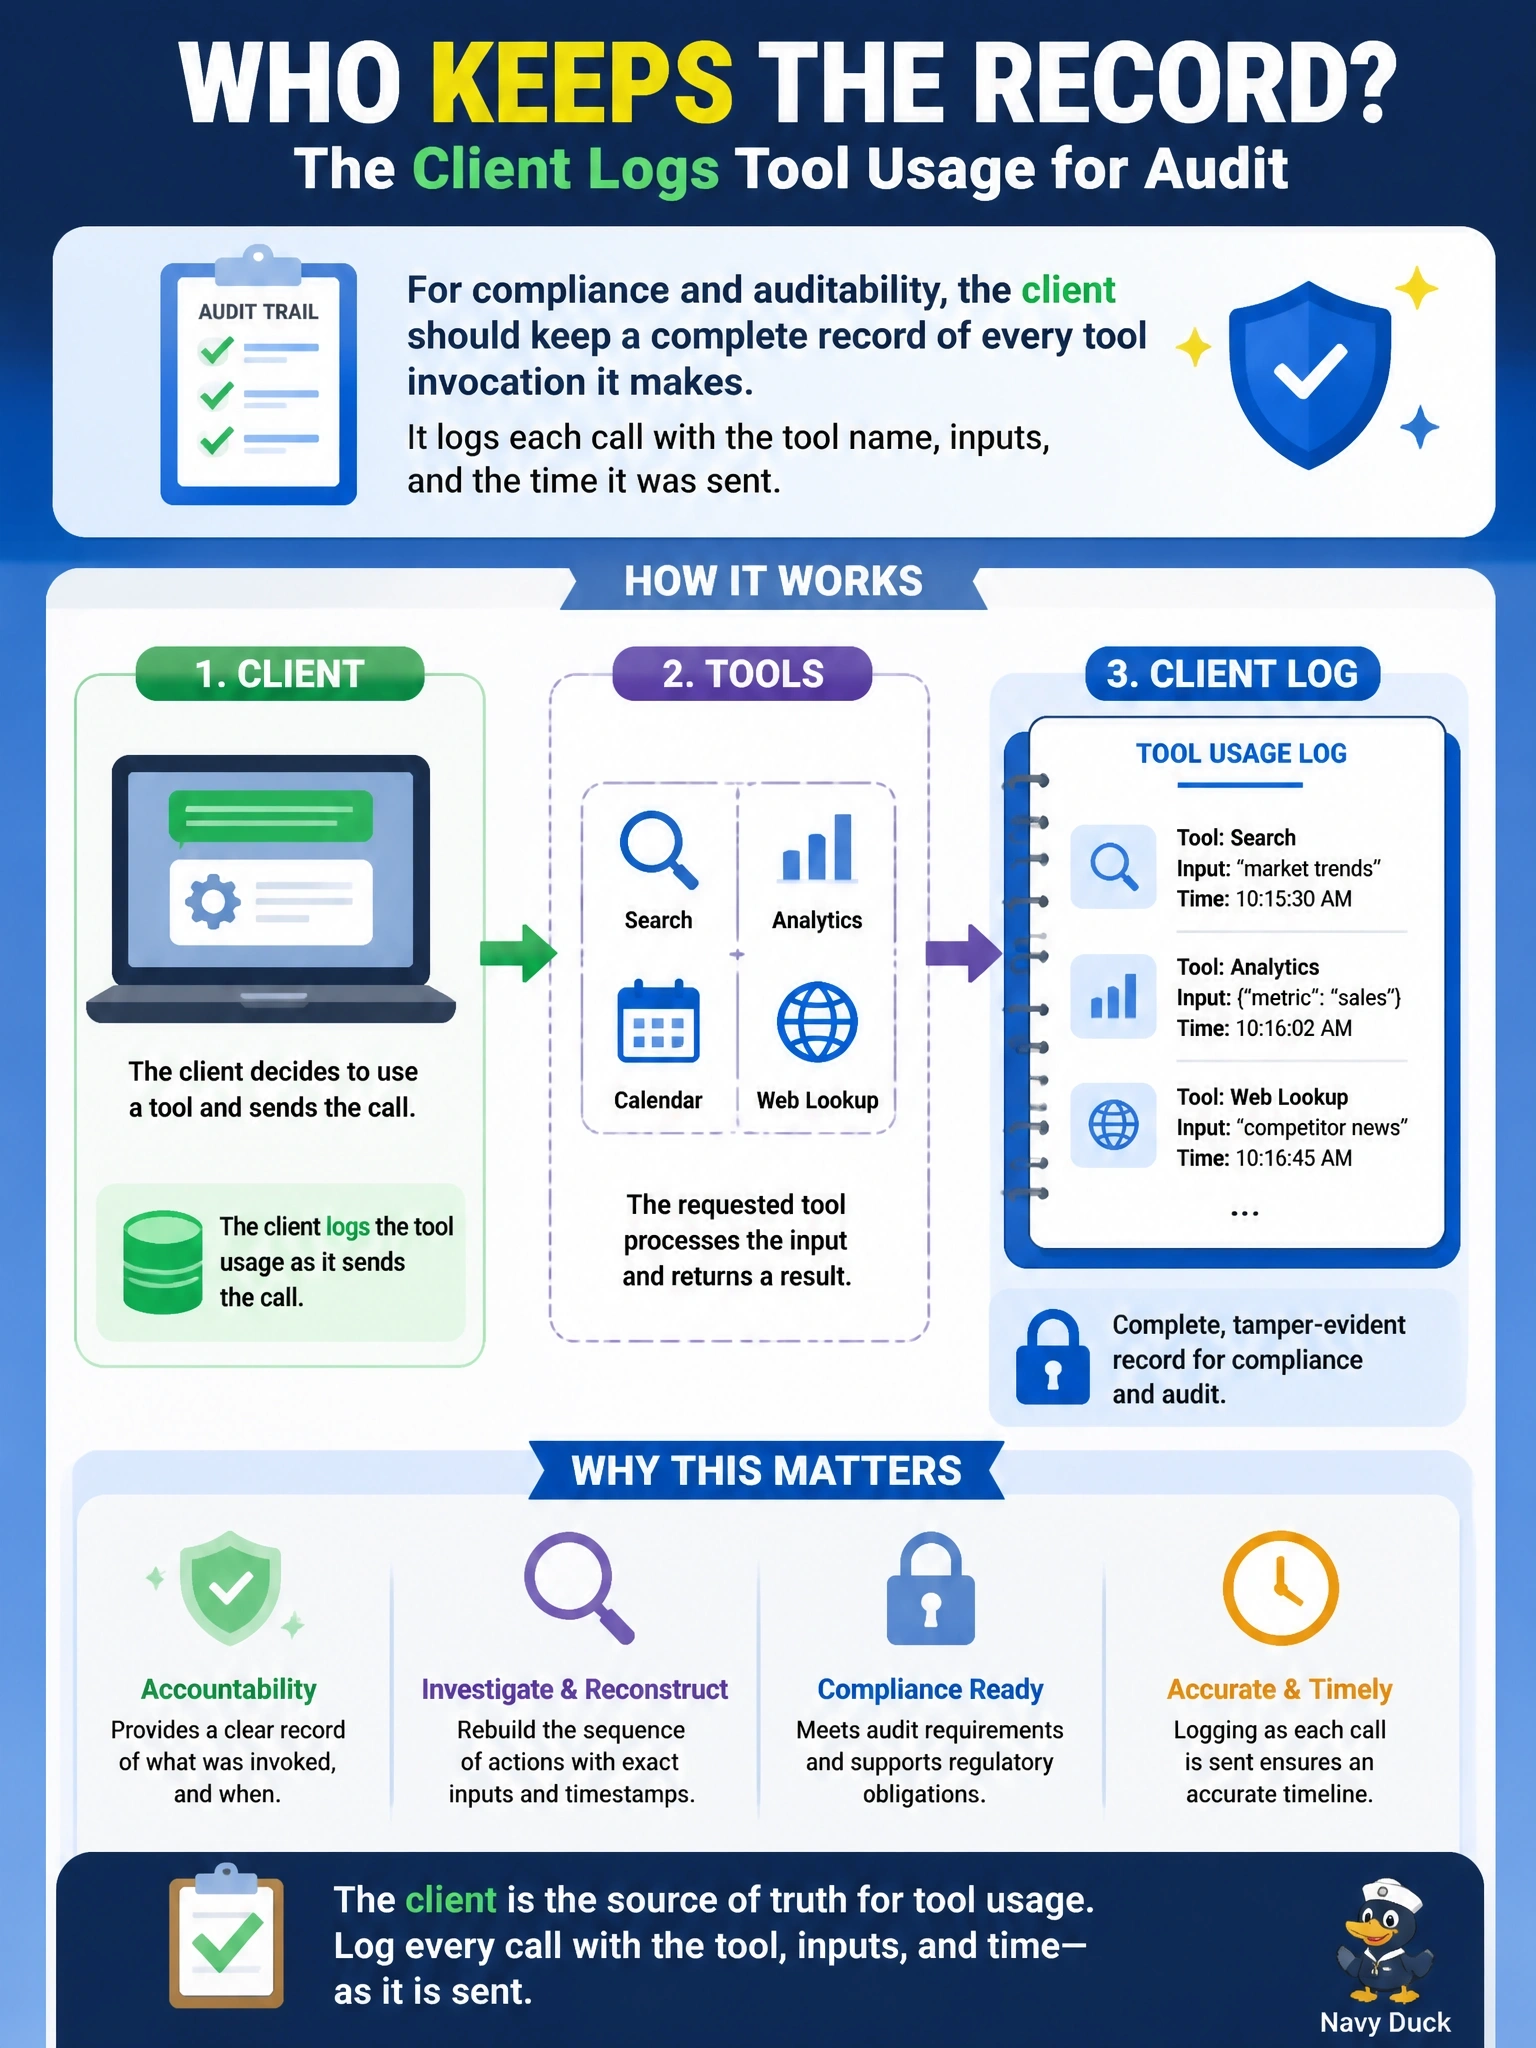
The client is the one standing at the till for every transaction, so it's the natural place for the receipt book. The tools spec says clients should log tool usage for audit. A model's summary is a story, not a record, and the authorization server never sees your tool arguments.
Full Explanation
The tools specification's security considerations list what clients SHOULD do: prompt for confirmation on sensitive operations, show tool inputs to the user before calling the server, validate tool results before passing them to the model, implement timeouts, and log tool usage for audit purposes. The client sees every tools/call it sends, including the tool name and arguments, so it is the component positioned to keep an authoritative record. A model-written summary is generated text that can omit or misstate calls and is not an audit record. notifications/message belongs to the Logging feature, which is deprecated in 2026-07-28, is emitted only when a request sets a log level, and clients MAY present or discard such messages rather than being required to keep them. The authorization server issues tokens; it sees scopes and resource indicators during authorization, never the arguments of individual tool calls. Exam caveat: servers keep their own operational logs too, and organizations managing local servers are advised to log which server, which tool and when on managed machines, but the specification's audit SHOULD for tool usage sits with the client. Operational check: run a test task, then confirm the client's audit log lists each tool name, its arguments, the timestamp and the outcome.