
A client team proposes automatically approving every tool from any server whose serverInfo name contains the word Official. Why is this a poor design?
Select an answer to reveal the explanation.
Short Explanation
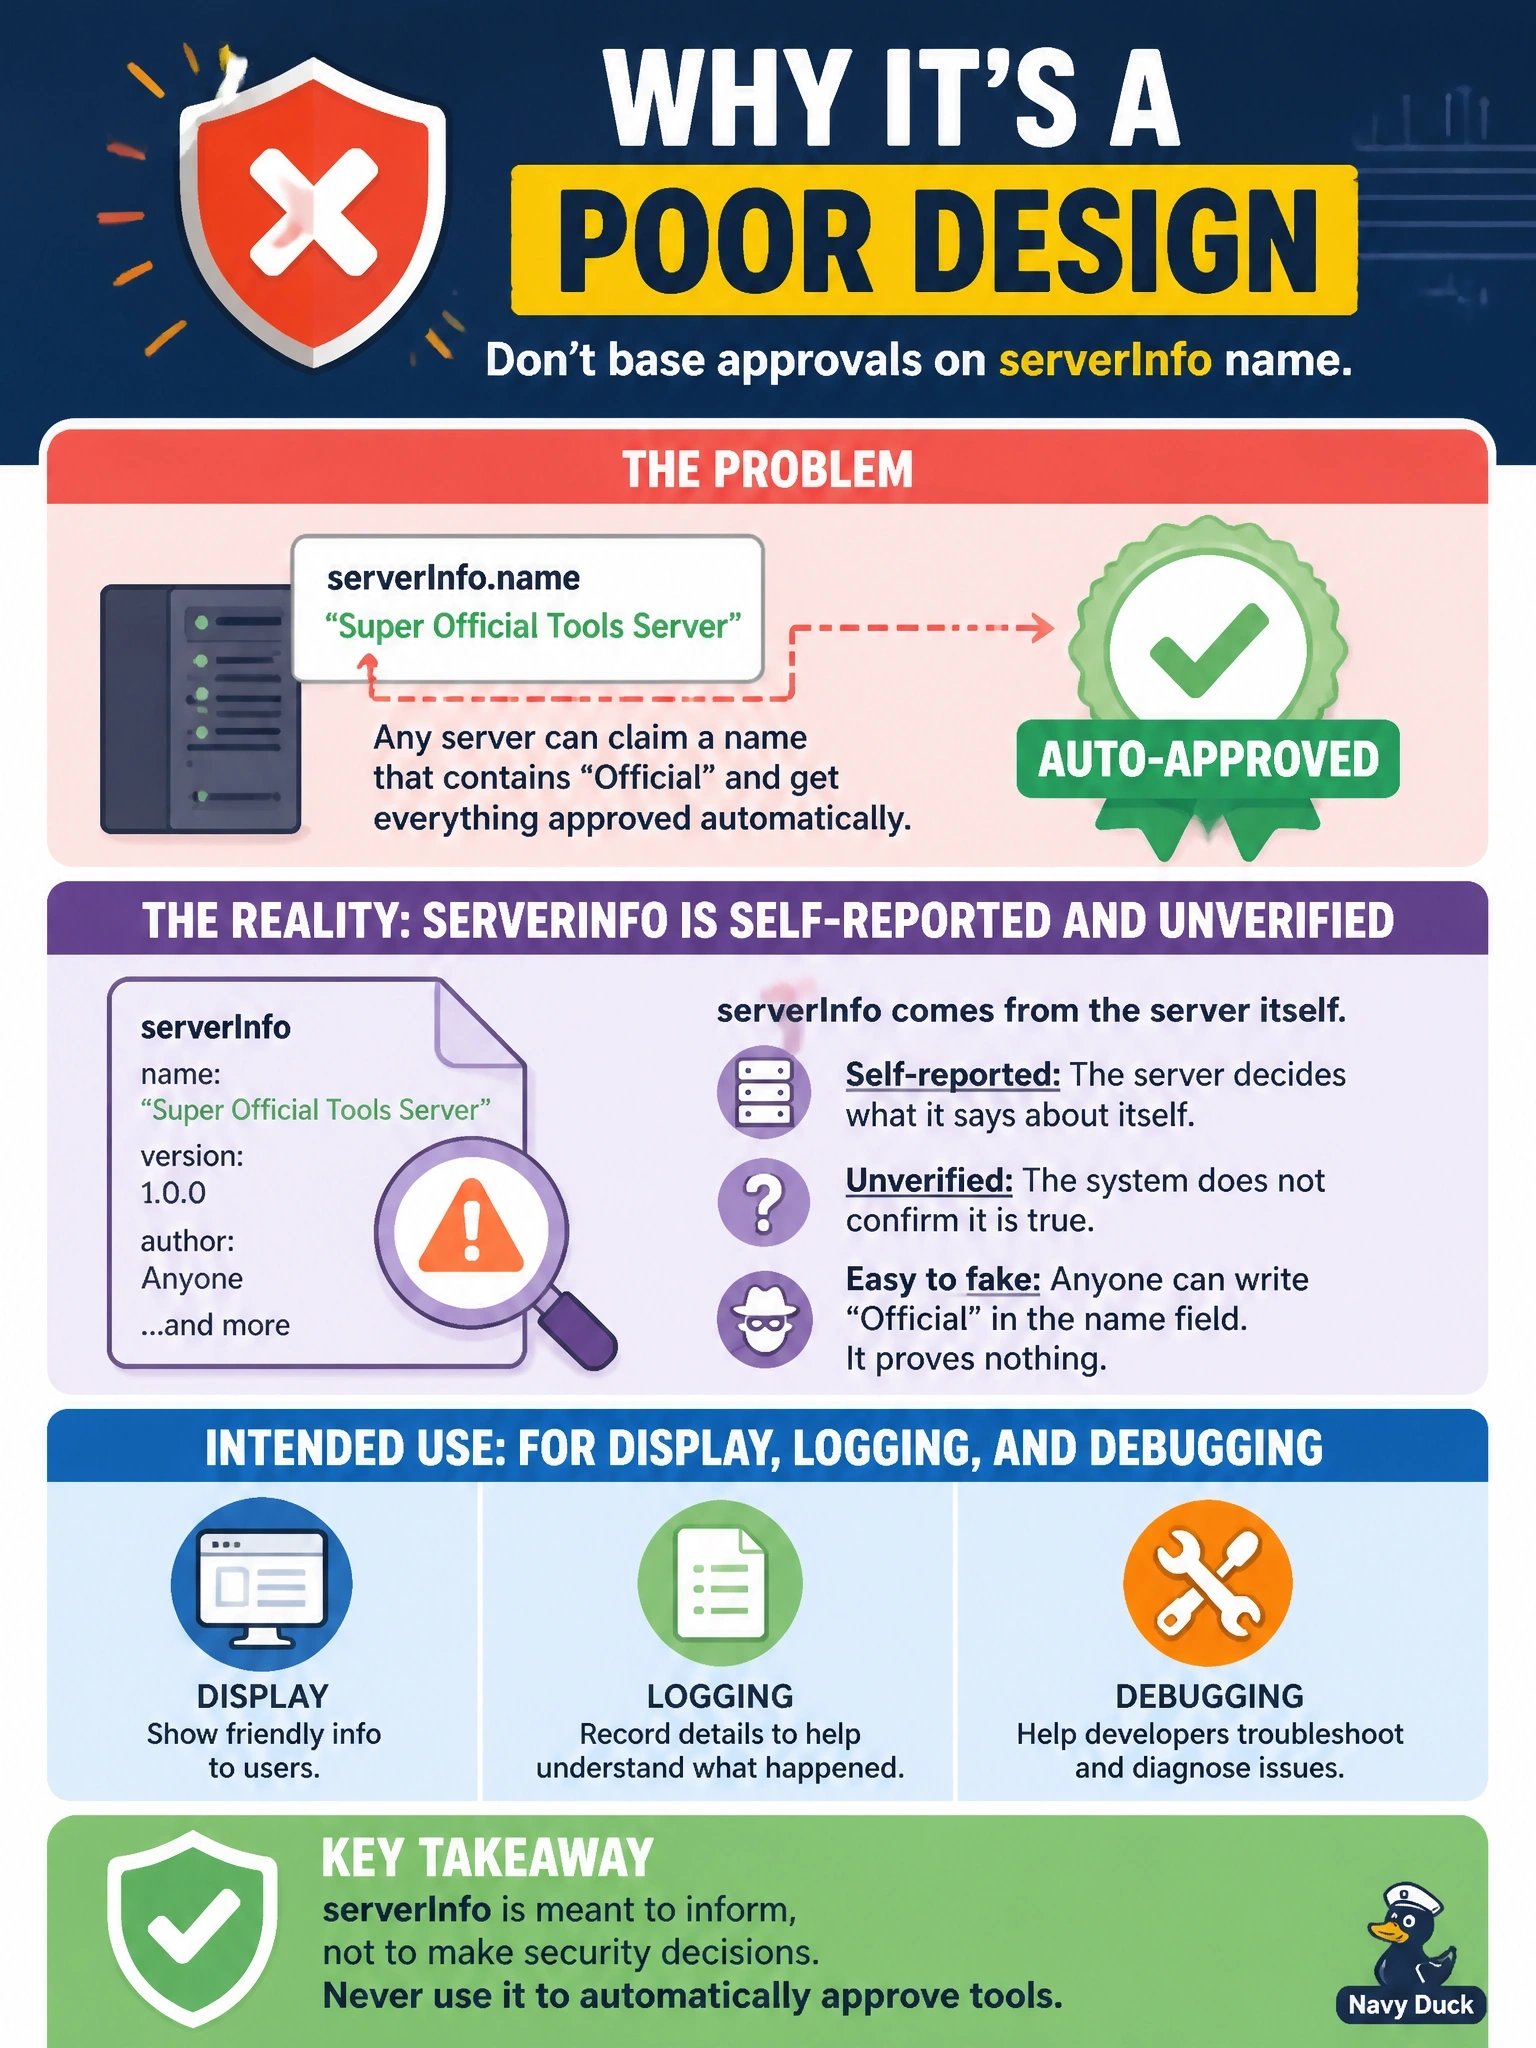
Anyone can write 'Official' on a name tag. serverInfo is just the server describing itself, so you use it for display and logs, never as a trust badge. Trust has to come from somewhere you actually verify.
Full Explanation
In the 2026-07-28 revision, servers SHOULD include io.modelcontextprotocol/serverInfo in each result's _meta to identify themselves without relying on connection state, and clients SHOULD include clientInfo in each request. The specification is explicit that both values are self-reported by the sender and not verified by the protocol. They are intended for display, logging and debugging, implementations SHOULD NOT use them to change behavior, and they SHOULD NOT be relied upon for security decisions. A malicious server can claim any name it likes, so auto-approval keyed to the word Official would let an attacker bypass the human-in-the-loop controls the host is supposed to provide. Saying serverInfo appears only during initialize describes the legacy handshake; in this revision it travels in result _meta and from server/discover. No registry signature is attached to serverInfo, so there is no prior validation that the check could duplicate. serverInfo is protocol metadata delivered to the client, not something only the model sees, which is exactly why a client could misuse it. Exam caveat: the same untrusted status applies to tool annotations unless they come from a trusted server. Operational check: confirm approval policy is keyed to administrator-configured server entries and verified credentials, and that serverInfo is used only in logs and the user interface.