
A metro EBGP Clos design assigns a private ASN per leaf. What concept does that ASN allocation illustrate?
Select an answer to reveal the explanation.
Short Explanation
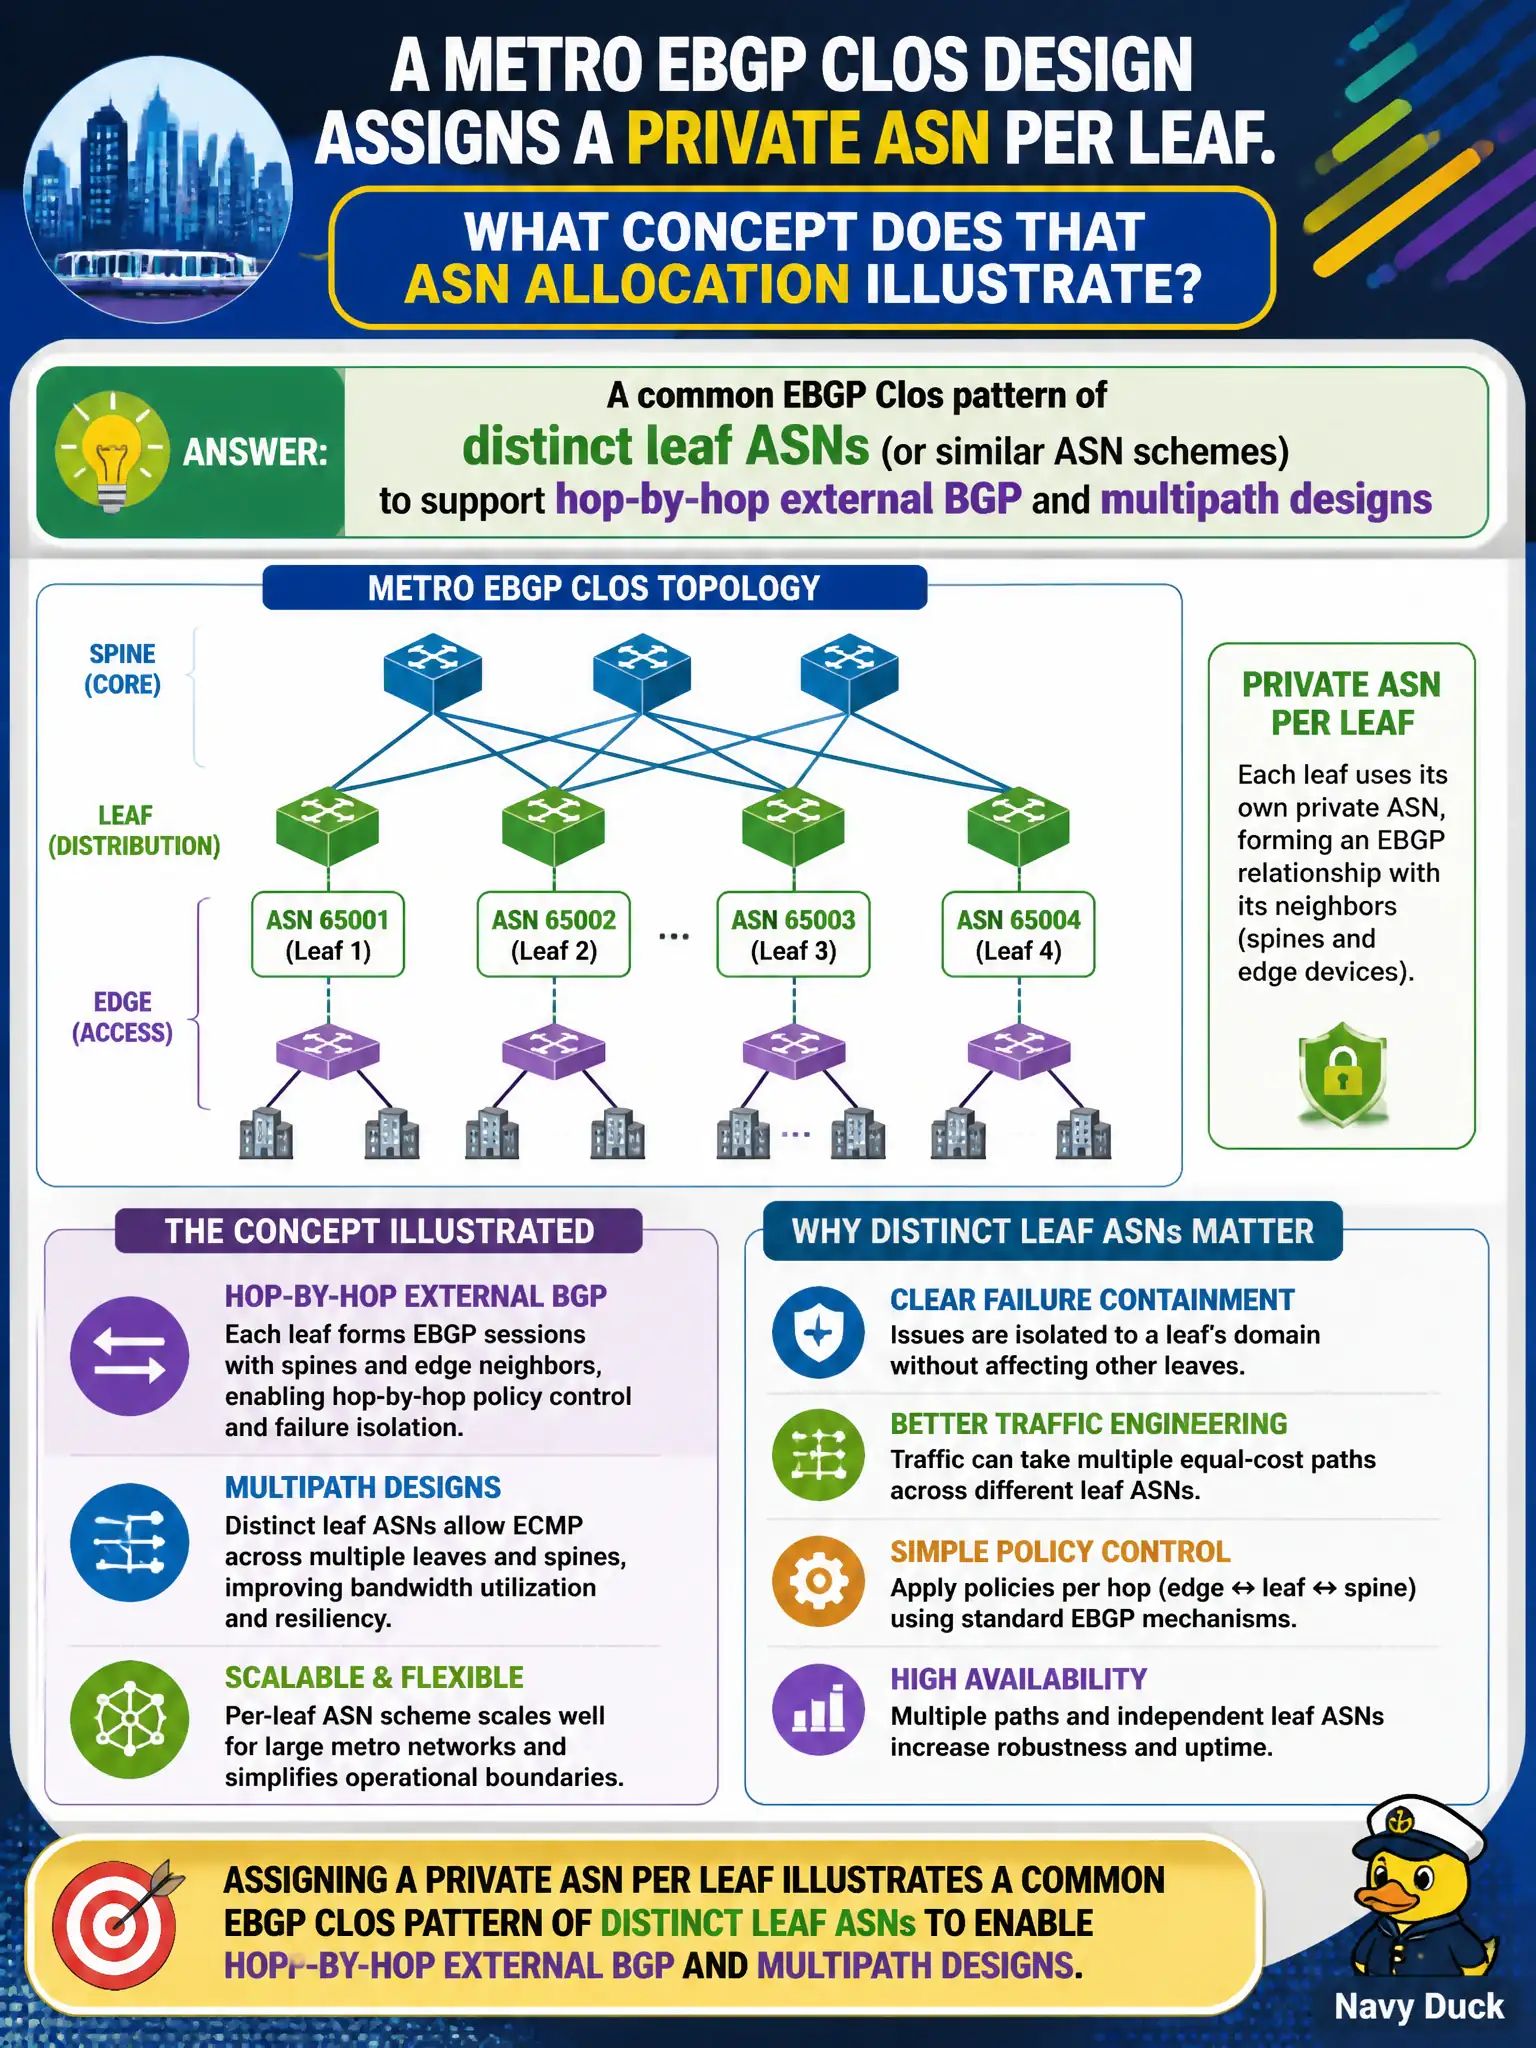
Giving each leaf its own private ASN is a familiar EBGP Clos phonebook trick—external BGP hop by hop without inventing public ASN paperwork. It is a pattern family, not a law that forbids other designs. Spines get ASNs in the plan too.
Full Explanation
Assigning a private ASN per leaf illustrates a common EBGP Clos pattern of distinct leaf ASNs (or similar schemes) supporting hop-by-hop external BGP and multipath designs in metro fabrics. Leaves need not use the same ASN as attached servers. Per-leaf ASN does not prove IBGP route reflection is mandatory in every Juniper fabric. Private ASNs are not forbidden on spines and reserved only for border routers. Exam caveat: It is a pattern family, not the only valid template; document ASN plan with multipath/policy. Operational check: Map leaf and spine ASNs and verify EBGP sessions and multipath install as designed. In civic data-center operations, record the expected CLI or collector evidence for this concept so the next on-call engineer can validate fabric behavior without re-deriving the design under incident pressure. In civic data-center operations, record the expected CLI or collector evidence for this concept so the next on-call engineer can validate fabric behavior without re-deriving the design under incident pressure. In civic data-center operations, record the expected CLI or collector evidence for this concept so the next on-call engineer can validate fabric behavior without re-deriving the design under incident pressure.