
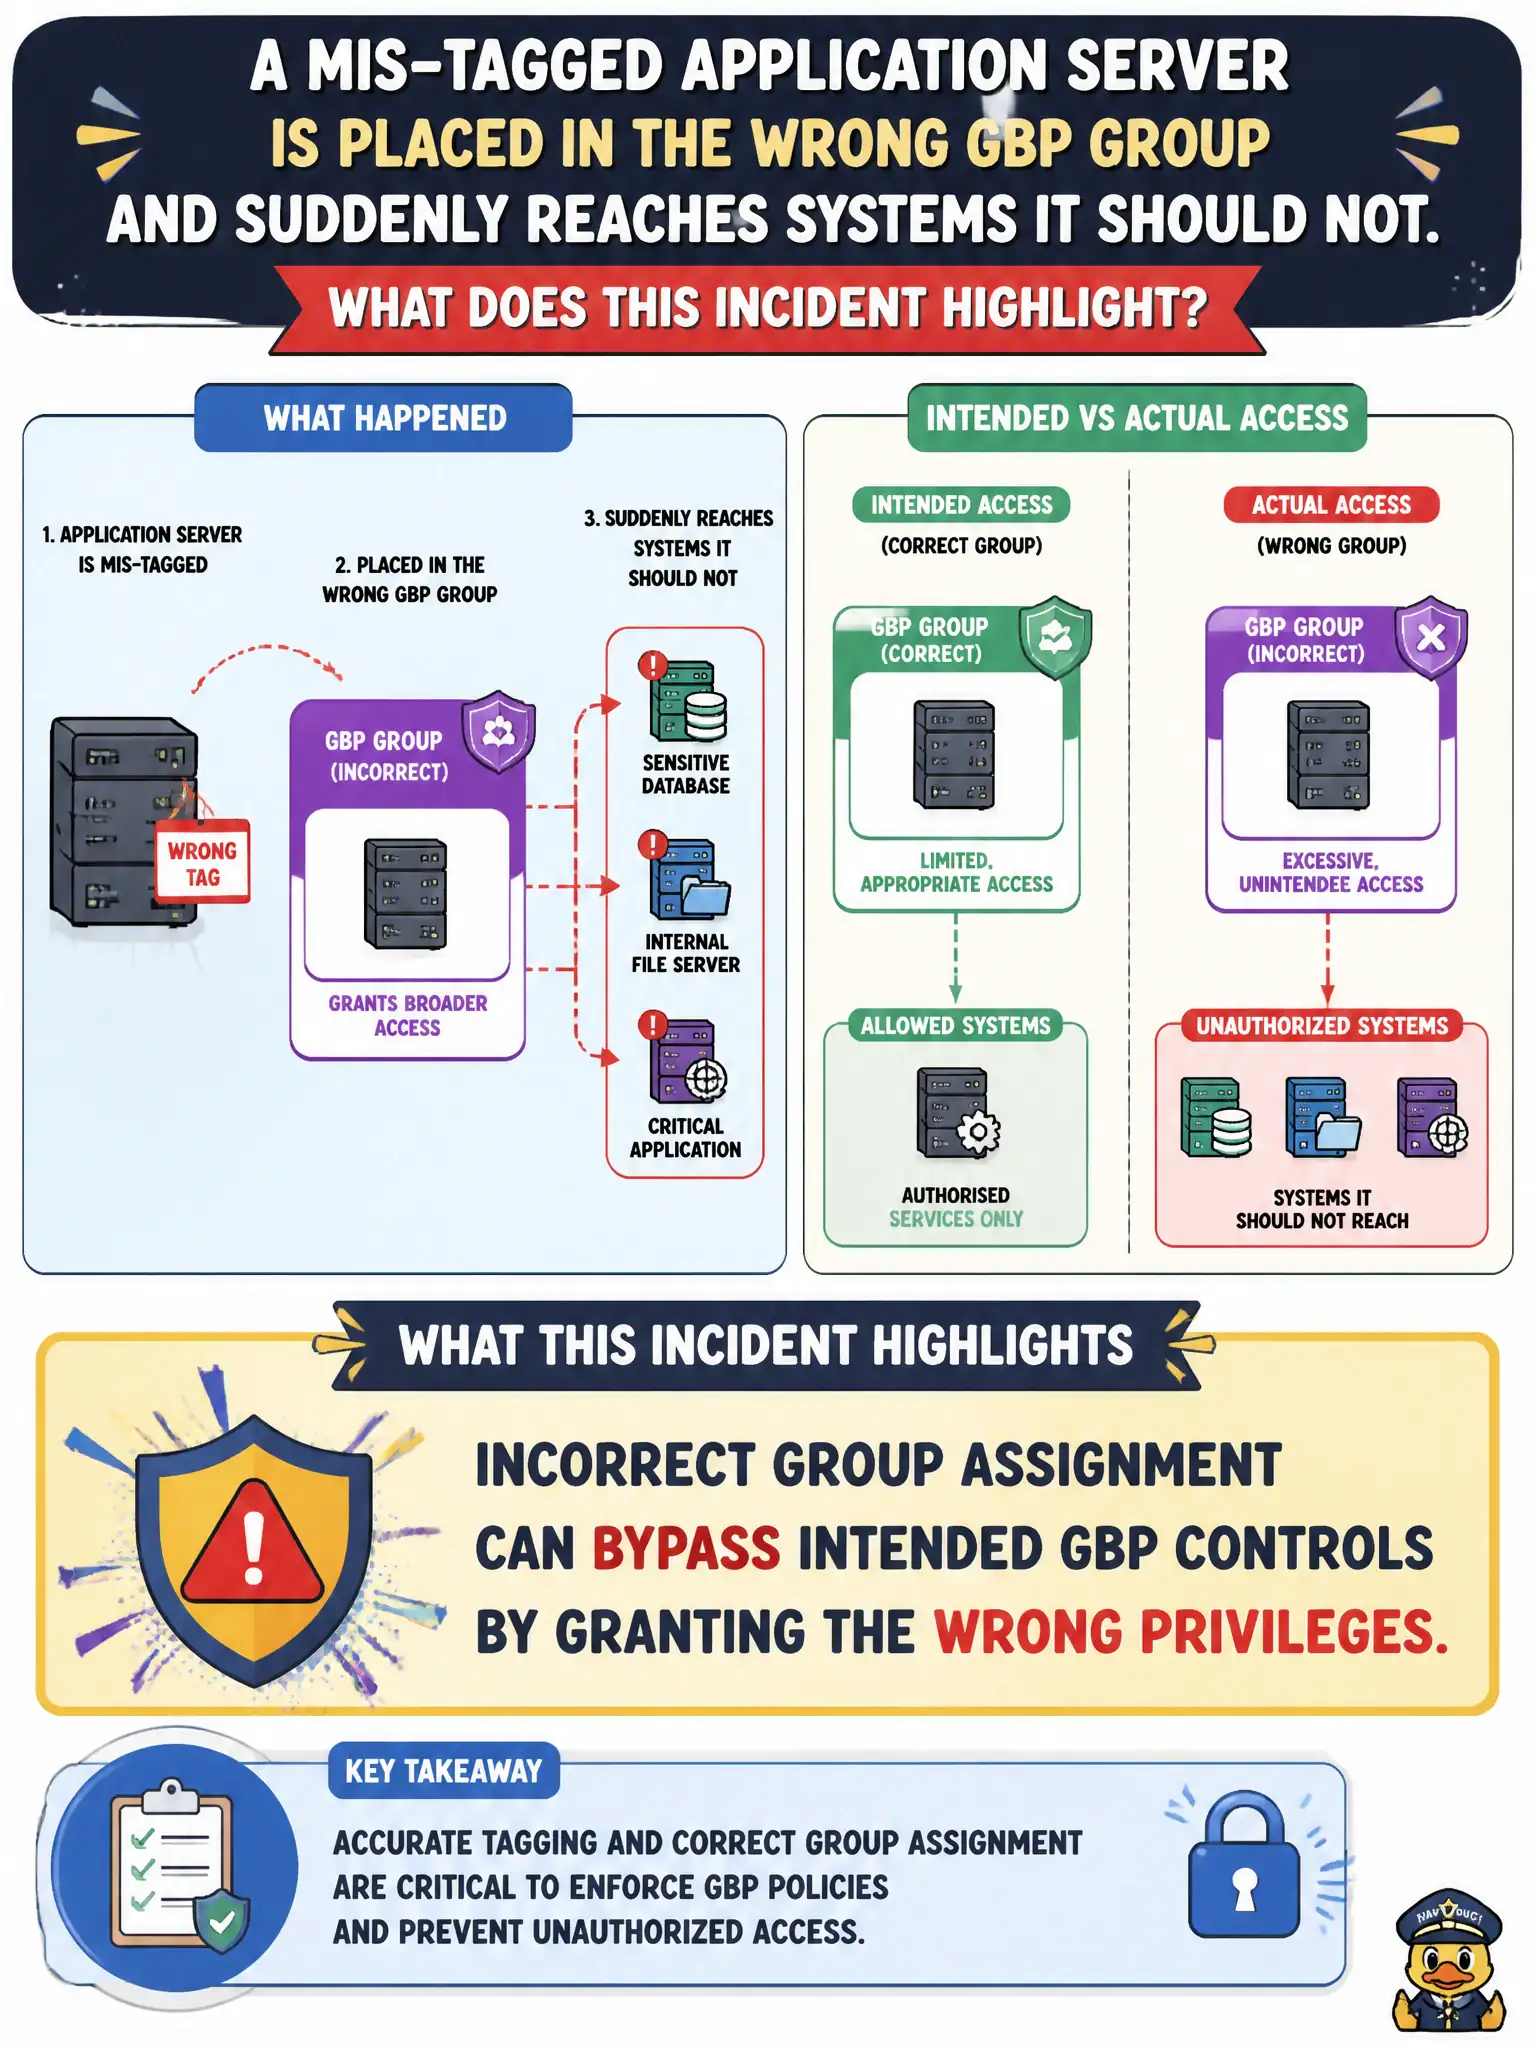
A mis-tagged application server is placed in the wrong GBP group and suddenly reaches systems it should not. What does this incident highlight?
Select an answer to reveal the explanation.
Short Explanation
Wrong badge, wrong doors. If the server wears the finance club tag by mistake, policy treats it like finance. Classification accuracy is the load-bearing beam under GBP.
Full Explanation
When a mis-tagged application server is placed in the wrong GBP group and suddenly reaches systems it should not, the incident highlights that incorrect group assignment can bypass intended GBP controls by granting the wrong privileges. GBP enforcement keys off membership, so a server tagged as finance instead of printers inherits finance east-west rights and defeats the municipality’s least-privilege design even though the fabric remains otherwise healthy. GBP does not ignore group membership once EVPN Type-2 routes exist; reachability plus a wrong tag is exactly how unauthorized sessions succeed. Incorrect classification is not harmless because underlay filters supposedly override all GBP results—operators cannot assume underlay ACLs silently fix bad tags. Mis-tags are not limited to telemetry dashboards; they change data-plane policy outcomes for civic workloads. Exam caveat: treat classification accuracy as a first-class security control equal to writing the inter-group rules themselves. Operational check: inventory GBP group membership for the affected server, correct the tag through the identity or mapping source of truth, clear stale state if required, retest the unauthorized path to confirm deny, and add a monitoring check that alerts on unexpected group assignments for regulated municipal tiers.