
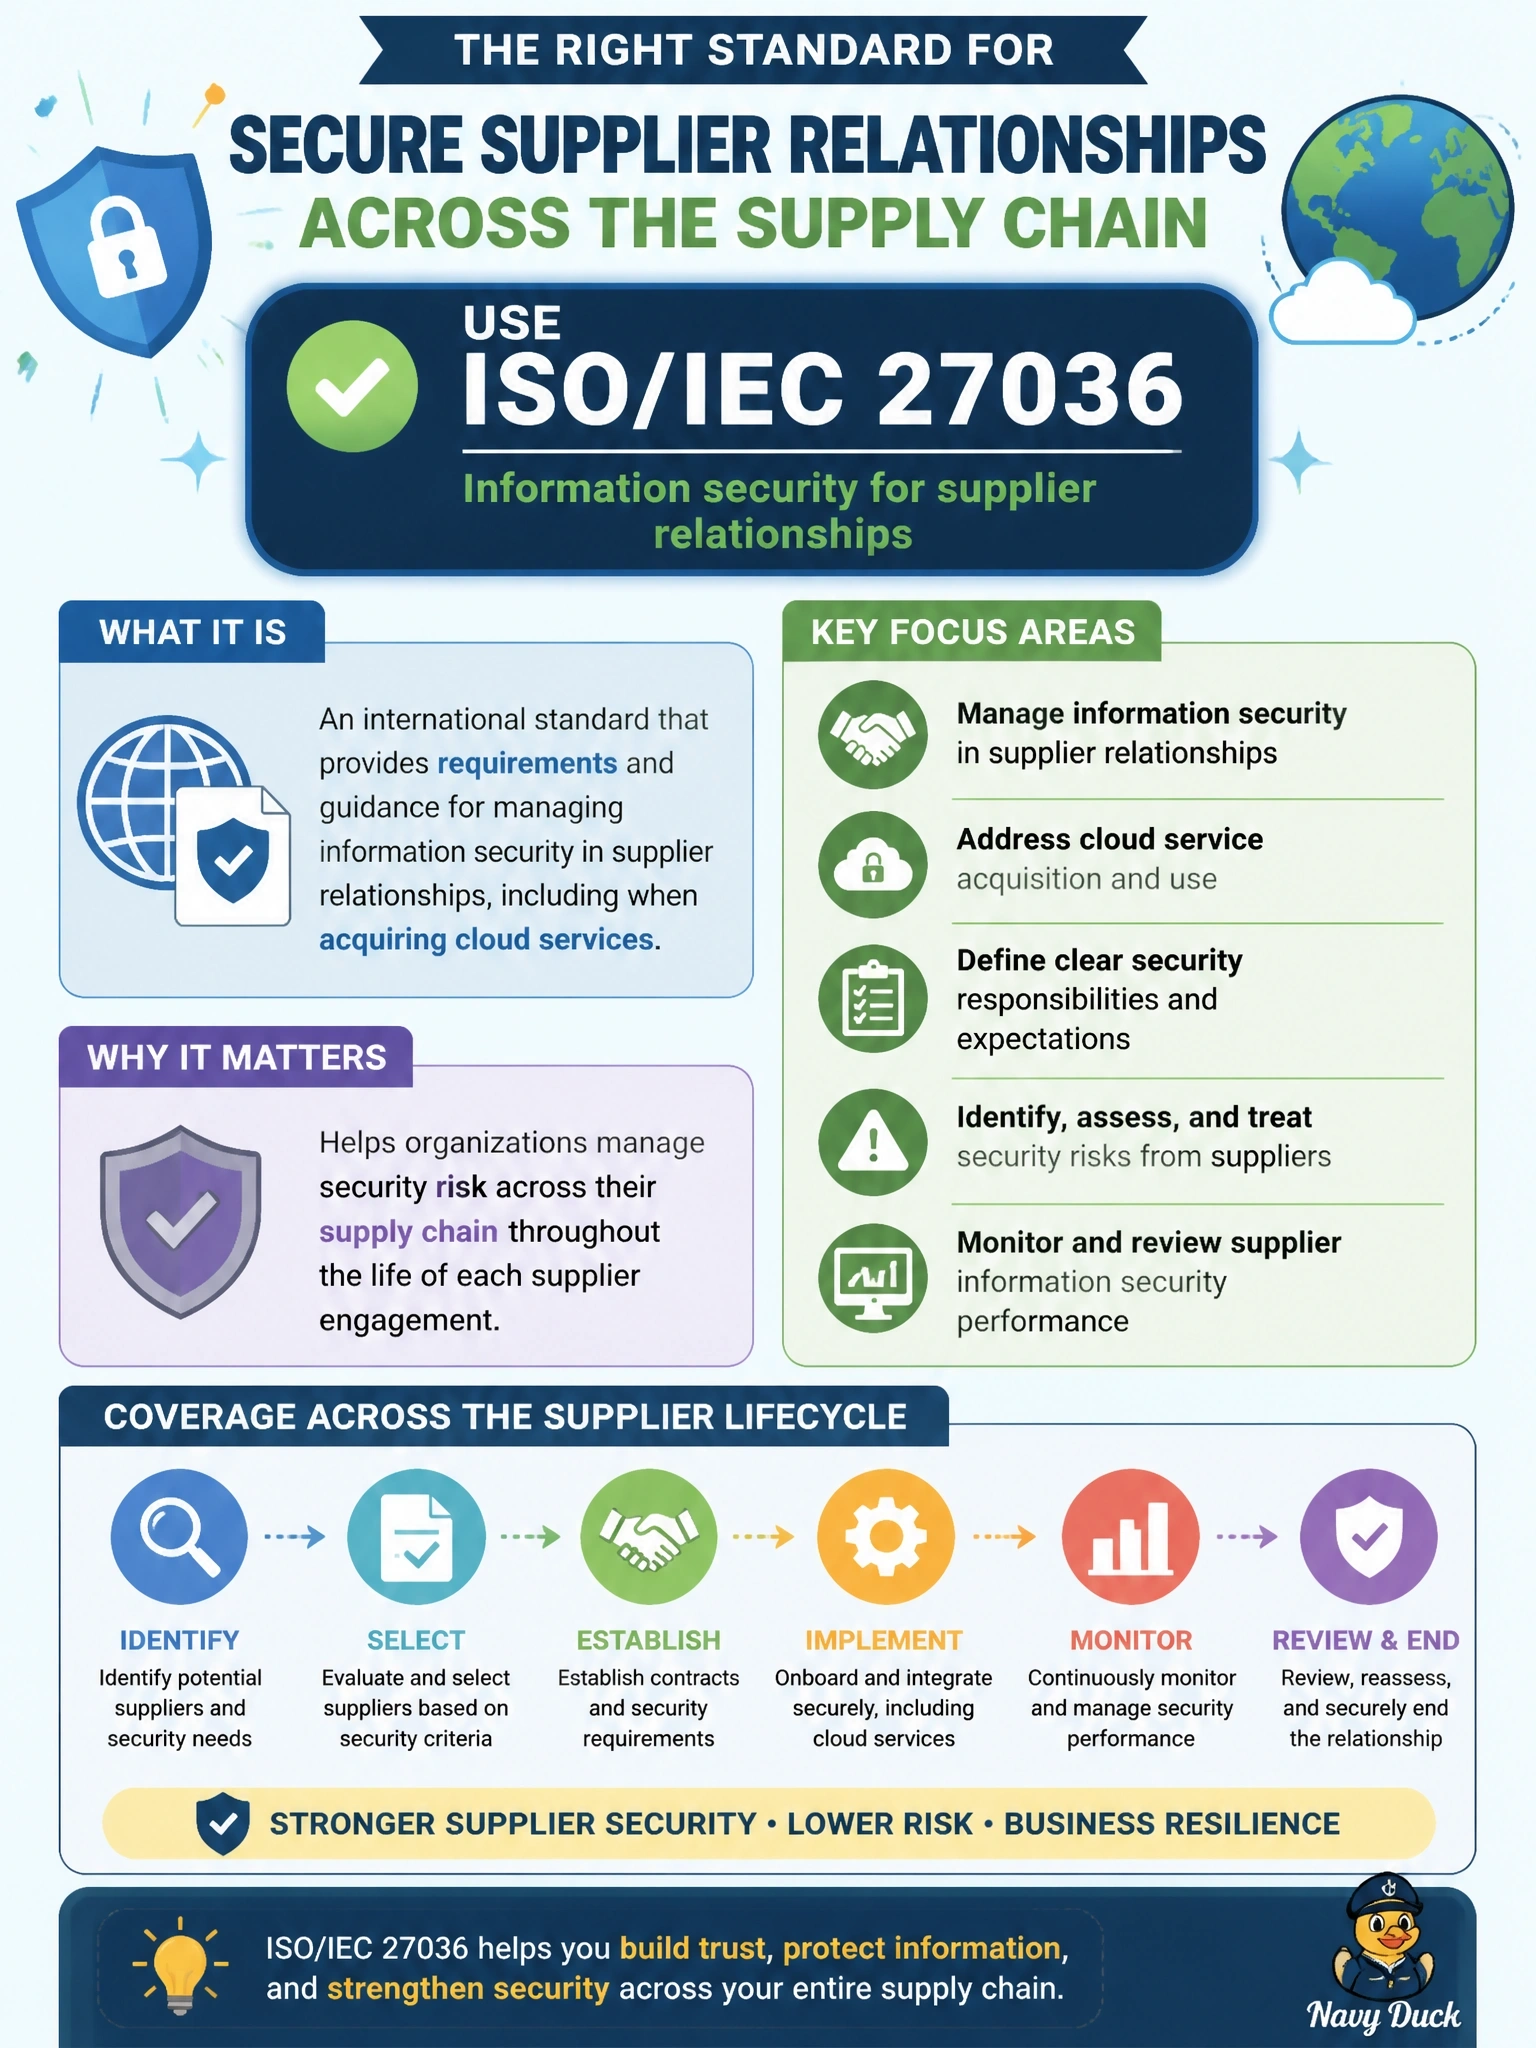
A company wants an international standard that addresses information security in supplier relationships, including acquiring cloud services, so it can manage security risk across its supply chain throughout the life of each supplier engagement. Which standard should it use?
Select an answer to reveal the explanation.
Short Explanation
Supplier relationships and supply chain security point to one number: 27036. It walks you through managing security with suppliers from selection to exit, and it even has a part dedicated to cloud services. The other numbers are real standards, just for eDiscovery, cloud PII and service management.
Full Explanation
ISO/IEC 27036 is a multipart standard on information security for supplier relationships. It provides an overview and concepts, requirements for defining and managing security in supplier relationships across their lifecycle, from planning and selection through agreement, management and termination, guidance on ICT supply chain security and a part addressing the security of cloud services acquired from suppliers. It thus covers flow-down of requirements to subcontractors and ongoing supplier monitoring. ISO/IEC 27050 addresses electronic discovery, the identification, preservation, collection and production of electronically stored information for legal proceedings, which is unrelated to supplier management. ISO/IEC 27018 is a code of practice for protecting personally identifiable information in public clouds acting as PII processors; it governs a provider's privacy controls rather than how a customer manages its suppliers. ISO/IEC 20000-1 specifies requirements for a service management system, covering how services are planned, delivered and improved; it touches supplier management as a process but does not focus on information security in supplier relationships. Exam caveat: ISO/IEC 27036 provides guidance and requirements for the relationship, not a certification of the supplier itself. Operational check: confirm supplier contracts and onboarding procedures reference ISO/IEC 27036 security requirements and include exit and monitoring steps.