
A vendor provides a SOC 2 report in which the auditor opines on the suitability of the design of controls as of a single specific date. The customer's risk committee needs evidence that those controls actually operated effectively throughout the past year. What should the customer request?
Select an answer to reveal the explanation.
Short Explanation
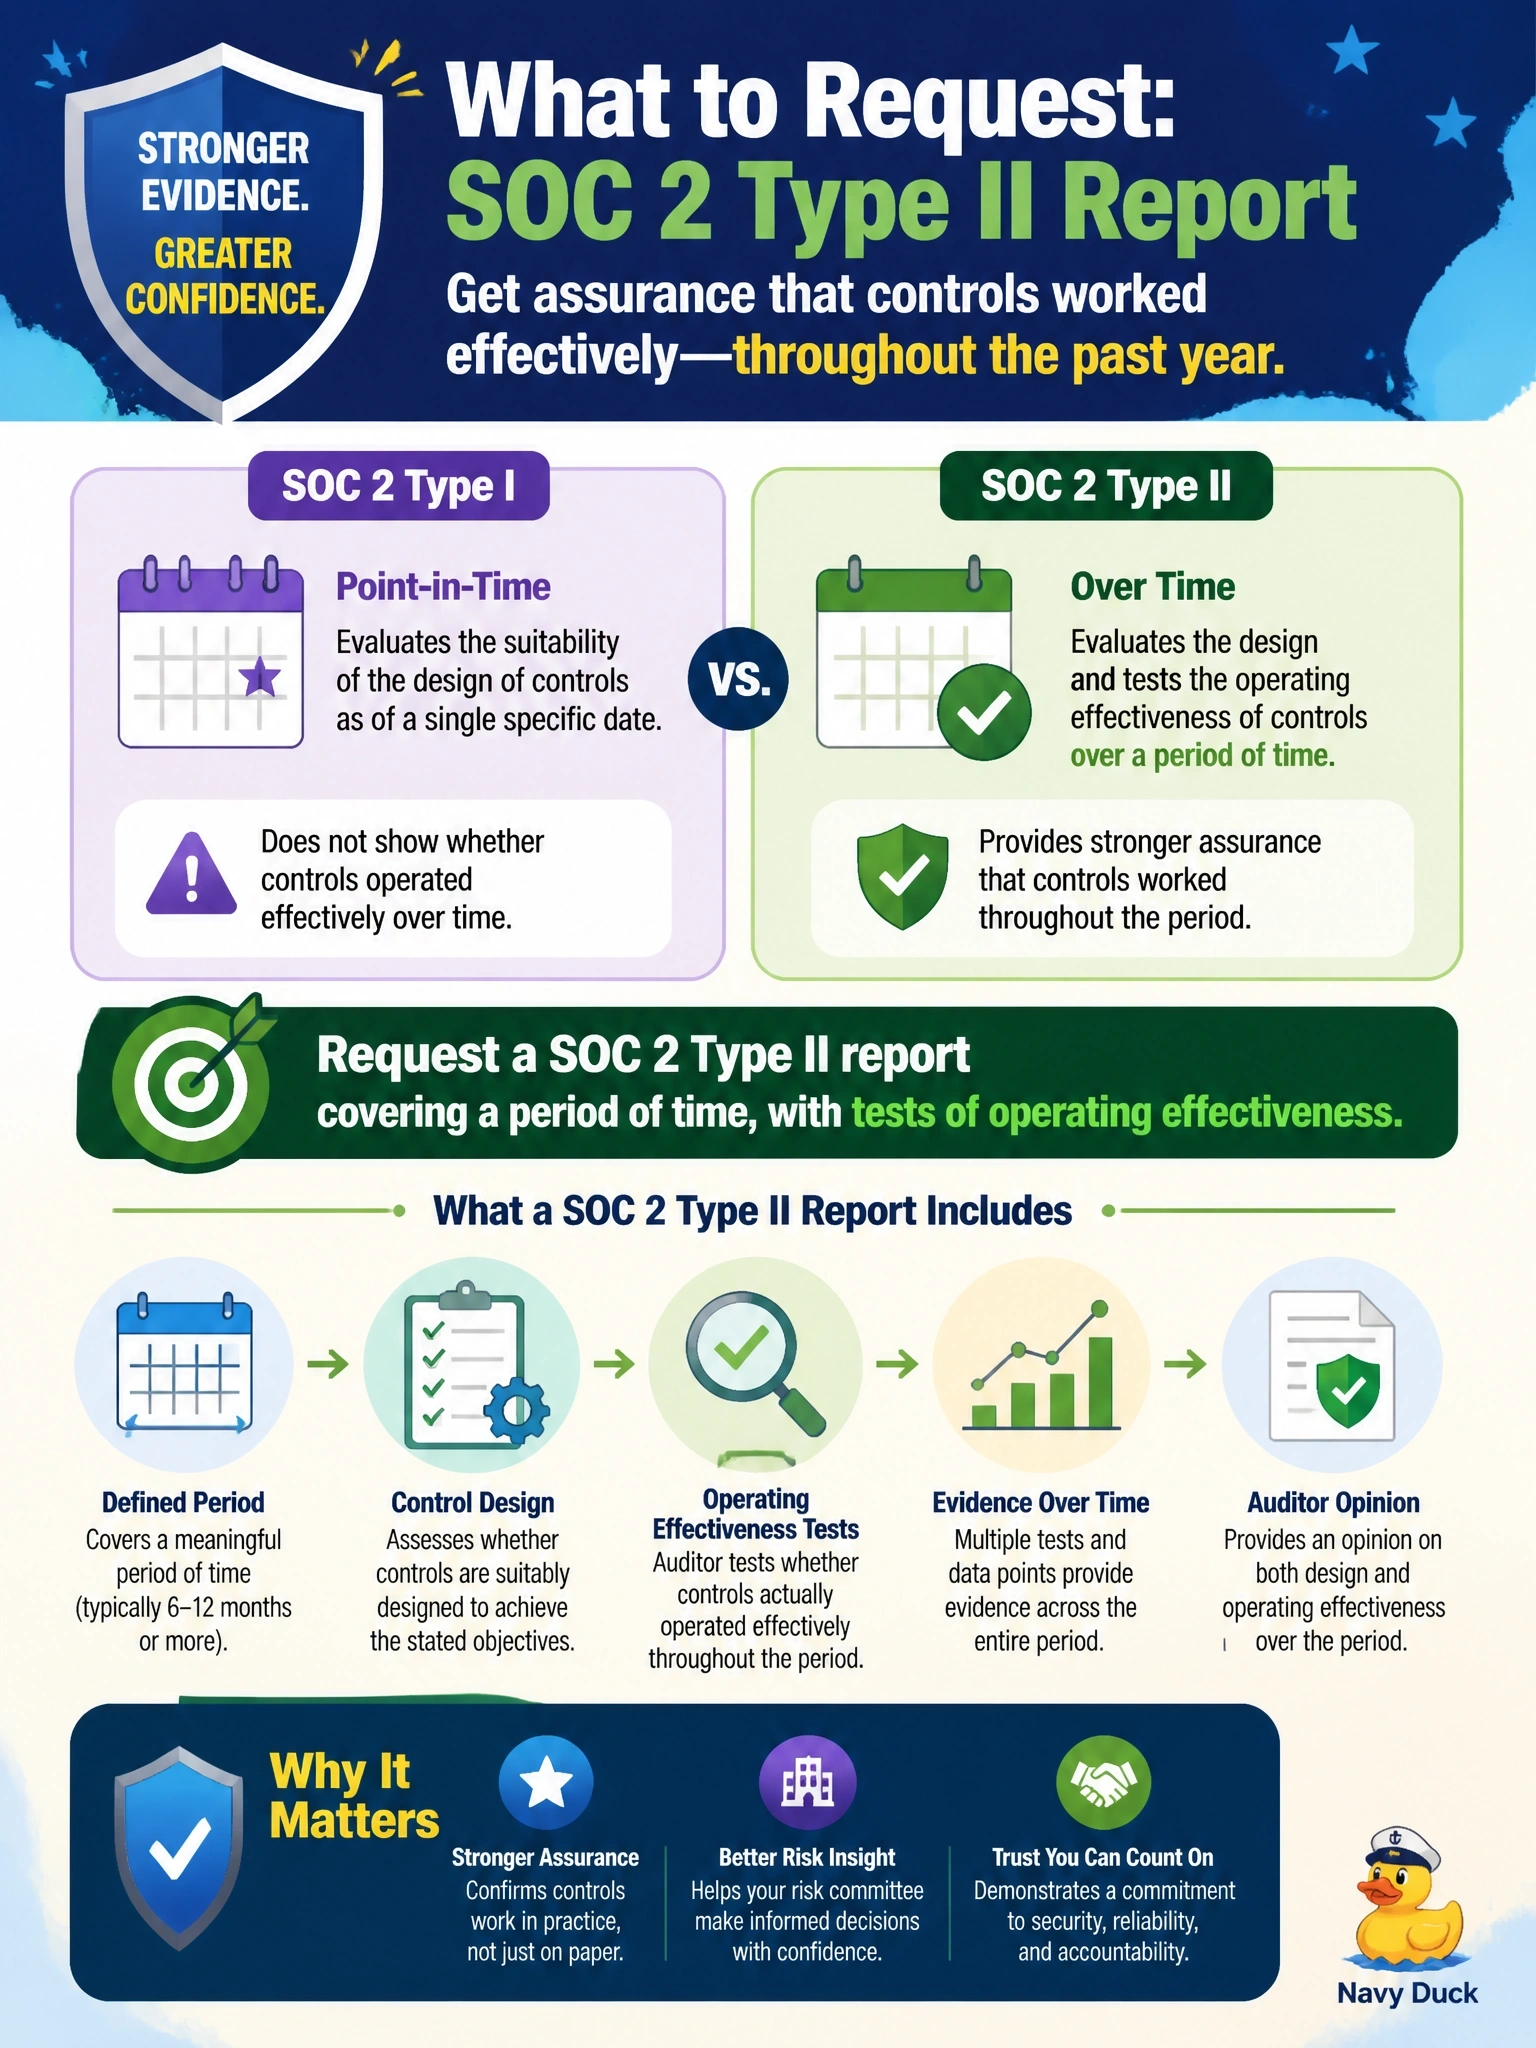
A design-only report is a snapshot: the controls looked well built on one day. A Type II report is the video, showing the controls working over months. If you need proof they operated all year, you want the video, not a newer snapshot.
Full Explanation
SOC reports come in two types. A Type I report addresses the fairness of management's system description and the suitability of the design of controls as of a specific date, without testing whether they worked over time. A Type II report covers a period, commonly six to twelve months, and adds the auditor's tests of operating effectiveness and the results, including any exceptions. Because the risk committee needs evidence of operation throughout the year, a Type II report is the appropriate request. A newer Type I report still evaluates design at a point in time, so moving the date forward does not provide evidence of operation over the period. A SOC 3 report is a general-use summary of a trust services examination; it does not add testing to a Type I report and omits the detailed test descriptions customers rely on. A SOC 1 report addresses controls relevant to financial reporting, and a Type I report of any kind is point-in-time, so it fails on both scope and period. Exam caveat: review exceptions noted in a Type II report and the bridge or gap period between the report end date and today. Operational check: confirm the report period, the testing results for each relevant control and whether a bridge letter covers the time since the period ended.