
In a private cloud, hypervisor management interfaces sit on the same layer 2 broadcast domain as tenant virtual machines, so tenant workloads can reach management services directly. Which network control best addresses this?
Select an answer to reveal the explanation.
Short Explanation
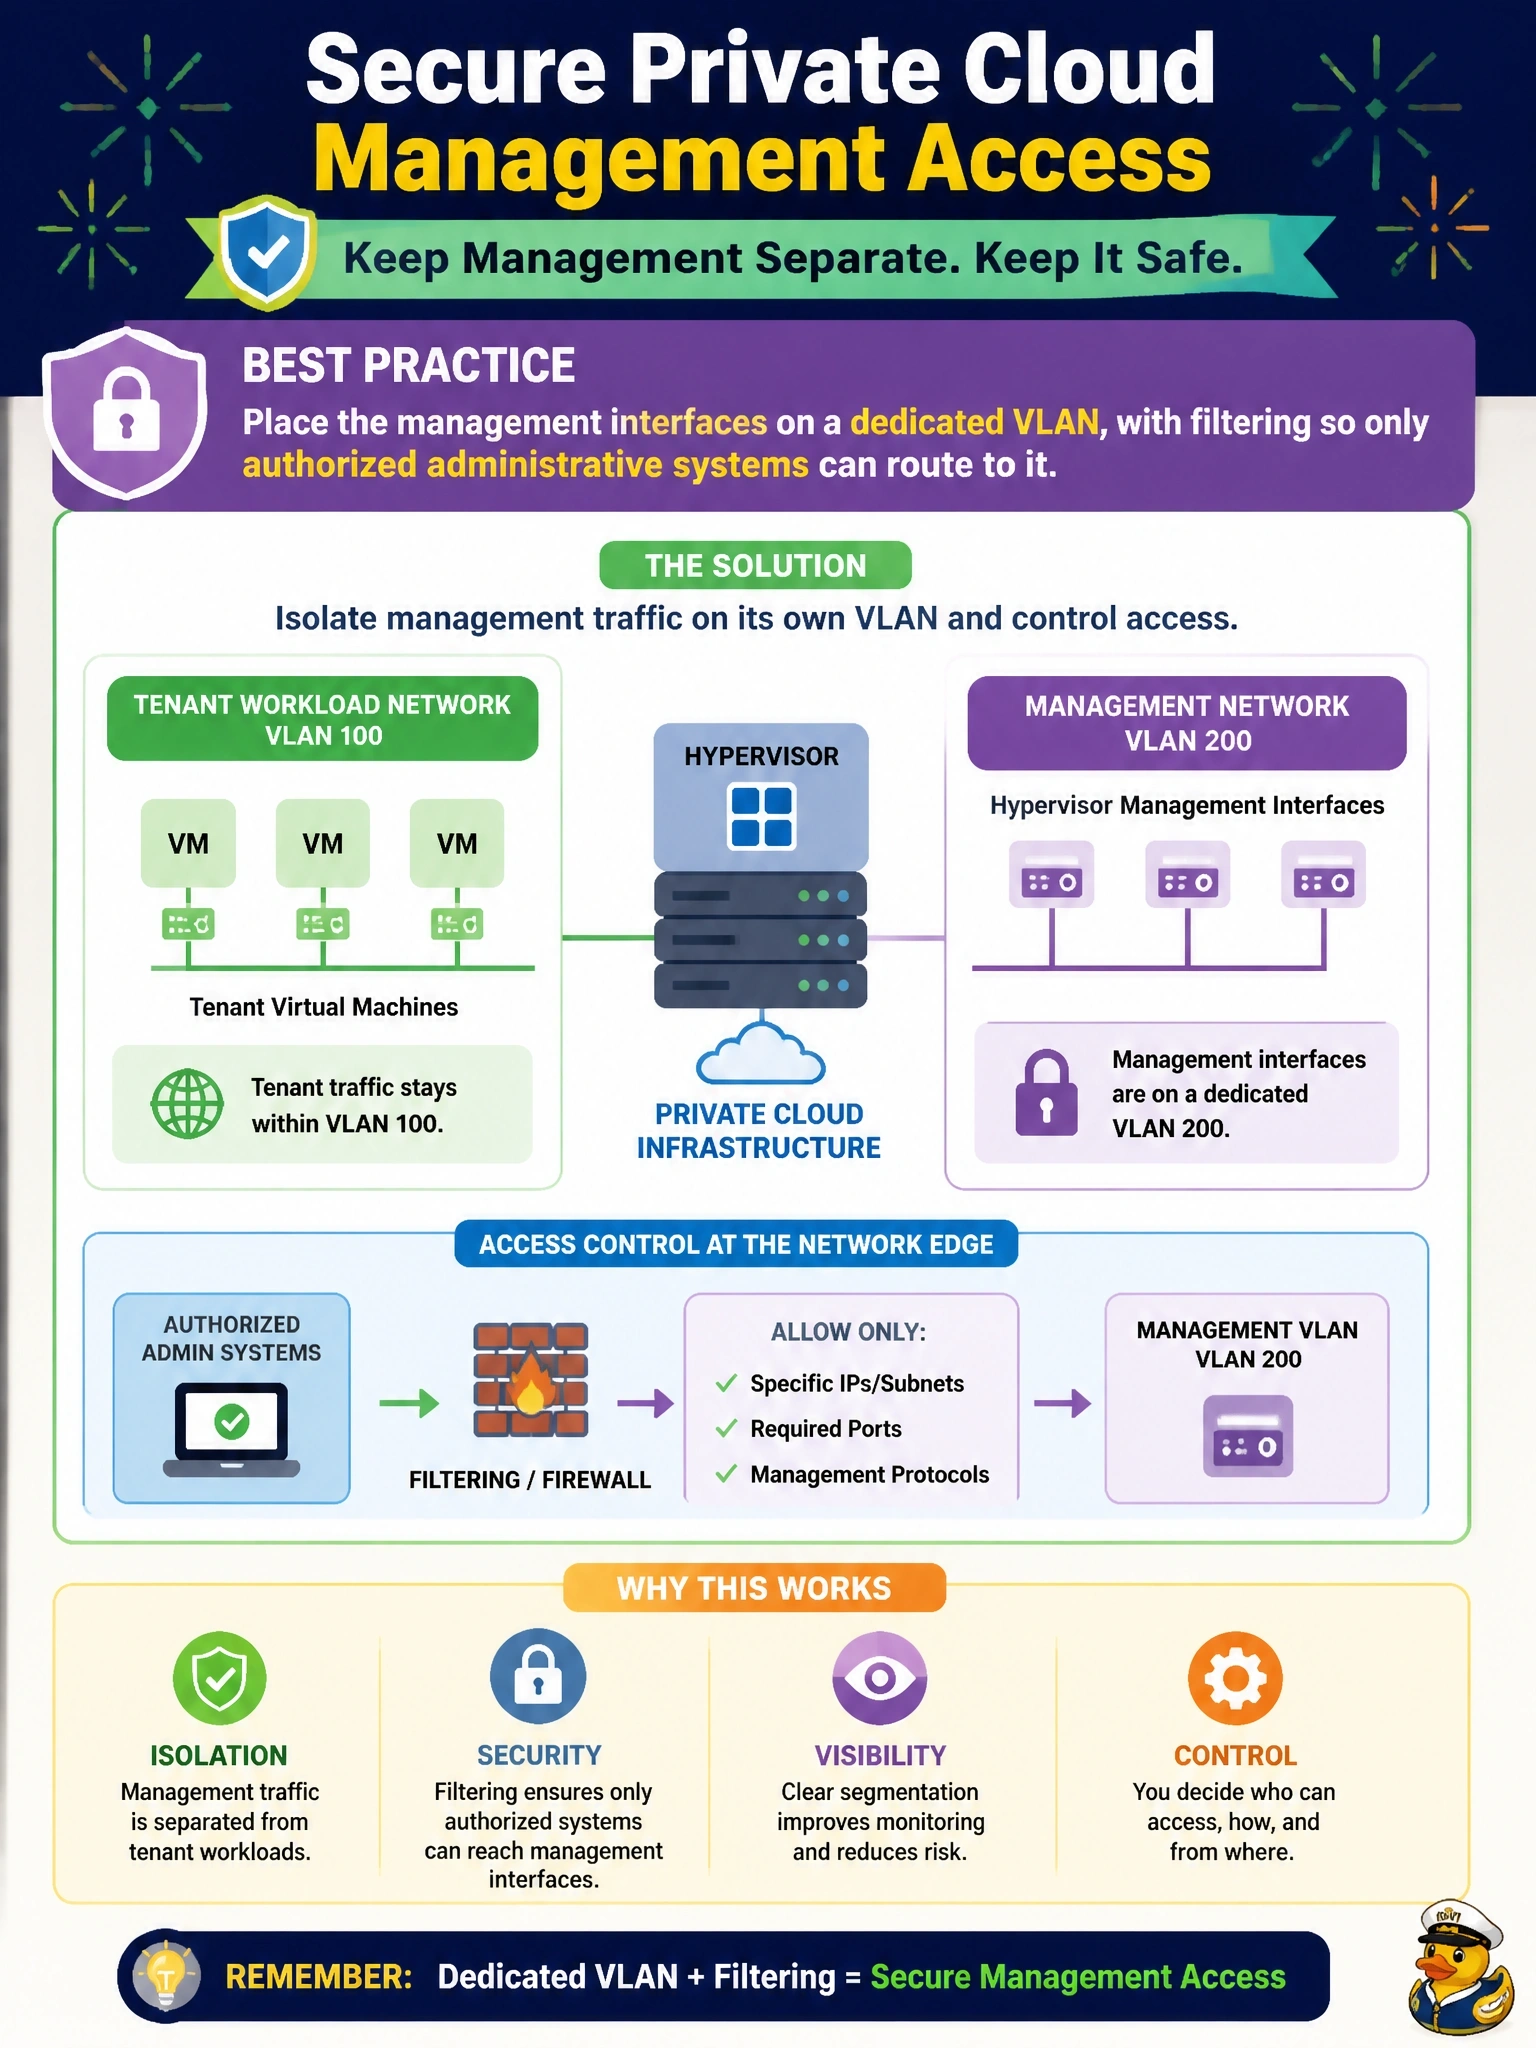
Management and tenants on one broadcast domain is like letting hotel guests wander the staff-only corridor. A dedicated VLAN puts a locked door between them, and filtering decides who gets a key. Encrypting or renumbering won't stop guests from knocking on the staff doors, so you need the wall.
Full Explanation
Virtual LANs divide a physical or virtual switching fabric into separate layer 2 broadcast domains. Placing hypervisor management interfaces on their own VLAN means tenant VMs no longer share a segment with them; traffic between the two must cross a layer 3 boundary where firewall rules or access control lists can restrict management access to administrative workstations or bastion hosts. This is network segmentation applied to the management plane. DHCP snooping prevents rogue DHCP servers and helps bind addresses to ports, but tenants on the same broadcast domain can still reach management services at their existing addresses and can attempt layer 2 attacks. Enabling TLS protects management sessions from eavesdropping, yet the services remain directly reachable, so tenants can still probe them, attempt authentication and exploit vulnerabilities. Enlarging the subnet or choosing distinguishable address ranges is an administrative convenience; without a boundary that enforces policy, addresses alone do not prevent communication. Exam caveat: VLANs provide logical separation, and the exam may note that VLAN isolation alone depends on correct switch configuration; filtering at the routed boundary is what enforces who may cross. Operational check: from a tenant VM, attempt to reach a hypervisor management address and confirm the connection fails, and review the inter-VLAN rules to confirm that only named administrative sources can reach the management VLAN.