
The CISO suspects that departments are using many cloud applications IT never approved, but there is no inventory of them. What is the best first step to identify which cloud services are actually in use across the organization?
Select an answer to reveal the explanation.
Short Explanation
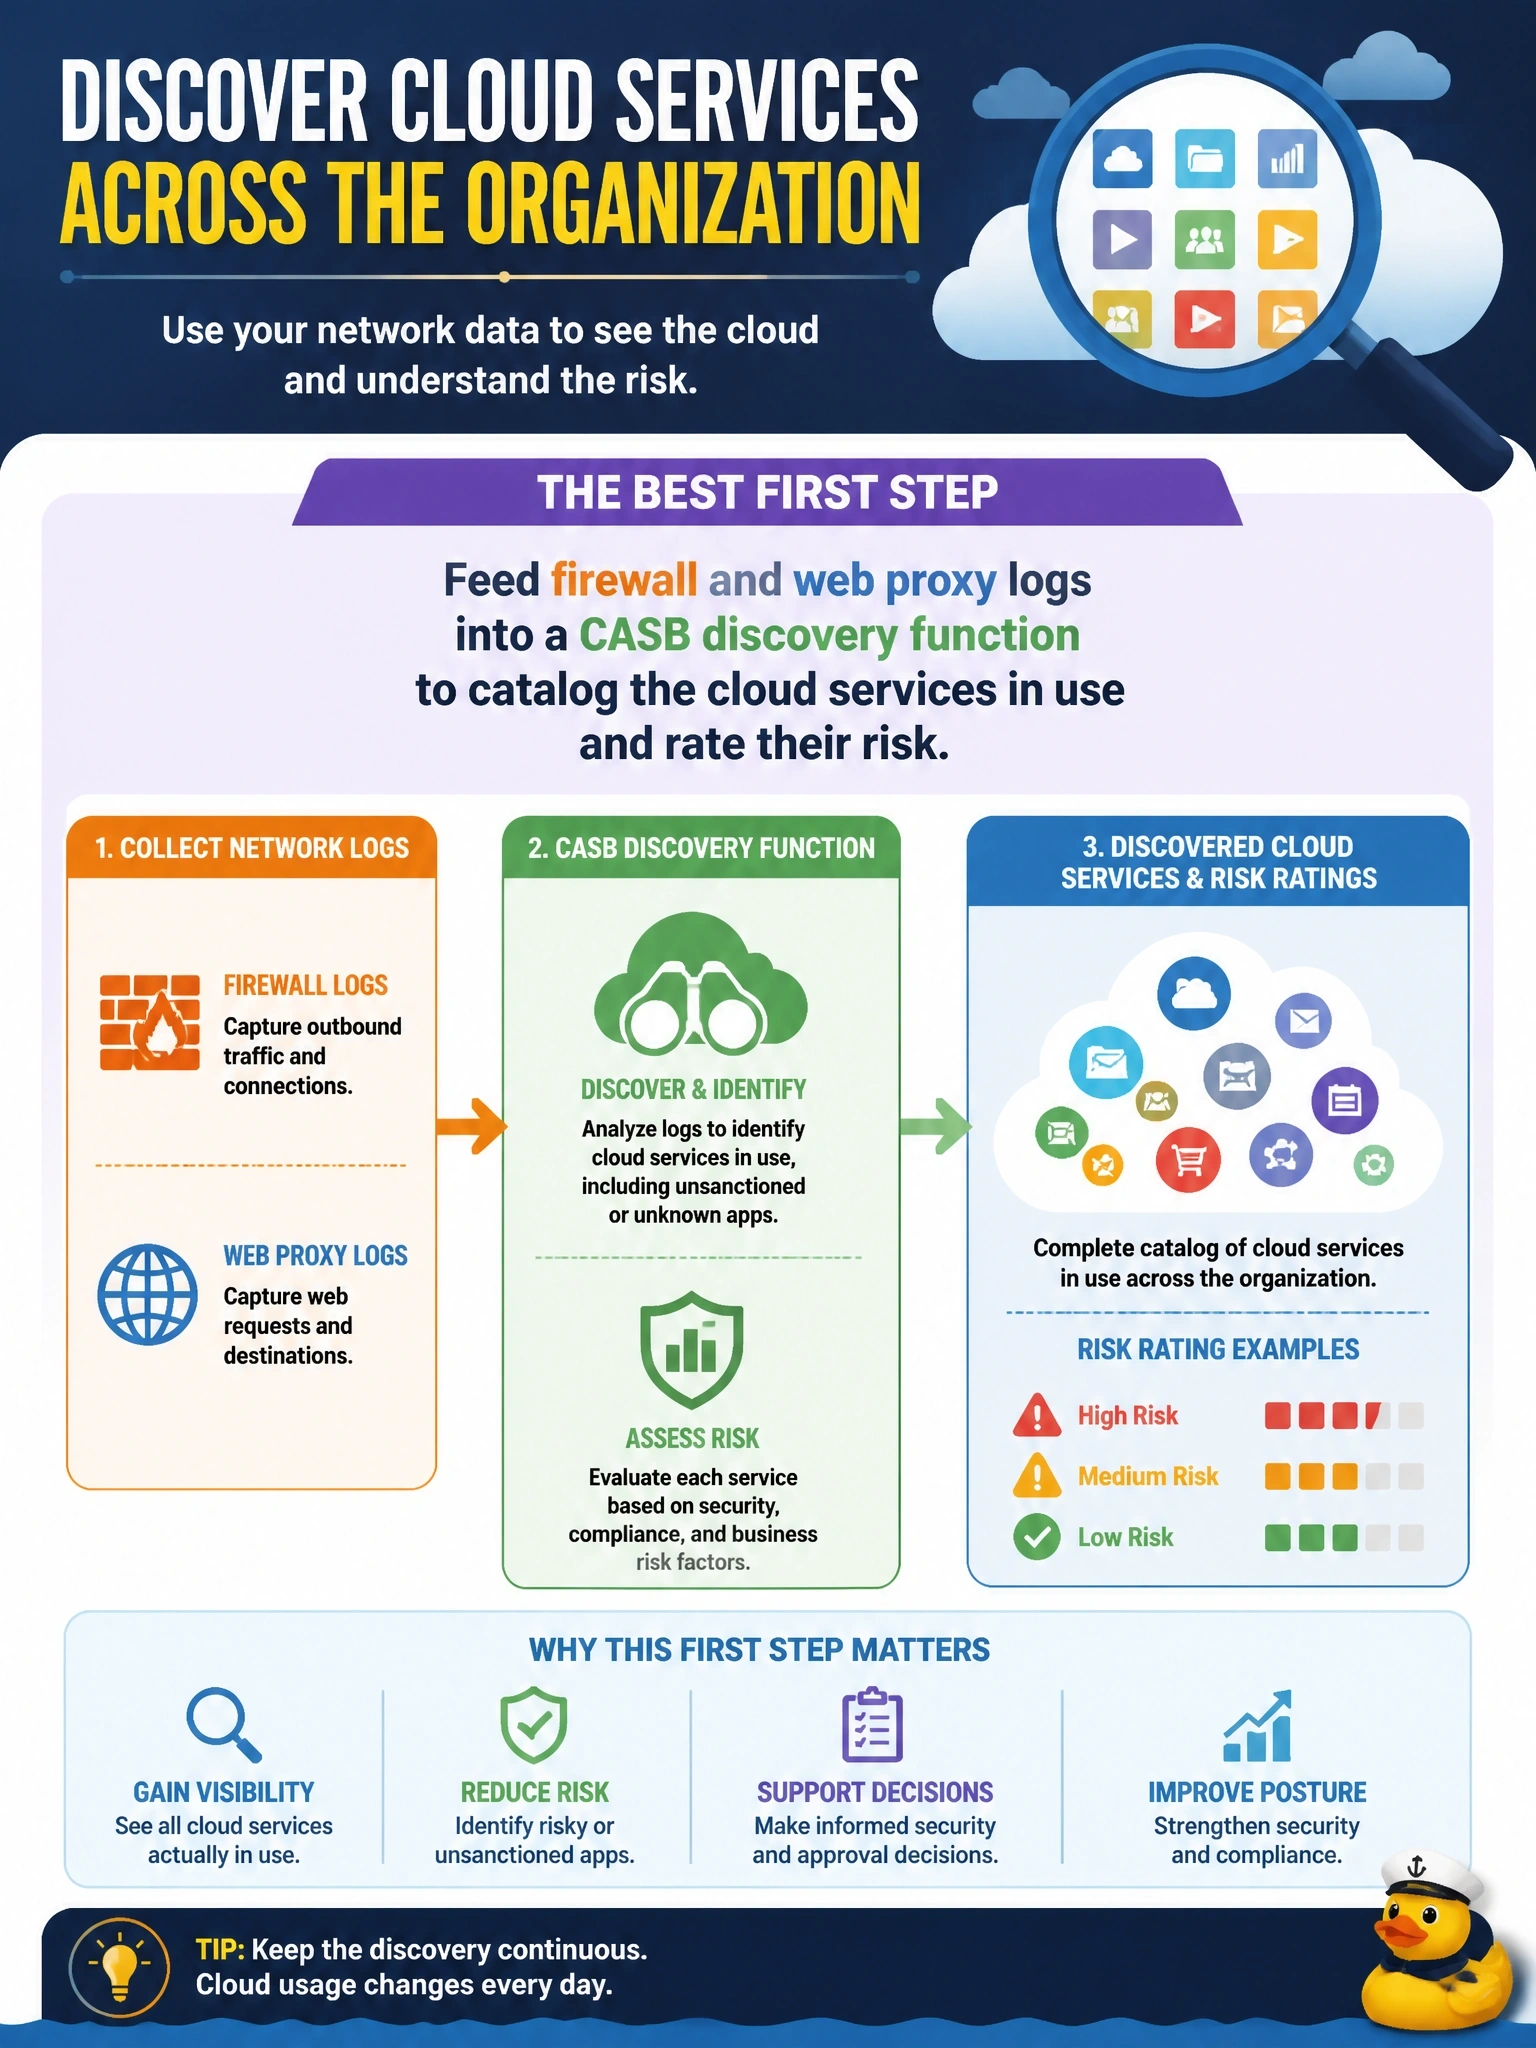
You can't manage what you can't see, and people don't always remember, or admit, what they've signed up for. Your network logs already know where everyone's going, so let a CASB turn them into a shadow IT inventory. The trap is asking people or blocking blindly before you've got any data.
Full Explanation
Shadow IT discovery starts from evidence of actual use. Firewall, secure web gateway and proxy logs record outbound connections from every managed network path; a CASB's discovery capability ingests those logs, maps destinations to a catalog of known cloud services, and scores each service against risk attributes such as data handling, certifications and terms of service. The result is an objective inventory with usage volumes and users, which then informs decisions to sanction, restrict or block. A survey relies on department heads knowing and disclosing every tool their staff use, and free or individually purchased services are routinely missed. Blocking everything except an allow-list before knowing what is in use disrupts legitimate business work, generates complaints rather than an inventory, and pushes users toward personal devices and networks that are even less visible. Card statements reveal only paid subscriptions billed to corporate cards; free tiers, personal payments and services paid through other channels never appear. Exam caveat: discovery reveals usage, not data content; follow-up controls such as API-mode scanning or inline policies are needed to protect data once services are known. Operational check: confirm that logs from every egress point, including remote-user traffic, feed the discovery tool, and review the resulting service list with business owners to classify each service as sanctioned, tolerated or prohibited.