
A team building a high-value cloud banking application needs a structured, testable set of security requirements, graded by the application's risk level, that testers can verify control by control. Which resource best fits this need?
Select an answer to reveal the explanation.
Short Explanation
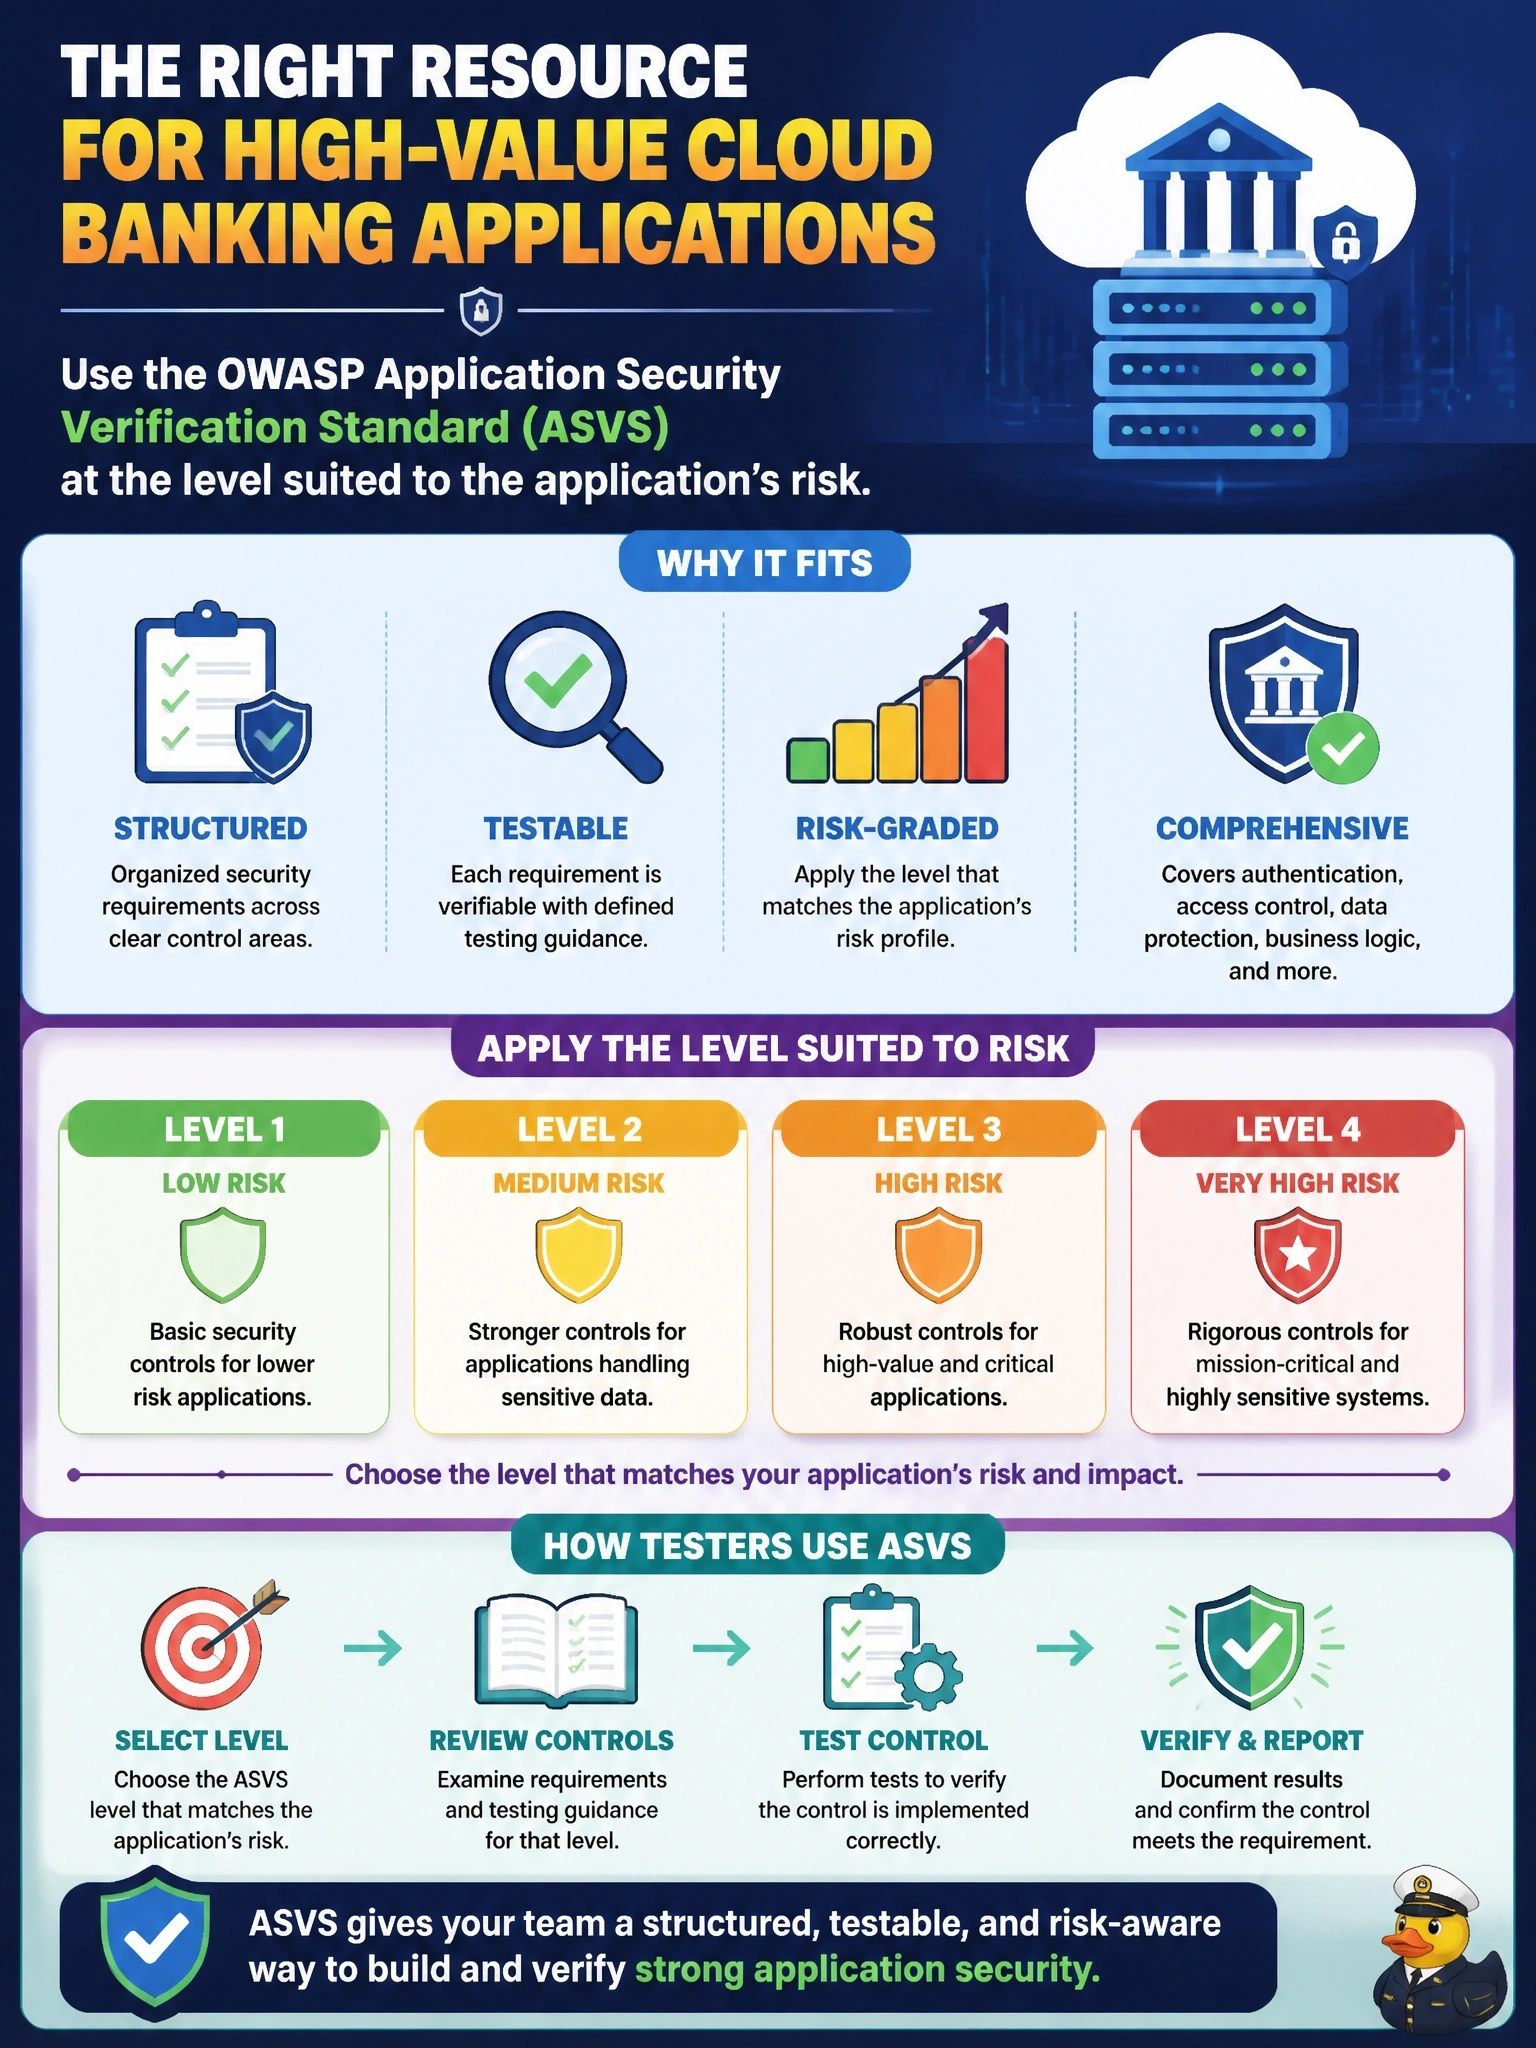
An awareness list tells you what usually goes wrong; a verification standard tells you exactly what to check, and how hard. ASVS gives you graded levels of testable requirements, so a high-value banking app picks the higher level and tests against it. The trap is using the Top 10 as if it were a full spec; it was never meant to be one.
Full Explanation
The OWASP Application Security Verification Standard is a catalog of security requirements written to be verified, organized by area such as authentication, session management, access control, validation and cryptography, and graded into levels so that applications handling more sensitive data or higher-value transactions apply more rigorous requirements. That makes it suitable both as a requirements baseline for developers and as a test plan for verifiers. The CWE Top 25 ranks the most common and impactful software weaknesses; it is excellent for awareness and for prioritizing training and tooling, but it lists weaknesses rather than graded, testable requirements, and it is not risk-tiered. The OWASP Top 10 is an awareness document describing the most critical web application risk categories; OWASP itself advises against using it as a complete standard, because coverage of ten categories leaves many requirements unaddressed. The Common Vulnerability Scoring System rates the severity of individual vulnerabilities after they are found; it does not define what an application must implement in the first place. Exam caveat: the 2026 outline names ASVS alongside the API and LLM Top 10 lists, and distinguishing a verification standard from an awareness list is the skill being tested. Operational check: record the chosen ASVS level in the security requirements and map each requirement to a test case in the pipeline.