
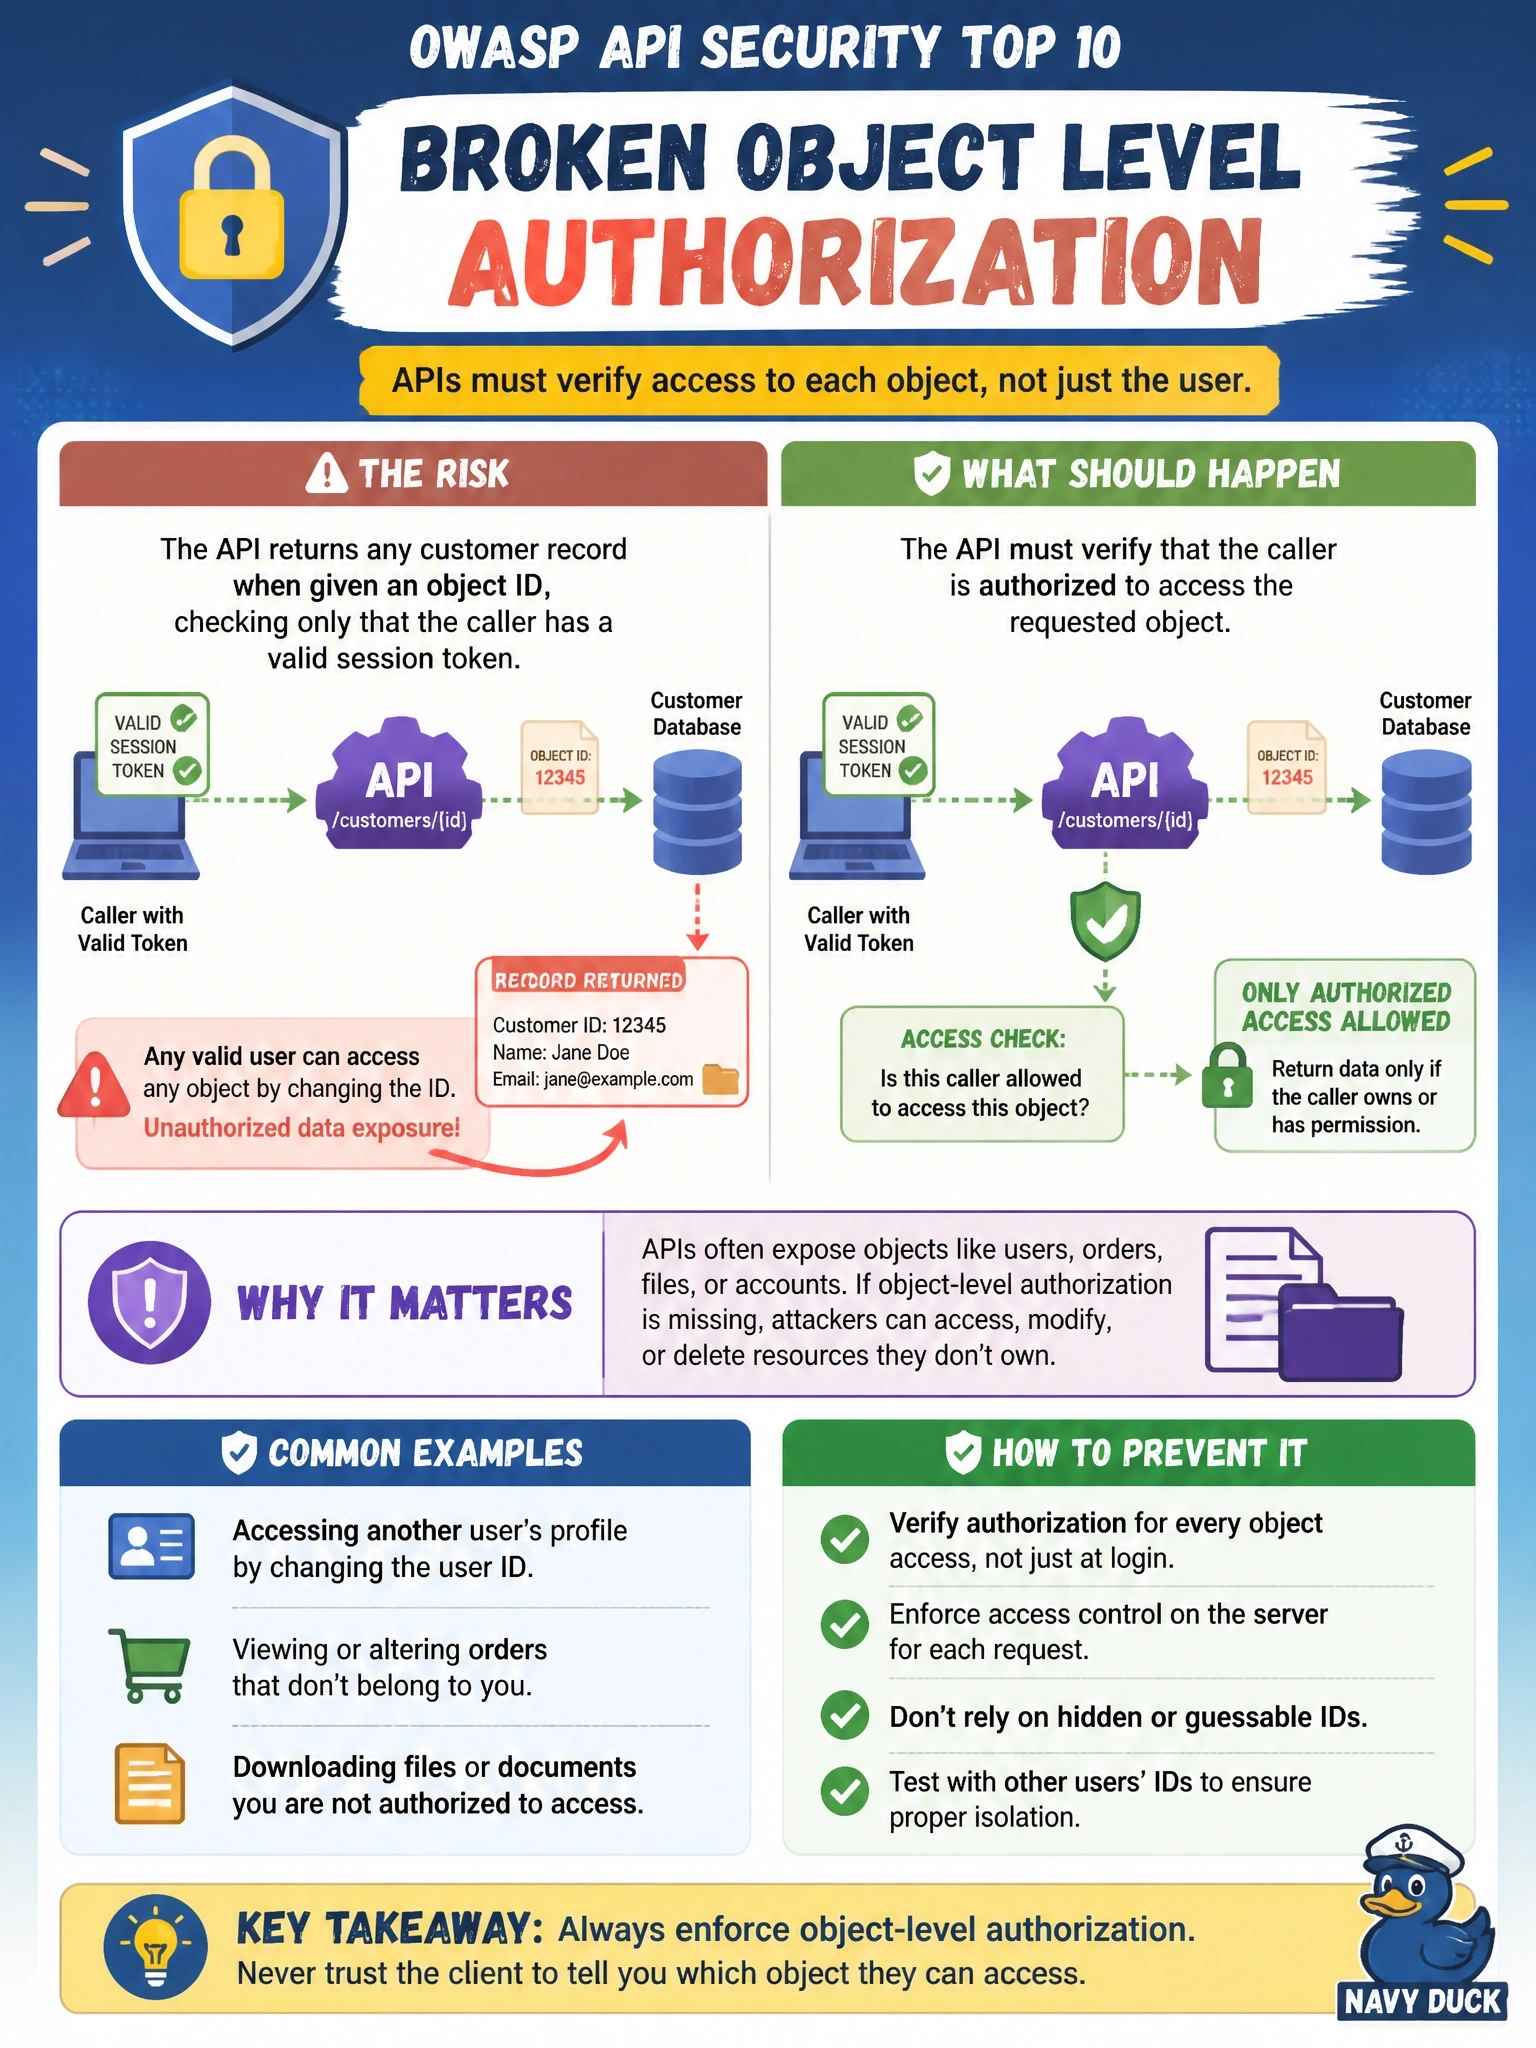
A mobile app's back-end REST API returns any customer record when the caller supplies its object identifier, checking only that the caller presents a valid session token. Which risk from the OWASP API Security Top 10 does this describe?
Select an answer to reveal the explanation.
Short Explanation
The API checks your ticket at the door and then lets you into any room you can name. Valid token, wrong object, no check: that's Broken Object Level Authorization. Don't confuse it with the function-level flavor, which is about reaching admin-only operations, not someone else's record.
Full Explanation
Broken Object Level Authorization, ranked first in the OWASP API Security Top 10, occurs when an API exposes endpoints that take an object identifier and fails to verify that the caller is permitted to access that particular object. Here authentication works, because the session token is valid, but authorization is only checked at the level of being logged in, so any record can be retrieved by enumerating or guessing identifiers. The mitigation is an authorization check in every function that accesses a data source using client-supplied identifiers, preferably with unpredictable identifiers as defense in depth. Broken Authentication concerns weaknesses in verifying identity, such as credential stuffing, weak tokens or missing validation of tokens; the scenario states that tokens are validated. Broken Function Level Authorization is about callers reaching operations they should not, such as a regular user invoking administrative endpoints; the operation here is a legitimate read, and the failure is which object it returns. Unrestricted Resource Consumption covers missing limits on request rates, payload sizes or costly operations, which affects availability and cost rather than confidentiality of specific records. Exam caveat: the OWASP API list is separate from the web application Top 10 and is named in the 2026 outline. Operational check: test each object endpoint with a valid token for a different user and confirm the API returns a denial.