
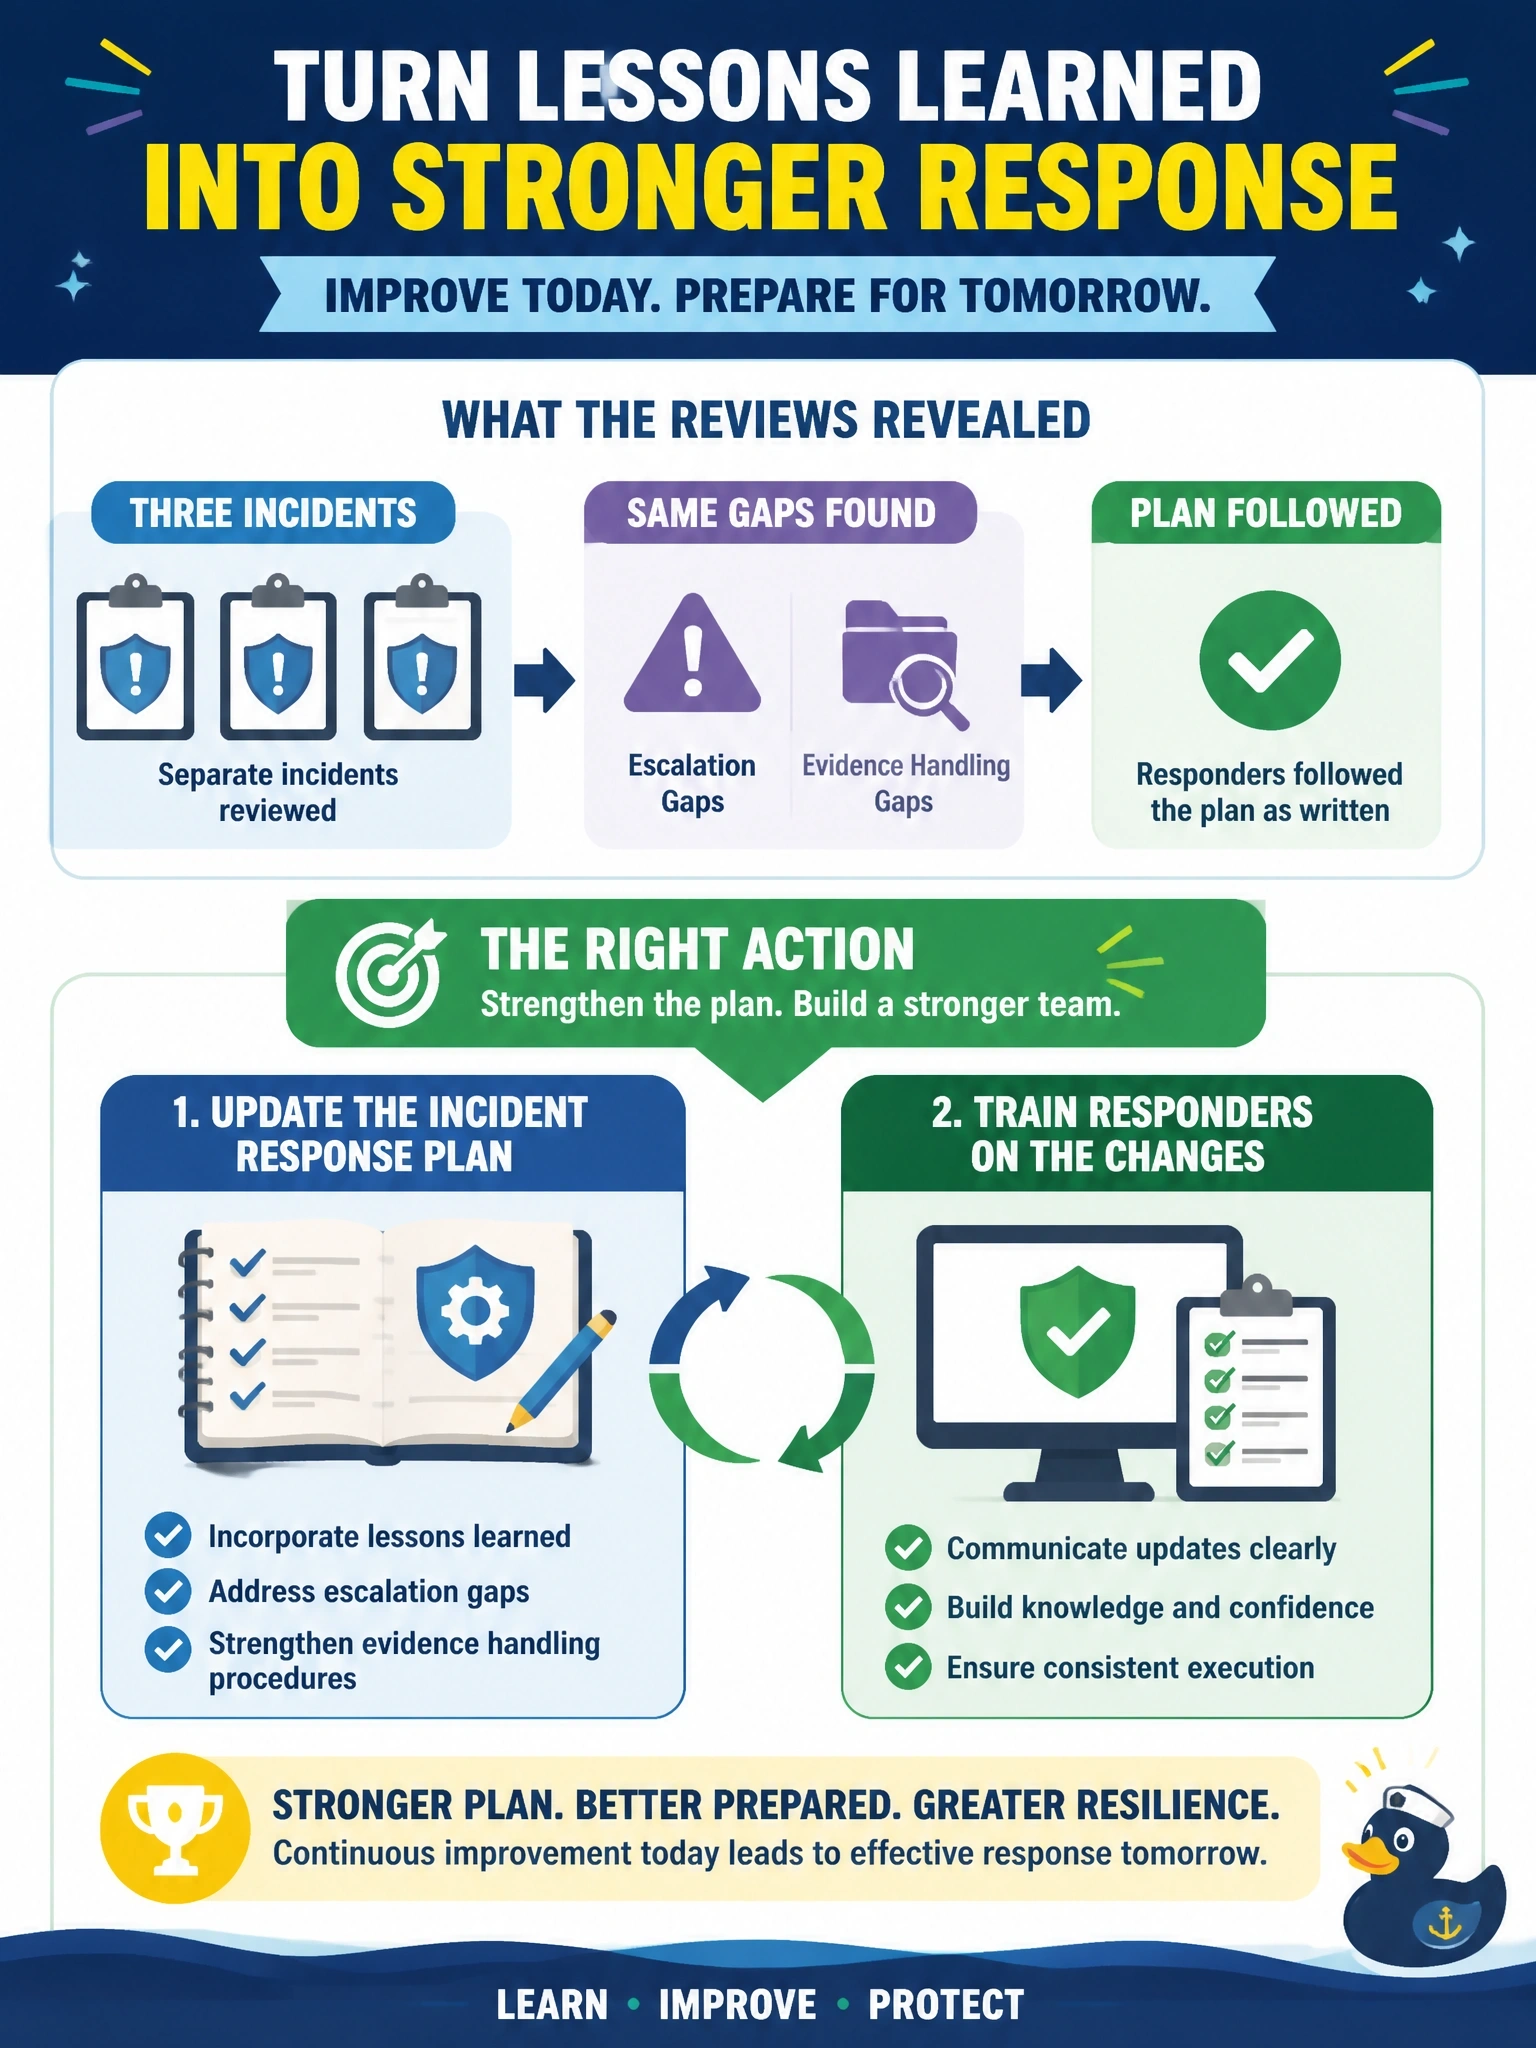
Post-incident reviews for three separate incidents identified the same gaps in escalation and evidence handling, and each time responders followed the incident response plan as written. What should the security manager do?
Select an answer to reveal the explanation.
Short Explanation
If people follow the recipe exactly and the cake keeps flopping, it's the recipe that needs fixing. Responders did what the plan said, so you change the plan and train on the new version. Retraining on the old recipe is the trap.
Full Explanation
Lessons learned are only valuable when they lead to change. When responders follow the incident response plan as written and the same gaps appear across multiple incidents, the evidence points to a weakness in the plan itself, such as unclear escalation criteria or missing evidence-handling procedures. Updating the plan to address those gaps, communicating the changes and training responders on them, then validating the changes in an exercise, closes the improvement loop. Retraining responders on the existing plan reinforces the procedures that are producing the gaps, because the responders were already following them correctly. Replacing the team with an external provider treats a plan defect as a people problem and does not transfer accountability; an external team following the same plan would encounter the same gaps. Reporting the recurring gaps to the board without changing the plan provides visibility but leaves the weakness in place and implies that oversight substitutes for management action. Exam caveat: plan updates should go through the organization's document governance, with approval by the appropriate authority and version control. Operational check: confirm the plan revision references the lessons-learned findings, the approval date and the training completion records for responders.