
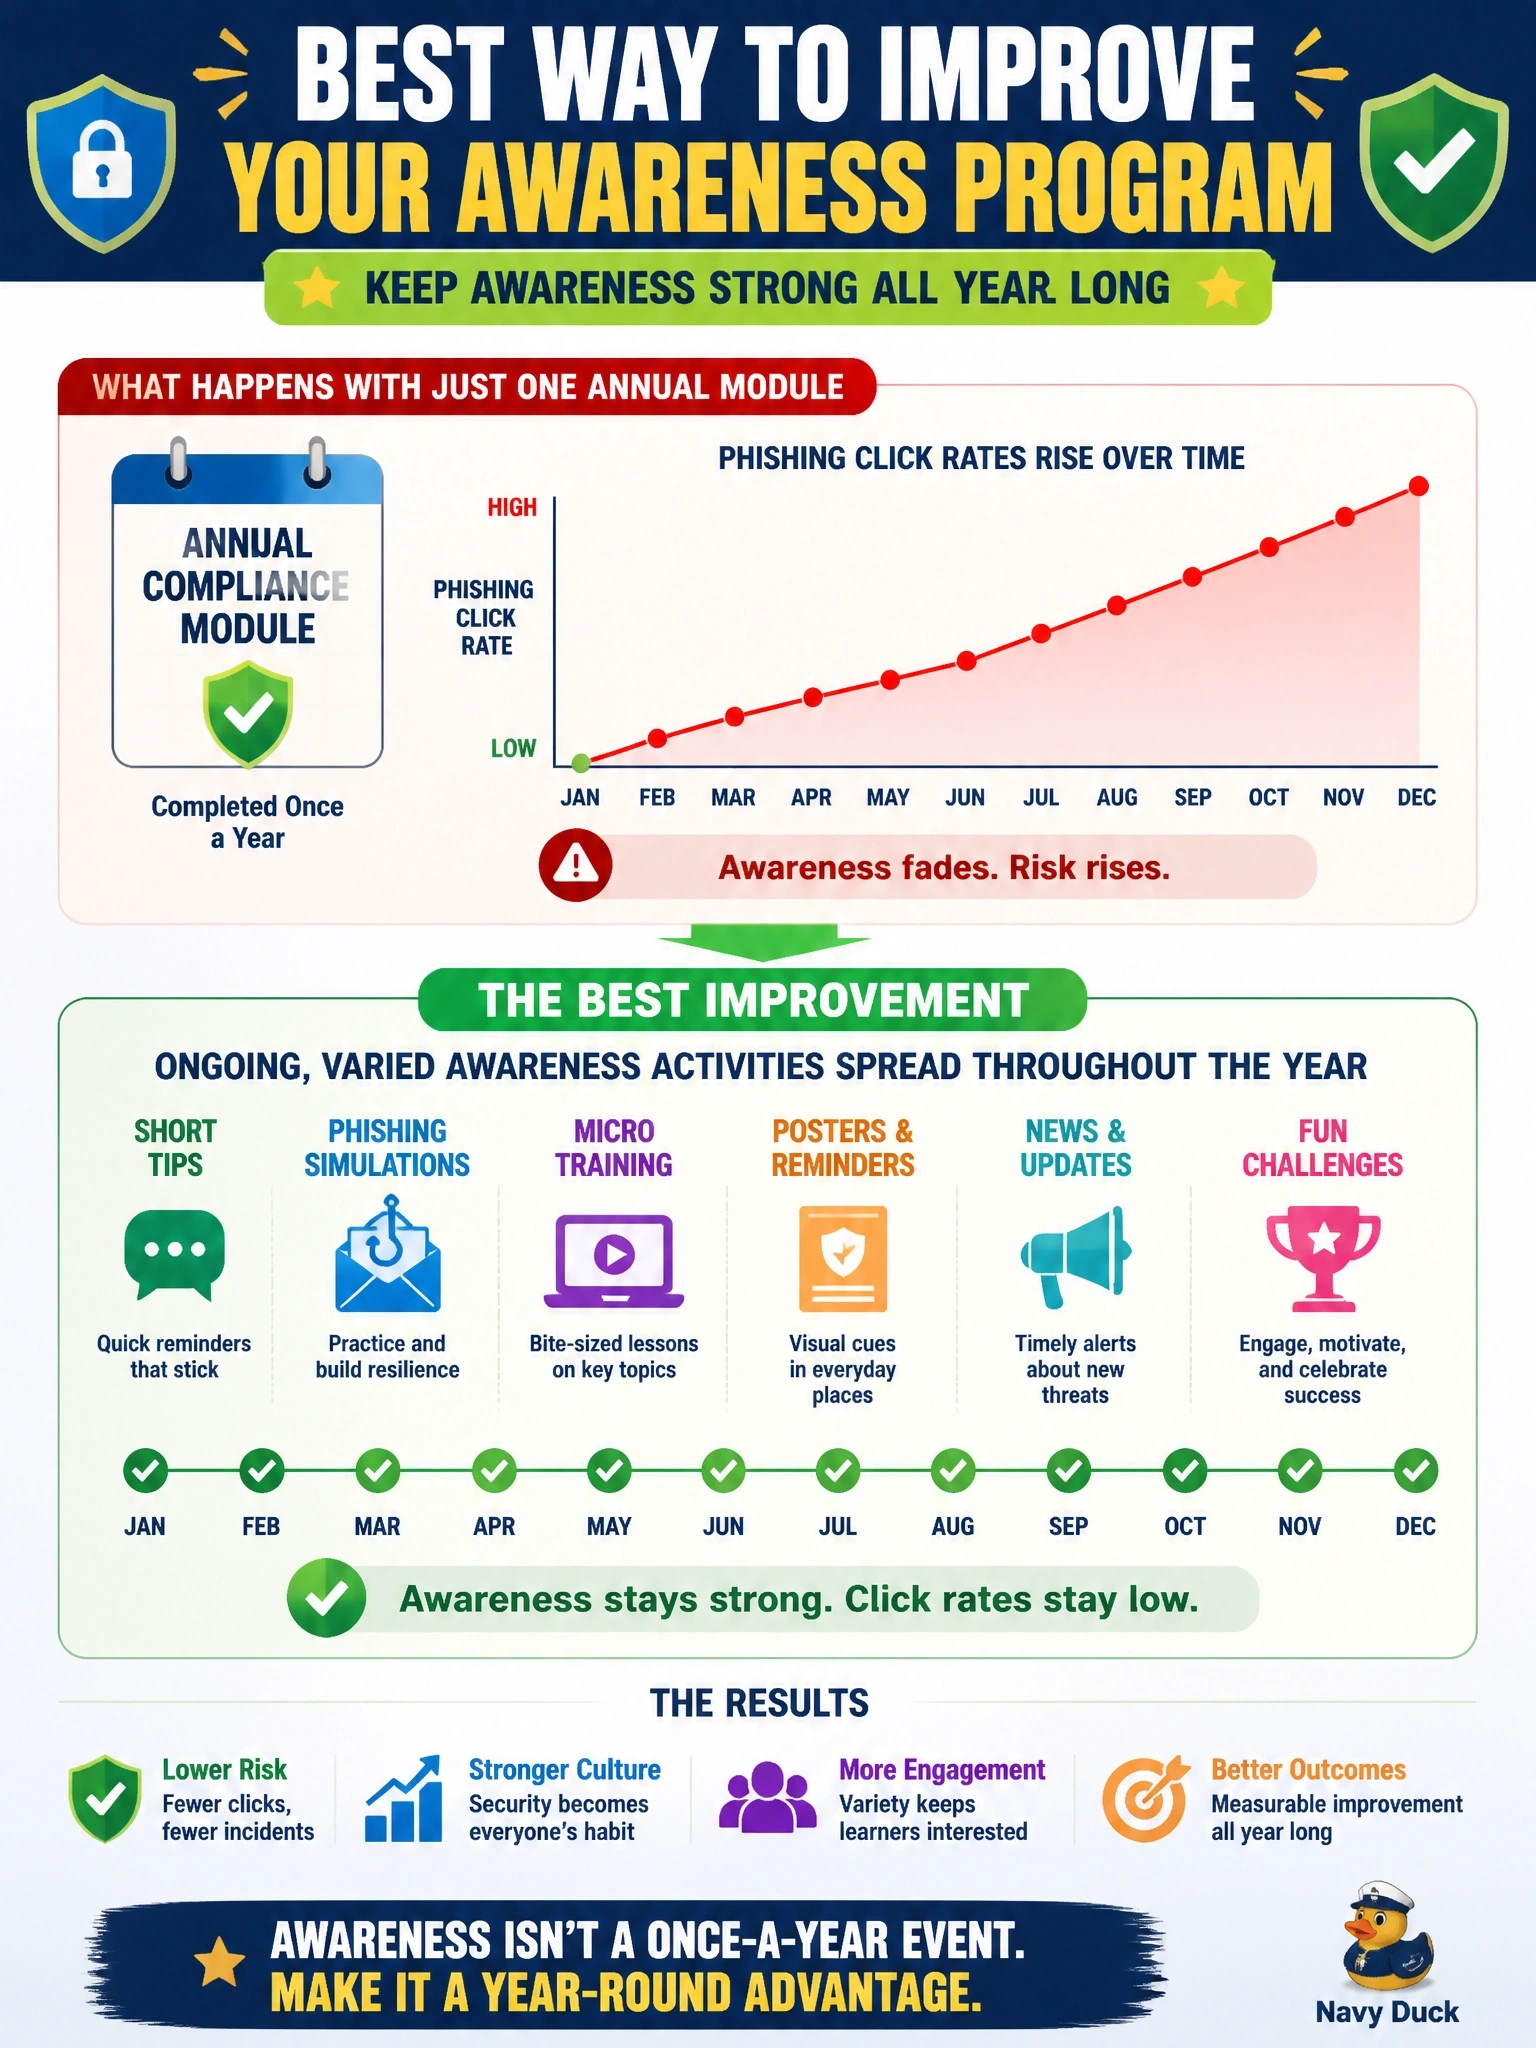
The security awareness program consists of a single annual compliance module, and phishing click rates rise steadily in the months after it is completed. What would BEST improve the program?
Select an answer to reveal the explanation.
Short Explanation
Going to the gym once a year won't keep you fit, no matter how long the session is. Awareness fades unless you keep topping it up. The trap is making the once-a-year event bigger instead of making the message come back regularly.
Full Explanation
The rising click rate in the months after the annual module shows that awareness decays over time when it is reinforced only once a year. A program of ongoing, varied activities, such as short micro-learning modules, simulations, timely alerts about current scams, newsletters and team briefings, keeps security in mind throughout the year and reaches people through different formats that suit different learners. Behavior is sustained by repetition and relevance rather than a single event. Making the annual module longer and more detailed concentrates even more content into one sitting, which increases fatigue and still leaves eleven months without reinforcement. Moving the module to a different point in the year changes when the decline begins but not the decline itself. A stricter pass mark on the quiz may raise immediate knowledge scores, but knowledge measured on the day of training is not what is fading; it is applied behavior over time. Exam caveat: annual training may still be required for compliance and acknowledgement purposes, so ongoing activities typically supplement rather than replace it. Operational check: introduce regular activities on a published calendar, measure click and report rates monthly, and confirm the post-training decline flattens compared with the previous year's pattern.