
After an audit finding, logging was enabled on all servers, but no one reviews the logs or acts on what they contain. What is the information security manager's MOST important concern?
Select an answer to reveal the explanation.
Short Explanation
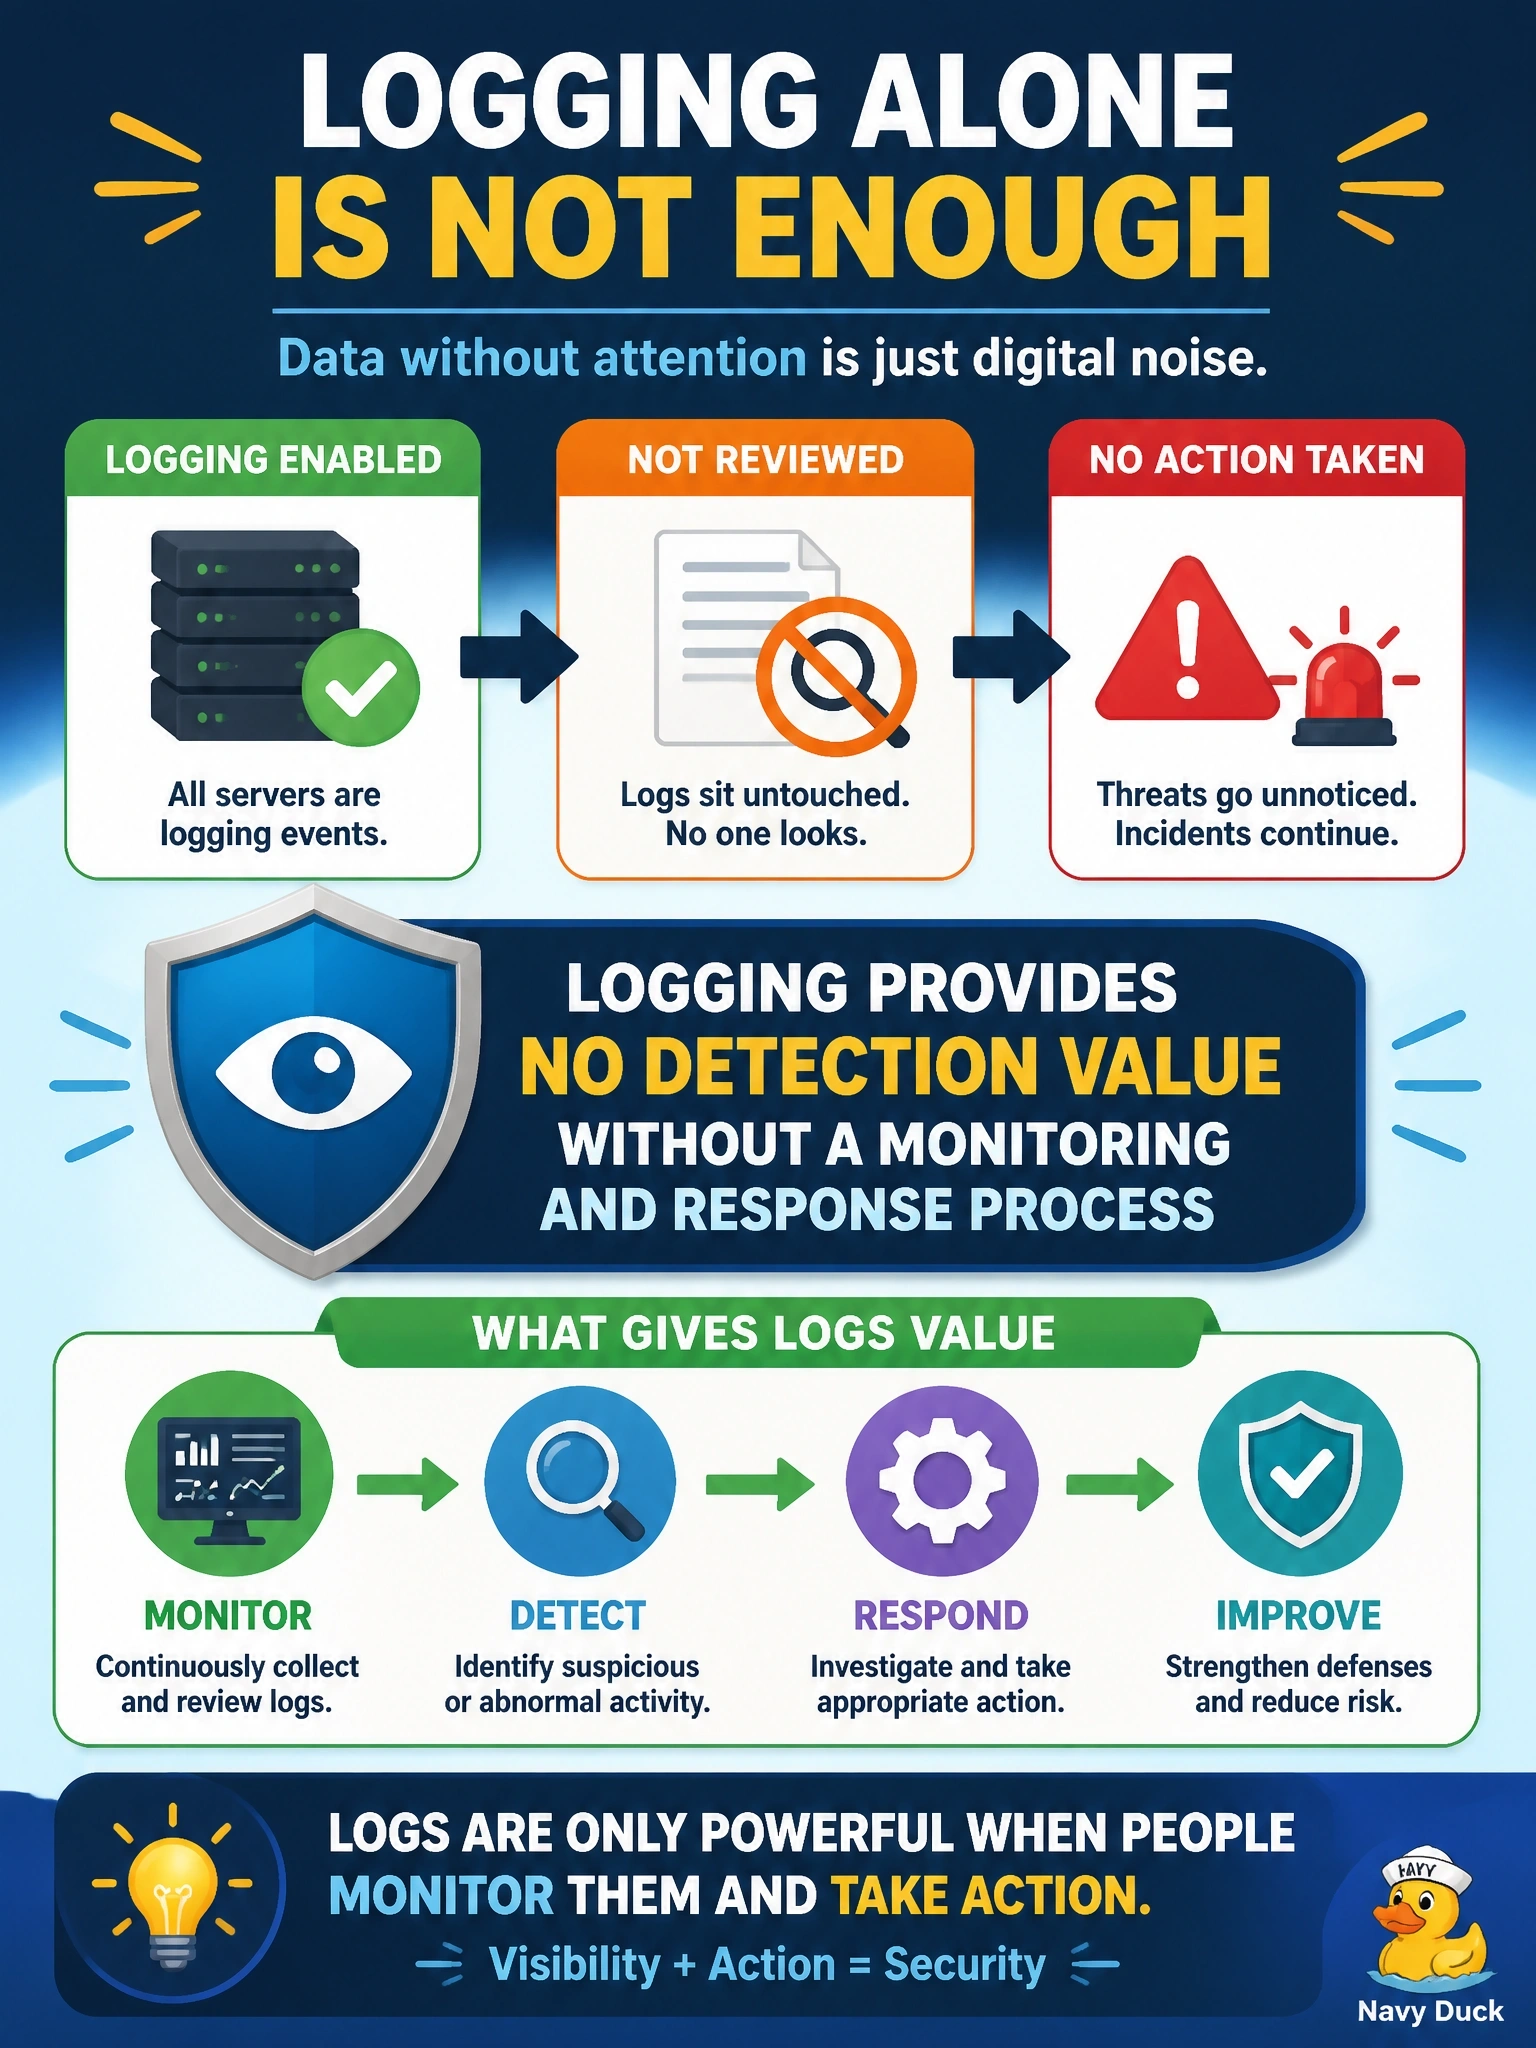
A security camera nobody watches is just a very expensive way to record a burglary. Logs only help you if someone looks at them and acts. The trap is focusing on storage or performance when the real problem is that the control isn't doing its job at all.
Full Explanation
A log is raw material for detection, not detection itself. For logging to function as a control, it must feed a monitoring process that defines which events matter, generates alerts, assigns responsibility for review and links to incident response so that suspicious activity results in action. Without that integration, attacks recorded in the logs go unnoticed, and the organization gains little beyond after-the-fact forensic data. Storage consumption is a real operational cost that retention policies manage, but it is minor compared with a control that provides no protection. Performance overhead from logging is generally manageable through configuration and is a tuning issue rather than the most important concern. The audit finding being reopened over format focuses on compliance appearance; the underlying problem is that the control does not achieve its objective, which an audit would also eventually identify. Exam caveat: CISM distinguishes implementing a control from integrating it into operations, and regards a control that is not monitored as ineffective regardless of how widely it is deployed. Operational check: confirm that defined use cases generate alerts from server logs, that each alert type has an owner and response procedure, and that metrics such as alerts reviewed and time to triage are reported to management.