
An organization claims that information security governance is integrated into its corporate governance. Which observation provides the BEST evidence that this is true?
Select an answer to reveal the explanation.
Short Explanation
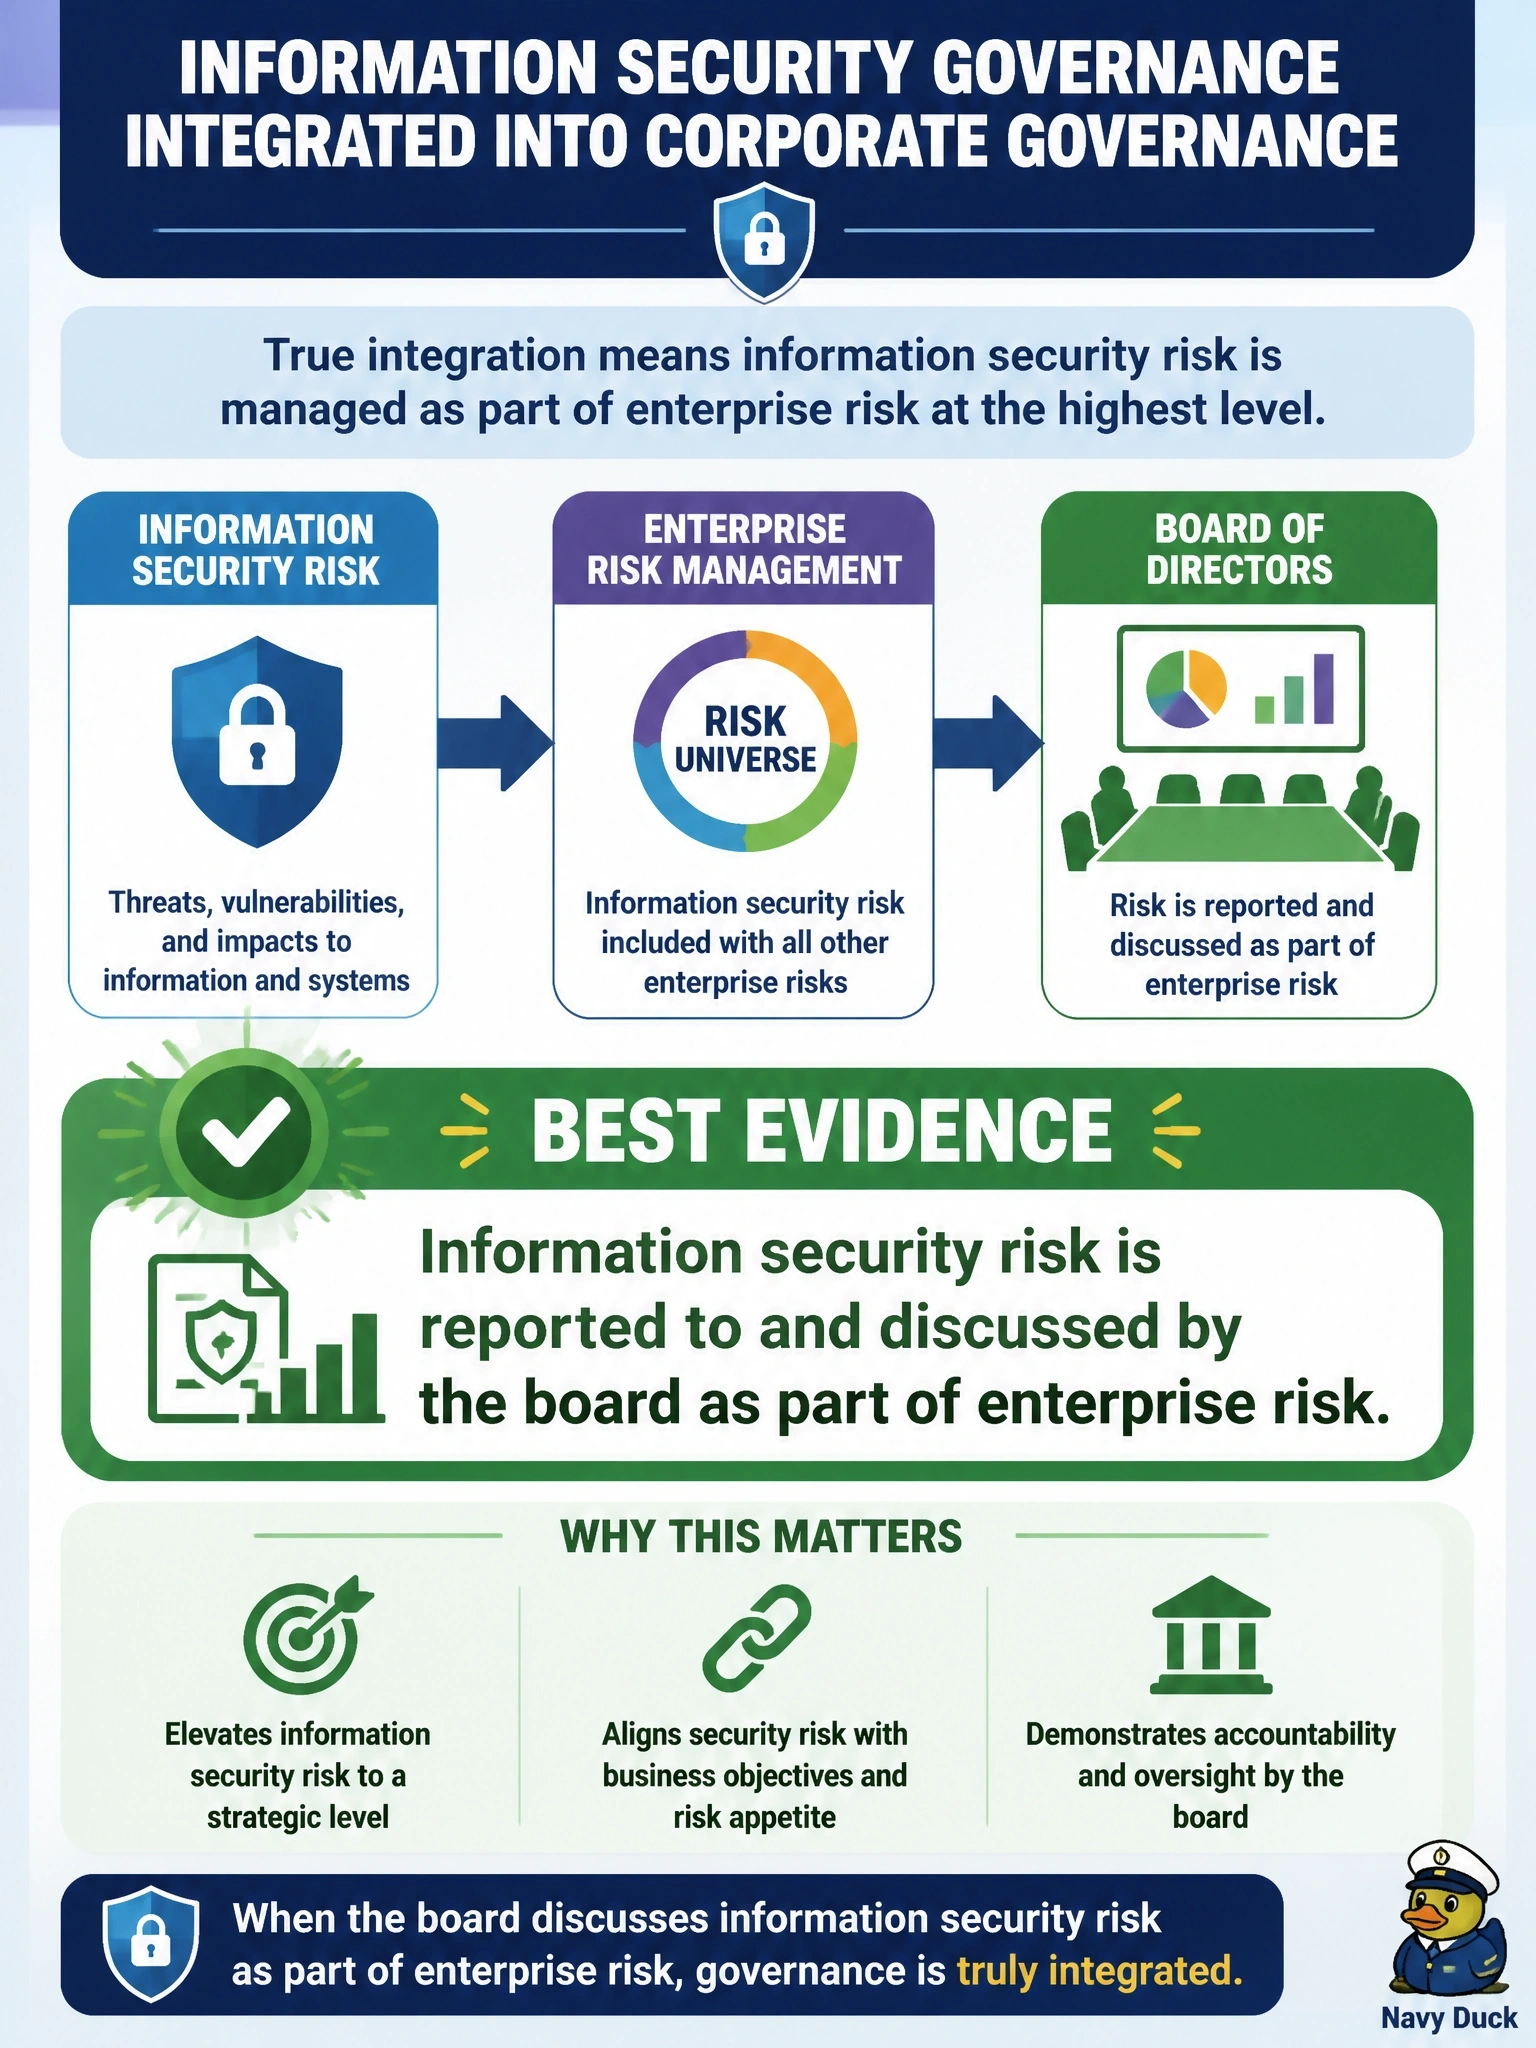
Integration means security shows up where the big decisions get made. If you see the board discussing security risk right alongside financial and operational risk, it's woven in; if it only lives in IT's reports, it's a side project. The trap is mistaking a good IT-level artifact for enterprise-level governance.
Full Explanation
Information security governance is integrated into corporate governance when security risk is treated as part of enterprise risk and is overseen through the same structures that govern the organization as a whole. The clearest evidence is that information security risk is reported to and actively discussed by the board, or its risk or audit committee, alongside other enterprise risks, with decisions recorded and management held to account. Monthly technical metrics for the IT director demonstrate operational management within IT, but they stay inside the technology function and do not show that the governing body directs or oversees security risk. Policies approved by the CIO and published internally show that a policy framework exists, yet approval at the CIO level rather than by executive management or the board suggests security is still treated as an IT matter. Certification of the data center demonstrates that a management system meets a standard for that scope, but it is limited in scope and does not show board-level oversight across the enterprise. Exam caveat: certification and good reporting are valuable, but the integration question is about who governs security risk. Operational check: review board and committee minutes for recurring information risk agenda items, decisions and follow-up actions.