
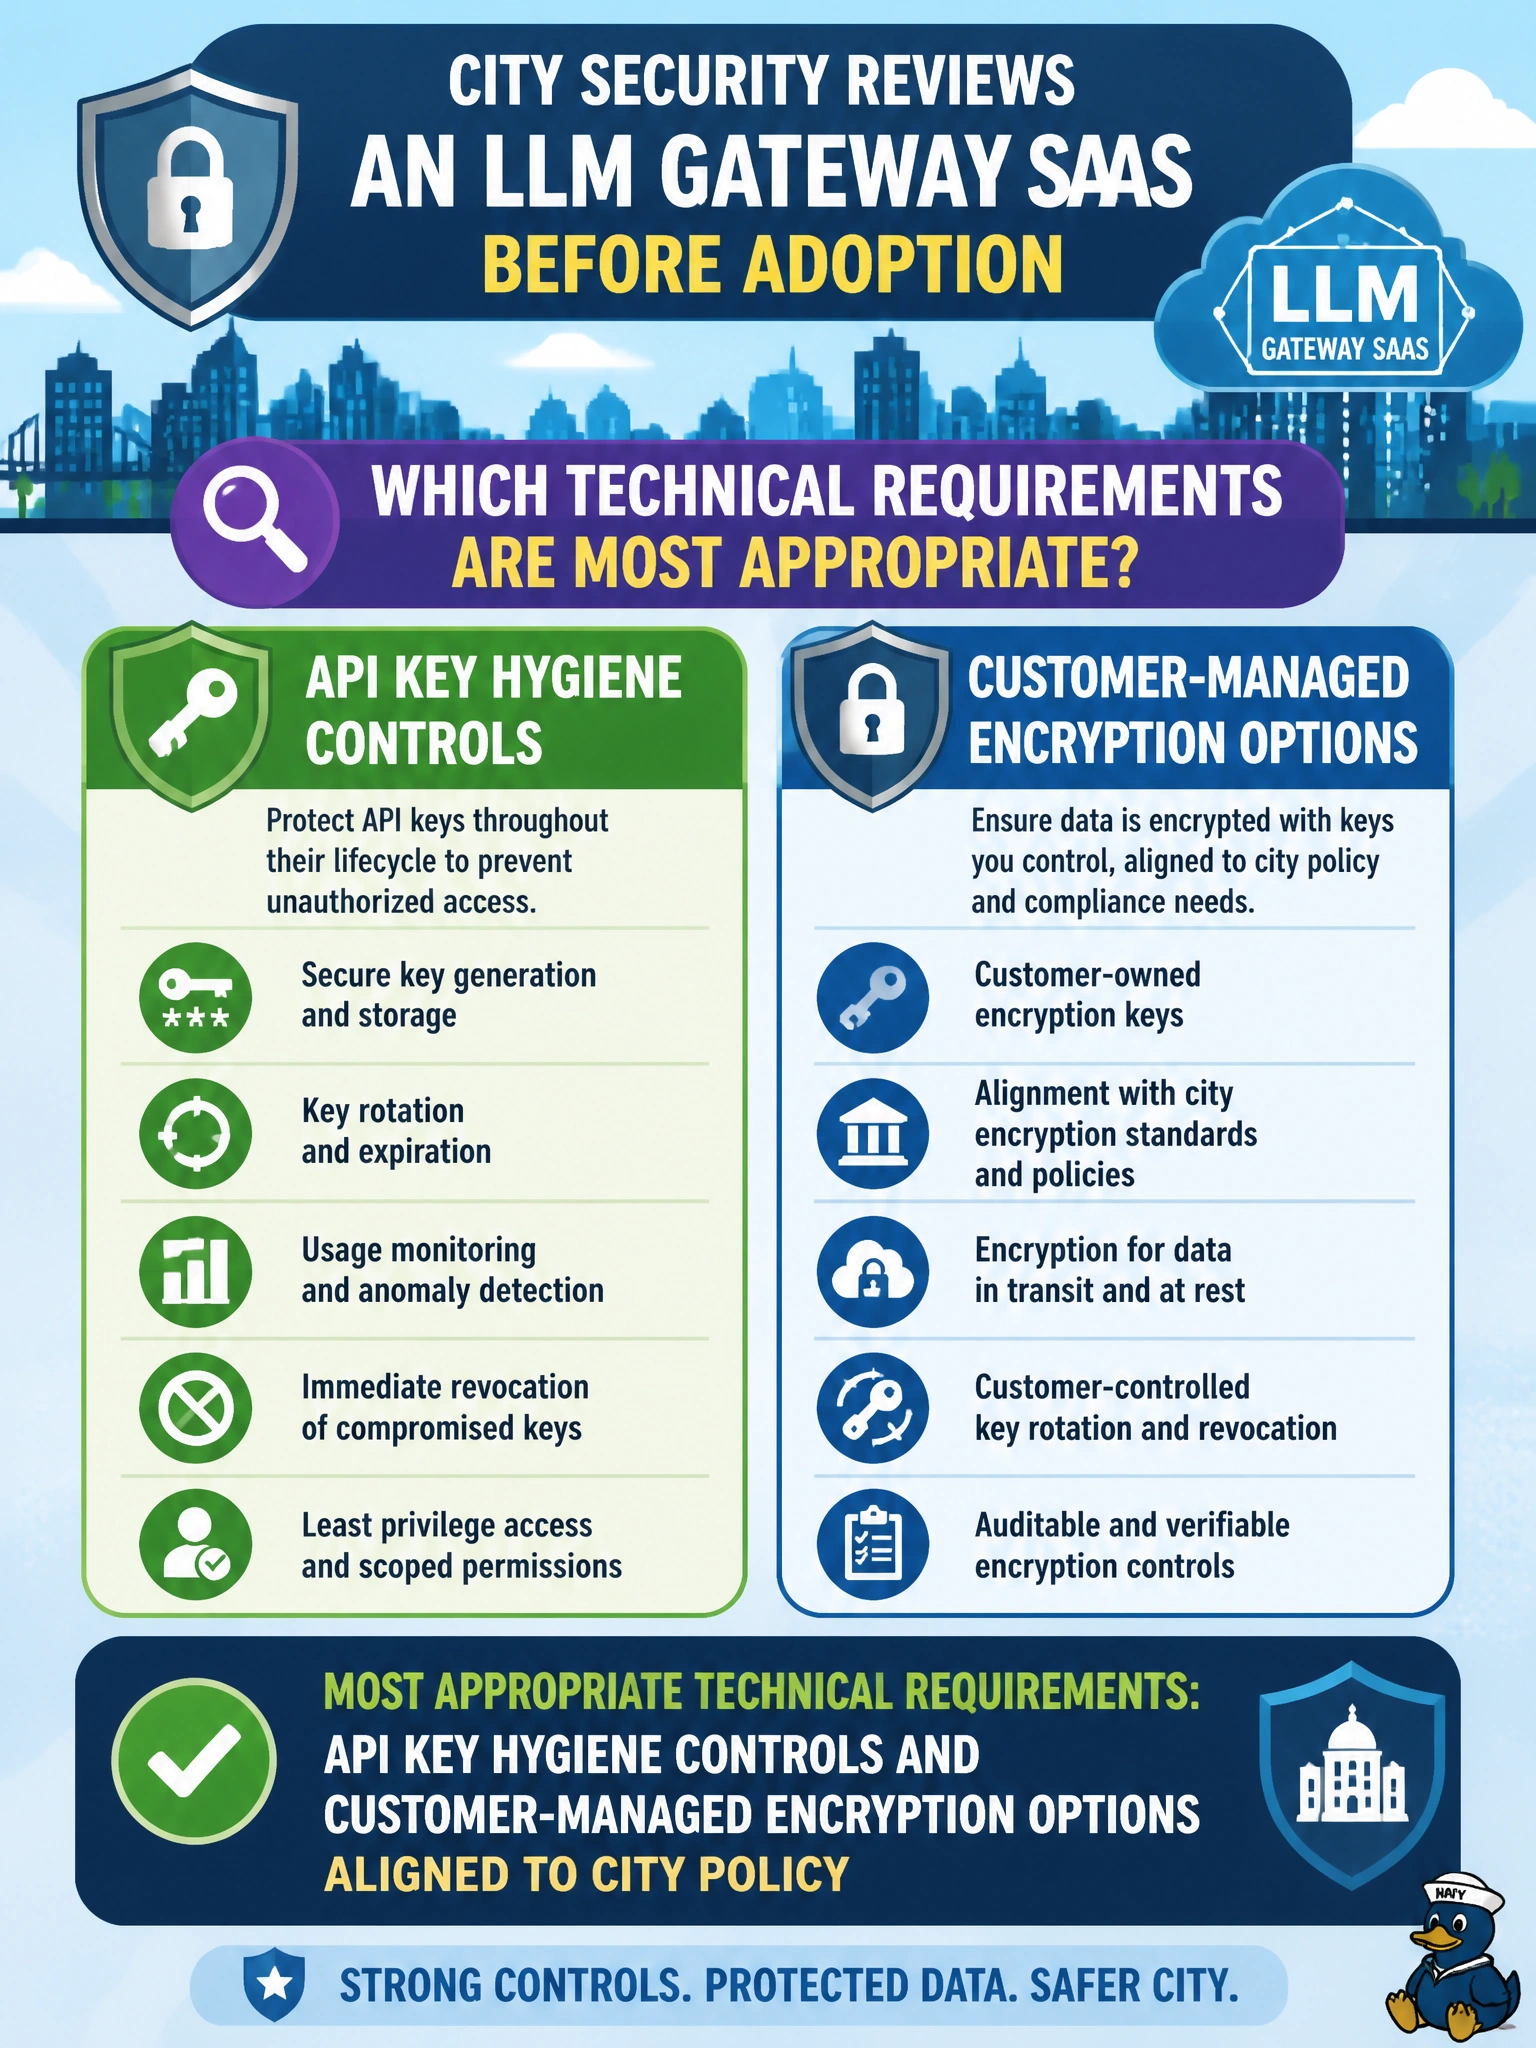
City security reviews an LLM gateway SaaS before adoption. Which technical requirements are most appropriate?
Select an answer to reveal the explanation.
Short Explanation
Gateway SaaS still needs grown-up key hygiene and encryption choices the city can own when policy says so. You're still exposed if an encrypted central archive keeps prompts broadly accessible, an org-wide vaulted key's still shared across workloads, and vendor-managed keys with long retention don't give you customer-owned control. Customer-managed options matter for municipal control.
Full Explanation
City security reviewing an LLM gateway SaaS before adoption should require API key hygiene controls and customer-managed encryption options aligned to city policy. Those technical requirements are most appropriate because gateway credentials and encryption key custody determine whether municipal prompt traffic and stored artifacts remain under city-controlled protection. Encrypted central prompt archive with audited role-based access aligned to city policy fails because it still centralizes municipal prompt artifacts for broad internal access; archiving with auditing does not provide API key hygiene or customer-managed encryption key custody required by city policy. Vendor-managed encryption keys with extended log retention aligned to city policy fails because it leaves encryption key custody with the vendor and expands retained log exposure; it does not provide customer-managed encryption options and does not address API key hygiene required by city policy. Organization-wide gateway API key with centralized vault rotation aligned to city policy fails because sharing one key across the organization weakens authentication and removes per-workload accountability for a high-value AI gateway; vaulted rotation does not fix the shared-key blast radius.
Exam caveat: customer-managed keys add operational burden; the city must staff key lifecycle processes or risk outages and unsafe workarounds. Operational check: mandate unique keys per workload, prohibit cleartext email distribution, require secrets-manager integration, and verify CMEK or equivalent options against written city policy before gateway adoption.
Prefer to study offline? Printable PDF study book + test engine ($7.50, unofficial). These questions stay free here.