
A financial institution's model risk team discovers that a third-party AI vendor has updated their credit scoring model without notification. What control should the model risk framework include to prevent this risk?
Select an answer to reveal the explanation.
Short Explanation
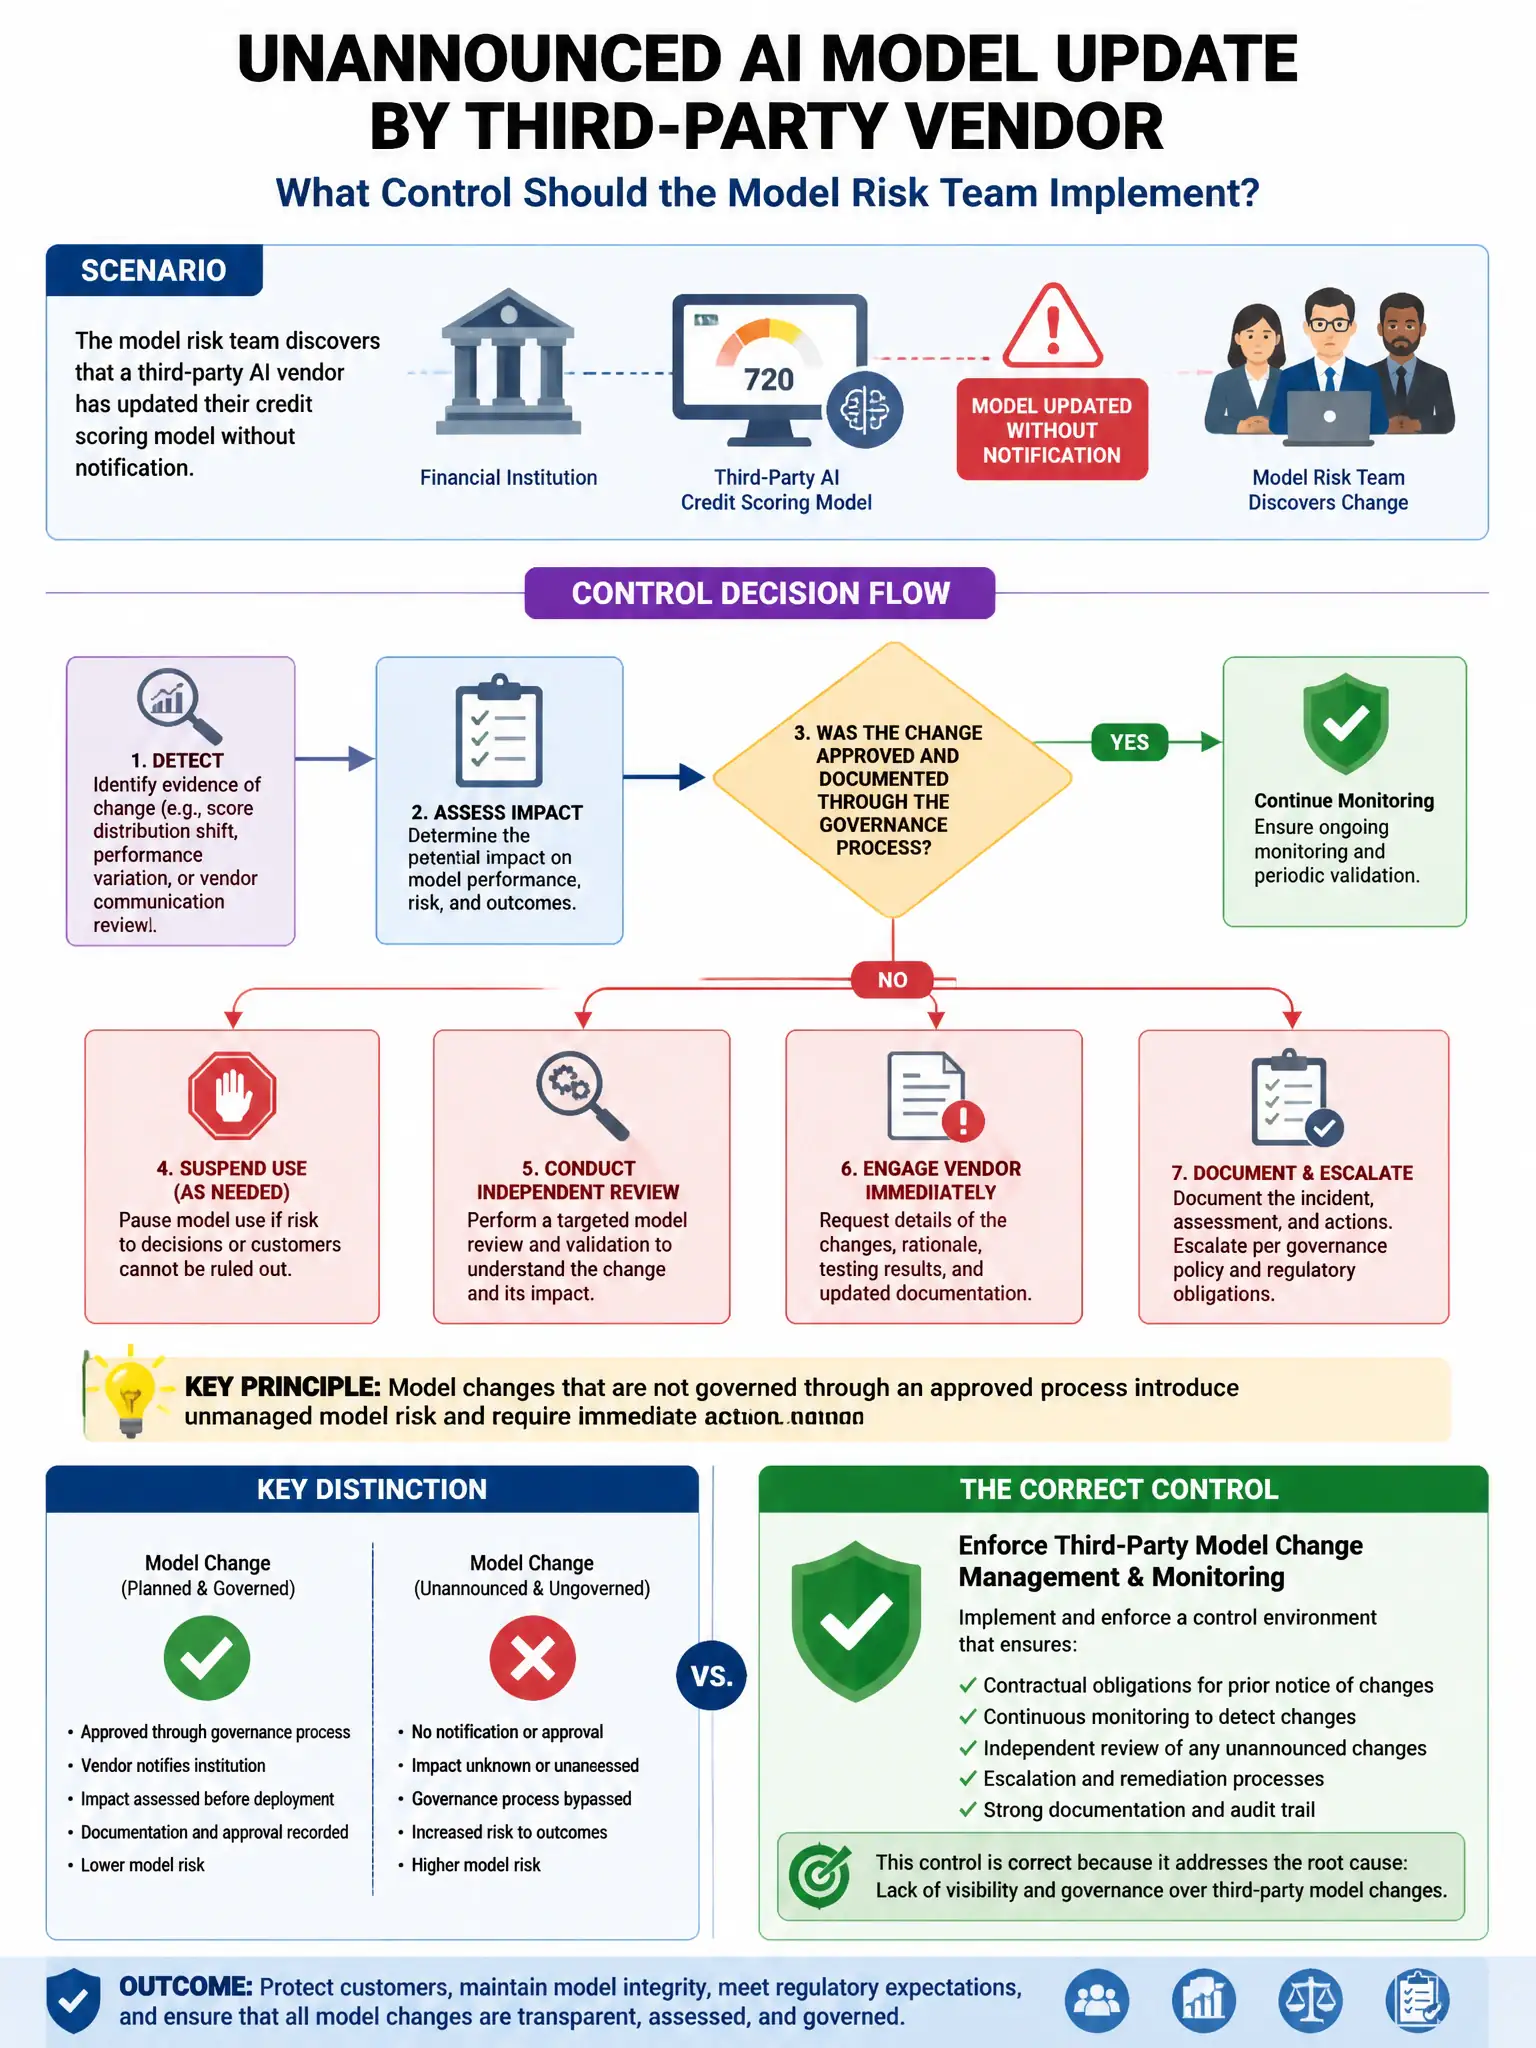
Here's the deal — you need contractual obligations for change notification and model validation rights, backed by independent performance monitoring. That gives you legal visibility and practical detection when a vendor changes a model without telling you.
Full Explanation
Contractual obligations for change notification and vendor model validation rights, supported by periodic independent performance monitoring, are correct because they give the institution legal visibility and practical detection of unauthorized model changes. Requiring open-source models only restricts vendor choice unnecessarily. Prohibiting third-party AI models for regulatory capital calculations is overly broad. Network monitoring for API traffic changes is technical but insufficient without contractual rights.