
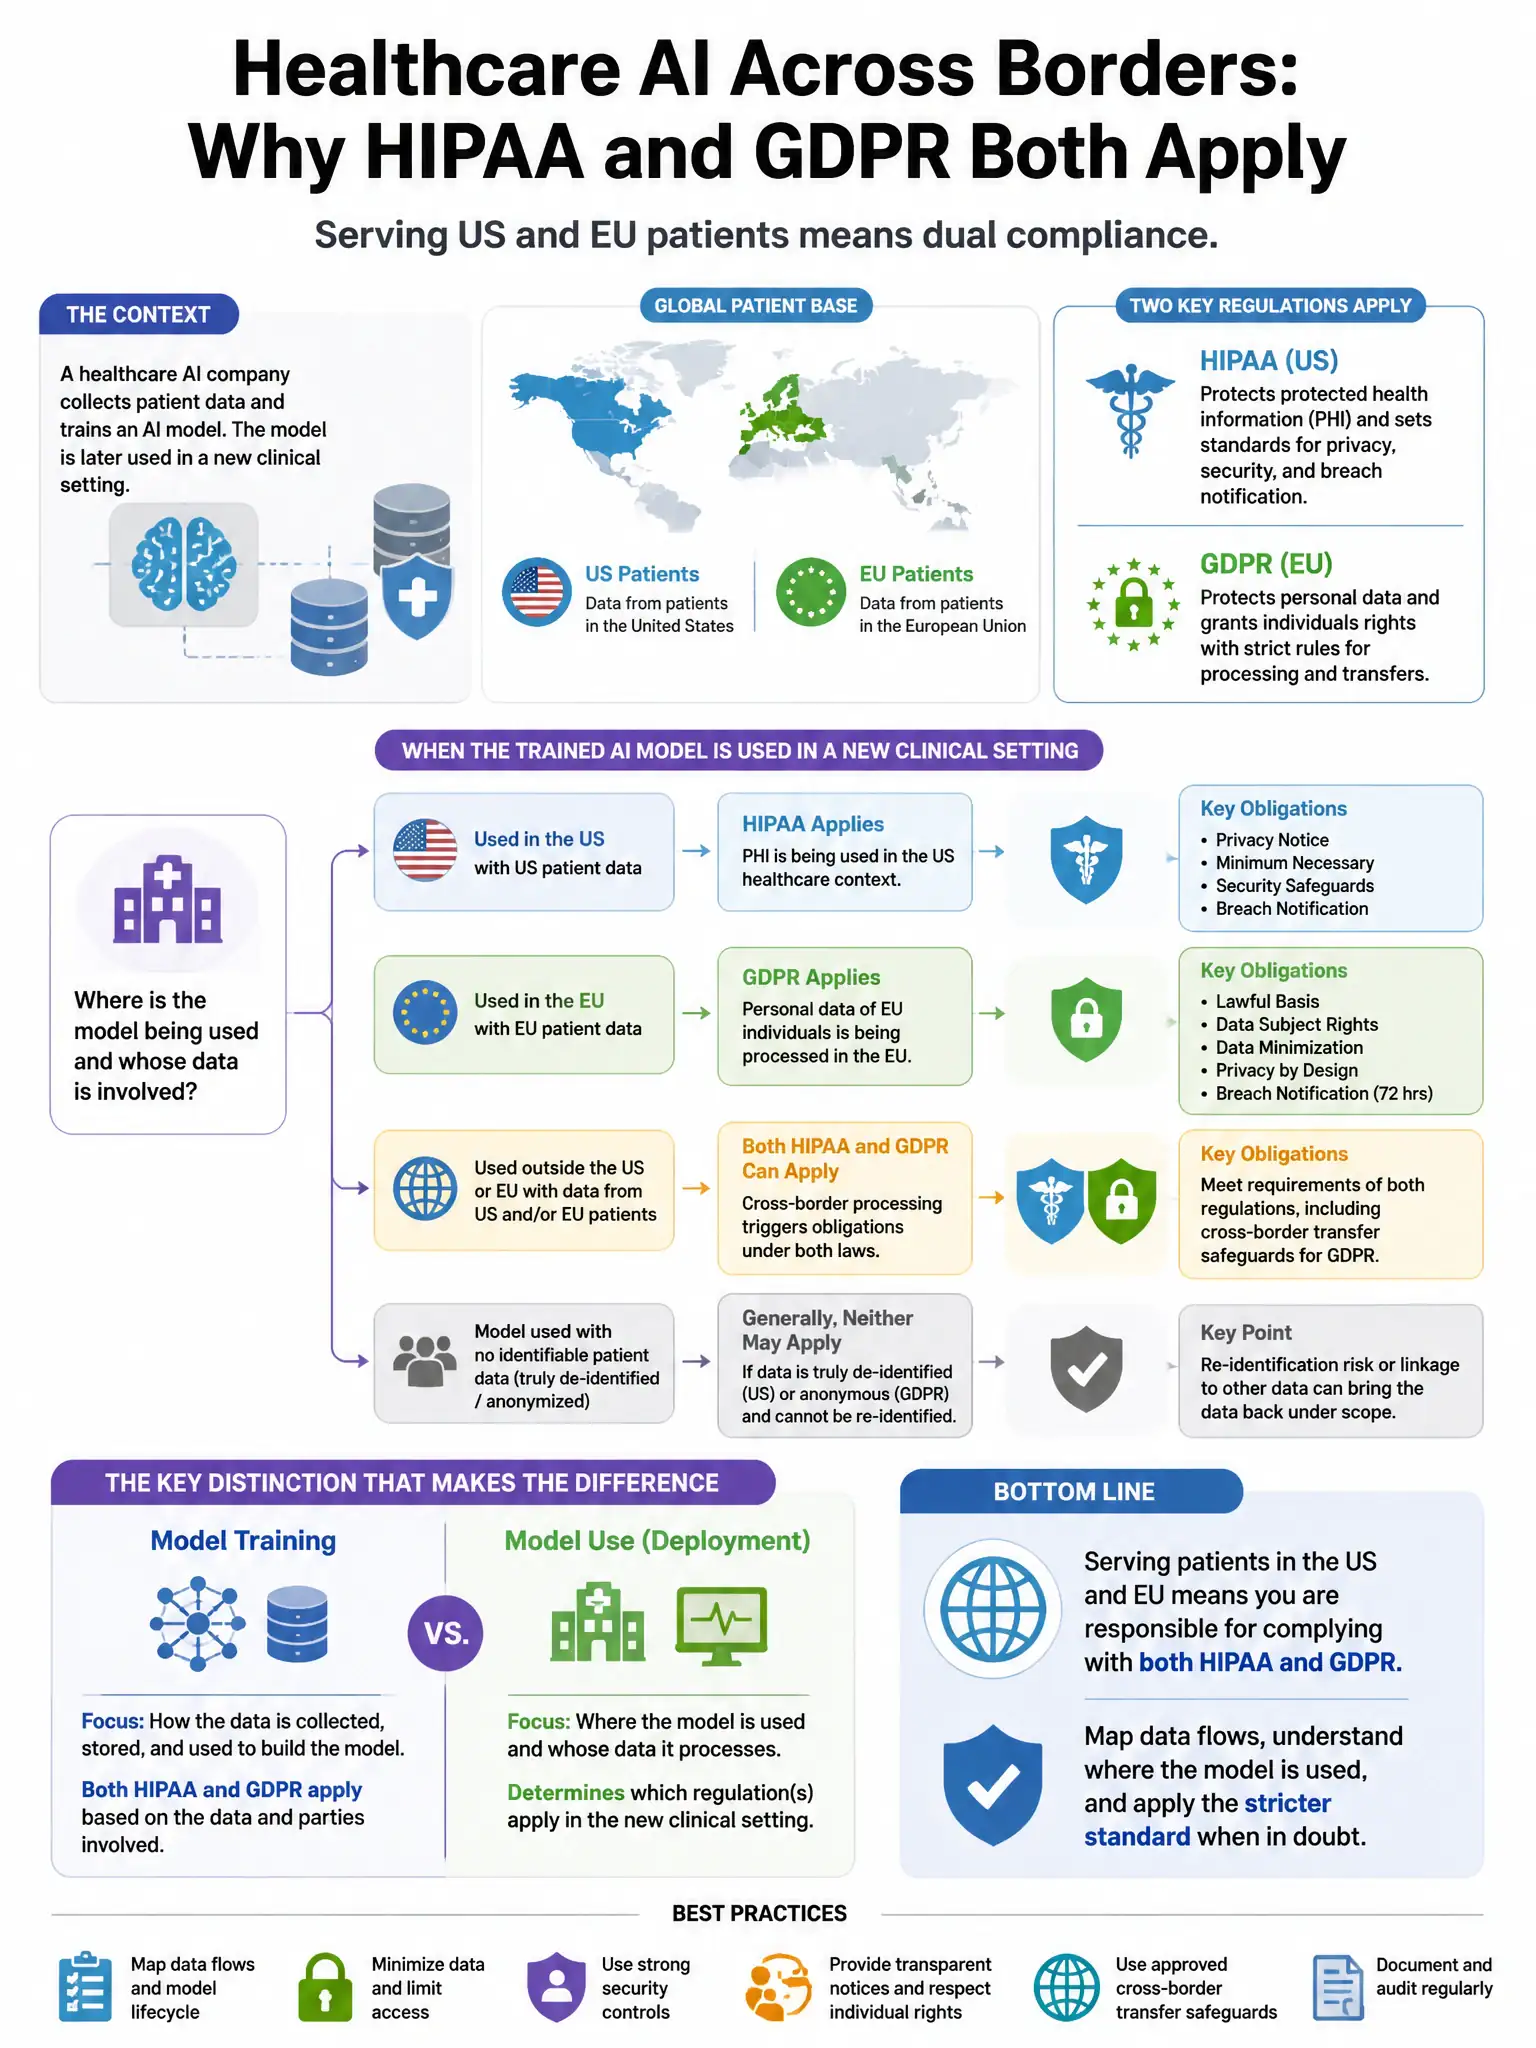
A healthcare AI company is subject to both HIPAA and GDPR because it serves US and EU patients. When an AI model trained on patient data is later used in a new clinical setting, which compliance obligation is MOST critical to address FIRST?
Select an answer to reveal the explanation.
Short Explanation
You’ve got to check first whether the new clinical use fits the original purpose you got consent or authorization for. HIPAA and GDPR both make that purpose check the starting point, so don’t jump to retraining, model cards, or privacy tweaks until you know the use is allowed.
Full Explanation
Assessing whether the new use falls within the original purpose for which consent or authorization was obtained is correct because HIPAA’s minimum necessary standard and permitted uses, and GDPR’s purpose limitation principle under Article 5(1)(b), require personal data to be used only for purposes compatible with the original collection, making purpose assessment the foundational first step. Re-training with synthetic data, publishing a model card, and applying differential privacy may be relevant next steps, but their necessity cannot be determined until the purpose assessment is complete.