
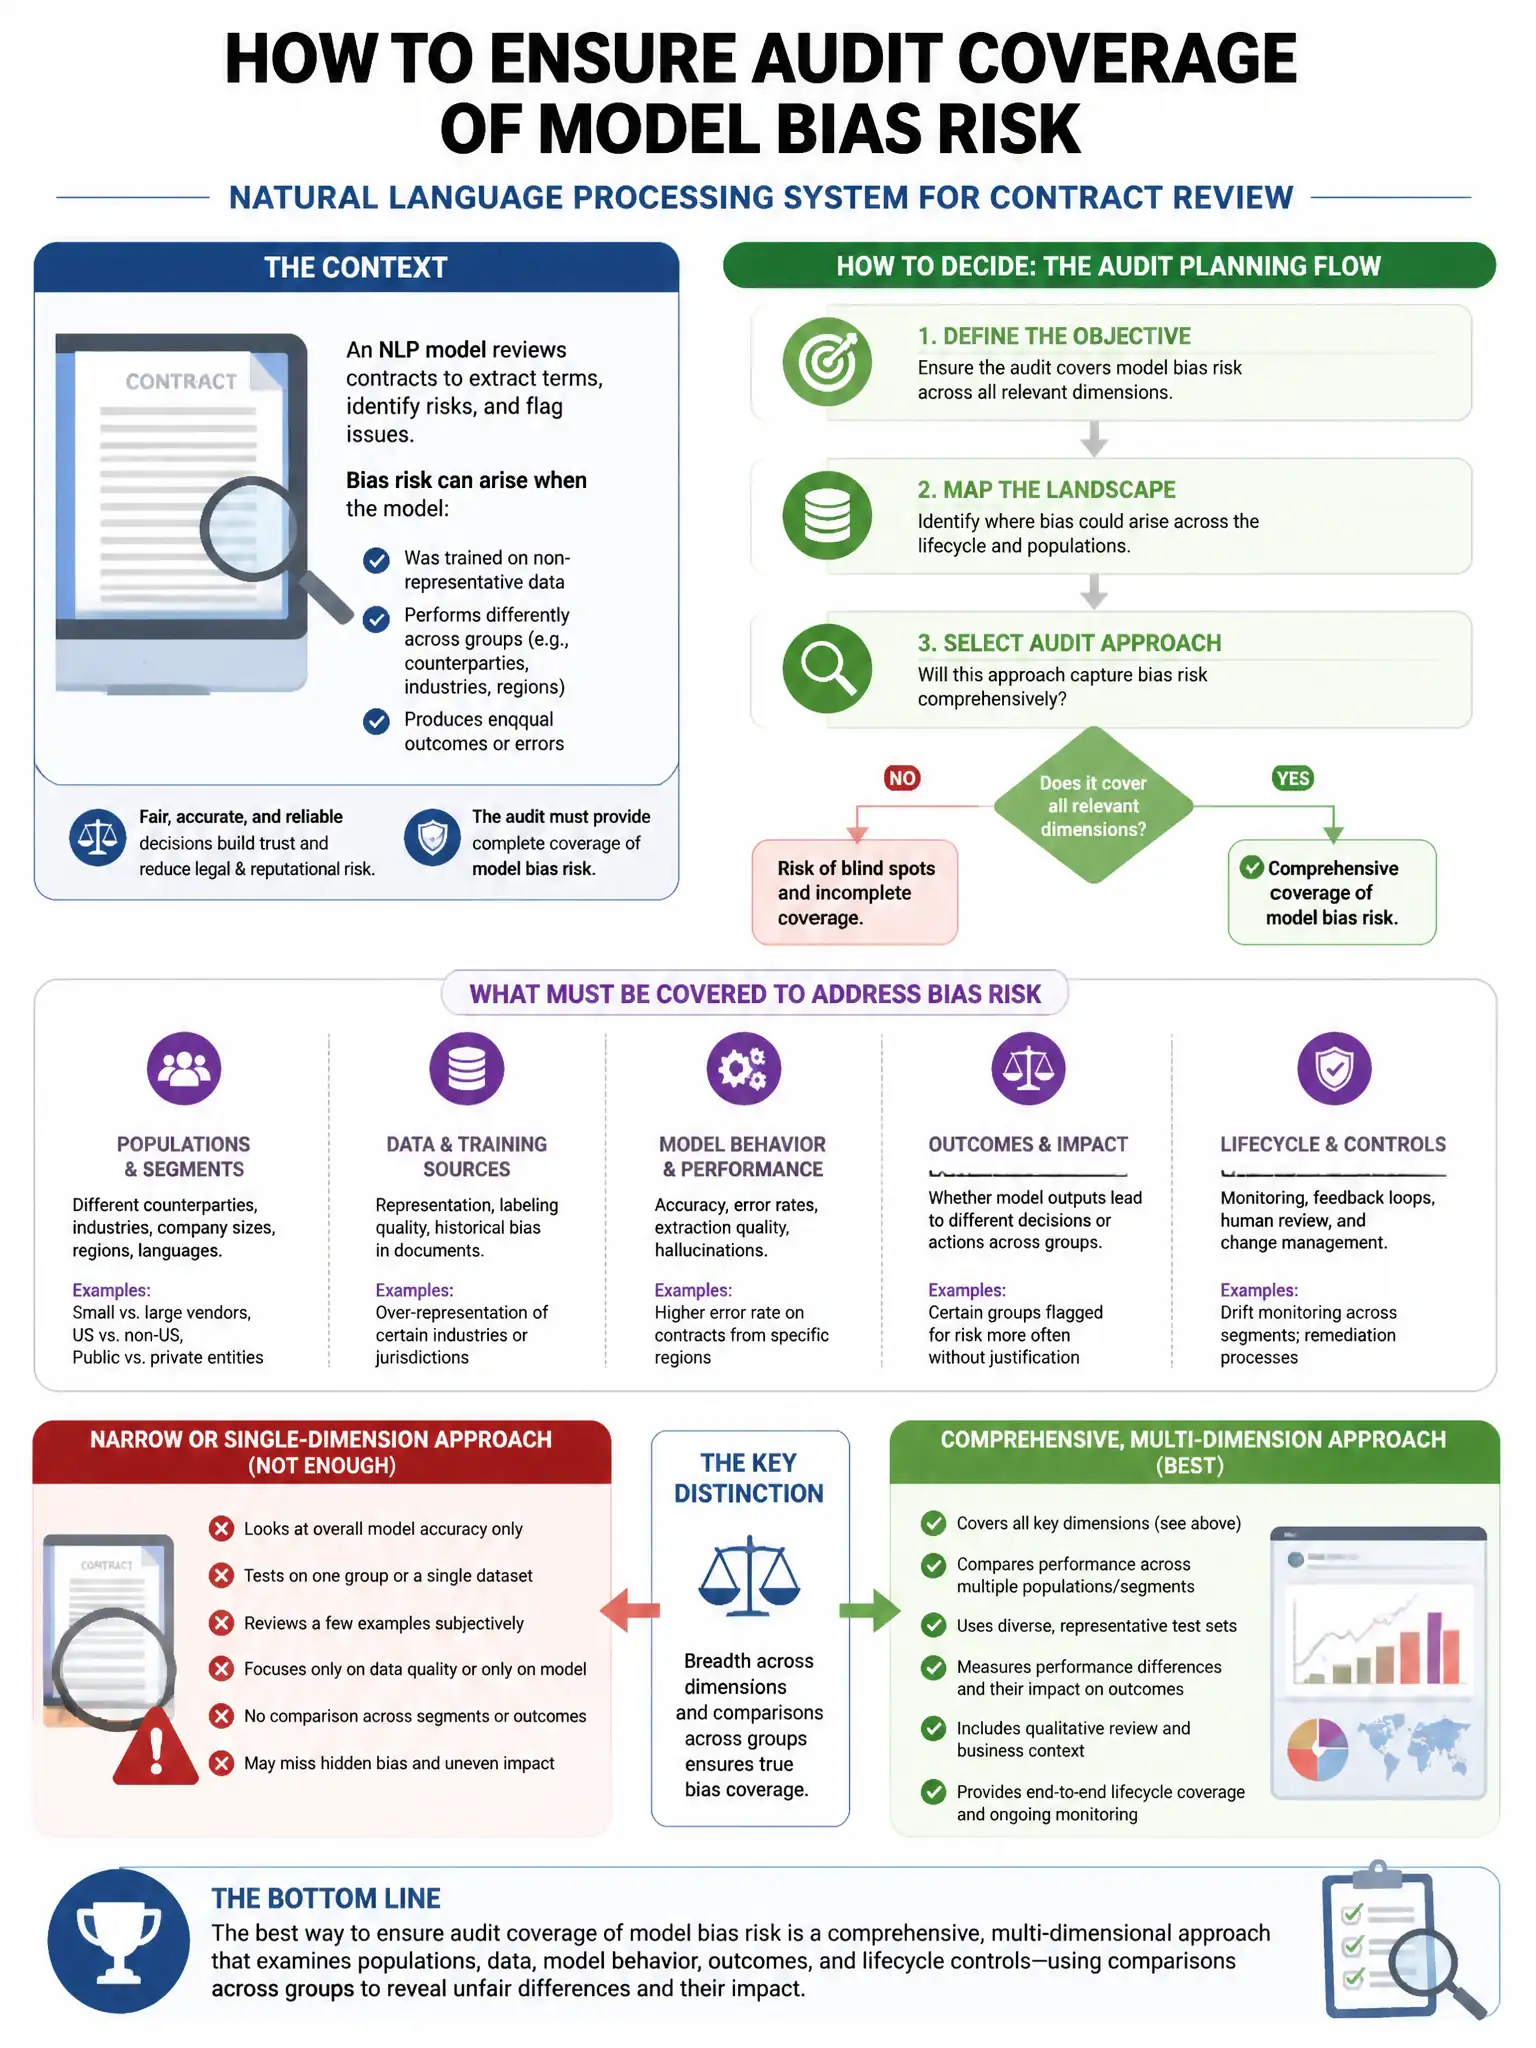
An internal AI audit team is planning an audit of a natural language processing system used for contract review. Which approach BEST ensures audit coverage of model bias risk?
Select an answer to reveal the explanation.
Short Explanation
You need to test the model's outputs on stratified samples across relevant demographic and document-type subgroups. That shows whether bias affects different segments. Reading code, vendor policies, or API security checks won't prove bias coverage.
Full Explanation
The best approach is testing model outputs on stratified samples across relevant demographic and document-type subgroups because bias audits require empirical testing on representative subgroups, revealing whether performance is consistent across segments. Reviewing source code for commented-out bias correction routines is insufficient because code review alone does not surface emergent bias. Verifying a published responsible AI policy is a governance indicator but does not test actual model behavior. Confirming API multi-factor authentication addresses security, not bias.