
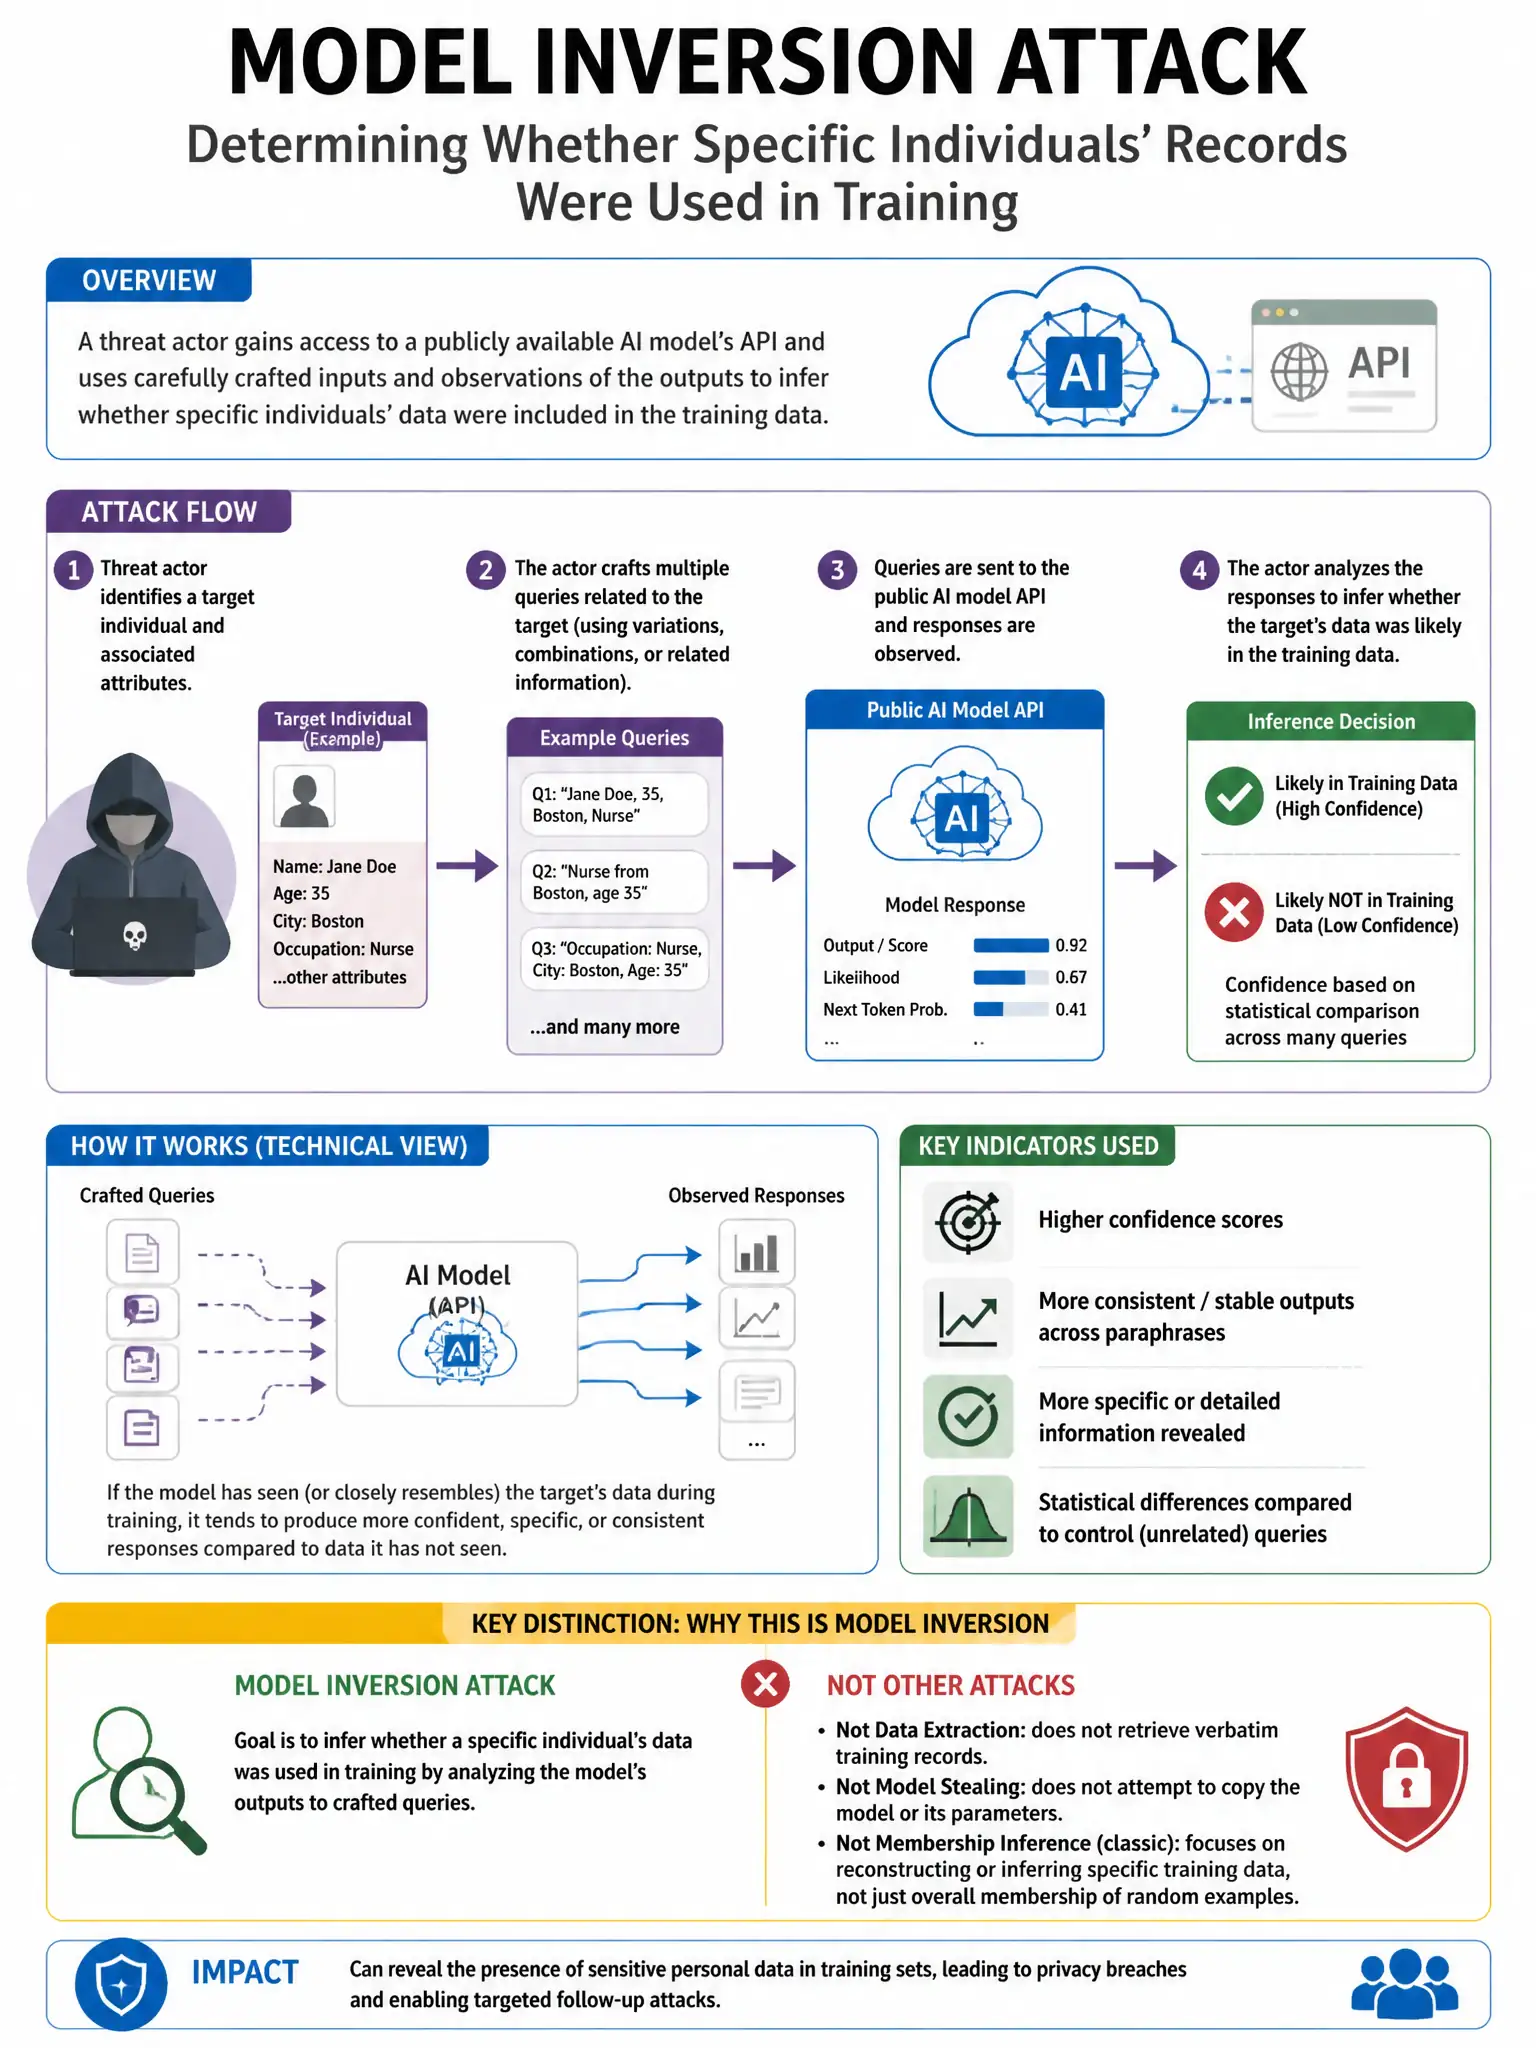
A threat actor gains access to a publicly available AI model's API and uses it to determine whether specific individuals' records were used in training. Which attack does this describe?
Select an answer to reveal the explanation.
Short Explanation
You're looking at a membership inference attack because the attacker queries the model's API to figure out whether specific records were in the training data. That's a privacy risk, not a way to copy the model or rebuild training data from gradients.
Full Explanation
A membership inference attack is correct because it involves querying a model's API to determine whether specific individuals' records were used in training, which poses significant privacy risks. A model extraction attack is wrong because it aims to replicate model functionality rather than determine training membership. A feature correlation attack is not a standard attack category for this scenario. A gradient inversion attack is wrong because it reconstructs training data from gradients, typically in federated learning settings.