
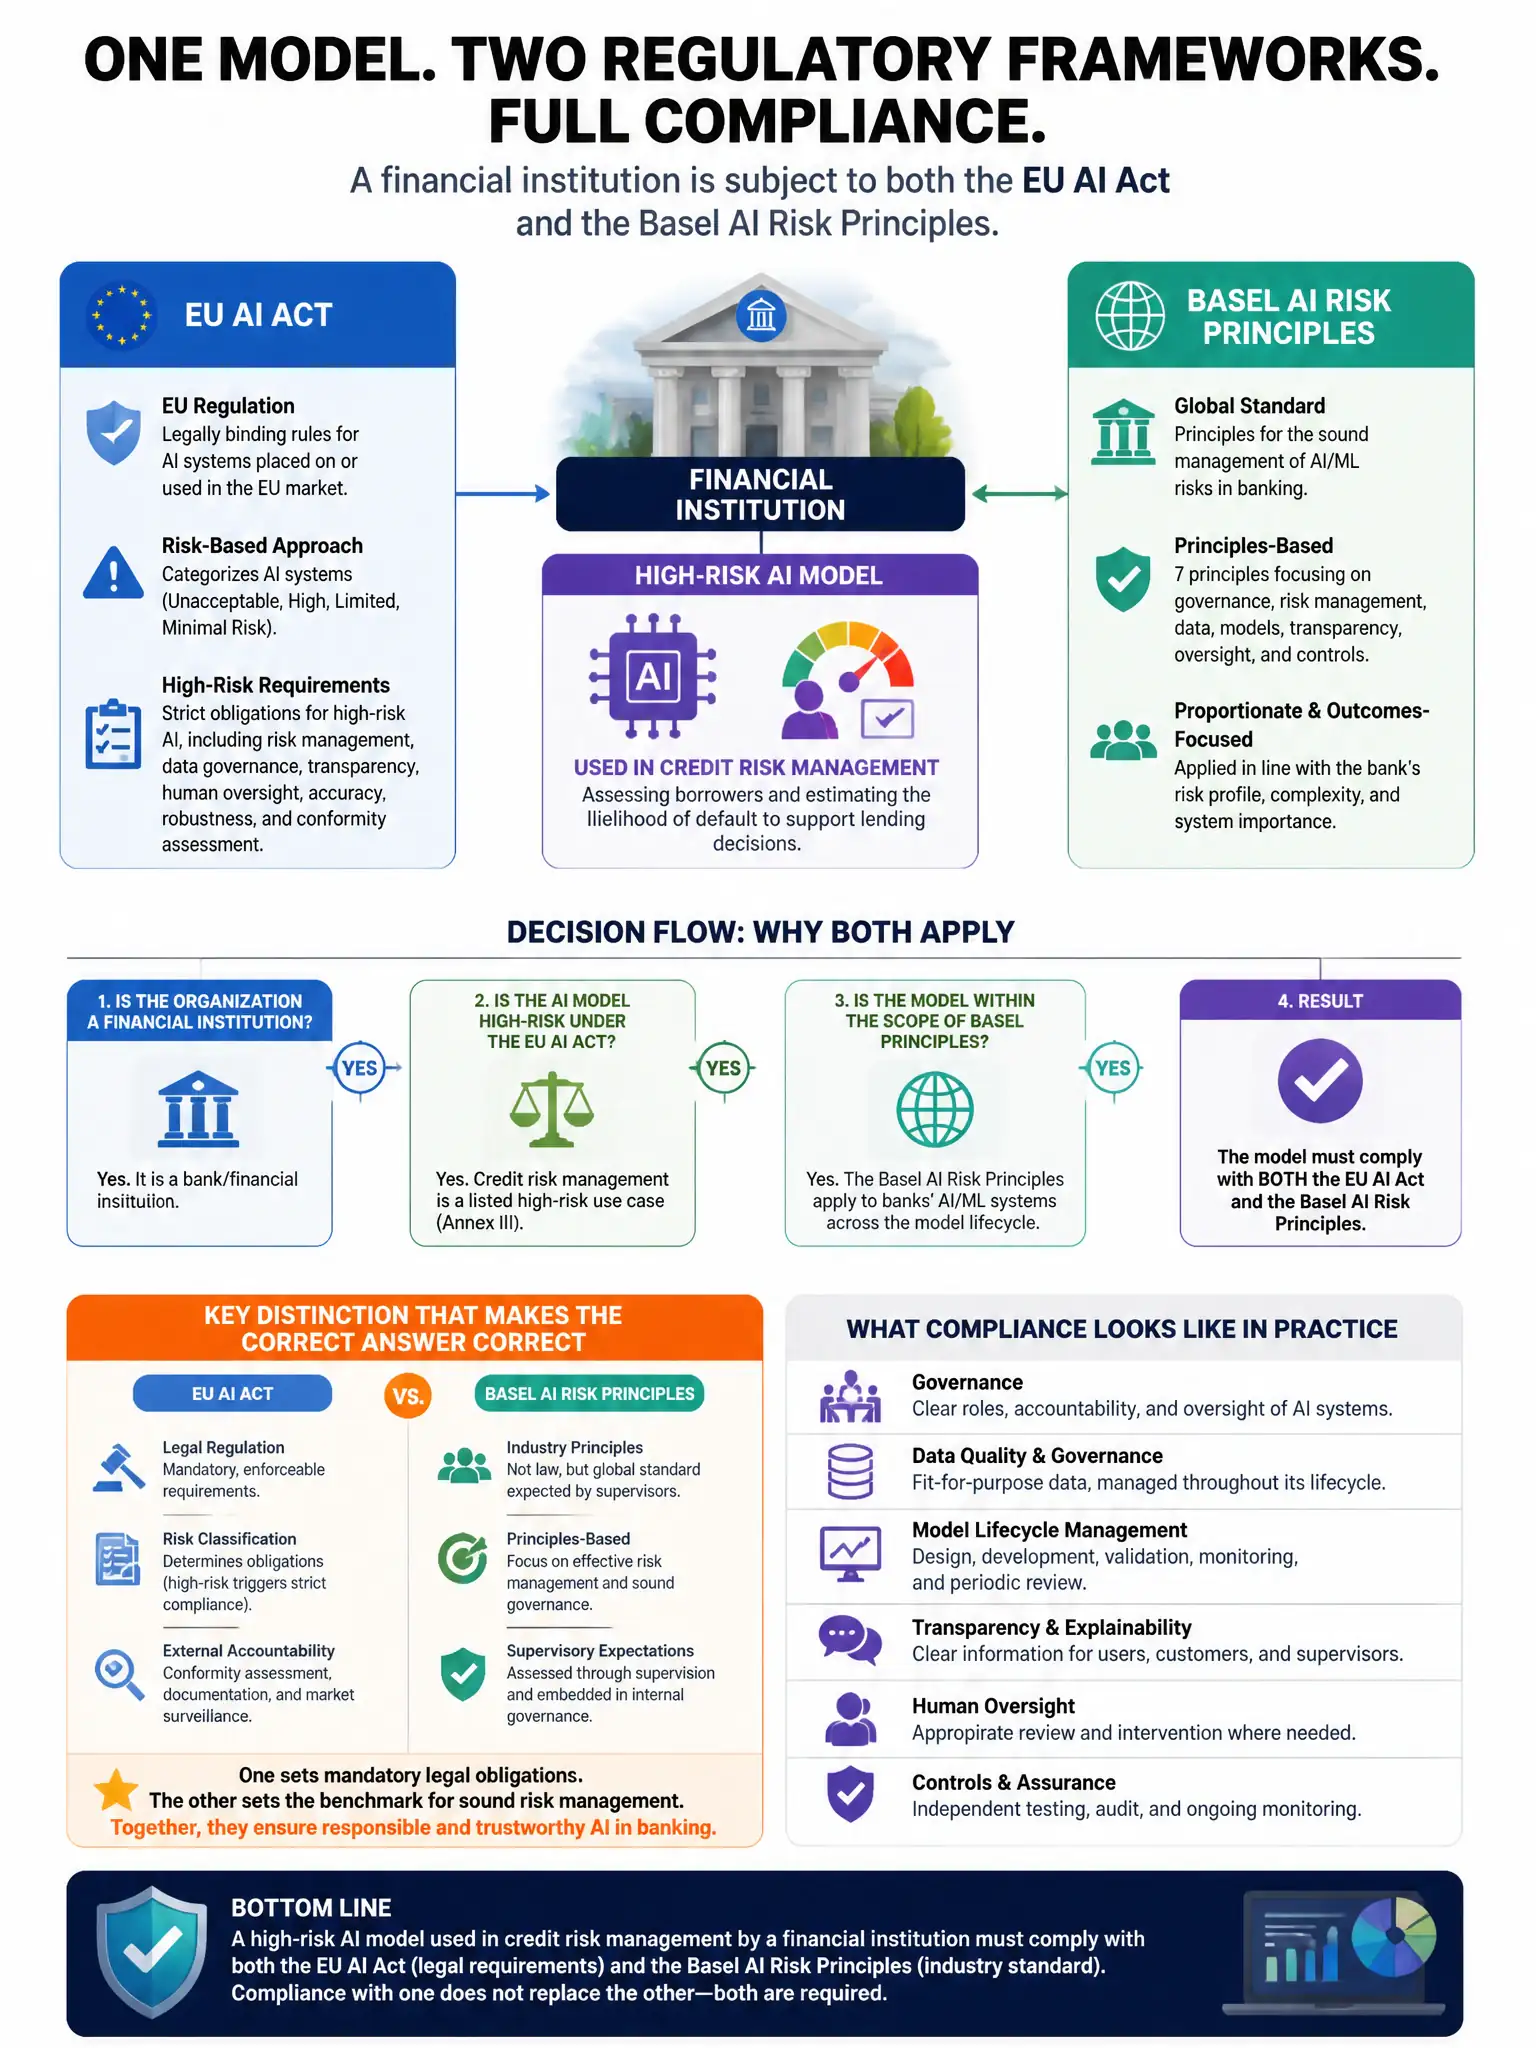
A financial institution is subject to both the EU AI Act and the Basel AI Risk Principles. A high-risk AI model used in credit risk management must comply with both frameworks. Which control would MOST effectively address requirements under both frameworks simultaneously?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — the control that combines robust model documentation, independent validation with explainability testing, ongoing performance monitoring, and human oversight for material decisions is the one that works because it hits the shared requirements of the European Union AI Act and Basel/SR 11-7 model risk rules. You get transparency, validation, monitoring, and governance in one practical control set.
Full Explanation
The correct control is the one that implements robust model documentation, independent validation with explainability testing, ongoing performance monitoring, and human oversight for material decisions. It works because the overlapping requirements of the European Union AI Act for high-risk AI systems—documentation, conformity assessment, human oversight, and transparency—and the Basel/SR 11-7 model risk principles—independent validation, explainability, monitoring, and governance—converge on a common set of practices: comprehensive documentation, independent validation that includes explainability assessment, ongoing performance monitoring, and human oversight for consequential decisions. These controls satisfy both frameworks' core requirements efficiently. Publishing the model's training data on the institution's public website is not required and may violate confidentiality. Registering the model in the European Union AI Act's notified body database and filing a compliance declaration satisfies only one framework's administrative requirement. Limiting the model's use to advisory recommendations so that all final credit decisions remain with human credit officers may be overly restrictive and still doesn't address validation requirements.