
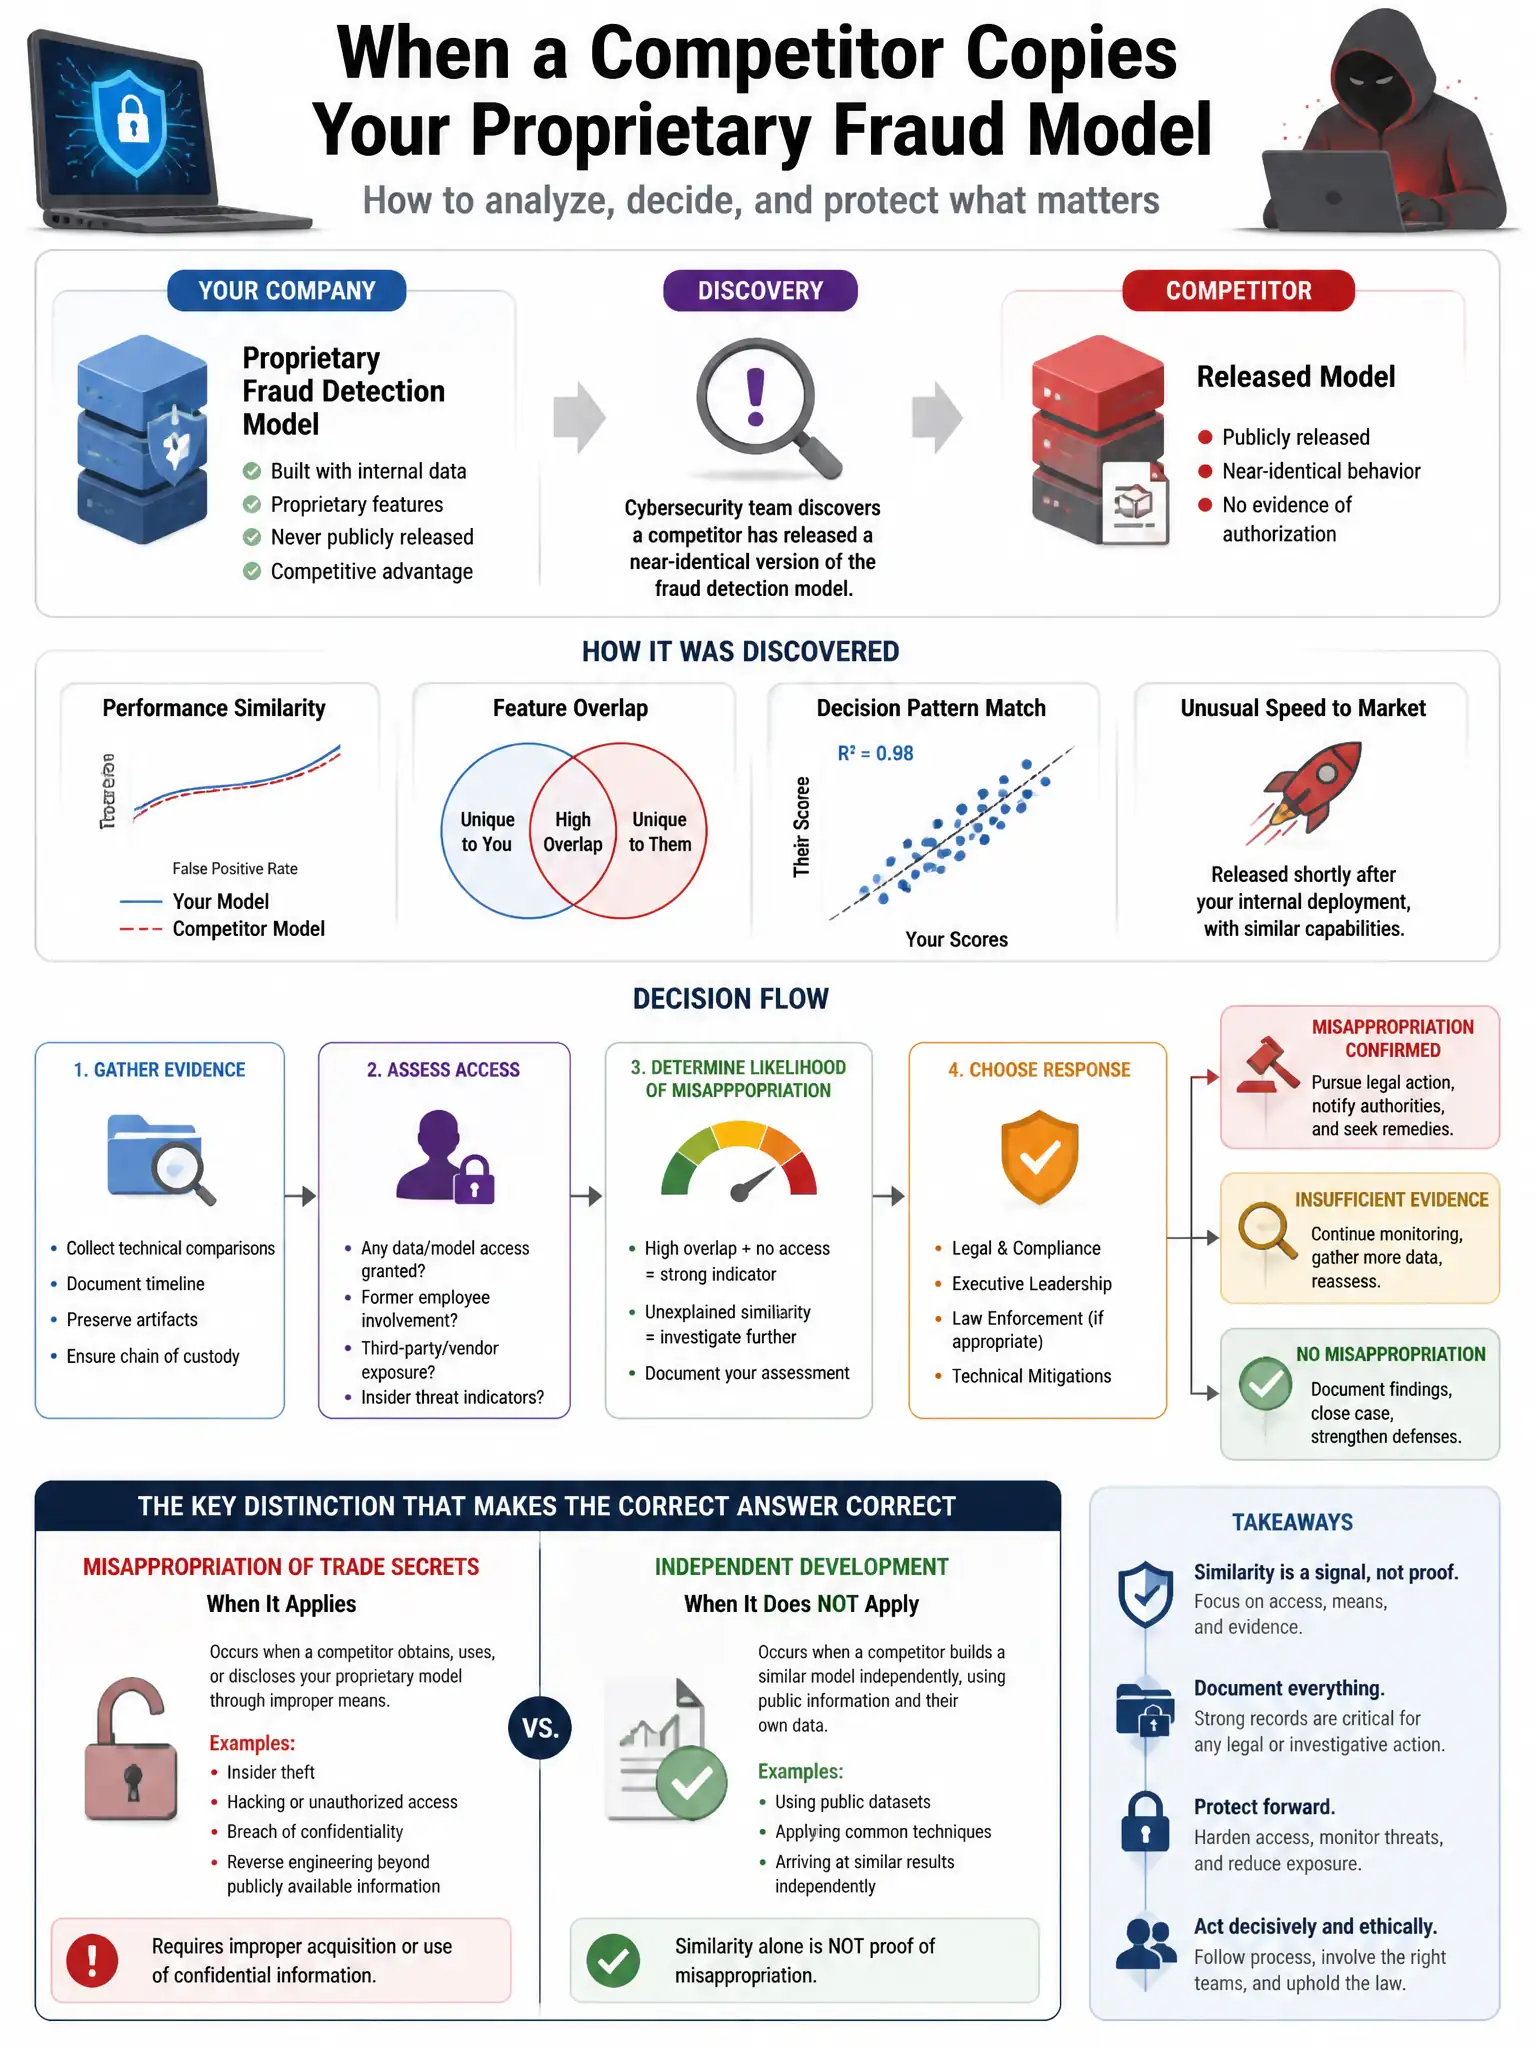
A cybersecurity team discovers that a competitor has released a near-identical version of their proprietary fraud detection model. The internal model was never publicly released. Which attack is the MOST likely explanation?
Select an answer to reveal the explanation.
Short Explanation
If a model was never public and a competitor has a near-identical copy, you're most likely looking at an insider who copied the weights or artifacts. API-based extraction usually gives a similar surrogate, not a near-identical clone.
Full Explanation
The insider threat where a model developer copied the model weights and shared them with the competitor is correct because a near-identical copy of a model that was never publicly released is most consistent with direct exfiltration by someone with internal access to the model weights, training code, or artifacts. The model extraction attack where the competitor repeatedly queried the internal model's API to train a surrogate model would typically produce a functionally similar but not near-identical model, and would require API access. The data poisoning attack that caused the internal model to behave identically to the competitor's model affects model behavior, not replication. The adversarial evasion attack that caused the internal model to adopt the competitor's decision boundaries affects how the model responds to specific inputs, not model structure. The near-identical characterization strongly suggests direct copying rather than reverse engineering.