
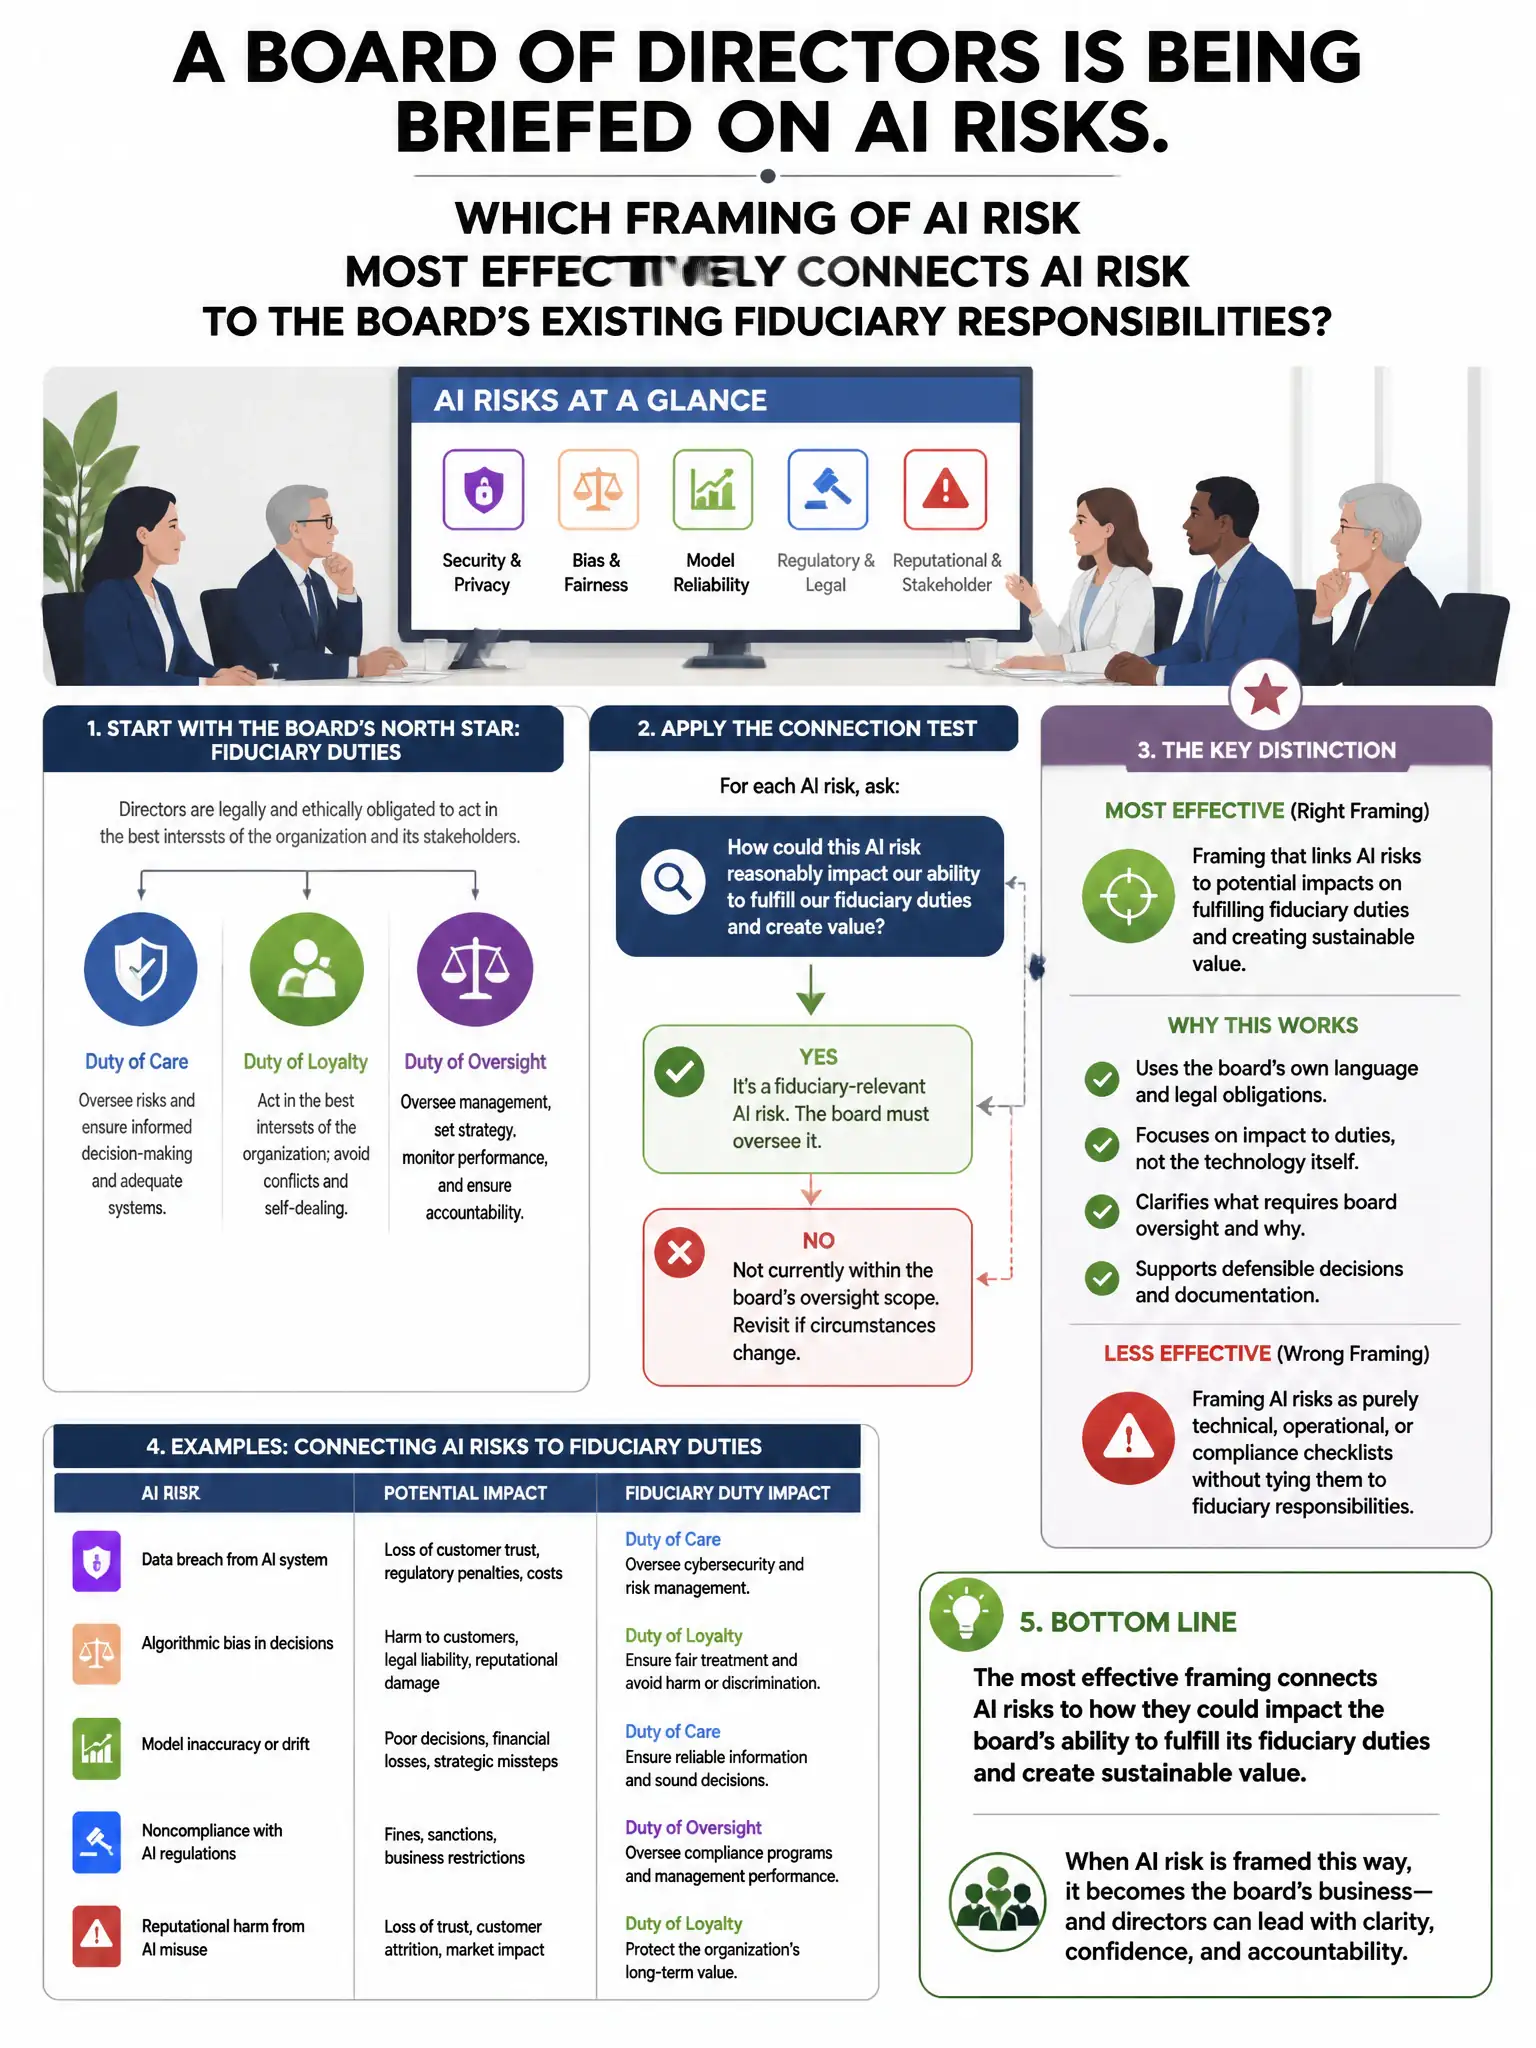
A board of directors is being briefed on AI risks. Which framing of AI risk MOST effectively connects AI risk to the board's existing fiduciary responsibilities?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you need to frame AI risk in terms boards already own: operational, legal/regulatory, and reputational risk that can hit shareholder value. That makes AI a fiduciary oversight issue, not just a tech problem.
Full Explanation
Presenting AI risks (bias, errors, regulatory non-compliance, reputational harm) as operational, legal/regulatory, and reputational risk that can threaten shareholder value and require board-level oversight is correct because boards govern through enterprise risk and shareholder value. Mapping AI risks to categories the board already oversees integrates AI risk into governance without requiring technical expertise. Describing models as black boxes may alarm the board without actionable framing. Focusing on hacking and offline systems is only one aspect. Recommending a technology-specialist-only committee would exclude the business judgment the board provides.