
An organization is evaluating whether to adopt ISO/IEC 42001 as its AI management system standard. A senior manager argues that the organization's existing ISO 27001 certification already covers AI systems. How should the AI risk manager respond?
Select an answer to reveal the explanation.
Short Explanation
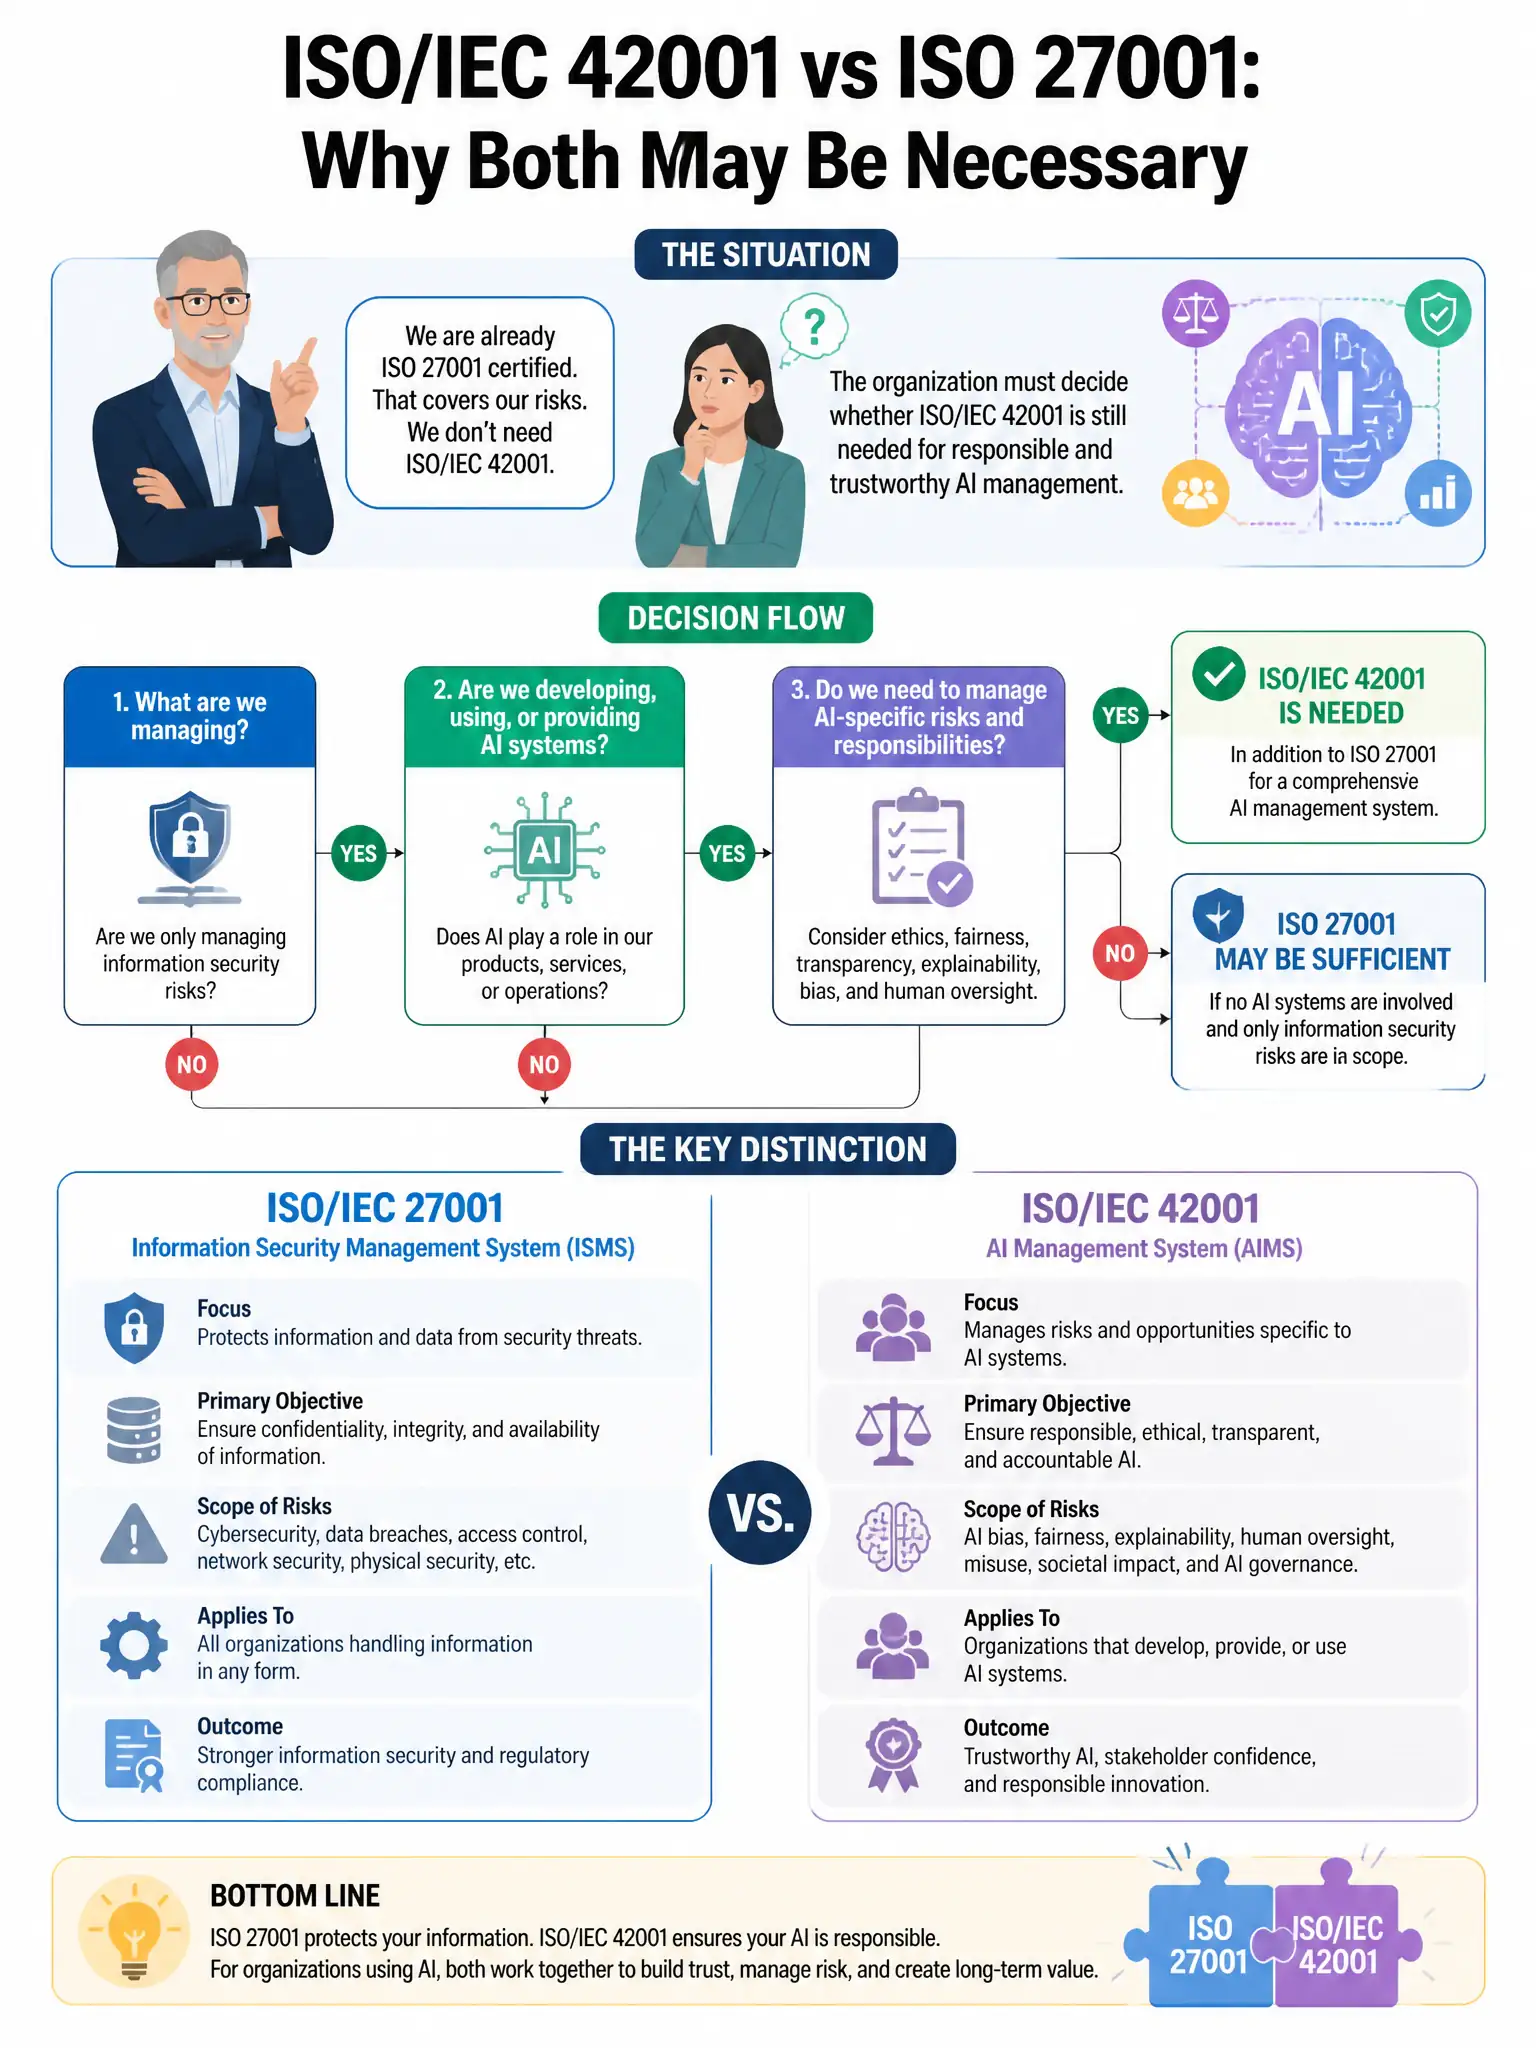
You shouldn't agree that ISO 27001 already covers AI. ISO 27001 handles information security risks, while ISO/IEC 42001 adds AI-specific governance, transparency, fairness, and accountability requirements. They're complementary, not redundant.
Full Explanation
ISO 27001 addresses information security management, including confidentiality, integrity, and availability of information assets, but it does not cover AI-specific concerns such as model fairness, bias, explainability, AI-specific governance structures, impact assessments, and AI system transparency. ISO/IEC 42001 is specifically designed for the unique governance challenges of AI systems, so the two standards are complementary, not redundant. The view that ISO 27001 covers all information system risks including AI-specific risks is wrong because those AI-specific governance concerns fall outside ISO 27001's scope. The claim that ISO/IEC 42001 is only necessary for developers, not deployers of third-party AI, is wrong because it applies to both. The recommendation to replace ISO 27001 with ISO/IEC 42001 is also wrong because both address different risk domains and should be maintained concurrently.