
An organization's AI red team is tasked with finding vulnerabilities in an LLM-powered agent that has access to internal databases and can execute SQL queries. Which attack scenario represents the HIGHEST severity risk?
Select an answer to reveal the explanation.
Short Explanation
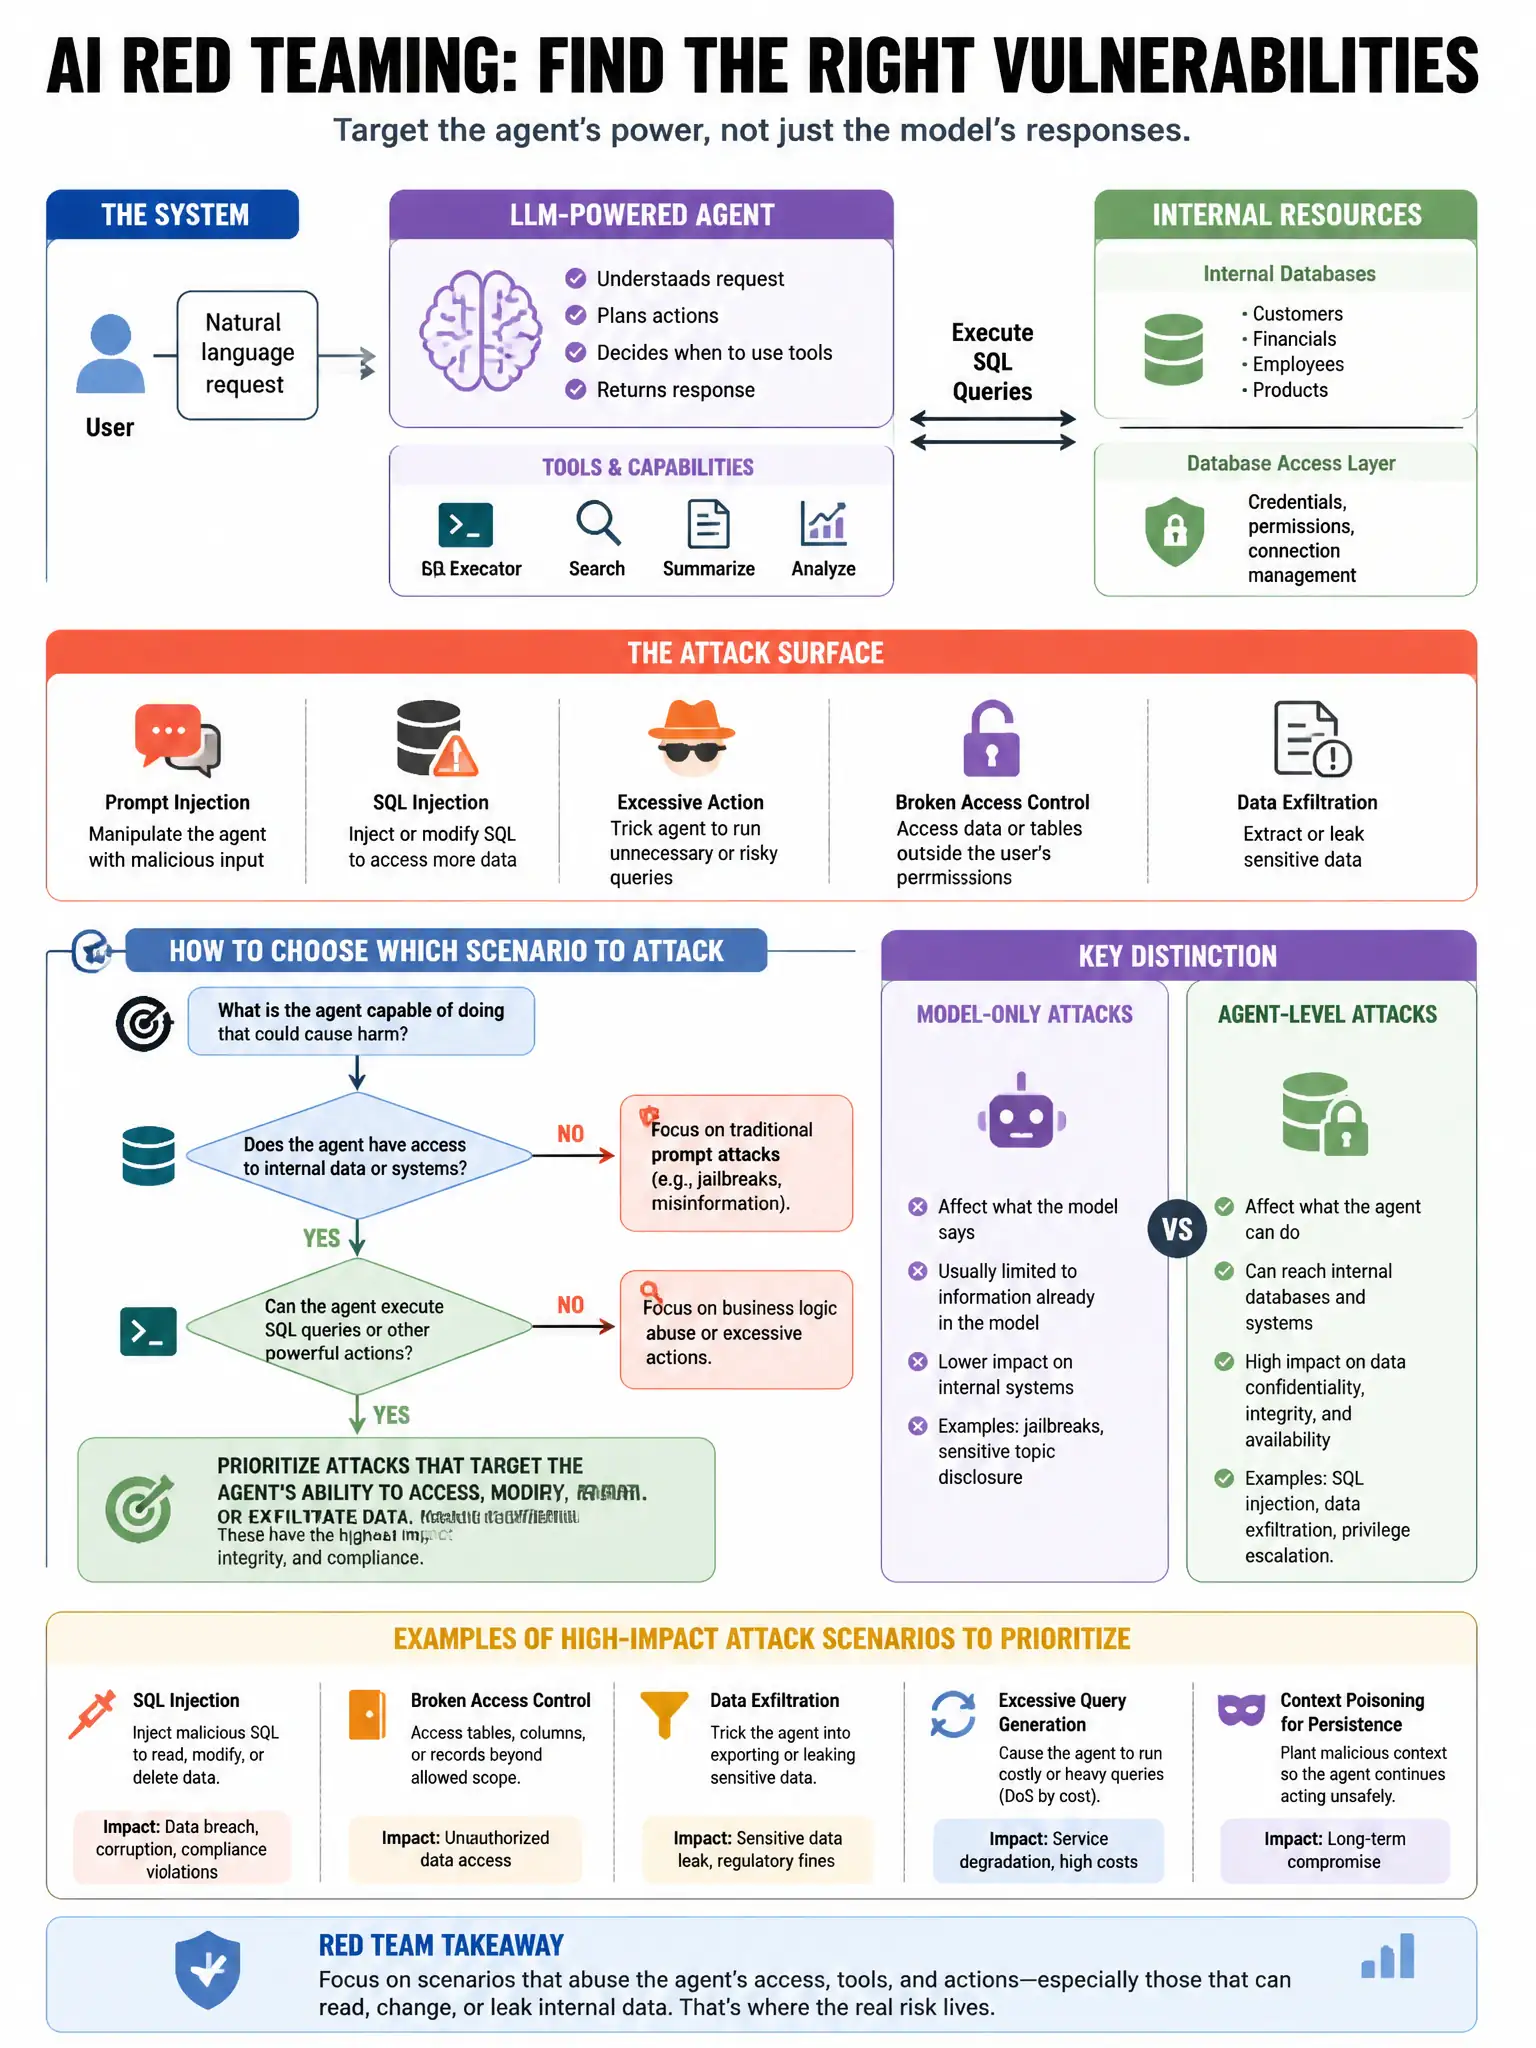
Here's the deal — you're looking for the scenario where a crafted user message tricks an LLM agent into running a DROP TABLE command on production. That's catastrophic because it combines prompt injection with real database access, hitting integrity and availability hard.
Full Explanation
The scenario where a crafted user message manipulates the model into executing a DROP TABLE command on the production database is correct because an agentic AI with database write/delete access that can be manipulated to execute destructive SQL commands represents a catastrophic integrity and availability risk. This combines prompt injection (the attack vector) with real-world system access (the blast radius). Causing the model to generate grammatically incorrect responses is a quality issue with minimal harm. Extracting the system prompt used to configure the model's behavior is a moderate confidentiality risk. Causing the model to refuse to answer legitimate user queries is a service availability issue. The DROP TABLE manipulation has both high likelihood of exploitation and catastrophic impact.