
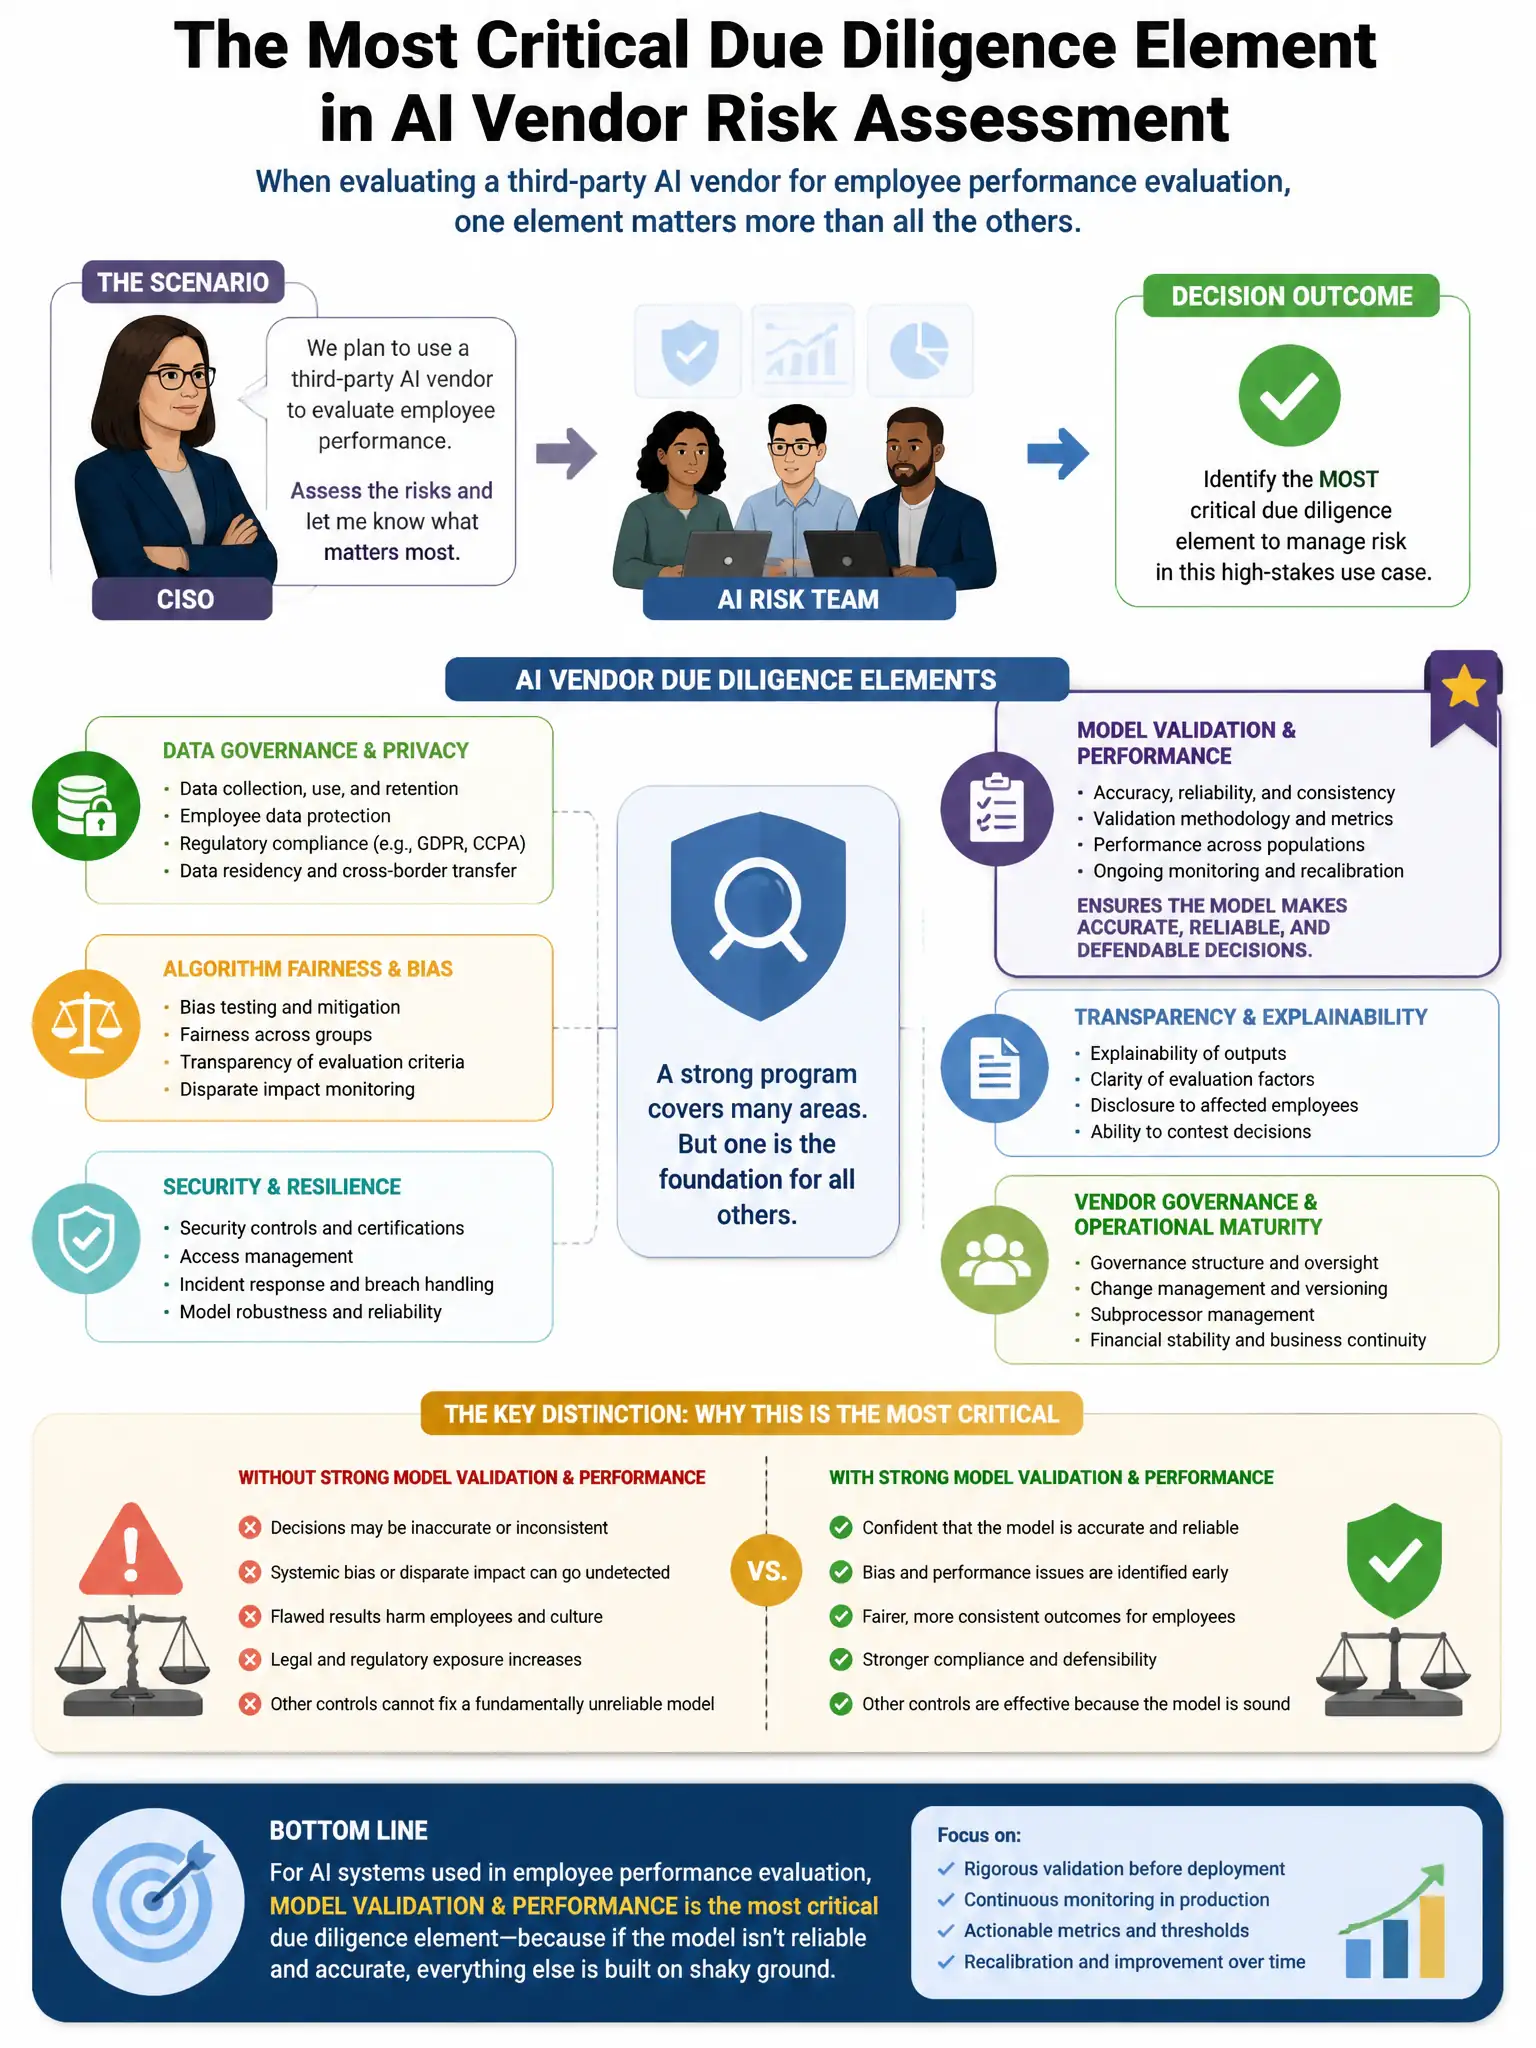
A CISO asks the AI risk team to assess the risks of using a third-party AI vendor for employee performance evaluation. Which due diligence element is MOST critical from an AI risk perspective?
Select an answer to reveal the explanation.
Short Explanation
You need the contractual right to audit the vendor's AI model validation practices and access to model performance documentation because you're the one deploying the AI system and you can't verify accuracy, bias, validation status, or controls without it. Without those rights, you can't manage third-party AI risk or meet your own obligations.
Full Explanation
The contractual right to audit the vendor's AI model validation practices and access to model performance documentation is correct because third-party AI vendor risk management requires the ability to independently assess the AI system's accuracy, bias, validation status, and control environment. Without audit rights and access to performance documentation, the organization cannot fulfill its own obligations as the deployer of the AI system. The vendor's revenue growth and financial stability is relevant to vendor risk but is not AI-specific. The geographic location of the vendor's data centers is a data residency concern. The vendor's marketing claims about model accuracy on benchmark datasets are marketing materials and do not substitute for independent validation.