
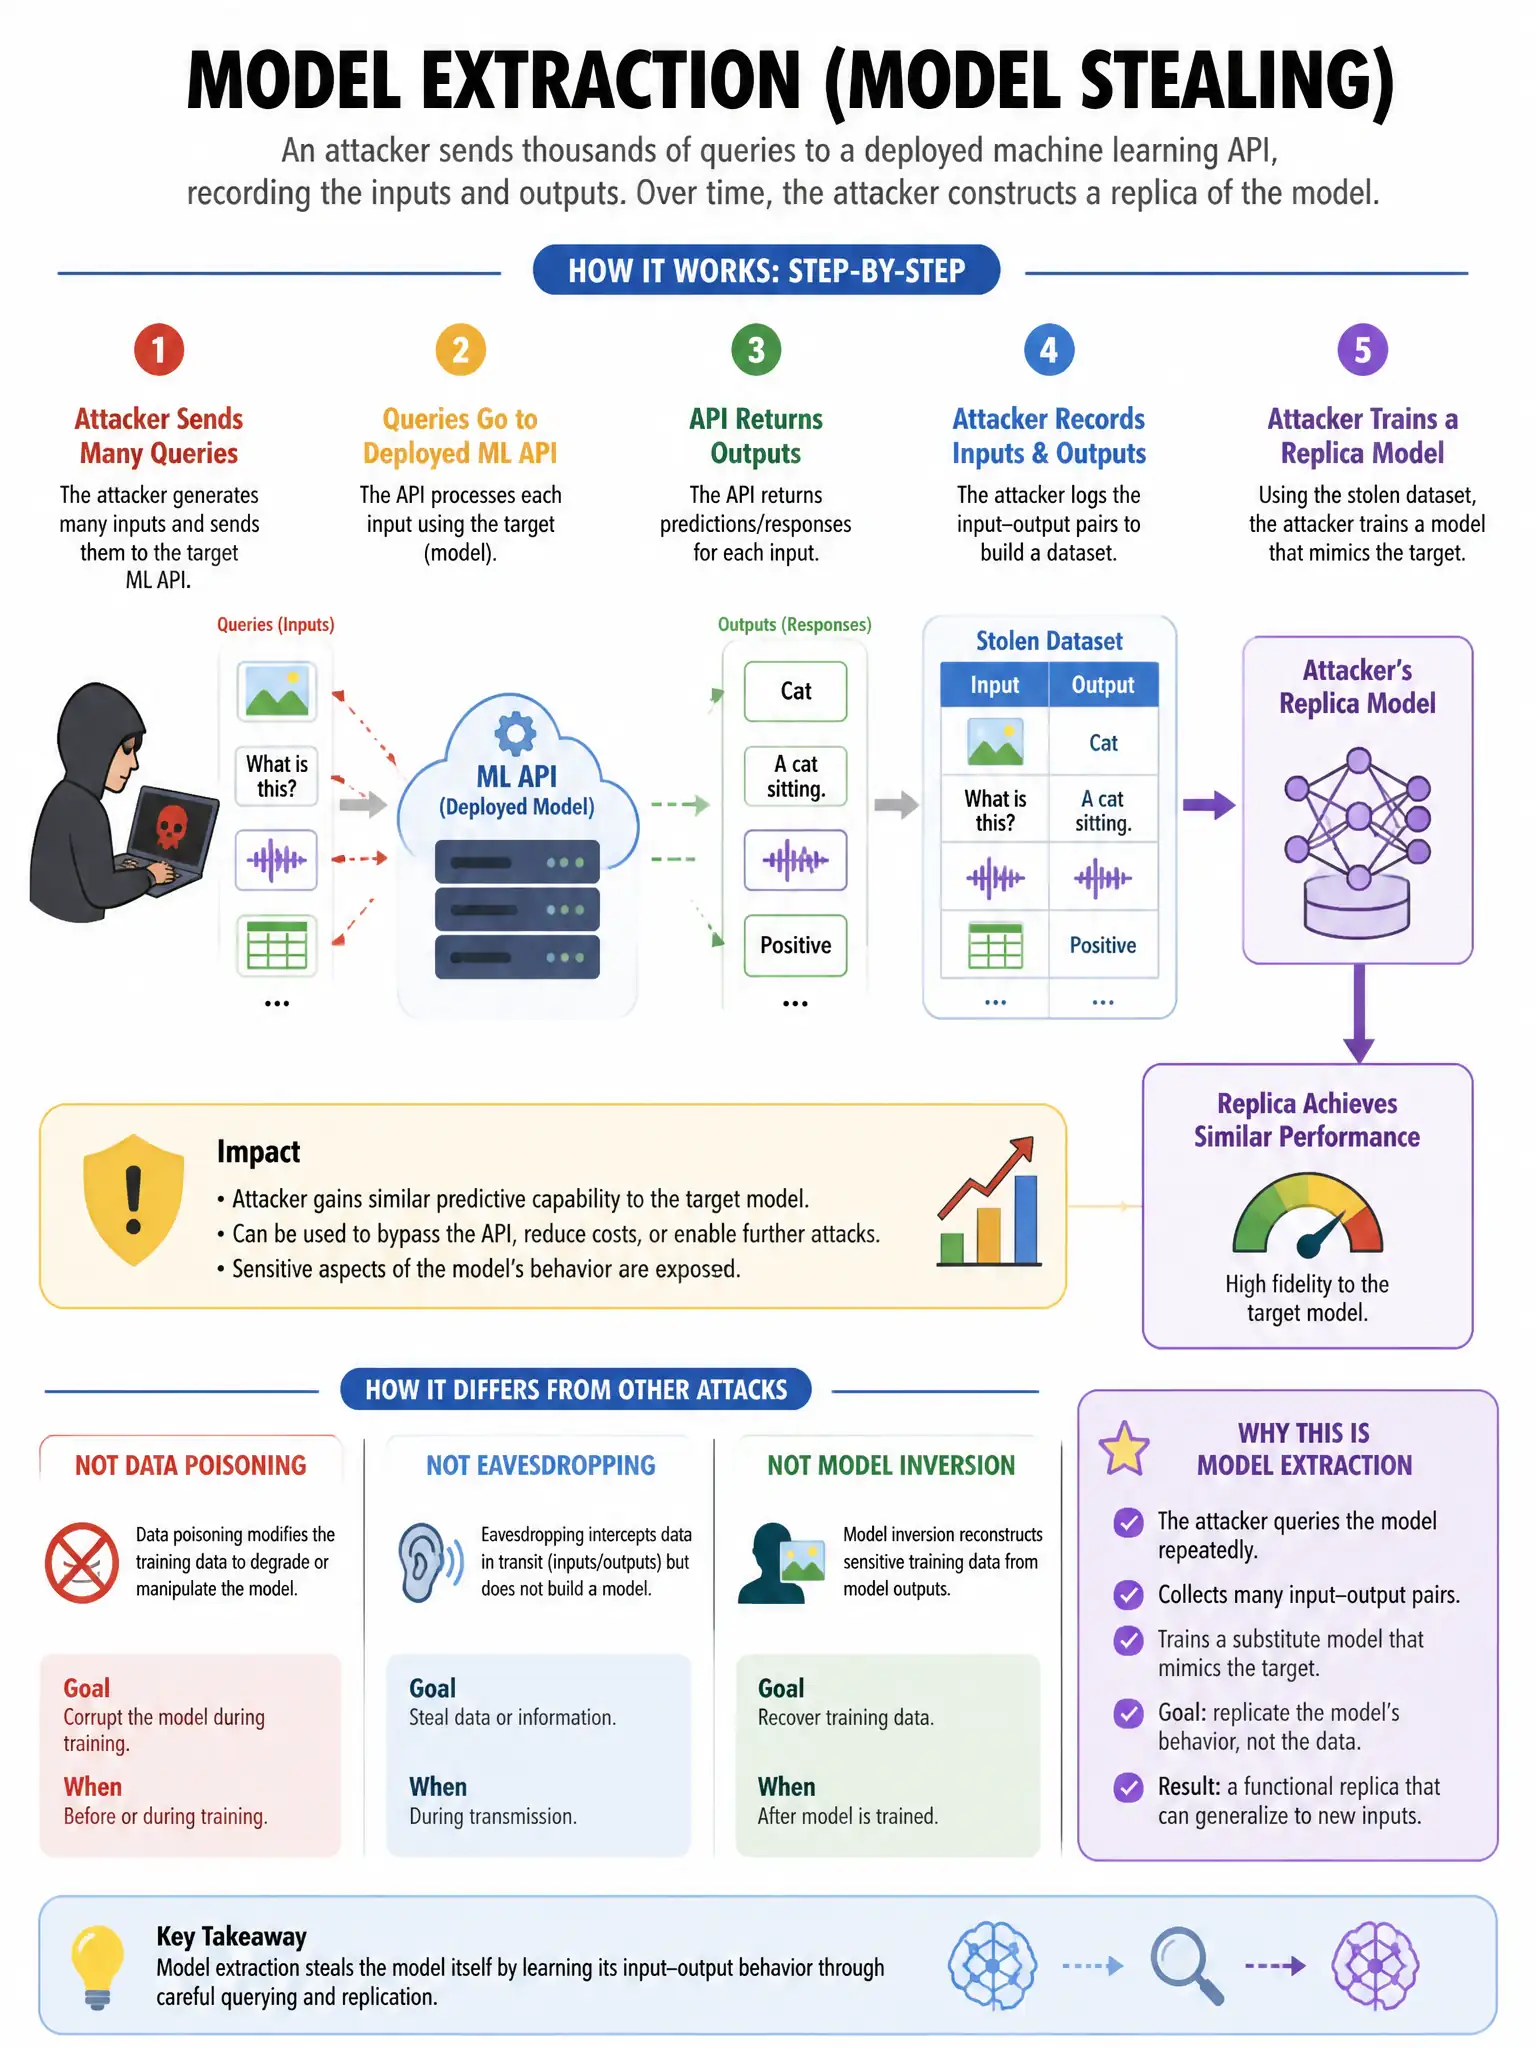
An attacker sends thousands of queries to a deployed machine learning API, recording the inputs and outputs. Over time, the attacker constructs a replica of the model. What type of attack is this?
Select an answer to reveal the explanation.
Short Explanation
Here's the deal — you're looking at a model extraction attack because the attacker uses thousands of query-response pairs to build a replica of the deployed model. That steals the model's behavior and can expose its decision logic.
Full Explanation
Model extraction (model stealing) using query-response pairs to approximate the model is correct because it involves repeatedly querying a model API to collect input-output pairs and using those pairs to train a surrogate model that approximates the original. This compromises intellectual property and may expose the model's decision logic. The data poisoning attack targeting the model's training pipeline is wrong because it targets the training phase, not inference. The evasion attack designed to cause the model to misclassify specific inputs is wrong because it crafts specific inputs to cause misclassification, not to replicate the model. The backdoor attack embedding a trigger pattern into the model during training is wrong because it is a training-phase attack that embeds hidden triggers.