
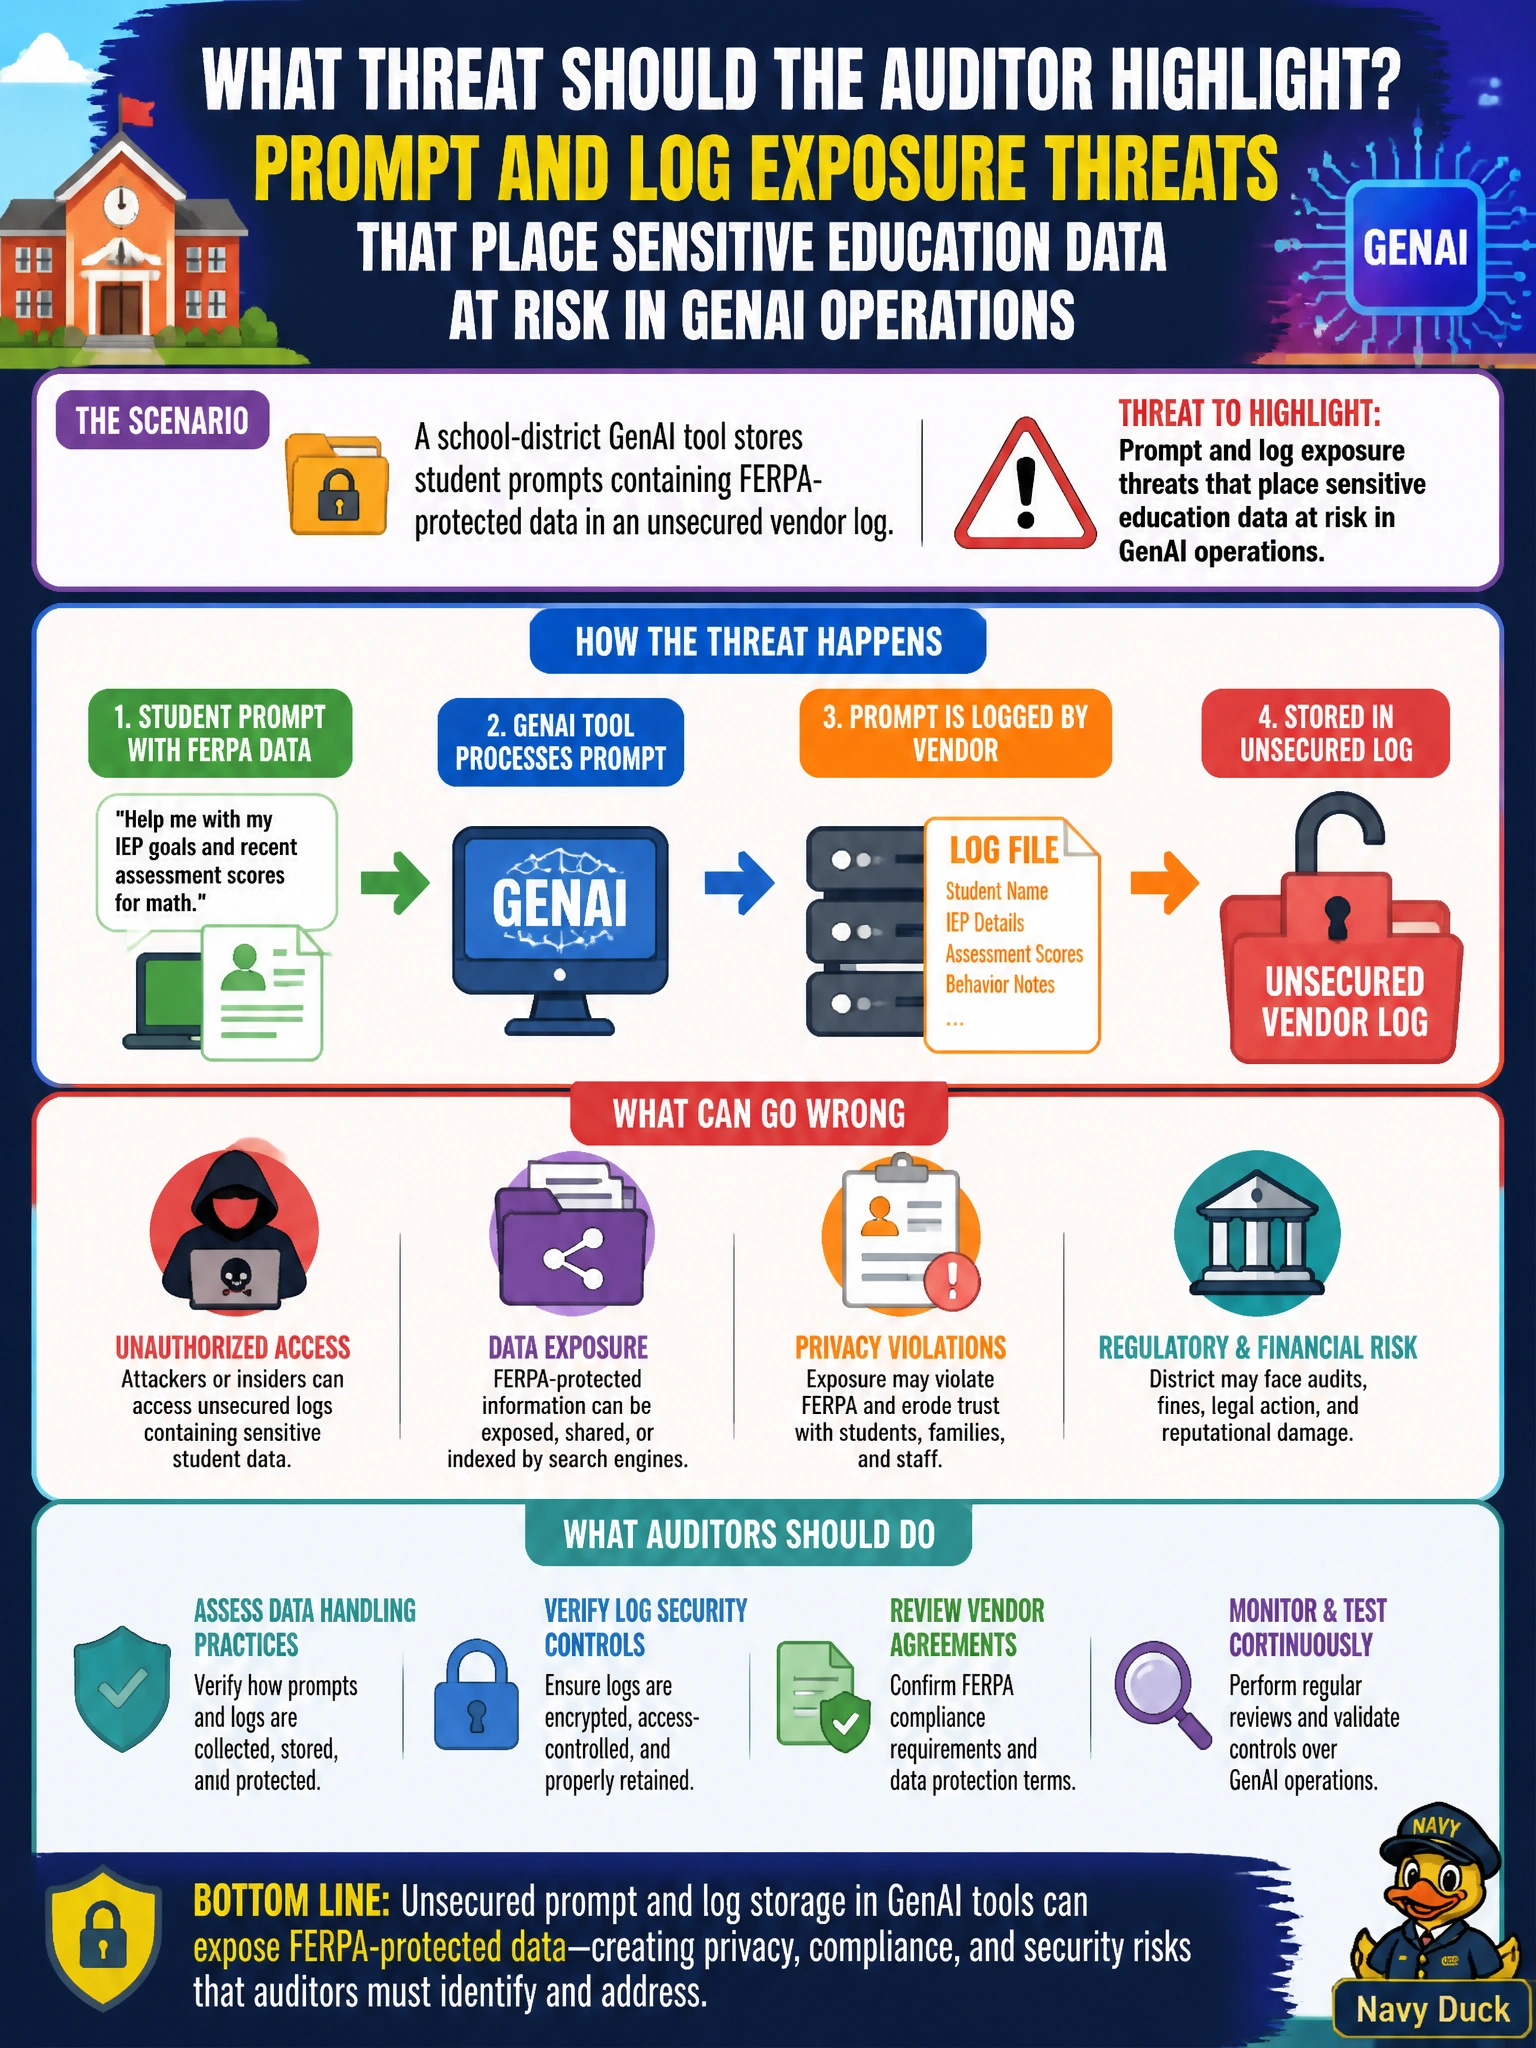
A school-district GenAI tool stores student prompts containing FERPA-protected data in an unsecured vendor log. What threat should the auditor highlight?
Select an answer to reveal the explanation.
Short Explanation
Student prompts in an unlocked vendor log are a privacy leak waiting to happen. GenAI logging is part of the threat surface for FERPA data. You won't find the exposure in slow replies, bad explanations, or missing version records.
Full Explanation
Highlighting prompt and log exposure threats that place sensitive education data at risk in GenAI operations emphasizes confidentiality of student prompts under FERPA-related expectations. The correct threat works because GenAI tools often persist prompts, completions, and debugging logs at vendors or intermediaries; unsecured storage of student content creates unauthorized disclosure pathways distinct from classic student-information-system breaches. School-district GenAI assurance must cover logging destinations, retention, access, and contractual processing limits.
Inference latency issues that slow tutoring chatbot replies during classroom peak periods fail as the threat because performance delays do not expose FERPA-protected prompts in vendor logs. Model hallucination risks that produce inaccurate tutoring explanations needing teacher review fail conceptually: output inaccuracies are unrelated to GenAI log exposure. Gaps in model version records that limit reproducibility of district tutoring outputs across terms fail because version-tracking gaps do not address unsecured storage of student prompts.
Exam caveat: "we turned off training on your data" does not automatically mean prompts are absent from operational logs, support tooling, or subprocessors. Operational check: inventory where student prompts are stored, require encryption and access controls on vendor logs, minimize retention, ban unnecessary prompt logging for sensitive workflows, and verify contractual and technical safeguards before district GenAI use.