
A new privacy regulation needs to be incorporated into an existing AI governance framework. What is the correct approach?
Select an answer to reveal the explanation.
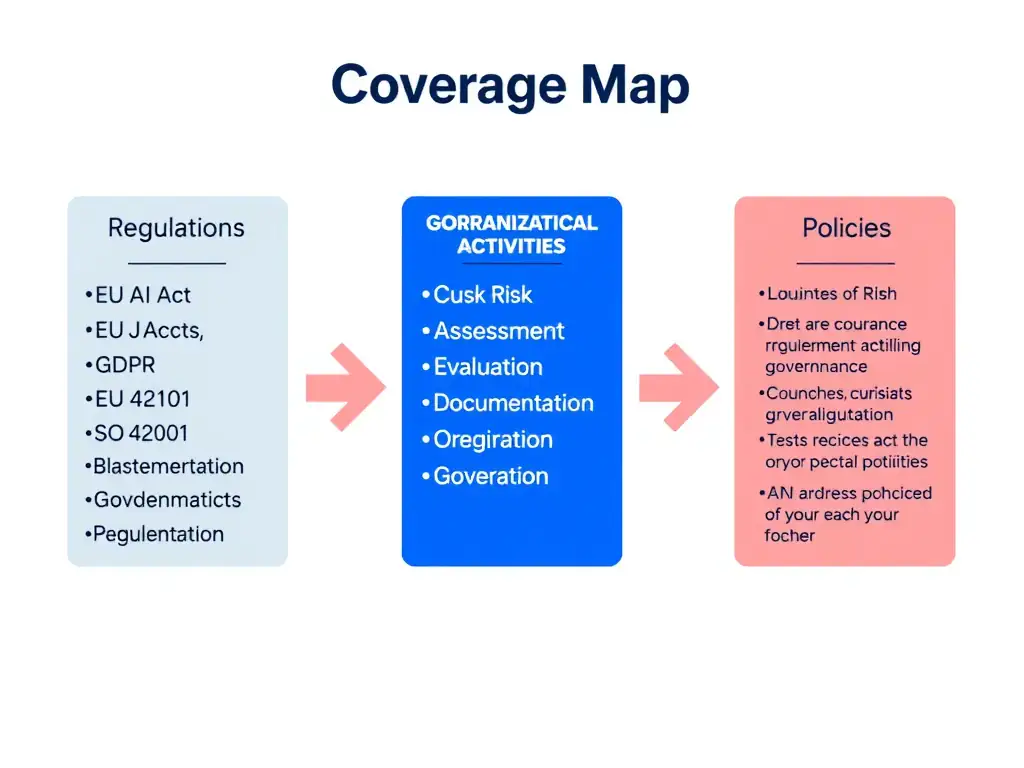
Short Explanation
The framework that was comprehensive last year isn't automatically comprehensive against rules that didn't exist yet. You need to map the new regulation to the framework's governance activities and update where gaps exist.
Full Explanation
The correct approach is to map the framework's governance activities to the new regulation's requirements, updating them where gaps exist. The new regulation needs to be explicitly mapped against what the framework already does, so any gap between what is required and what is currently covered can be identified and closed.
Ignoring the new regulation until an audit specifically references it is incorrect because waiting for an audit to raise the issue means the organisation operates out of compliance in the meantime.
Assuming existing activities already cover it, since the framework was designed to be comprehensive, is incorrect because assuming coverage without checking is exactly the gap that mapping is meant to catch.
Applying the new regulation only to new artificial intelligence systems, leaving existing systems as they are, is incorrect because existing systems remain subject to the new regulation just as much as new ones, unless the regulation itself says otherwise.
For the exam, treat new regulatory requirements as something to explicitly map and reconcile, not assume or defer.