
A GitHub Actions workflow drives HCP Terraform through the API: it uploads a configuration version and then reports success. A hard-mandatory Sentinel policy failed on a recent run, yet the workflow showed green and nobody noticed. What should the workflow do?
Select an answer to reveal the explanation.
Short Explanation
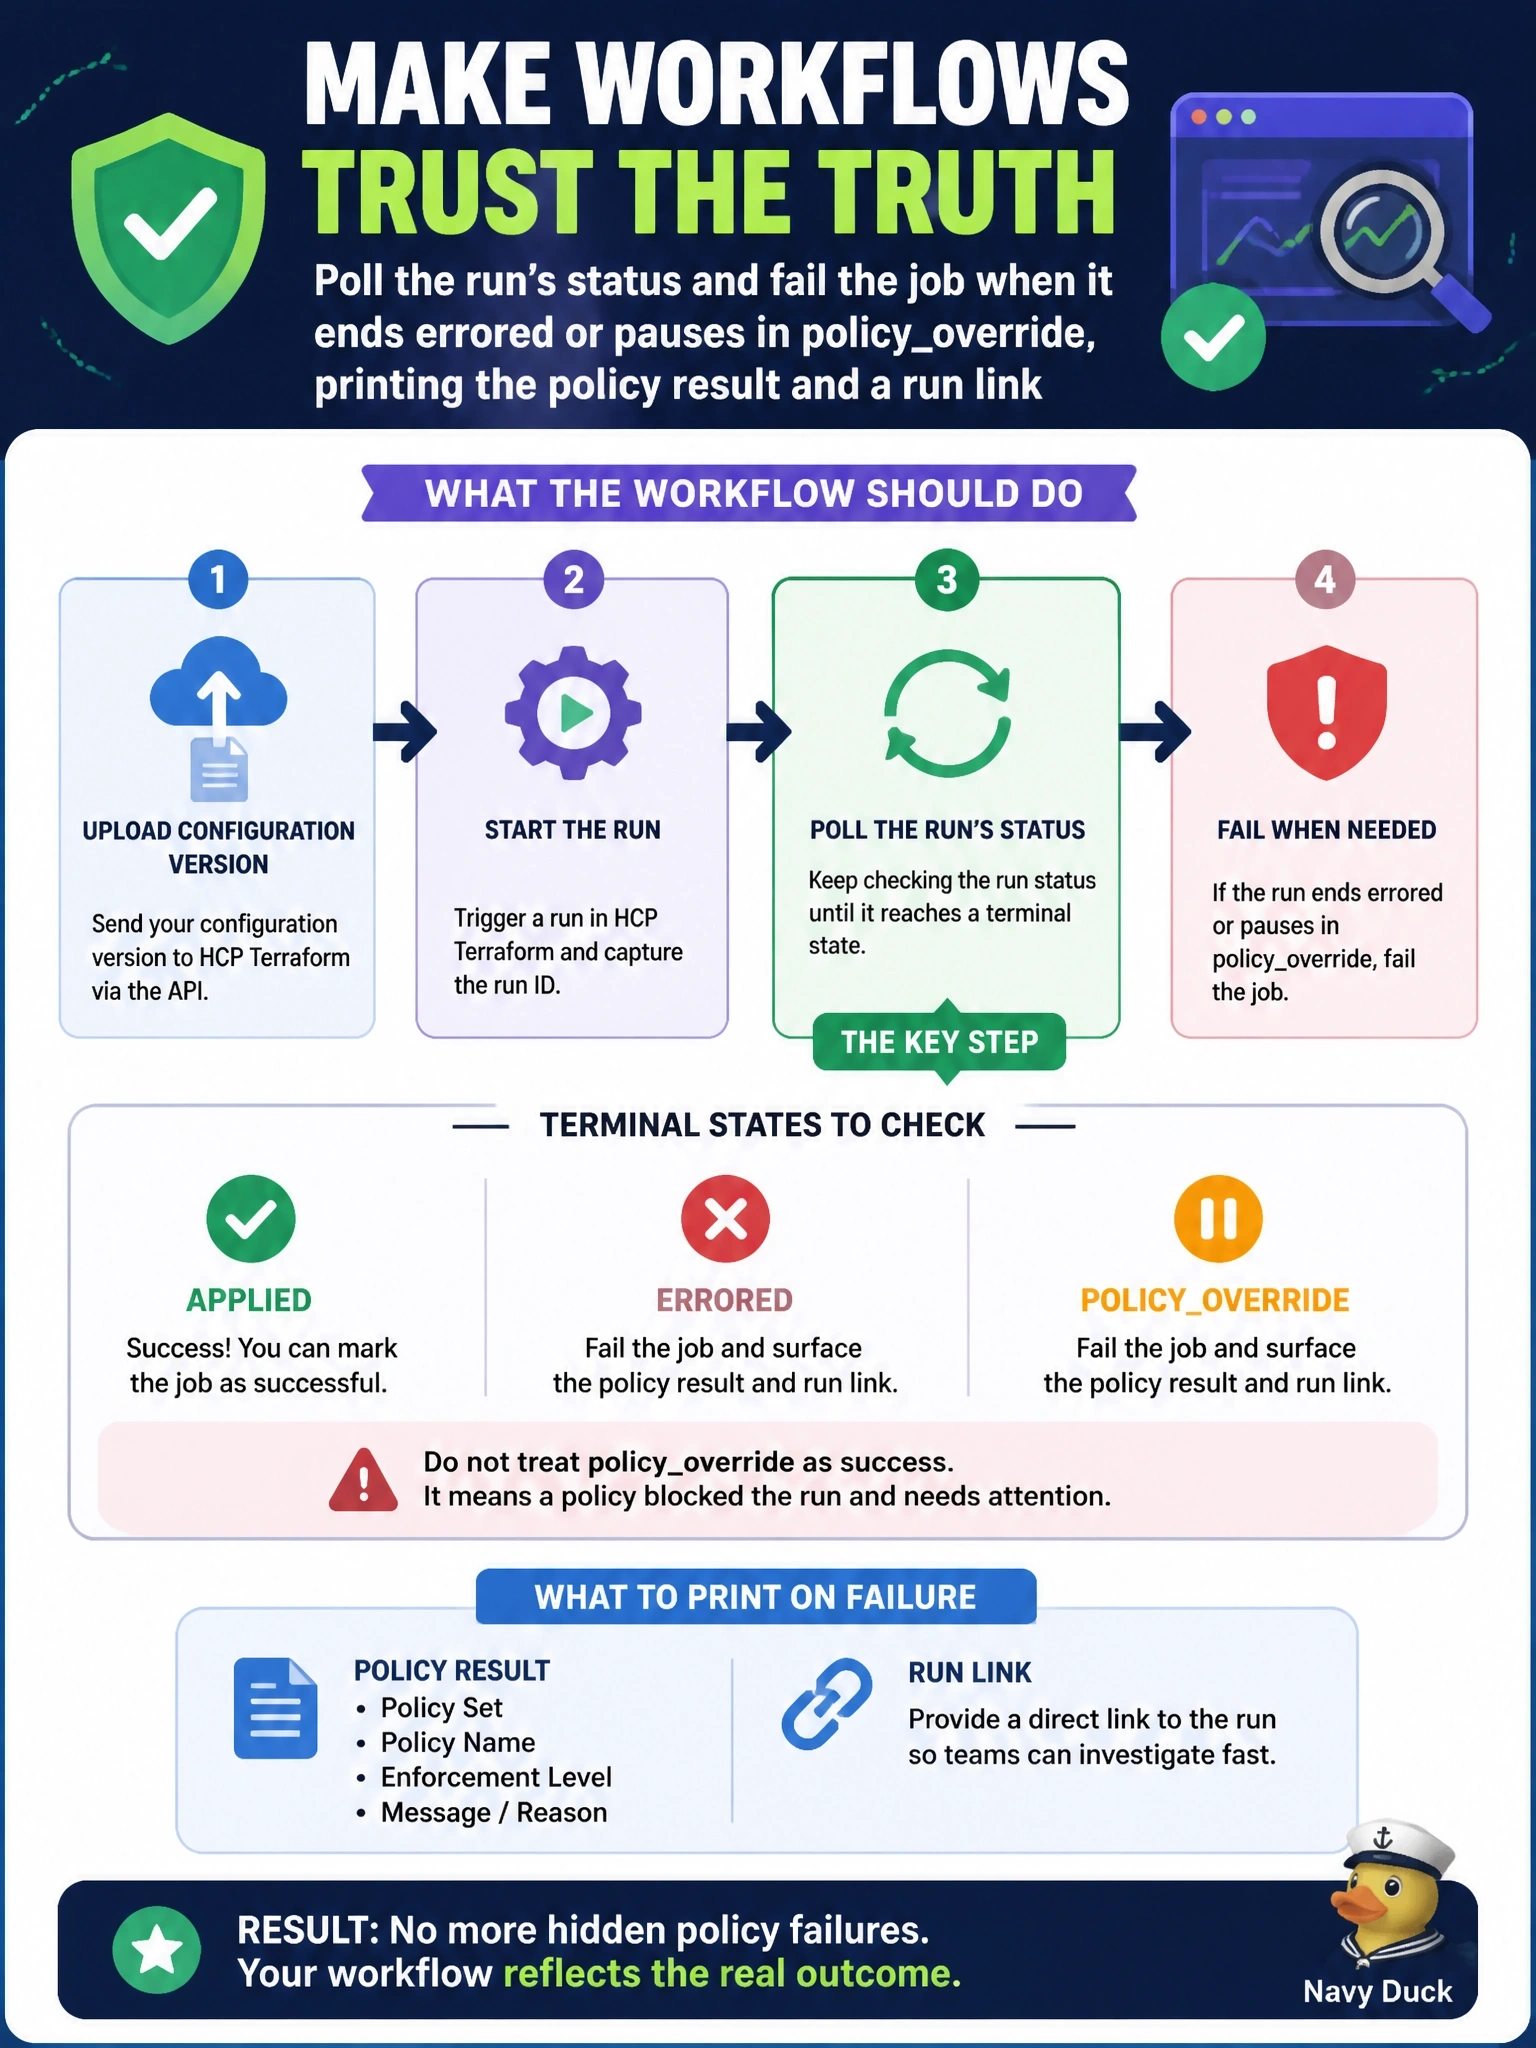
Uploading the configuration is just mailing the letter; you still need to check whether it was delivered. Poll the run, and if it errors or stops at a policy override, turn the pipeline red and show people why.
Full Explanation
In the API-driven workflow, uploading a configuration version only starts a run; the plan, cost estimation, policy check and apply happen afterwards inside HCP Terraform. The pipeline therefore has to follow the run through the Runs API and translate its final status into a job result. A hard-mandatory Sentinel failure ends the run without applying, in the Plan Errored state, which the API reports as errored; a soft-mandatory failure pauses the run with status policy_override until someone with override permission acts. Failing the job on those statuses, and printing the policy check output and a link to the run, surfaces the failure where engineers are looking. Treating the upload as success is precisely the gap that hid this failure. Retrying the same configuration cannot change a deterministic policy result and only wastes runs and concurrency. A run cannot be applied before its plan and policy stages complete, and a run that failed a hard-mandatory policy can never be applied, so calling the apply endpoint early does not bypass the check. Exam caveat: plan-only runs that soft-fail end in policy_soft_failed, and the workflow should treat that as a failure as well. Operational check: push a change that violates the policy and confirm the workflow fails with the policy name and run link in its log.