
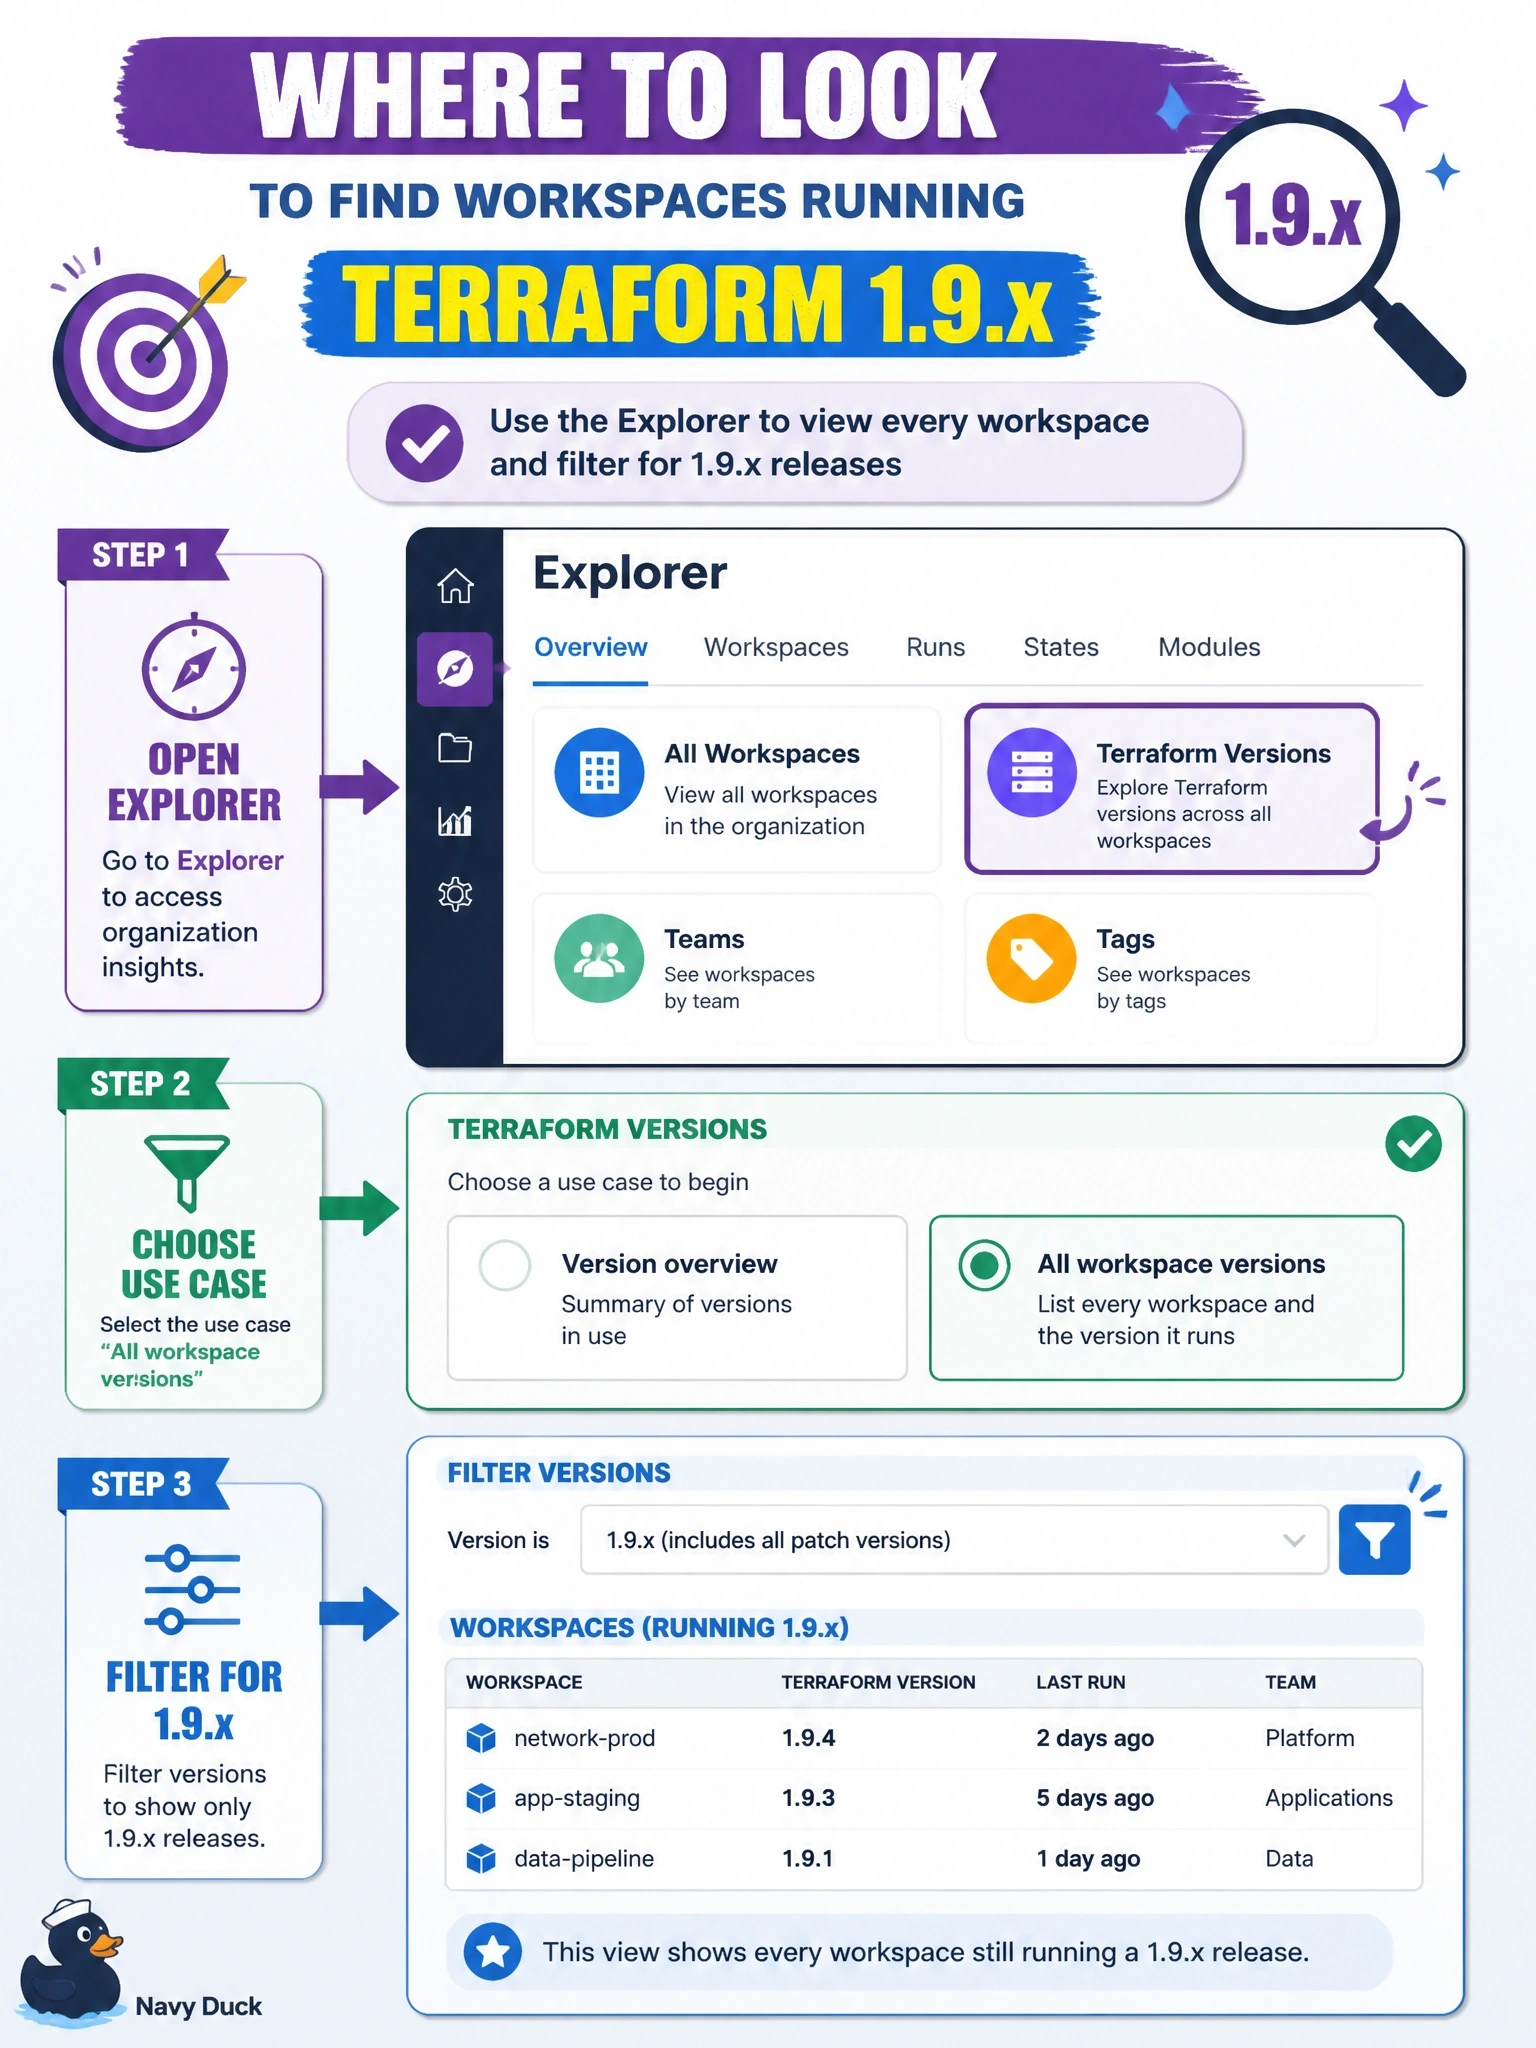
Terraform 1.9 has reached end of life inside the company, and the platform team needs a current list of every workspace in the organization that still runs a 1.9.x release, with no changes to any workspace. Where should it look?
Select an answer to reveal the explanation.
Short Explanation
The explorer already knows which version every workspace runs; you just filter. A policy only learns about a workspace when it runs, and the version field you'd need isn't in tfrun anyway.
Full Explanation
The explorer for workspace visibility supports a Terraform versions type alongside workspaces, modules and providers, and includes use cases such as Latest Terraform versions, Top Terraform versions and All workspace versions. A query filtered to the 1.9.x releases returns the affected workspaces across the organization immediately, without changing anything, and the view can be saved and re-run to track progress as workspaces are upgraded. The Usage page summarises managed resources, projects, workspaces and applies, and plan limits; it does not break workspaces down by Terraform version. A Sentinel policy would only see workspaces as they run, so idle workspaces would never appear, and the tfrun import's workspace namespace exposes fields such as name, tags, execution mode and VCS repository, but no Terraform version field. The metrics endpoint publishes gauges such as run status and resource counts, but it has no per-workspace Terraform version metric, and it needs a metrics service token and a collector. Exam caveat: the explorer requires organization owner or View all workspaces permission, and the HCP Terraform API can produce the same list for automation. Operational check: run the filtered query, export or save it, and confirm the count reaches zero as upgrades complete.